In 2023, @Synacktiv researchers identified an authentication bypass in #Danfoss SM800 and SC255/SC355 controllers. The same vulnerability, reported again in 2025, could be linked to the recent supermarket refrigeration attack.
🔎 Authentication Bypass - Danfoss SM800 & SC255/SC355: https://t.co/Gzf4DrntWp
🔎 Multiple Vulnerabilities - Danfoss SM800A: https://t.co/A3EsNHKiC4
How can an HTTP Range request help exfiltrate files and secrets from VMs?
At T-REX 2026, @TG91aXMK presented Fusetea, a tool we use during TLPT engagements to speed up Red Team ops.
🔎 Discover Fusetea: https://t.co/B7wGACShck
📑 Check out the slides: https://t.co/hTec5GDyPx
@oenb
In our latest article, @croco_byte presents new scripts allowing to simulate legitimate AD services in a flexible manner, and demonstrates their use through GPO exploitation ⬇️
https://t.co/qkgQsFltEa
Nous sommes à quelques mois de la sortie du remake de Ocarina of Time.
Timing parfait vous proposer quelques extraits choisis de cette interview en 100 questions de Miyamoto publiée quelques mois avant la sortie du jeu original.
⤵️ Un LINKOTHREAD, ça faisait longtemps 😁
1/40
CI/CD pwnage with a pre-auth RCE in #ArgoCD by @hugow_vincent 💥
Discover how a single misconfiguration in a Helm chart can lead to a full cluster compromise sprinkled with some CodeQL shenanigans! 🥷
https://t.co/bNH8rE7uNo
Using #Helm and #Kubernetes in your CI/CD pipeline? An attacker only needs access to the values.yaml file to compromise your cluster.
Recent research by Paul BARBE details a new injection technique to escalate privileges and deploy unauthorized resources ⬇️
https://t.co/xZecmuPxwc
We've been working on something for a while.
The talks your blue team doesn't want you to see.
🔴 Red Teaming. Initial Access. AD. Cloud & Web exploitation.
📍 Paris - Le Dernier Étage
📅 March 19–20, 2027
https://t.co/WcrpbyzSSV
CFP and additional details coming soon.
Releasing DCOMIllusionist as part of our talk on DCOM at @x33fcon with @k3vinTell. It's a remote in memory fileless lateral movement technique based on some research of @tiraniddo
https://t.co/XLljazKmnH
Our talk on DCOM got accepted at @x33fcon with @k3vinTell ! I'll also be giving a Red Teaming AD training with @wil_fri3d. Let's hack some Active Directory 🧙
This second blogpost concludes @yaumn_'s research on #Windows authentication reflection.
He discloses the new Kerberos authentication coercion technique he discovered to remotely compromise Windows systems 💥
A little bonus is even included at the end 👀👇
https://t.co/RsJHxCdIGe
Double trouble at #SOCON2026! Our ninja @kalimer0x00 was busy breaking down Microsoft SCCM (once again!), while @croco_byte unveiled new GPO-based attack paths & his latest BloodHound contributions targeting OUs & AD Sites. Awesome job! 👏
Finally, after many months of work, @_Worty and I finally finished putting all the pieces together to show you each detail of our research on Livewire.
Hope you will enjoy it 😁
HID recently disclosed HID-PSA-2025-002, a critical flaw in the #ActivID Authentication Appliance 8.7.
In our new blog post, @us3r777 and @__pierreg break down exactly how they uncovered it, from methodology to exploitation 💡
Read it here ⬇️
https://t.co/wmXamNEqra
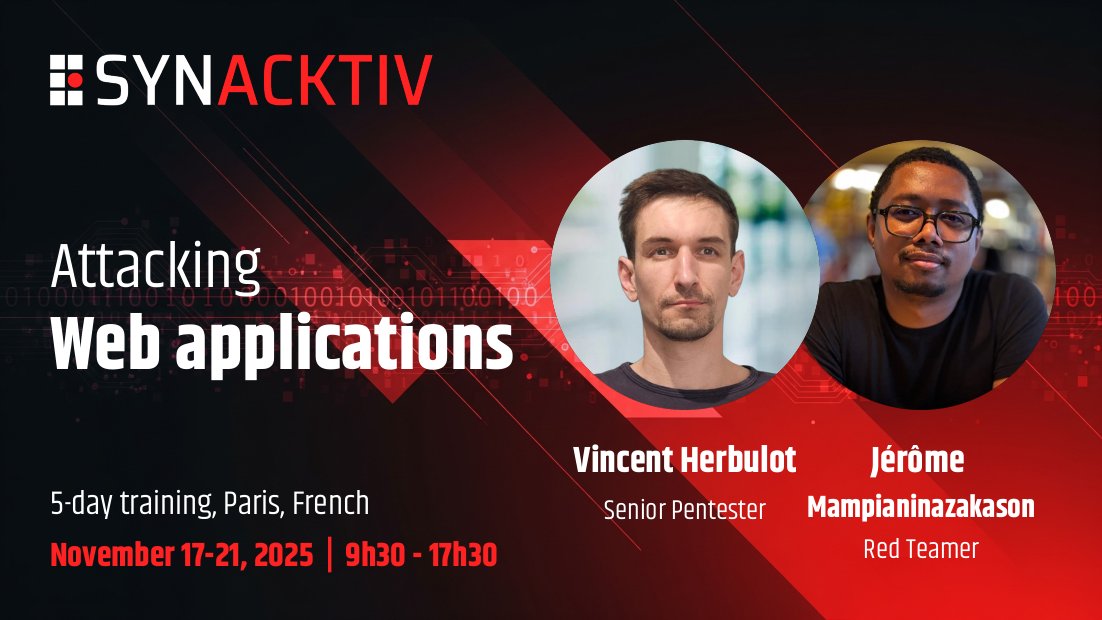
The web is a prime target for attackers. Want to refine your intrusion methods?
Join our ‘Attacking Web Applications’ training course from 17 to 21 November!
▪️ 5 days of expertise
▪️ 35 hours of lessons, more than 30 exercises
▪️ Java, PHP, Python, https://t.co/d2rWpJOTiY...
Information & registration via 👇
https://t.co/0U4lWwnFmE
The GroupPolicyBackdoor tool, presented at #DEFCON 2025, is now available on Synacktiv's GitHub: https://t.co/CWLknch5RZ
This python utility offers a stable, modular and stealthy exploitation framework targeting Group Policy Objects in Active Directory!
gpoParser, which I presented at #leHACK2025 and #DEFCON, is available here: https://t.co/sHgmiOrPCV
It is a specialized utility designed to enumerate Group Policy Objects (GPOs) and identify potential security misconfigurations.
🔥 A few hours ago our experts took the stage at #DEFCON33, sharing cutting-edge research on SCCM exploitation and modern GPO attacks in Active Directory. Proud of the team! 🙌 cc @kalimer0x00 @quent0x1 @wil_fri3d