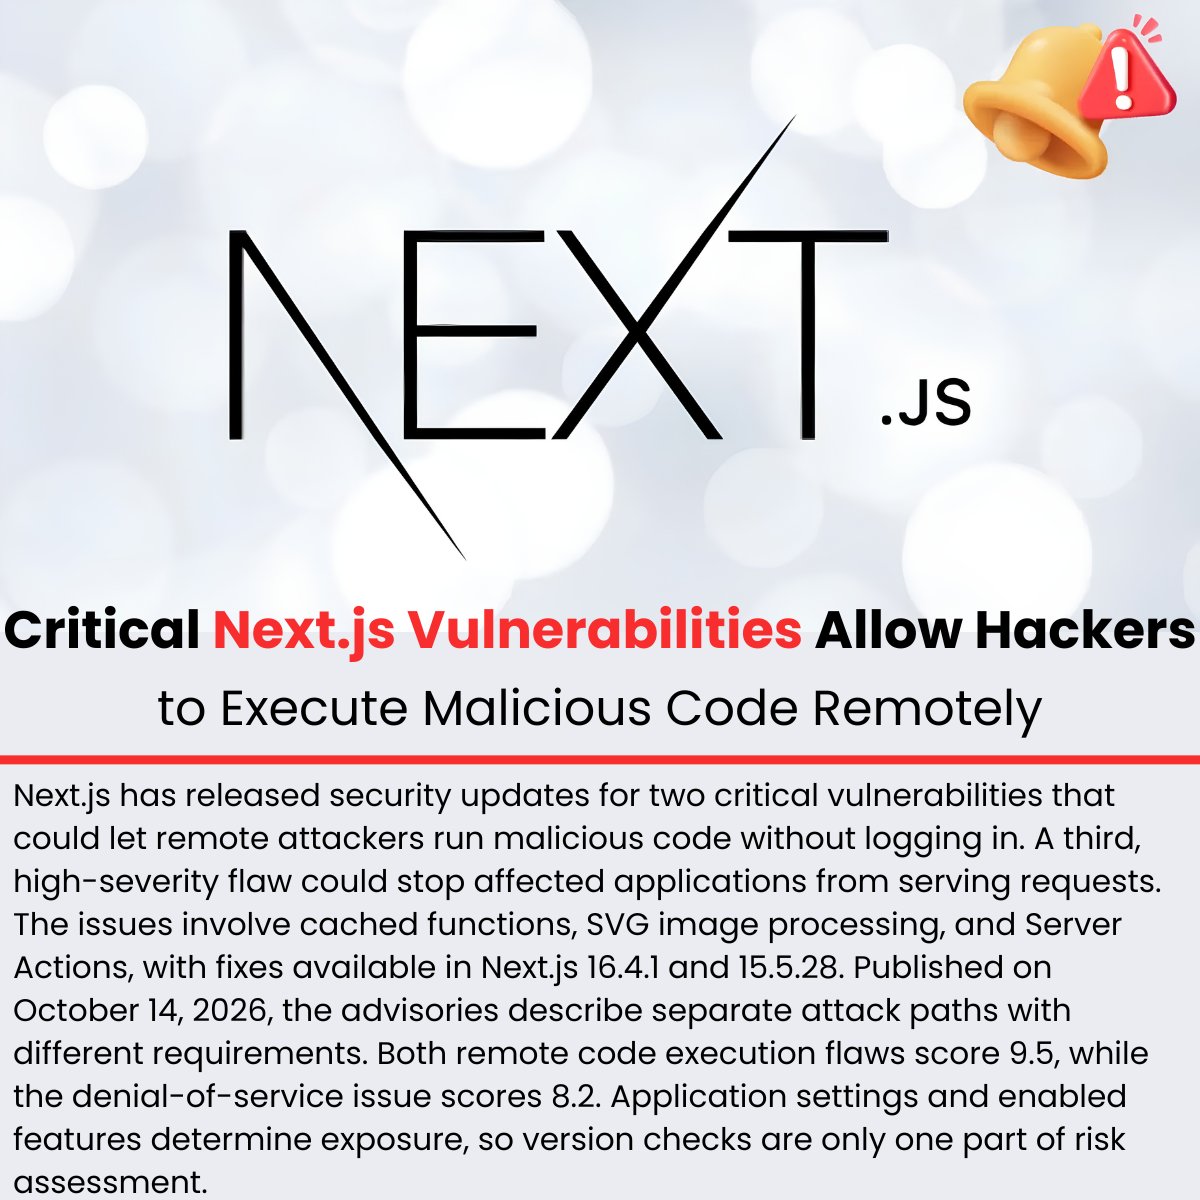
⚠️ Critical Next.js Vulnerabilities Allow Hackers to Execute Malicious Code Remotely
Details: https://t.co/TxguCCSrtv
Next.js has released security updates for two critical vulnerabilities that could let remote attackers run malicious code without logging in.
A third, high-severity flaw could stop affected applications from serving requests. The issues involve cached functions, SVG image processing, and Server Actions, with fixes available in Next.js 16.4.1 and 15.5.28. Published on October 14, 2026, the advisories describe separate attack paths with different requirements.
Both remote code execution flaws score 9.5, while the denial-of-service issue scores 8.2. Application settings and enabled features determine exposure, so version checks are only one part of risk assessment.
#cybersecuritynews