The blog that hosted the 2011 to 2015 Top 10 Web Hacking Techniques lists is gone. So are hundreds of the articles those lists cite.
I rebuilt all of it. Every nominee since 2006, all 1,136 of them, plus 351 more the nomination rounds missed.
https://t.co/89ZaEHDPLE
Quick 'n dirty BloodHound ecosystem overview. The different ingestors, collectors, analysis tools.
There might be things missing.
https://t.co/w9UI3Rii7d
.@BobDaHacker compromised FIFA and was able to hijack their livestream cameras.
They considered replacing the FIFA cameras with the 1987 hit classic "Never Gonna Give You Up" by Rick Astley. Instead, they reported it and FIFA immediately fixed the issue
https://t.co/MVfGwOnNoa
The Internet is falling down, falling down, falling down
Welcome back to another disaster - this time, an Auth Bypass in cPanel/WHM, tracked as CVE-2026-41940
Enjoy with us..
https://t.co/bOzCPy8iS1
We asked Claude to find a bug in Vim. It found an RCE. Just open a file, and you’re owned. We joked: fine, we’ll switch to Emacs. Then Claude found an RCE there too.
Full story: https://t.co/nQo9MF1Npe
Oh this is clean. A searchable, filterable RFID attack reference.
HID Prox, MIFARE, EM4100, animal tags, organized by frequency AND tool (Proxmark, Flipper, Chameleon...). This is the cheat sheet that used to live in your notes app.
Bookmark it!
you'll thank yourself on your next physical engagement.
https://t.co/XJL1B5tbkR
More fun stuff to follow as we mature out and continue to build the testing framework and remediation / hardening recommendations over time.
For the full project (and list of contributors) see: https://t.co/vUv3slhsc0
Yo, a new blog about Red Team infra
Likel : C2 , Redirectors, CDN Relays (Azure, AWS, GCP), Serverless Lambda, Cloudflare Tunnels, Phishing , Mail Servers, Malleable Profiles, and full OPSEC hardening https://t.co/6p6yfxB4tG
#APT#redteam#infrastructure#C2
It's easy to feel imposter syndrome as a hacker when you don't find bugs, but remember this.
You're looking for something that shouldn't even exist in the first place, and might not exist! It's a tough game!
Credential Guard was supposed to end credential dumping. It didn't.
@bytewreck just dropped a new blog post detailing techniques for extracting credentials on fully patched Windows 11 & Server 2025 with modern protections enabled.
Read for more ⤵️ https://t.co/mYPHg1mTKj
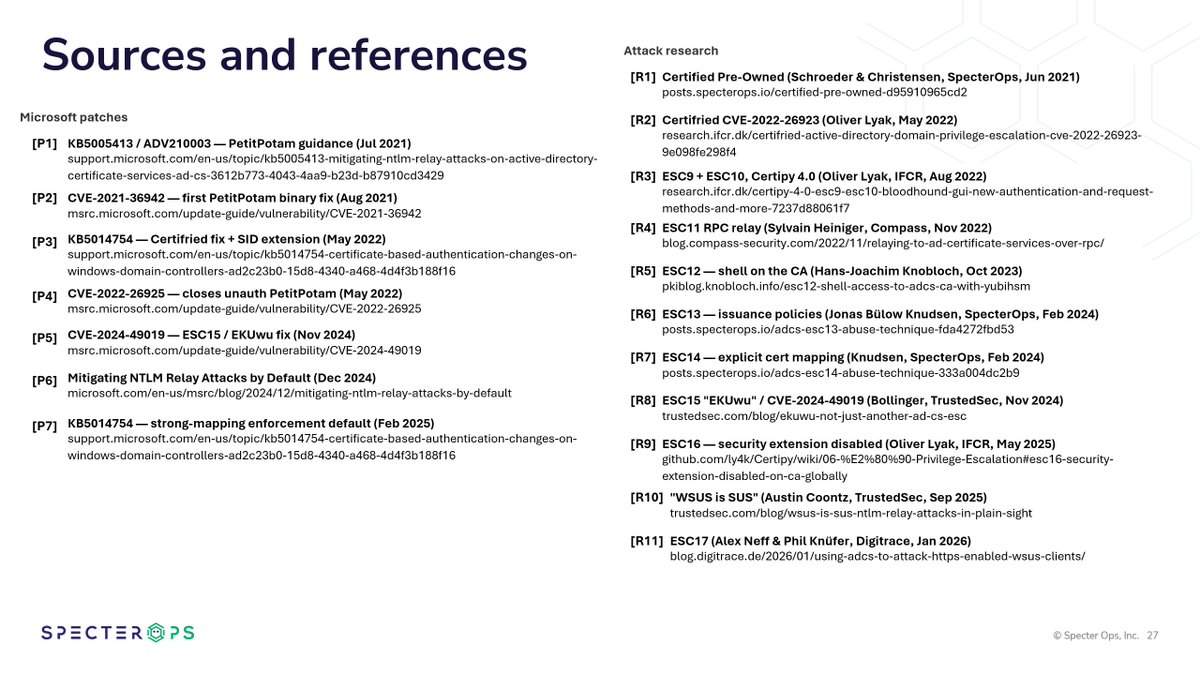
That was an interesting case about NTLM reflection but yeah, any machine that does not have th patch is vulnerable and it completely bypasses Channel Binding token (ie: we poced the relay from a ADCS server back to its fully HTTP web enroll endpoint and got the cert) pretty fun!
Classic NTLM relay problem: Stuck on port 445/TCP, can't use WMI (needs 135/TCP), and dumping hashes triggers EDR alerts.
So what's a stealthy attacker to do? 🤔
Our latest blog post explores evasive alternatives beyond the old techniques. https://t.co/s5MGVTHTO7