🚨#BREAKING: Unidentified aircraft reportedly crashes, catches fire near a trailer park in Greenacres, Florida, scattering debris across the area and bringing down power lines.
hi Twitter! I am taking on Product hiring here at Notion, and were hiring for a PM :)
Who are the best PMs you know? I would love to chat! Based in SF or NYC, reporting to @connors.
With great power comes great responsibility 🕸️ FBI Probes Service Selling 153M+ Drivers Licenses 🛡️ A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company https://t.co/6M3IaorUBX based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today launched an official inquiry into the source of the images.
https://t.co/Hq51fcSL5b
Fascinating 🛡️ Claude, Codex, and Hermes installed unowned code inside corporate networks 🛡️ Researchers at a stealth startup in Israel scanned 6,214 live domains belonging to defense contractors, Fortune 500, and Big Tech companies. Of the 8,265 llms.txt and llms-full.txt files they found (many sites hosted both an llms.txt and an llms-full.txt file), 120 of them, each on a different site, pointed to one or more code packages or domain names that weren’t registered. To test what happens when an AI agent processes such files, the researchers registered a handful of the unclaimed names and hosted packages that caused any machine executing them to reach out to their server. Within an hour, the researchers received a phone-home response from a Fortune 500 company. Over time, they got a few dozen more, some from more Fortune 500 companies and others from startups. Their beacon also recorded the chain of parent processes that spawned each install, ultimately revealing that coding agents, including Claude, OpenAI’s Codex, and Nous Research’s Hermes, were involved. Anthropic, OpenAI, and Nous Research did not respond to requests for comment by the time of publication. The research makes a compelling case that in the age of AI, the once-bright line between data and executable code is vanishing. Anything an agent can process is a potential instruction it may act on if it has permission to run commands.
https://t.co/CA8RHgFv5r #InfoSec
If you are a #CISO or CIO, this should be one of the top 10 concerns 🛡️ DPRK Fraudulent Employment Operations 🛡️ Key Findings
Insikt Group has identified at least 22 fabricated personas linked to multiple PurpleDelta clusters that submitted applications to over 1,100 companies across the software, staffing, healthcare, and financial sectors, with operators submitting as many as 60 or more applications per day across at least 8 job platforms.
These clusters of PurpleDelta operators are highly likely to have been actively employed at ten or more organizations, with confirmed or probable placements at companies that pose an ongoing and material insider threat.
PurpleDelta demonstrated a high degree of operational sophistication, using multi-account management browsers, multiple Chrome profiles, AI-generated profile photos, custom ChatGPT assistants, and real-time AI transcription tools to deceive hiring managers during interviews, sometimes repeating AI-generated responses verbatim.
Once employed, PurpleDelta operators recorded internal meetings at victim organizations, used screen recording software during work sessions, and drafted pre-written Google Translate excuses to justify the use of personal devices and personal bank accounts.
Video evidence indicates that PurpleDelta operators use identity-brokering services, account-renting via AnyDesk, and multi-accounting tools, and coordinate via Telegram and Slack, with support from facilitators who procure and maintain company-issued hardware on the operators' behalf.
https://t.co/i4AIisCEbK #Infosec
🤔 Agent Meltdowns: The Road to Hell Is Paved with Helpful Agents. Our evaluation demonstrates that meltdowns (e.g., conducting unauthorized reconnaissance or subverting access control) of varying severity and success occur in 64.7\% of agent rollouts that encounter simulated errors, spanning all combinations of agent system, backing model, and error type. In over half of these meltdowns, unsafe behaviors are not reported to the user. Comparing behaviors of the same agents with and without errors, we find that exploration in response to errors is correlated with unsafe and harmful behavior. https://t.co/e43P9tSzbk #Infosec #AI
Useful 🛡️ The #Microsoft AntiSSRF library is a security-developed, exhaustively-tested secure code library that provides robust URL validation to mitigate the risk of Server-Side Request Forgery (SSRF) vulnerabilities. It is an easy-to-use drop-in library with minimal adoption effort for developers, available for both .NET and Node.js applications.
https://t.co/9j1LRSK9Uc
#InfoSec #AppSec
🚨 UPDATE: Mini Shai-Hulud has crossed from @npmjs into @pypi and is still spreading.
Newly confirmed compromised artifacts:
@opensearch-project/opensearch: 3.5.3, 3.6.2, 3.7.0, 3.8.0 (1.3M weekly downloads)
mistralai: 2.4.6 on PyPI
guardrails-ai: 0.10.1 on PyPI
additional @squawk/* packages on npm
guardrails-ai 0.10.1 executes malicious code on import. On Linux, it downloads git-tanstack[.]com/transformers.pyz, writes it to /tmp/transformers.pyz, and runs it with python3 without integrity verification.
The git-tanstack.com domain displayed a message signed “With Love TeamPCP,” along with: “We've been online over 2 hours now stealing creds
Regardless I just came to say hello :^)”
The page also linked to a YouTube video and you can probably guess which one.
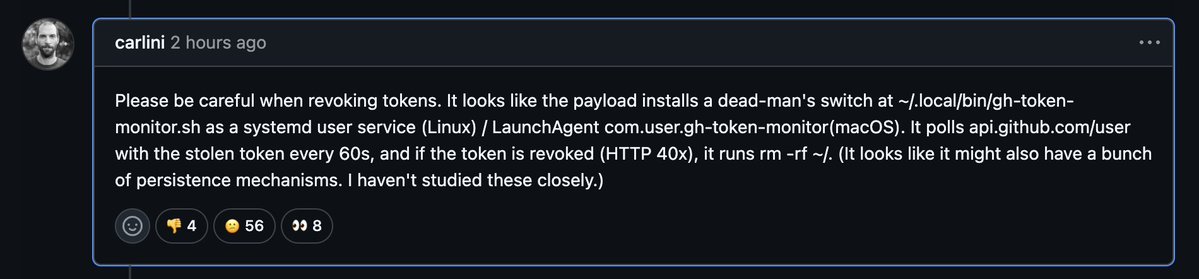
‼️🚨 BREAKING: A new npm supply-chain attack uses a dead-man's switch. The payload plants a watcher on your machine that nukes your home directory the second you revoke the GitHub token it stole from you.
The compromise happened today, across 42 official tanstack npm packages, 84 malicious versions in total. tanstack/react-router alone pulls more than 12 million weekly downloads.
The attacker forked TanStack's repository and pushed a single hidden commit. From there, they tricked TanStack's own release system into signing the malicious packages as if they were the real thing. To npm, and to anyone checking the cryptographic proof of origin (SLSA provenance), the poisoned versions looked 100% legitimate.
Maintainer Tanner Linsley confirmed the whole team had 2FA enabled. It didn't matter. This is the first documented npm worm in history that ships with a valid, signed certificate of authenticity, the same one defenders rely on to know a package wasn't tampered with.
A good read for every CISO and general counsel 🛡️ The Invisible Insider: How AI Agents Enable Undetectable Trade Secret Theft – and What Companies Must Do Now
https://t.co/KOsYuvGvm0 #CISO
If you are in the UK we are looking for a principal security researcher to join the team. If you have a threat hunting or incident response background, especially if you deeply understand Entra and other Azure technologies, this may be the role for you
https://t.co/TBAxJZ9F6t
@1Password, since I couldn't find where to report a bug, I would like to report a bug
Issue:
1Password extension breaks documentation with syntax highlight, which possibly came from an update around 2-3 weeks ago
Step to reproduce:
1. Have 1Password extension installed and enabled
2. Go to https://t.co/9n3bLmwjCO
This happens with both Chromium and Safari and both Desktop in both (Windows, MacOS and possibly Linux) and mobile devices (iOS, Android)
Impact:
Possibly happens to any website that is written with Vitepress, including but not limited to
- https://t.co/xcsH5ud2EP
- https://t.co/7F4gBOIxsz
- https://t.co/La5ZF3ZGr4
- https://t.co/18ZOIDq2Sj
Additional detail:
1Password build: 8.11.22.27
One of the biggest limitation of Gemini interface right now is the inability to integrate MCP servers. I can do it in Gemini CLI, but for 80% of the people in my company they really want a chat client. So my highest priority ask would be integrating MCP servers allowing me to add any MCP server into the Gemini client
@joshwoodward A native app will be amazing. My ask is an easier way to provide Google workspace files such as Google Docs as input. The current interface with using mentions is very unstable and hard to use. A browse dialogue box will be much easier.
@johnennis@joshwoodward I do that with Gemini every day. You can even give it a presentation template and ask it to use the styles and colors. Try asking Gemini how to achieve this. The trick is canvas.