The #FBI issued a FLASH advisory warning that cybercriminals and state-aligned hackers are exploiting ARTEX, a super intelligence-powered penetration testing framework, to automate attacks against businesses and organizations worldwide. ARTEX can accelerate intrusions from initial targeting to privileged access in under three hours. It was used in the October ConnectWise supply-chain compromise, which exposed Microsoft 365 customer environments and involved attempted authentication against more than 2,250 downstream tenants.
The FBI is urging businesses and organizations to strengthen access controls, monitor suspicious automated activity, and report potential compromises to https://t.co/Y65F8KJfqo.
Read more here: https://t.co/Cl5lpZ7cgG
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
We're partnering with @huggingface to investigate an unprecedented security incident.
Cyber-capable OpenAI models compromised Hugging Face production during a benchmark evaluation.
Sharing preliminary findings to help defenders understand emerging risks:
https://t.co/CIor15y9xk
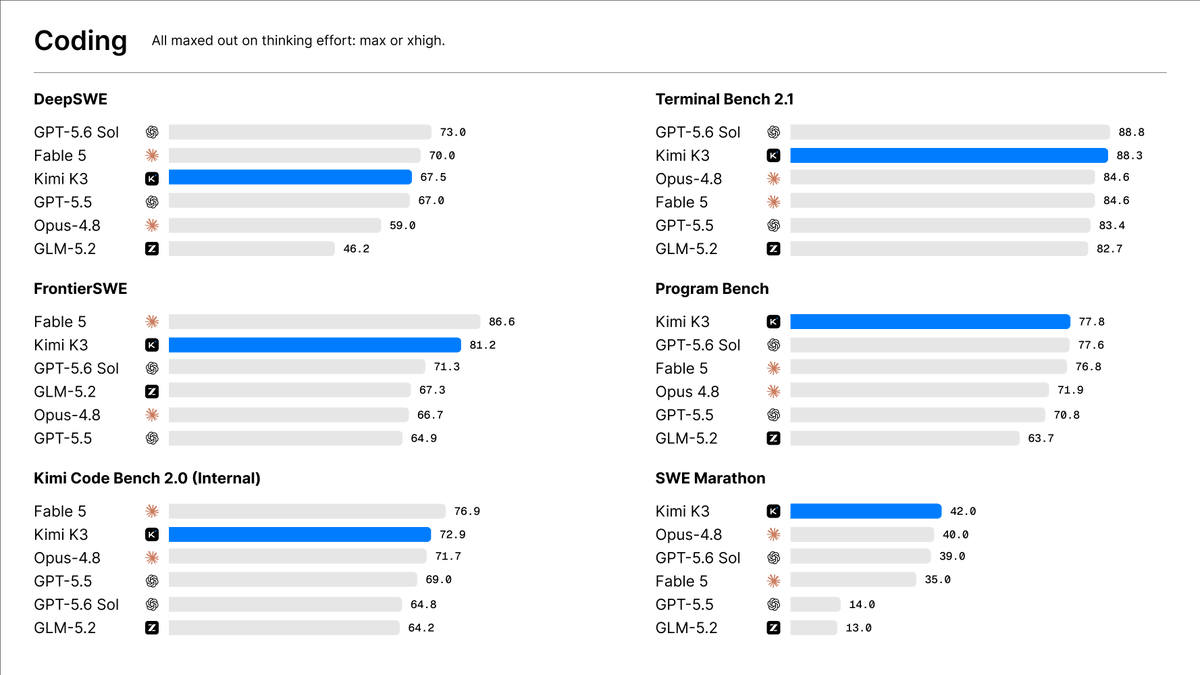
Introducing Kimi K3: Open Frontier Intelligence
🔹 2.8 Trillion Parameters, 1 Million Context, Native Multimodal
🔹 Kimi Delta Attention enables up to 6.3x faster decoding in million-token contexts
🔹 Attention Residuals deliver ~25% higher training efficiency at <2% additional cost
🔹 Built for long-horizon agentic coding and self-evolving workflows
Kimi K3 is now live on on https://t.co/zrk6zZxZUo, Kimi Work, Kimi Code, and the Kimi API.
Open Weights by July 27, 2026.
🔗 API: https://t.co/XCrgjXAqMw
🔗 Tech blog: https://t.co/YTfiMSNM1f
New Mimikatz
Researchers took an old version of Mimikatz and taught it how to dump credentials from the latest operating systems!
The research: https://t.co/JxZwg135Mr
The repo:
https://t.co/Lpsu09AMng
#redteam#pentesting
Actor exploiting CVE-2023-46747 (F5 BIG-IP Auth Bypass Vuln ) from 195.248.71.38 🇷🇺
( LLC Melt-internet )
VirusTotal Detections 0/95 🟢
Actor attempts to create a new admin user with full permissions
0-Click Microsoft 365 Copilot Vulnerability Lets Attackers Exfiltrate Sensitive Data Abusing Teams
By Guru Baran - June 12, 2025
https://t.co/dYKxuMMk3A
Hahahahhahahaha
Unironically a good idea. It's so unbelievably stupid and it works. Depending on explorer layout, the .exe might not be visible.
Filename.mp4 + ??? spaces + .exe
Hahahahahaha UNC6032 is wild as hell
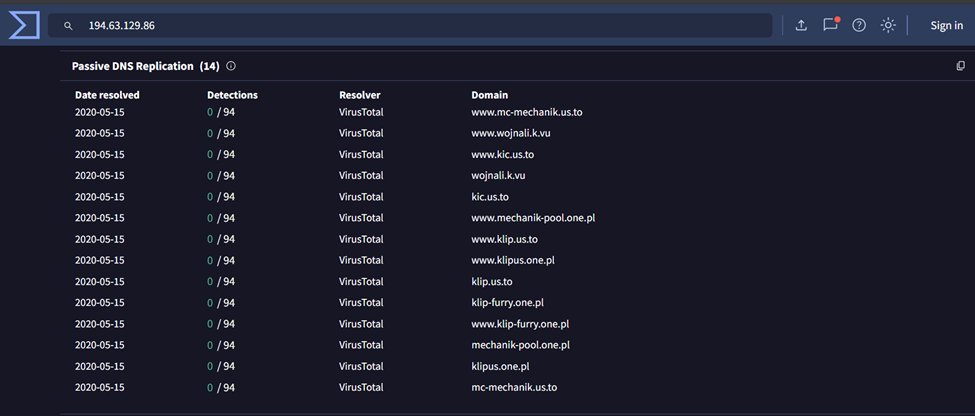
just hunted down fresh undetected & low detected APT43 (kimsuky) infra by pivoting using HTTP header analysis and SSL JARM fingerprinting
162[.]220[.]11[.]84 --> 0/94
194[.]63[.]129[.]86 --> 0/94
3[.]89[.]115[.]251 --> 0/94
110[.]142[.]212[.]109 --> 1/94
More IOCs in replies
OneDrive - New Default Sync Feature: Automatic syncing bypasses established security protocols, as it lacks inherent controls, logging mechanisms, and corporate policies that typically govern the synchronization of personal accounts on business devices.
https://t.co/rohdaVkCuo
NEW: CrowdStrike announced that it will lay off around 500 workers as part of "a strategic plan" to "to evolve its operations to yield greater efficiencies."
The cuts represent 5% of its global workforce.
https://t.co/WtPWU0c3vx