Four more Equixly updates to close October!
🔐 Login Steps: Describe login; Equixly authenticates.
🧭 SPA discovery: Find more endpoints.
✨ Guided setup: New wizard + clear next steps.
⚡ Sidebar shortcuts: Launch scans from anywhere.
Read more in the first reply 👇
PHP released fixes today for #PHP2Shell (CVE-2026-109618, CVE-2026-109619), two critical RCE vulnerabilities in PHP.
Update to 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restart PHP-FPM or your web server.
How the details leaked and why a version check isn’t enough 👇
🚀 Equixly August 2026 update is here!
🧭 Attack Trace: see how the agent reached each vuln
🤖 AI Red Teaming: now configurable in the UI
⚡ Faster pentest scans, clearer scan checks
🏷️ Discovery tags, better filters, bulk actions
🔗 Simpler MCP server URL
#AppSec#APISecurity
🚀 Equixly July 2026 update is here!
🕸️ Service Overview: your full attack surface on one radial map
🔗 Qualys integration: push findings to VMDR, pull asset inventory
🔍 Smarter Discovery: rate-limit awareness + exponential backoff
#API#AppSec#CyberSecurity#WAF
🚀 Equixly June 2026 update is here!
🧠 AI Red Teaming for your LLM
🕸️ Attack Surface graph
🔍 Discovery: scheduled scans, MCP detection, technology tagging & natural-language auth
📋 Three tailored reports per scan
#API#AppSec#CyberSecurity#AIRedTeaming
🚀 Equixly May 2026 update is here!
🧠 Knowledge settings for app-aware testing
🔍 Faster API and web app discovery
📋 Restyled compliance section
⚡ Multi-service creation from one upload
📥 API spec export
🤖 MCP Server coming soon
#API#AppSec#CyberSecurity
🚀 April 2026 Equixly Update!
🔍 Discovery: Auto-find & test APIs without specs.
🌐 DAST: Dynamic App Security Testing for SPAs & web apps!
🔗 Integrations: Native Jira, GitHub & ServiceNow syncing.
🛠 MCP Security: Dedicated testing for AI infrastructure.
#api#security
✨ Equixly’s February Product Update is here!
🎨 Redesigned UI for simpler navigation
🍪 Advanced cookie management for complex auth flows
⚡ Faster workflows and improved performance
Built to make API security testing easier, faster, and more reliable.
#API#security
Top 12 Tips for API Security
- Use HTTPS
- Use OAuth2
- Use WebAuthn
- Use Leveled API Keys
- Authorization
- Rate Limiting
- API Versioning
- Whitelisting
- Check OWASP API Security Risks
- Use API Gateway
- Error Handling
- Input Validation
--
Subscribe to our weekly newsletter to get a Free System Design PDF (158 pages): https://t.co/uc5M7CdXXC
Remote hackers can compromise your entire network just by sending you a Fax message
https://t.co/2gMcODVM2L
Check out video demonstration and learn how the 'Faxploit' attack works.
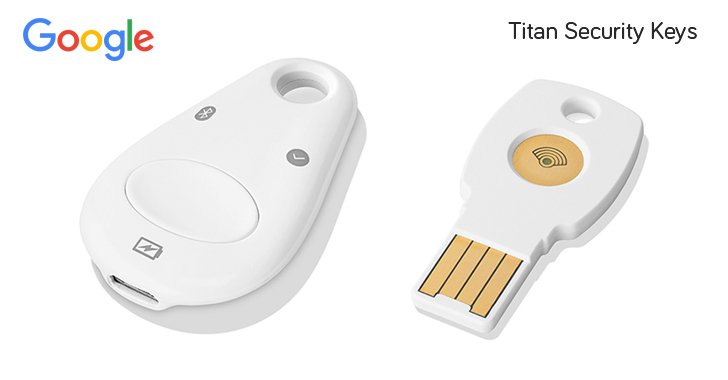
Titan Security Keys — Google launches its own USB-based FIDO U2F physical security keys.
https://t.co/2RuY7z5VID
It includes a firmware developed by Google that verifies the integrity of security keys at the hardware level for stronger two-factor authentications.
Google said it has not had any of its 85,000+ employees phished on their work accounts since early 2017, when the company began requiring logins via Security Keys https://t.co/kAWIgvCn3r