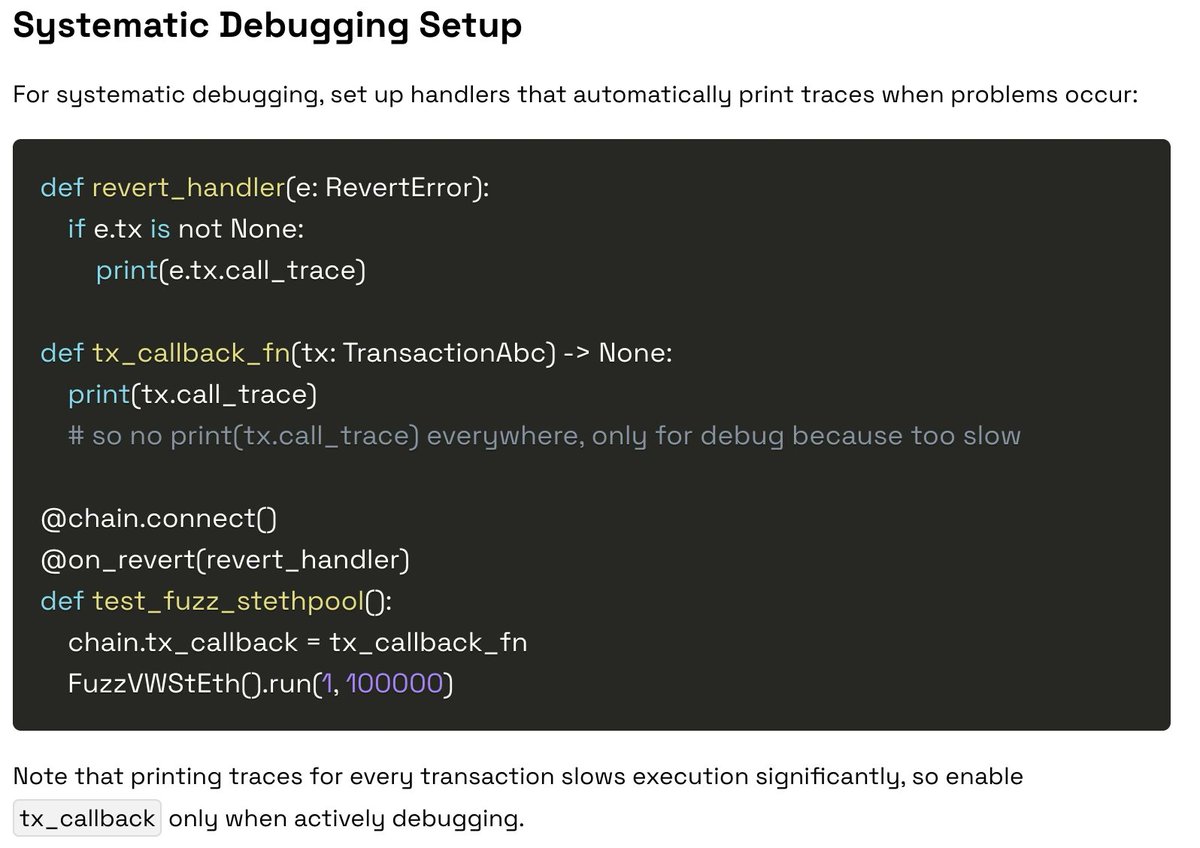
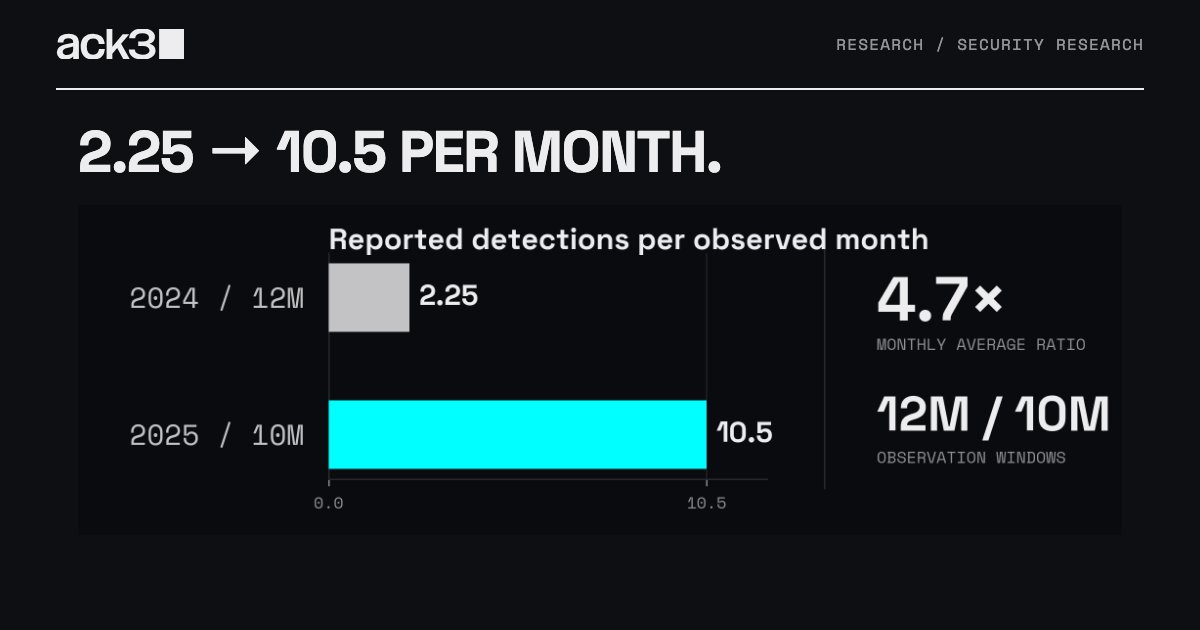
Your fuzz run failed. You're 2 hours into printf debugging.
Wake gives you Python's ipdb + Solidity console.log + transaction traces + automatic shrinking.
The debugging workflow Ackee's audit team uses to turn hours into minutes:
Thread ↓
アセンブラ短歌. Assembly tanka: a program that runs in exactly 31 bytes of machine code, written as five phrases of 5, 7, 5, 7 and 7 bytes. No instruction may cross a line break.
@meditationduck wrote the poetry for EVM▮
1/ Just finished my talk at @Web3SecSummit during @belgradebw 🫡
Traditional fuzzers: 73/153 bugs after 8h.
AI-guided fuzzing with Wake: 153/153 in 79 min.
Measured on the Daedaluzz benchmark.
So, what are my takeaways? 🧵⬇️
SPEAKER ANNOUNCEMENT 📣
AI can already find smart contract bugs by reading code. So, do we still need fuzzing?
@michprev, author and lead developer of Wake, joins Web3 Security Summit to answer exactly that.
See you in Belgrade 🫡
NEW SPEAKER ANNOUNCEMENT 📢
@michprev, AI Tooling Partner at @ack3ai, is joining ETH Belgrade.
Michal is building AI agent tooling for smart contract security. He is also the author of Wake, the open-source Solidity development and static analysis framework built at Ack3, where he spent years developing tools used in security audits.
His session will look at how AI is changing smart contract security and the developer tooling built around it.
Hear Michal’s perspective on where automated auditing is heading next 👇
our data in @RektHQ's story.
H1 2026: 135 verified DeFi hacks, $939.86M lost.
we have read every audit report of the hacked projects:
- 94.4% of audited-victim losses were outside audit scope
- verified in-scope exploits: only 4.9% of losses
- median gap between audit and exploit: 18 months
filter every hack/auditor in the dashboard: https://t.co/q08sj2EVfM
VS Code extensions have become a security nightmare.
One click grants access to source files, local processes and the network.
Here is how not to get scammed ↓
if you manage to jailbreak Fable, you'll find that you can report it through the @AnthropicAI bug bounty program (for $0 reward, though) on @Hacker0x01
but it's triaged by H1, so potentially, if they claim your jailbreak isn't a jailbreak, Anthropic won't even know about it? And that would mean you could legally use Fable for whitehat work (since it is not a jailbreak)?
there's no motivation for anyone to report the guardrails bypass, and based on the public data, they're not overloaded with submissions, so I'm just amazed that nobody even wants to discuss it with me
Registration for #SekaiCTF 2026 is now open: https://t.co/GzovO60S6Y
Our prize pool features USD$8,000 in cash and prizes worth over $10,000! Additionally, the top team will be invited to the 11th XCTF Finals.
P.S. Make sure to bring your essentials...
Fuzzing is a MUST in every smart contract codebase's security
It would be awesome if someone released a free, single command, fast-running AI Skill that builds high-coverage fuzz testing suites. Maybe some good person is preparing to launch such an AI Skill this week...🤔
Introducing Sakana Fugu: A full multi-agent orchestration system accessible via a single model API.
Our ‘Fugu Ultra’ model matches the performance of Fable and Mythos, delivering frontier capability without the risk of export controls.
Try it: https://t.co/hhO6qTawgb 🐡
Did you know we open sourced a fuzzer, an AI Framework and a VS Code / Cursor Extension for Fuzzing Solidity?
- One click to scaffold
- One line command to have AI work for you
- One command to run a 10x fuzzer
All on our Github