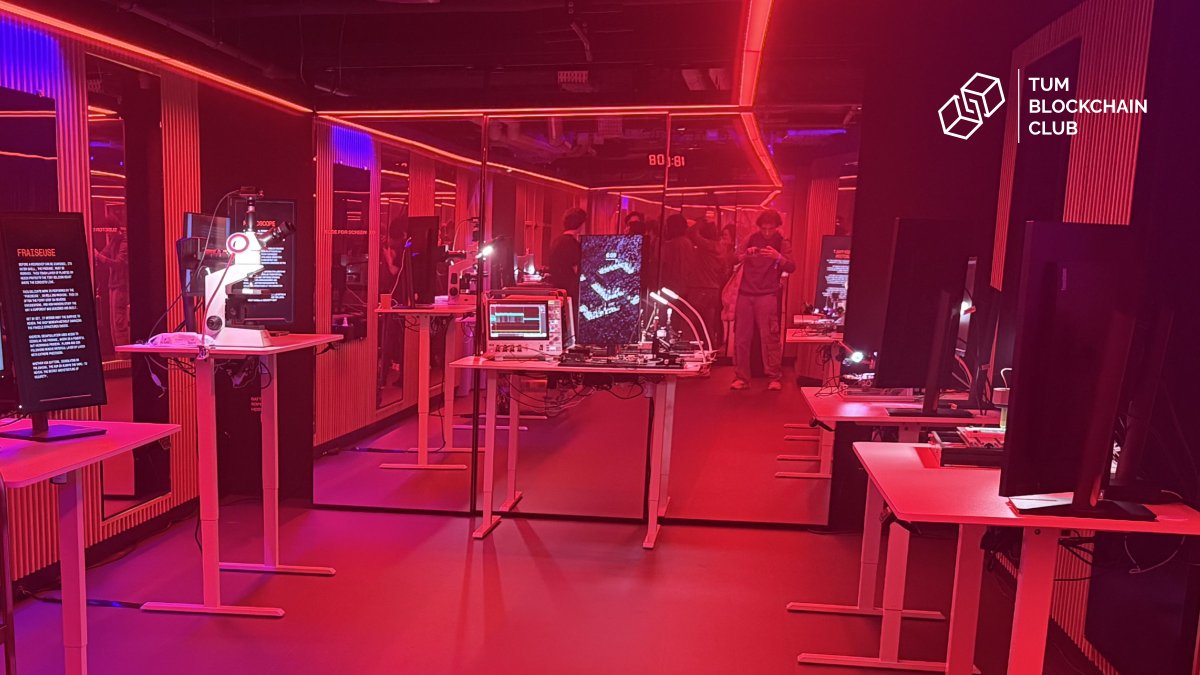
gm from the students’ day at Op3n 🇫🇷
Workshop, panels, hackathon finals & networking.
A packed day for the next generation.
Everything happening today 👇
Update from Ledger Donjon on the CryptoBilis investigation 🔽
@DonjonLedger is investigating Ledger signers sold by CryptoBilis, a reseller in Southeast Asia, that contained an unauthorized hardware implant. Ledger confirmed this on October 10th for one affected user's signer. All confirmed fund losses tied to the incident disclosed on October 9th involve signers sold through CryptoBilis. We have not verified a drain linked to a signer bought elsewhere. CryptoBilis has confirmed it stopped selling Ledger signers while the investigation continues.
Based on the Donjon's analysis of the attack, the implant sits inside the enclosure and reads the data shown on the screen. During setup, the signer displays the 24-word recovery phrase. When the implant detects these screens, its microcontroller decodes the words and transmits them over LTE using a provisioned eSIM. The implant is a separate component. It does not modify the Secure Element or the Ledger operating system, and it does not alter transactions or signatures.
The Donjon will analyze the signers it receives and will share more as the investigation continues.
We have not confirmed the total number of affected users or the total value lost. Figures circulating online come from third parties and Ledger has not fully verified them. If your funds were drained and you have not contacted us, please do so through Ledger Support so we can include your case. We are also reviewing reports of implants in other signers and locations. We will continue to share information as the investigation progresses. Rest assured the Ledger team is going above and beyond to leave no stone unturned to investigate this situation to the strongest possible outcome.
If you bought a Ledger signer from CryptoBilis and have not set it up, do not set it up and contact Ledger Support. If you have set it up, transfer your assets promptly to a new signer with a new recovery phrase. Do not enter or restore any recovery phrase on a signer bought from CryptoBilis. Never enter your recovery phrase into a website, app or form.
If you lost funds or hold a tampered signer, contact Ledger Support at https://t.co/QzukOZdEzq and file a report with local law enforcement. Do not send the signer to anyone before speaking with Ledger Support or local law enforcement. If you lost funds, coordinate with law enforcement before opening the signer. Researchers and others with relevant information can write to [email protected].
If you did not buy from CryptoBilis and want to inspect the inside of your signer, the guide is at https://t.co/Bh9DHQulIv. Use caution and make sure your recovery phrase is backed up first, because opening a signer can damage it.
Ledger will never call you, message you directly, or ask for your 24-word recovery phrase. We will update this post when we verify new information.
We regularly communicate about the results we achieve. But sometimes, the journey matters just as much as the result.
We recently managed to bypass the RP2350-A4 debug protection using an innovative approach combining two techniques: photon emission imaging and laser fault injection.
Here our technical blogpost: https://t.co/y6E6r1BbGw
A big thank you to @Raspberry_Pi for the collaboration and for highlighting this work.
💥
Every morning, a team of elite hackers walks into Ledger HQ.
Their job: strengthen the security of every device we ship: and raise the standard for the entire ecosystem.
This is the Ledger Donjon 🧵
What if a hacker could gain total control of your smartphone, not via malware, but the hardware itself?
The @DonjonLedger discovered a potentially unpatchable flaw impacting MediaTek Dimensity 7300 - a popular Android phone SoC - enabling arbitrary code execution in minutes. Here’s how 🚨
The absolute highlight? An exclusive tour of the *Ledger Donjon* 🛡️.
This is Ledger's top-secret lab where their white-hat hackers relentlessly attack their own hardware (and competitors') using side-channel attacks, fault injection, and more.
Their goal: Find vulnerabilities before bad actors can, and responsibly disclose them to secure the entire ecosystem.
🚨At Ledger Donjon, we don’t just secure our own products, we help make the entire crypto ecosystem safer.
As part of our ongoing security research and responsible disclosure efforts, we identified an important vulnerability in Tangem’s Android app.
👇🧵
Security leaves no room for error, a single variable mishandled, and the entire security model can collapse.
We're excited to share an illustration of this through our recent research on the Tangem card.
Big thanks to the @Tangem team for their responsiveness and collaboration!
DevOps practices are all well and good, but beware of the configuration of the tools that access your production.
Find out more about Argo CD misconfiguration in this new blog post.
⏬
https://t.co/56FTTAuR3C
#argocd#security#devops#devsecops
Last week at @hardwear_io NL 2024, we showcased some of our attack tools we use in the Donjon, and a live demo of a double fault injection ⚡️⚡️ with the transportable laser bench!
Our tools are open-source and presented on our webpage: https://t.co/ulu1YsAxZu
🔬 Live Fault Injection Demonstration!
Join @mickm111 at #hw_ioNL2024 as he showcases lightweight test bench utilizing laser injection and simple optical hardware. See fault injection methodology in action 🤓⚙️
👉 https://t.co/aHPpdlCpST
#faultinjection#hardware#donjon
This week the Donjon brought its transportable laser bench to the https://t.co/xrCRQEAv2a conference in Rennes by train 🚄.
A proof that a functional Laser Fault Injection bench is not that impossible to see anywhere.
Next step in the Village @hardwear_io NL 2024 conference!
During next @hardware_io conference, @DonjonLedger will showcase tools developed and used for Fault Injection Attacks!
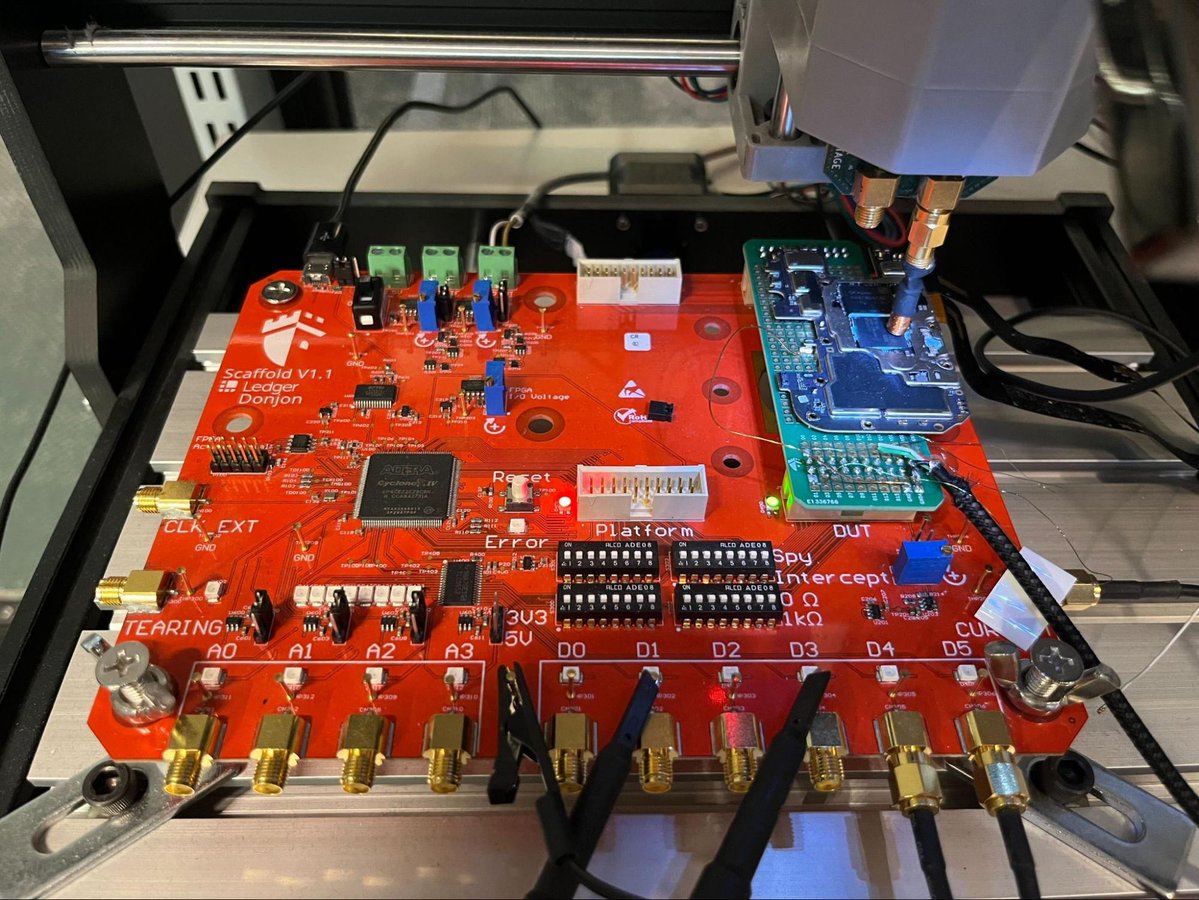
Pass by in the Village to see a part of our Tool Suite: Scaffold, Silicon Toaster, Laser Studio, QuickLog, Curmea… operating on our transportable laser bench!
Ledger will be in Nashville for @TheBitcoinConf this week!
We’re eager to spend a week fully immersed in the Bitcoin world, with leading speakers, educators, and inspiring keynotes. Stay tuned for an exciting announcement of our own!
Scroll down to learn more about how you can find us here at Bitcoin Nashville.
Exciting news from @DonjonLedger!
Introducing cargo-checkct, our cutting-edge tool to protect against timing attacks.
Curious about what timing attacks are & why typical solutions don’t quite cut it in crypto? Dive into our latest article to learn more! https://t.co/FUaEll9QZP
We are thrilled to have open-sourced cargo-checkct, to help bridge the gap between academic research and industry practices for the early detection of timing vulnerabilities in cryptography libraries. Read more about it in our blog post. https://t.co/WlFmaxxGN2