DON'T WASTE YOUR TIME ON THE PROGRAM'S BUGBOUNTY
They've been spamming us with duplicates; the companies don't fix the bugs and just say, “Sorry, we've already found everything,” and you're left high and dry.
#bugbounty#scam
This finds more subdomains than Subfinder
Passive sources only know what they've seen. Internal staging environments, recently created subdomains, anything that never got indexed — invisible.
Add puredns bruteforce with a solid wordlist and you're checking names passive tools never saw.
The pipeline:
subfinder for passive
puredns bruteforce for what passive missed
merge both
httpx for live hosts
Best wordlists: SecLists dns-Bitquark-subdomains-top1million or assetnote best-dns-wordlist.txt. The difference between a 10k and 10M wordlist is real.
HE'S ALREADY FINDING BUGS WORTH 1000$
Your AI agent just got access to 150+ pentest tools.
HexStrike is an MCP server. You connect it to Claude, GPT, or Copilot — and the model gets hands-on access to nmap, sqlmap, nuclei, metasploit, and 150+ more. It picks the tool, runs it, reads the output, and decides what to do next.
Not a copilot suggesting commands. An agent actually running them.
CVE-2026-21858 (Ni8mare), CVSS 10.0.❗️
n8n sits on a lot of self-hosted automation. Plenty of those boxes are exposed.
No auth. Public form-workflow. File read on the host.
Chained, that's instance takeover.
Affected: 1.65.0–1.120.x
Fixed: 1.121.0
n8n Cloud: not affected
PoC:
https://t.co/iY6htz7NX9
A bot that was never in your group could read your Telegram messages.
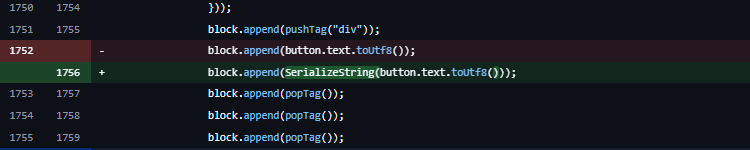
Telegram Desktop escaped everything except inline button text. A bot hid a script there, someone forwarded the message into a chat, and it sat in history for months — firing the moment that chat got exported to HTML and opened.
Two years and four months in production. The fix is one line.
6.9.4 / 7.0.1. Updating doesn't clean exports you already made.
Found by Denis and Aleksander Rostilov, ExPatch.