Super excited to finally share @the_st0rm and my year-long research into Telegram at @BlackHatEvents!
Telegram user? Curious how it works, how secure/private your conversations are, or just here for some cool vulns?
Buckle up cause we’re crashing the paper airplane #BHEU
RASPIRE (@raspire_) is building app security at AI speed.
As AI accelerates mobile attacks, their platform protects Android and iOS apps from fraud, reverse engineering, and API abuse with zero code changes. They're already securing apps used by 20M+ people across banking, fintech, and healthcare.
Congrats on the launch, @EzV01d & @hsanmost!
https://t.co/0J7Sw3GOHe
🔐 Just launched DVBank Lab - an open-source vulnerable banking app for hands-on AppSec training! Built with Python/Flask & React. Learn source code review through real banking scenarios 👨💻 https://t.co/mcTzQ72Mcc #AppSec#CyberSecurity
Synack Red Team member @Zombiehelp54 knows a thing or two about permission #misconfigurations. Read along to understand his thought process to find the exploit path as well as his suggestion for preventing the vulnerability. https://t.co/LBrGcSm2FJ
#infosec#pentesting
I’m thrilled to announce the first release of candytools which is a tool I wrote to automate the process of preparing Android OTA images for analysis. https://t.co/h9BQAcdYhU
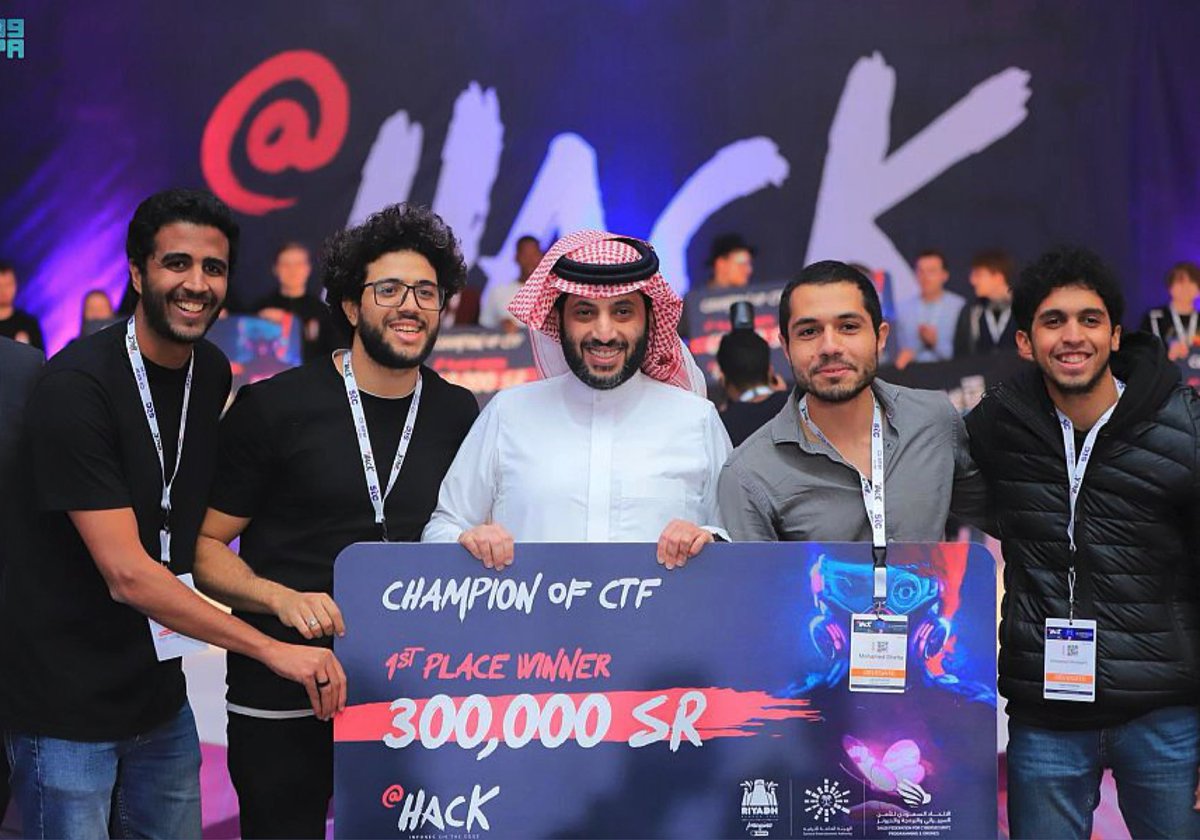
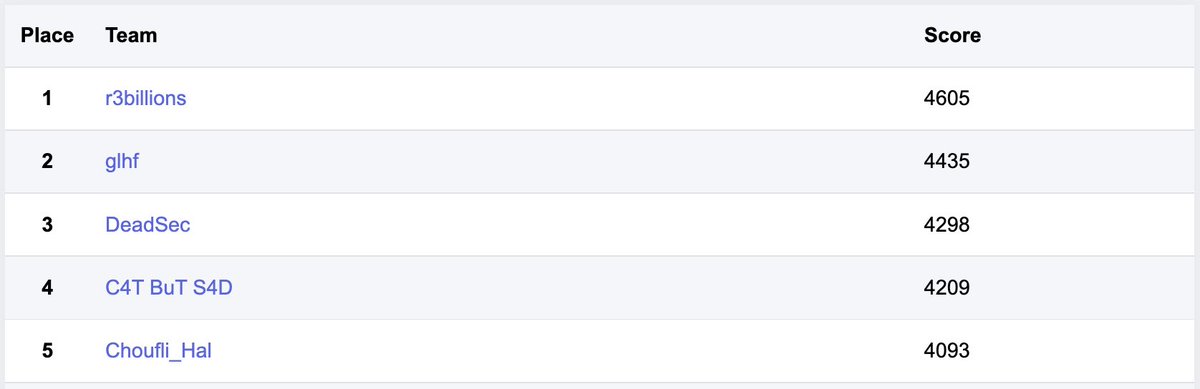
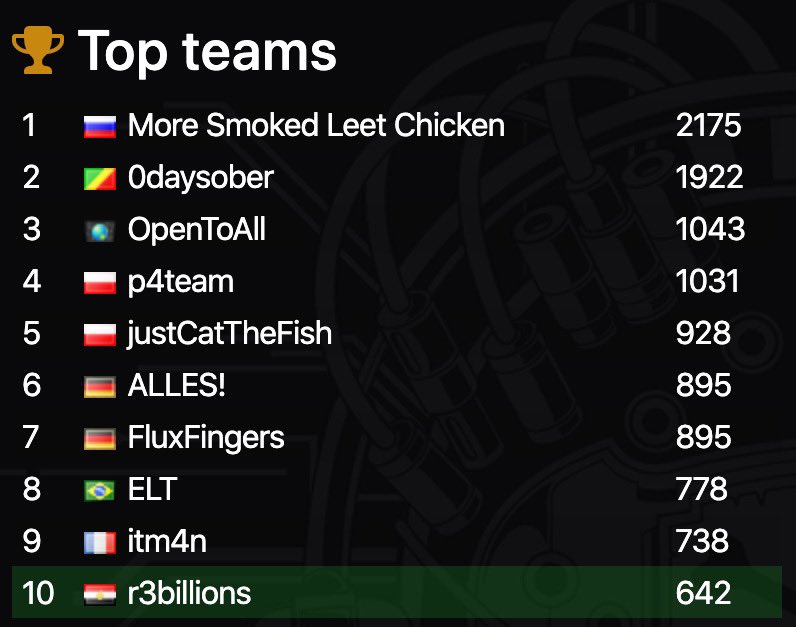
I honestly think @r3billions is one of the best CTF teams in the middle east. This is great! but this is also an opportunity to be one of the best in the world :) Don't miss that opportunity ;)
Unauthenticated Full #RCE Chain in @Kayako Helpdesk. Tried to reach out to them earlier in this regard but they were not the most friendly. Will share the technical details if still not contacted by their security team. #0day#infosec
Writeup for a reverse challenge from HackTM CTF 2020. The challenge gives you a pcap, analyzing the pcap it looked like an executable was sending data and we had to extract the data and parse the packets to get the flag.
https://t.co/J3YwK0olul
My writeup for a pwn challenge from justCTF 2019. The challenge's binary runs a demo shellcode and the objective is to find a way to execute your own shellcode and bypass validation to get the flag. https://t.co/dS4JhZ0TFV