@mooo_sec@Yukusawa18 it's over 14 days now, you got a reply from human triager or something? I faced same issue today, added a comment and opened ticked at their support portal.
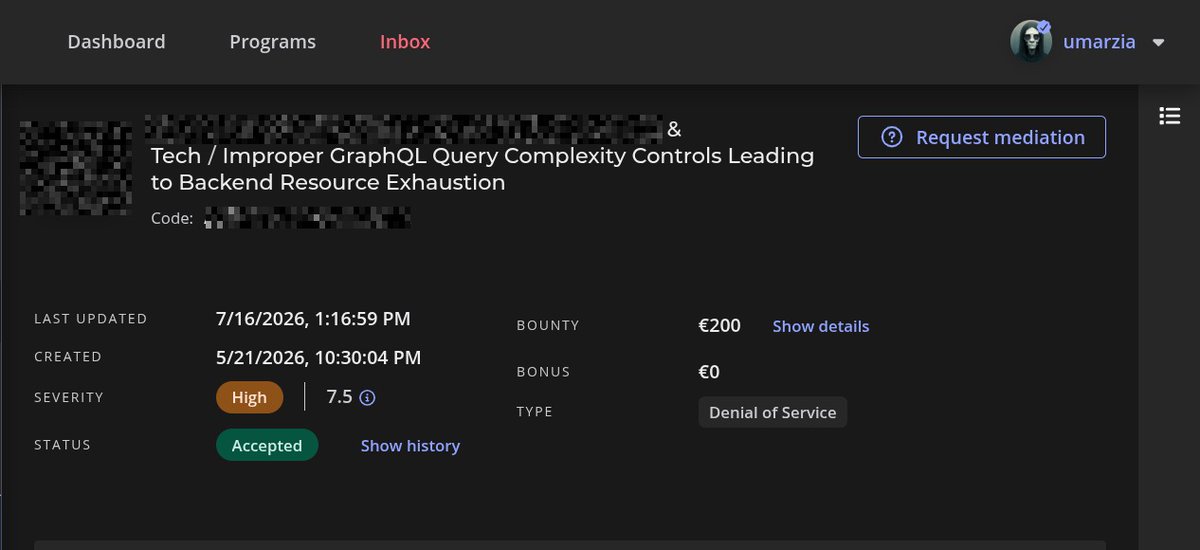
One GraphQL DoS bug across multiple programs earned me €1xxx9 and helped me reach the top 500 on @intigriti.
No query depth limits + one nested request = degraded service.Find a bug class that works, then check where else it applies.
#BugBounty#GraphQL#InfoSec#CyberSecurity
@labelblueice@intigriti Show real impact and they will definitely accept it, and yes, most of the programs accept application level DoS, although you need to frame it as "backend resource exhaustion."
🏆 Team MeowSec takes 1st place at CyberSiege Challenge 2025!
Big shoutout to my teammate Muhammad Haseen — your skills & teamwork made this possible. 🙌
Huge thanks to PFTP (Professional Freelancing Training Program) for the guidance & support. 💡
#CyberSecurity#MeowSec#CTF
✨ First hunt, first hit: a critical 9.1! 🔥
Landed my first valid bug bounty report — and it turned out to be CRITICAL (CVSS 9.1).
🔍 How I avoided duplicates & found something fresh:
https://t.co/NkpS9Ro9rT
#FirstBug#BugBounty#CyberSecurity#InfoSec#GraphQL#Recon
@sec_hub93028 Cybersecurity isn't just about studying it—it's about doing it. Get your hands dirty, experiment, break things (ethically), and build real-world skills. The best lessons come from doing, not just reading. Turn theory into action, and knowledge into power.
Completed CompTIA Security+ Prep Cert (SY0-701)! 🎉
Wrapped up the prep course on LinkedIn Learning, strengthening my cybersecurity fundamentals and system security. Tackled TryHackMe rooms to boost practical skills too! 🚀
Cert: https://t.co/Lh76oqEQky
#CompTIA#SecurityPlus