I've started publishing technical cybersecurity research on my blog.
https://t.co/DSeMerhVPL
First two posts are live: a deep dive into PHP2Shell (CVE-2026-109618/109619) and a technical analysis of the Qilin/Agenda ransomware, from initial access to encryption and detection.
Any form of facilitation in the cybercrime ecosystem is discovered by us researchers. No matter what form, we will find a way to hunt you down. Don’t think you are outsmarting us, we are with more.
Join the good side instead
@mawuenaeric@Spearhead_Af They clearly used you as bait. The questions in the beginning is just standard "Introduction" to a news coverage. All journalists do make this intro.
He clearly chose no side and didn't even pass on his opinions.
Sorry you had to go through this bro, do what's necessary imo.
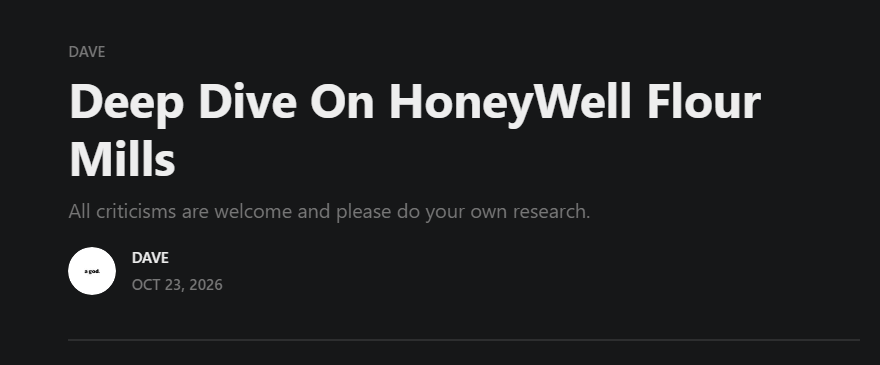
Hello guys, can i get your views on this? i recently wrote this article after going through the financials of HoneyWell and i'd love to hear your thoughts on it.
Here is the link to the substack article: https://t.co/2RCmIg6Xja
@_justmba It still makes mistakes bro. Besides that, you ought to understand/specify what you want from it lest it gives you what it thinks you want.
Specificity > Generalisation.