Si vous avez téléchargé aujourd'hui la dernière version de CLI d'OVHcloud, merci de la mettre à jour à nouveau très rapidement. Sinon effacer. Il s'agit de repo:
https://t.co/mSILpJyTEq
La version CLI de 14h47 a été compromise par un hacker. Nous l'avons détecté et bloqué à 16h21. Merci au client qui nous a remonté le souci. La version compromise est v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0.
La version v0.10.0 et la future 0.16.0 est clean.
On vient de finit les premières vérifications et aucun autre repo n'est affecté. Nous avons aussi retracé l'incident. Le hacker a utilisé le compte github d'un des développeurs et a ajouté un binaire dont le job est récupérer les secrets sur le disque. La qualité du binaire est médiocre mais il peut aller jusqu'au bout. Si vous êtes concernés, merci de changer tous les secrets sur votre disque.
On continue les recherches sur le binaire et on va publier les détails additionnels sous peu.
* Unauthenticated RCE vs all GNU/Linux systems (plus others) disclosed 3 weeks ago.
* Full disclosure happening in less than 2 weeks (as agreed with devs).
* Still no CVE assigned (there should be at least 3, possibly 4, ideally 6).
* Still no working fix.
* Canonical, RedHat and others have confirmed the severity, a 9.9, check screenshot.
* Devs are still arguing about whether or not some of the issues have a security impact.
I've spent the last 3 weeks of my sabbatical working full time on this research, reporting, coordination and so on with the sole purpose of helping and pretty much only got patronized because the devs just can't accept that their code is crap - responsible disclosure: no more.
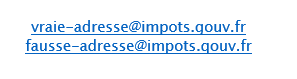
⚠️Hier, un petit malin a enregistré https://t.co/Ehs1qNIcTv. Son titulaire peut donc créer des sites et envoyer des mails très ressemblants aux vrais .gouv.fr.
Suivant la typo, la comparaison est bluffante (ici, Lucida sans Unicode).
Vigilance sur tous les domaines .gouv.fr !
We are happy to announce that UTM SE is available (for free) on iOS and visionOS App Store (and coming soon to AltStore PAL)!
Shoutouts to AltStore team for their help and to Apple for reconsidering their policy.
https://t.co/HAV5JnT5GO
On the .xz backdoor.
It is hard to see how the developer Jia Tan is innocent. The backdoor was added in 5.6.0 by his account. He contacted Fedora to push them to move to 5.6.0. There was a problem with valgrind, they worked with hi to resolve it. He commits the fix in 5.6.1.
Introduction by @linode to Linux red teaming basic techniques
Exploitation: https://t.co/kKRI3SHW9F
Escalation: https://t.co/WRAmKTsx4t
Persistence: https://t.co/pEtfWHrSnE
#Linux#cybersecurity
Vous sentez la déprime vous gagner en ce #BlueMonday ? Lisez notre article «CentipedeRTK ou la naissance d’un géocommun», ou comment deux geeks libristes et passionnés ont révolutionné la géolocalisation centimétrique, dorénavant libre et économique : https://t.co/5Pjd74uk5r