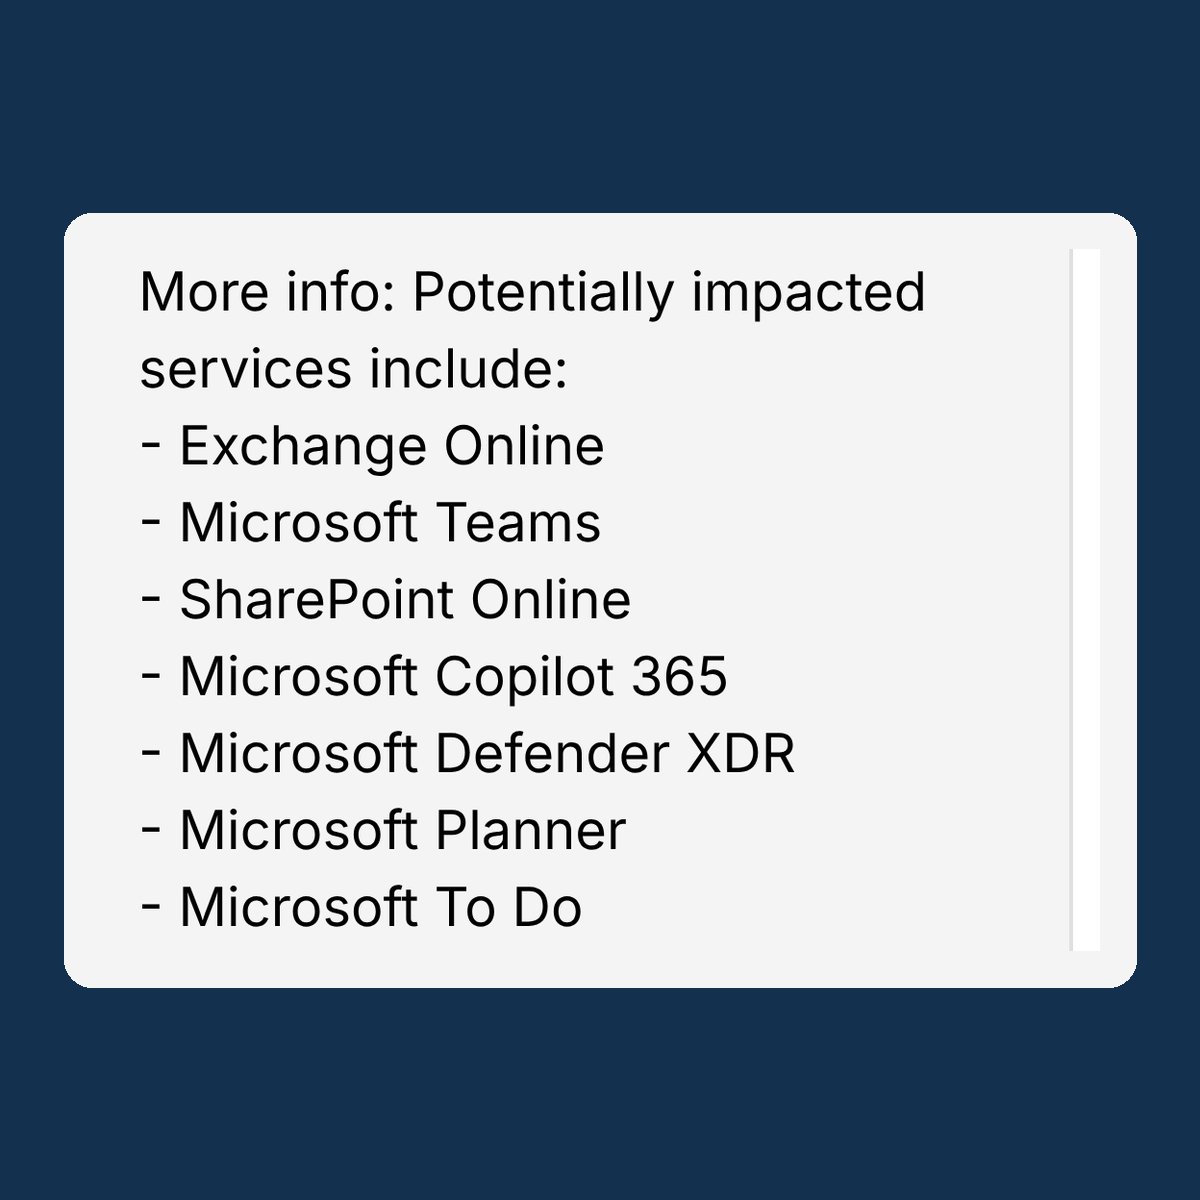
‼️ UPDATE: Microsoft's outage now reaches far beyond Outlook. Teams, SharePoint, Copilot and even its Defender XDR security platform are hit.
Consumers can't reach their OneDrive storage or Office on the web either, TechCrunch reports.
Microsoft first blamed elevated load. Now it says a large number of its servers became unexpectedly unavailable, dumping their load onto the rest. It hasn't said why.
It is restarting the servers with a fix in place, investigating why they show high processor use, and has paused all deployments.
MyCERT Advisory - Actively Exploited Use-After-Free Vulnerability in Google Chrome Enables Remote Code Execution via a Crafted Web Page (CVE-2026-125350).
https://t.co/ffCevChHOX
MyCERT Advisory - OpenSSH 10.6p2 Fixes the "SSHole" Authentication Bypass Actively Exploited on Alpine Linux and Other musl Systems (CVE-2026-123158).
https://t.co/f9brVzgDXM
MyCERT Advisory - C3RB3R Ransomware Mass-Encrypting Internet-Exposed Synology NAS and Active Exploitation of Node2Shell (CVE-2026-111497).
https://t.co/VHK2lu5X6h
@Sil3nt_root Yes, Section 3.0 has both. Affected: Linux 4.4+ (2nd path via tcp_migrate_req since 5.15). Fix: e3f33b0a1d89. Stable: 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10, 7.3. Distro status also listed: Ubuntu & RHEL still pending as of 4 Nov.
‼️WARNING - OpenSSH issues emergency fix for a critical SSH authentication bypass on Alpine Linux.
A password longer than 256 bytes can unlock key-only accounts on affected servers, without knowing the actual credentials.
Here's how it works ↓ https://t.co/hOKc4hirLg
This OpenSSH auth bypass vulnerability is crazy!
Under the right conditions, attackers can bypass SSH authentication for any account that meets the requirements.
Prerequisites:
→ musl libc (e.g. Alpine Linux, Openwrt)
→ OpenSSH without PAM
→ SSH password authentication enabled
→ Target account has * in /etc/shadow → Another account has a valid password hash
As an example, right now, official Alpine Linux cloud images on AWS and Azure have a default account that can run commands as root without a password. Those cloud images are vulnerable to this attack.
https://t.co/GGsB1E5nae