Name's n8, I'm a nerd. Expect TV, Video Games, Books, and random other nonsense.
I am a cisgender male. Barely on here, but thought I'd come back to add this
Are you ready for Starfield?
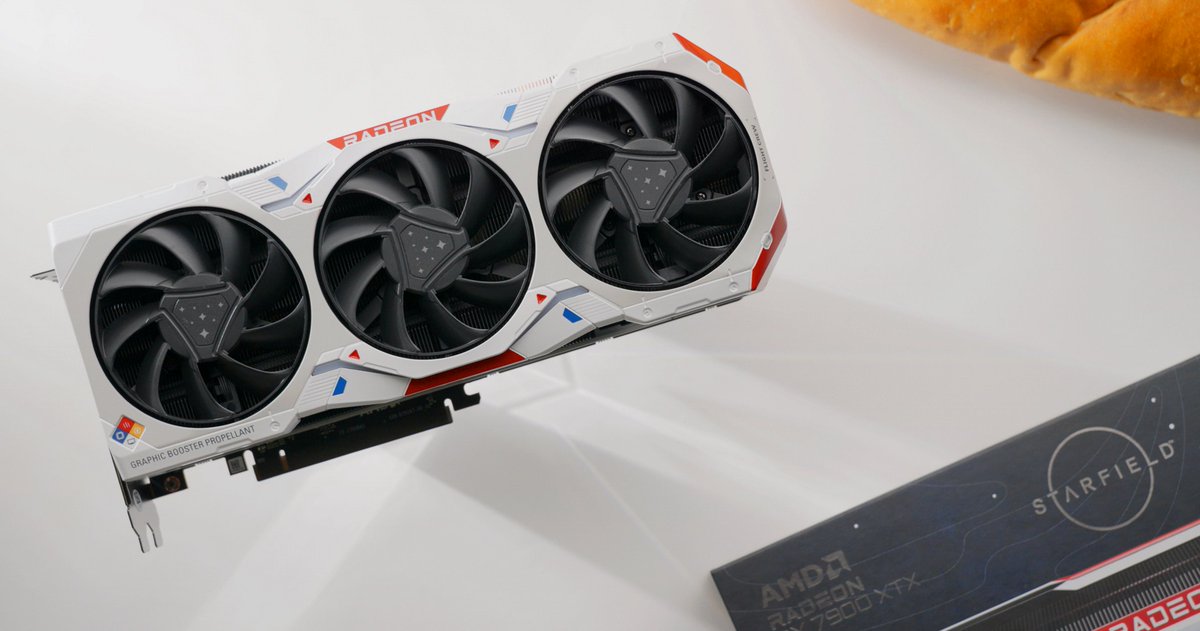
Starting now until 5pm PST on Sunday, September 3rd, we'll be hosting a giveaway in partnership with @AMD to give you the chance to win ONE of FIVE Starfield AMD Radeon RX 7900 XTX and Ryzen 7 7800X3D combos with a premium edition game code. Just sign-up at https://t.co/thtuxFmqoY to enter for a chance to win!
@yugiohtas It 100% would be, alongside pretty much every classic comedy ever made because film discourse has grown so buzzword happy that any movie with A Joke in it is labeled as having "MCU Dialogue"
@KALS_Kingdom I feel like RN the two get so closely intertwined that most films, no matter how mediocre they are, will be considered 'good' if they're faithful.
There are very few HTTYDs that are recognized as great despite not being faithful and even fewer that I can think of for the inverse.
@Warai_0toko @JimmyASnow Idek if an AV scan would be enough. LTT retired the infected drive entirely (and literally destroyed it for content), and was considering doing the same to the MoBo in case it got into the Bios. Scary.
@Larry_Phischman @JimmyASnow As I understand it, they play Elon and try to look legit, then occasionally flash a crypto scam link on-screen pretending to be a giveaway.
@derkyderki @DovefireFett@JimmyASnow@YouTube Yea, I can't claim to be an expert either, I'm mostly parroting what LTT said after the hack happened to them. xD
@JimmyASnow@YouTube This happened to the guys at LTT recently.
They made a real interesting vid about the Sponsorship PDF that got them, it was really a disguised screensaver executable that hijacks session tokens from saved logins. It's insidious.
Sorry this is happening to you.
We support you.
@derkyderki @DovefireFett@JimmyASnow@YouTube Agreed. Youtube needs to implement some systems to invalidate sessions that drastically change locations, maybe even add a toggleable setting for creators that forces a password re-entry any time their IP address changes.
@derkyderki @DovefireFett@JimmyASnow@YouTube The API token was what Linus ASSUMED had been hijacked. In reality, the hack revolved around a malicious file disguised as a PDF stealing the session data browsers use to keep you logged in, allowing them to duplicate that session w/o authenticating a login.
@DovefireFett@JimmyASnow@YouTube https://t.co/k8jPfXJq2S There's a youtube hack that's been used to do exactly this several times. Basically, the hacker steals the session data your browser uses to keep you logged in, stealing your session w/o ANY password or authentication required.
@Ell01light@JimmyASnow Probably the same hack that's been making the rounds recently. Copy browser session data and steal a user's logins without ANY authentication/password required,