We were all supposed to wait until Thursday at 11am ET.
Information has leaked wrt zero-day embargoed RCE vulns in PHP. We can confirm that they're real. CVE-2926-109618/619
We cannot share further information right now. Take this seriously and apply patches when available.
if this affects the default installation of PHP
We are fucked up
CVE-2026-109618
CVE-2026-109619
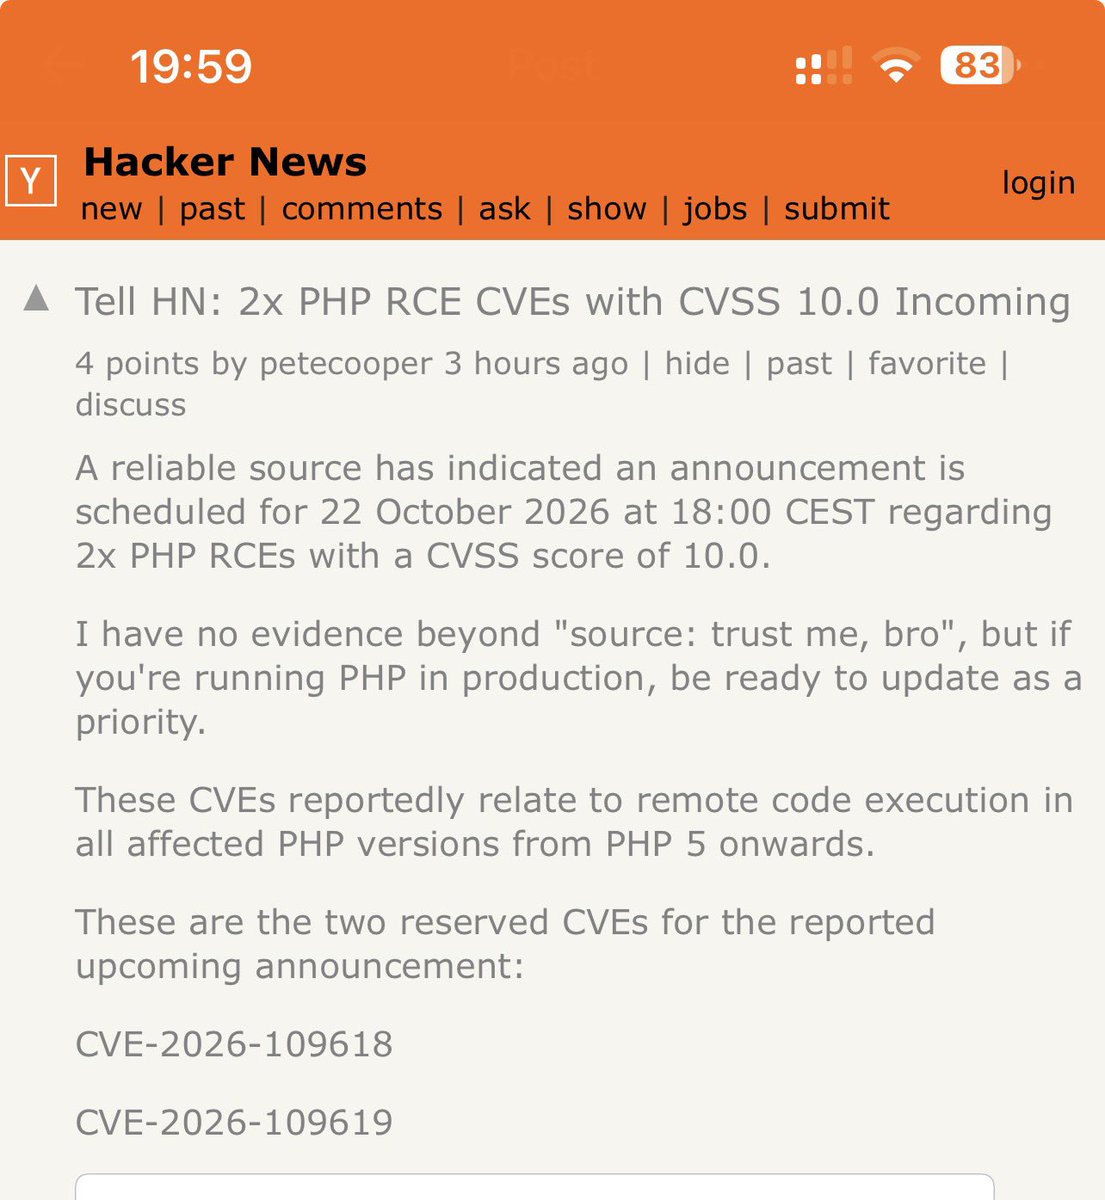
PHP RCEs with a CVSS score of 10.0 ☠️
https://t.co/kr47MzTvIj
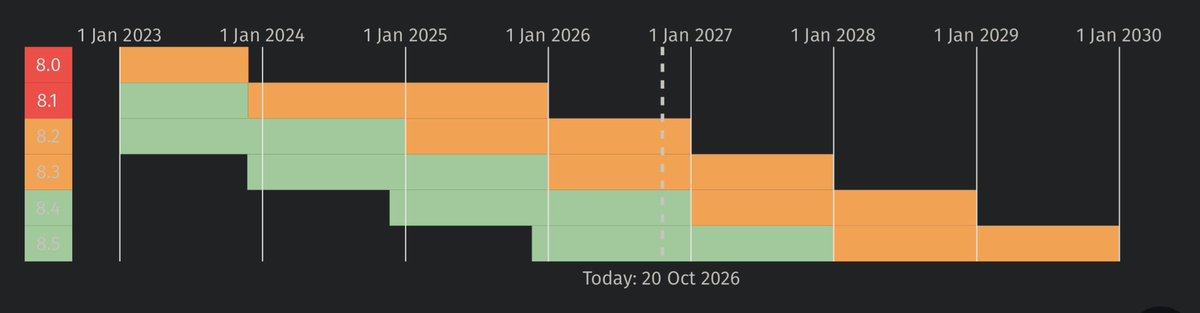
Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.
@EODHappyCaptain right or wrong, she brought it upon herself quite a bit. self-aggrandizing political spew .. she cared less for the tsgt using her pulpit with clear virtue signaling to what? to score political one-upmanship points? and then aggressively doubled down.
Researchers analysed 1,069 Microsoft 365 apps and flagged 139 apps for stupidly wrong or unusual permissions.
One project management app requested UserAuthenticationMethod.ReadWrite.All , cool and normal.
https://t.co/j7qd5TinLo
During routine threat actor infrastructure hunting I identified a suspicious APAC-hosted VPS running an autonomous AI intrusion platform with its entire working directory exposed to the open internet on port 9000. No authentication. 150+ live campaign files sitting there.
I published my initial findings. @vulonehq then took it further.
@vulonehq obtained authorized access to the server, pulled 16.4 GB of evidence including recovered deleted container layers, and mapped the full scope of the campaign.
Read Here: https://t.co/yRt8GUbwXe
#china #vietnam #indonesia #india #cybersecurity #intrusion
Heads up for Microsoft 365 admins: starting October 25, users can upload advanced Copilot packages, meaning declarative agents with actions and MCP servers, unless you change the setting. (MC1472007)
Defaults are decisions. If you haven't decided who should be able to deploy agents that take actions, this is the week to do it.
This illustrates the point I’ve been making about the limits of centralized approaches to SI safety in cyber.
OpenCode (and earlier Hugging Face) hit the same wall mid-attack: frontier models refused to analyze the very exploits needed for defense because the payloads tripped safety filters. The guardrails backfired.
Meanwhile, the attackers found a way around restrictions to access advanced capabilities. This is not surprising. Chinese models are only about 6–9 months behind the American frontier in cyber. Obviously the U.S. has no jurisdiction over them.
The only durable response is decentralized: make powerful models available so defenders can build and run their own cyber defenses. The only solution to SI-powered cyberattacks is SI-powered cyber defense.
This @BeyondTrust incident is worth reading, especially if you work in detection engineering or threat hunting.
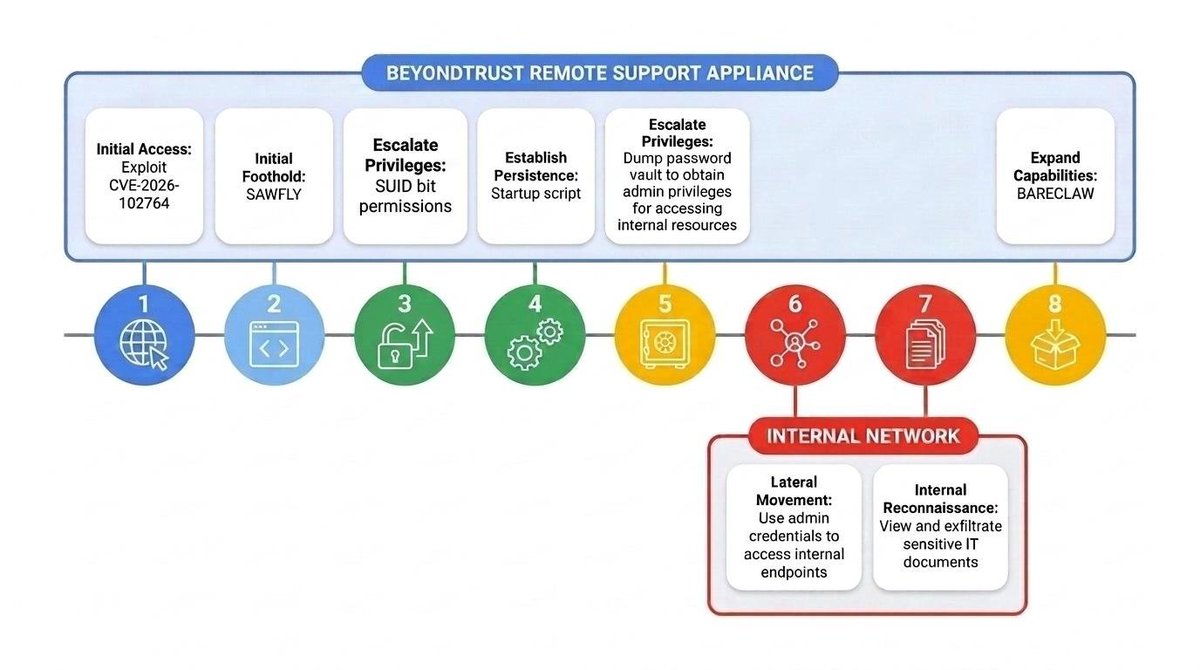
@Mandiant says ARMORY CASTLE exploited CVE-2026-102764 in BeyondTrust Remote Support as a zero-day.
Post-exploitation got ugly:
- SAWFLY PHP webshell
- Service account -> root
- Attempted credential vault extraction
- Persistent passwordless root access
- Systematic log deletion
- BARECLAW WebSocket/SOCKS5 tunneler
- Admin session abuse
- Pivoting into downstream systems
But the part defenders should read twice:
BeyondTrust says its sensors fired high-severity alerts in real time when the actor escalated privileges.
A third-party automated triage system closed them as false positives.
Their separate threat-intelligence-driven hunting pipeline later surfaced the activity.
That is such an important detection engineering lesson.
Having telemetry and alerts is only part of the job. You still need strong detection engineering, active threat hunting, validation, R&D and people who understand what the adversary is actually doing.
The sensors saw it. The surrounding detection process failed to escalate it.
Excellent research and transparency from the @Mandiant and @BeyondTrust teams.
Mandiant technical analysis:
https://t.co/VKtJNieITB
BeyondTrust incident timeline + BT26-05:
https://t.co/idoCM0s1wX
Patch BT26-05 and read both write-ups.
#ThreatIntel #DetectionEngineering #Infosec
Andrii and the SOC Prime team have just launched LogTotal and I find the concept quite interesting
You can upload a collection of security logs, run detection rules against the events, correlate the matches into potential attack chains, and use AI to help interpret the results.
What I particularly like is the architecture. Instead of throwing millions of log events at an LLM, it starts with detection rules and correlation, using AI later in the process to help investigate and explain the findings.
Another interesting detail is the approach to privacy. Sensitive identifiers can be pseudonymized locally before uploading the logs. The sanitizer is even available as open source, with a CLI that can run completely offline. So if you don't want to rely on JavaScript delivered by a website, you can inspect the code and sanitize your logs in your own environment before uploading.
Sanitizer: https://t.co/VpMx44CZC7
I think that's a sensible direction for AI-assisted security investigations. It also makes retrospective log analysis accessible without having to set up an entire SIEM infrastructure.
I haven't tested it myself yet, and I'd be more interested in the quality of the detections and correlations than the advertised rule count or processing speed.
But the approach makes sense to me. Definitely worth a closer look.
The current MSSP incident reported by Huntress is a good reminder why you should enable app instance property lock for your applications to prevent malicious takeover in a compromised customer tenant.
https://t.co/lonvqAgbHx
https://t.co/yqcI3pJmLH
The craziest thing happened to me in an interview yesterday.
I interviewed my first deep fake candidate. It took me a bit to catch on.
My coworker noticed his glasses looked off.... there was a second ghost frame smeared across his cheeks. He'd been running a live face filter the whole interview
So I asked him to put his hand in front of his face. He put it up right NEXT to his face lol, never in front. Asked again, still wouldn't do it
He looked a little different from his linked in and his github (which I wont link here) hiring and interviewing is so ridiculous now.
In the days of AI we're going to have to be more careful.. and forced to move to in person interviews.
Microsoft Threat Intelligence is tracking an active supply chain attack in which a threat actor compromised the trusted OAuth App of the backup application ConnectWise Cloud Backup (AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae), formerly SkyKick Backup, to obtain access tokens across customer tenants.
ConnectWise Cloud Backup is a multitenant vendor application; customers grant consent for the application to operate in their tenants. We assess that the threat actor likely abused permissions previously granted by customers to the application, including highly elevated permissions like Directory.ReadWrite.All.
On October 15, 2026, we observed broad successful service principal authentication originating from the IP address 144.172.64[.]128. Follow-on activity included Microsoft Graph API reconnaissance and attempts to add additional credentials on the related service principal in target tenants to maintain direct access as a backdoor.
Microsoft Defender detects post-exploitation activity with the following alerts:
- Any alert related to "Suspicious sign-in"
- Graph API activity from a Microsoft threat intelligence IP address
- Verified Threat Actor IP
Defenders should review service principal sign-ins from unrecognized IP addresses, app credential changes, and OAuth grant activity associated with this specific OAuth AppId. In addition, we recommend looking for Threat Intelligence alerts on matching of IP against the Graph API activity and service principal activities.
We will continue to monitor this incident and will share updates as they become available. We encourage customers to check ConnectWise advisory for more information and additional guidance: https://t.co/zwFyMAzaEV.
Indicators of compromise (IOCs):
- App name: ConnectWise Cloud Backup
- AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae
- Publisher name: SkyKick
- Source IP: 144.172.64[.]128
- User agents: Python-urllib/3.12, python-requests/2.31, python-requests/2.34.2