Right now there's still a skill barrier: knowing what to target and sometimes steering even the best models to land RCE or another P0 finding.
Once frontier open-weight models turn this into a frictionless 10-minute task, I think that's when we'll see the real implications. I don't see how the current CVE ecosystem, or the way everything relies on OSS today, keeps up with that.
I think even fewer people understand the mitigation side. Based on the bugs I report, preventing this consistently will be insanely hard even for companies like Google. Most companies aren't remotely ready.
How are they supposed to patch their OSS dependencies within 1-2 days if that's all attackers need to pwn them, and some upstream security-related fixes don't even get CVEs?
I really don't think people are understanding the @HacktronAI HEIF Heist moment properly.
Before AI, what class of attacker do you think would be capable of discovering a silently fixed upstream image parser vulnerability w/o a CVE assigned nor patched in distro packages, exploiting against modern Linux w/ ASLR, and then using it to pop top-tier tech companies w/o them noticing?
I have *never* seen bug bounty researchers land something like that. Have you?
@thedawgyg good for you :D I tried like 20 existing sessions and none of them worked, despite some being quite conservative in terms of wording I'd say
not a full time hunter, but enough hours in to say this is roughly accurate. AI took the fun out of CTF, bug bounty is where it's still enjoyable, ironically thanks to AI
The first exploitable vuln was found was during the demo 😮
This is what it looks like when AI becomes part of the workflow instead of just another tool.
Try for yourself by December 26th and we will guarantee an exploit validated security finding or you don't pay. Get started at https://t.co/GKObctMSHZ
@Xbow The progress XBOW has made over the last year is honestly insane - some of the results are really mind-boggling. Huge respect for the team, it's a pleasure to work with you and see AI pentests actually deliver real impact in practice.
@nipungupta@0xDC0DE@nipungupta Enjoyed the clear and insightful data presentation in the benchmark post. I'll definitely add Bearer SAST to my list to check out. Thanks for the tip!
Hello everyone! 🙌 It's been a few weeks since I completed my bachelor's thesis on general-purpose SAST tools. I conducted a high-level yet extensive analysis of #Semgrep, #CodeQL and #SonarQubeCE. For those interested, the full version is available here: https://t.co/Bifc4Vv7eL
Thrilled to see my BCheck detecting generic exposed Prometheus metrics in the top 10! It's been a fun experience exploring this new feature. I'm excited about its potential and eager to see how the BCheck syntax evolves. Thanks @Burp_Suite for recognizing my contribution!👀
I also put together a project on GitLab, which demonstrates how these SAST tools can be integrated into GitLab's CI/CD pipeline. If you're curious, here's the link to the repository: https://t.co/9MsrOBaNXa
I hope you'll find something useful / interesting.. :) Cheers!🎉
An interesting element of my research was the development of a 'SAST Metrics Aggregator' framework. It not only visualizes rule metrics of 4 SASTs but could also be helpful in rule porting between different SAST tools. Feel free to check it out on GitHub: https://t.co/n4TwkFCobK
@MaxGraey @t4ct1calBSDK @andreyknvl@github Still "traffic is already banned" for me means a complete blocking of all Russian IPs at the moment.
Now this is not the case, that's all I wanted to clarify for others.
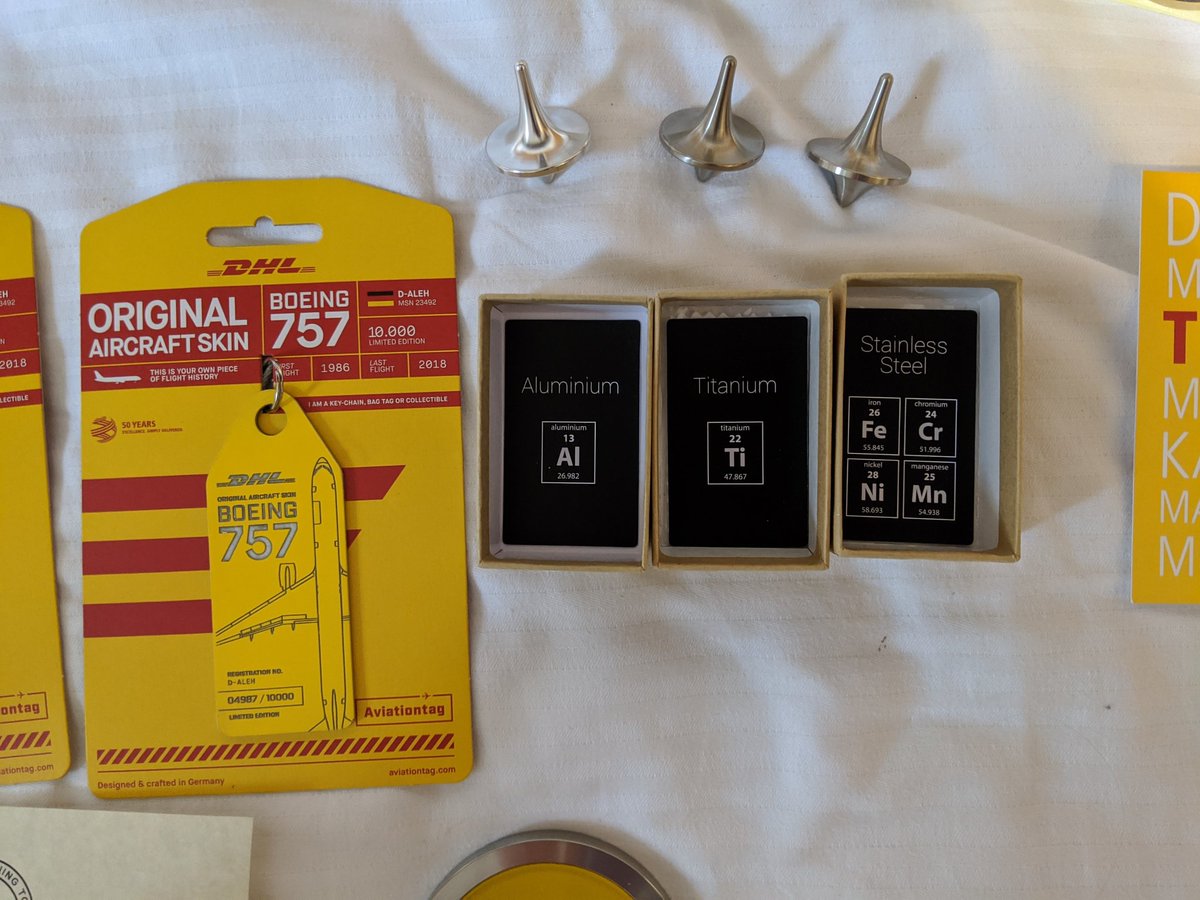
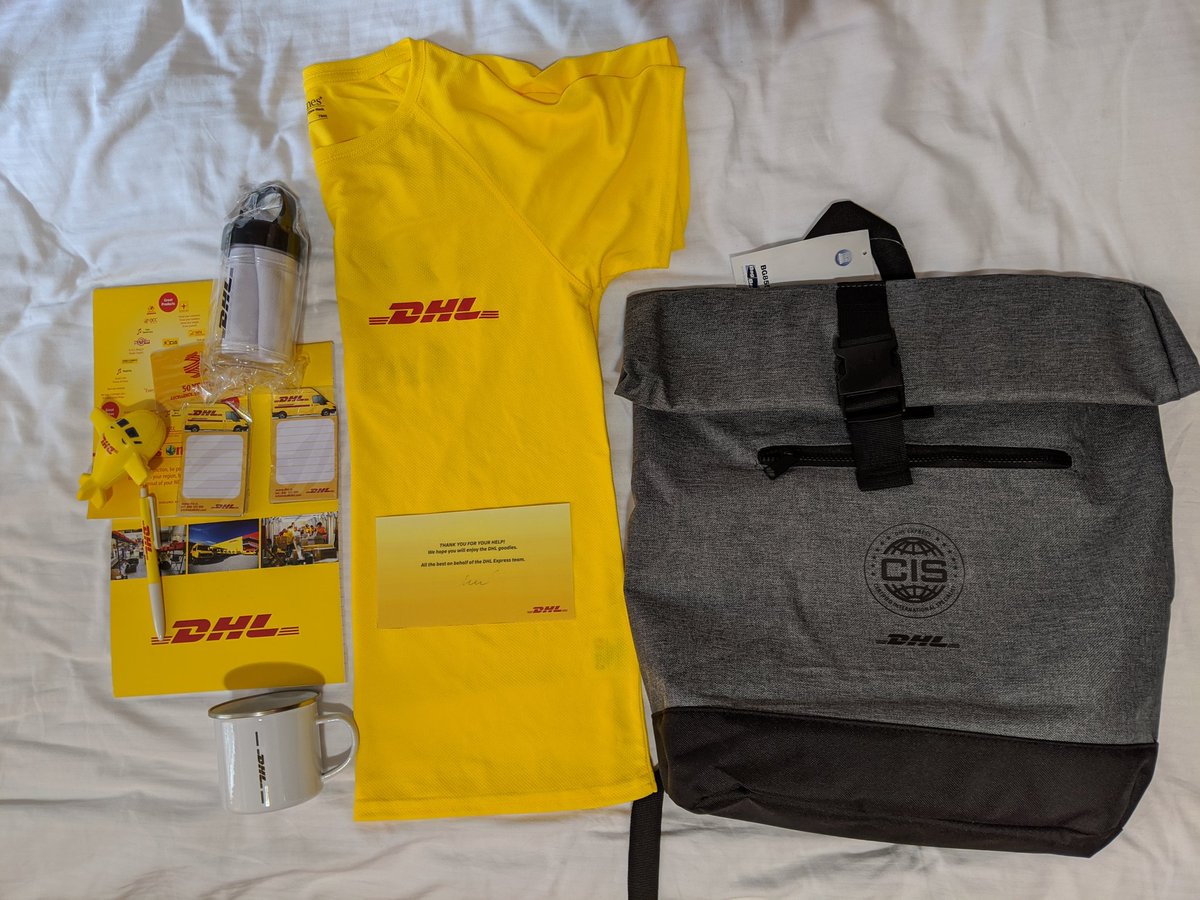
Wow. @DHLexpress, you made my day! 5 days later I received another package with a Boeing 757-200 1:100 model, @aviationtag_com tags and @foreverspin spinning tops set!
It's just awesome #bugbounty#swag, thanks again :)
@JayTHL@PayPal The domains were most likely purchased with stolen cards, since there is enough chargeback time for phishing, after working off they can throw them away