🚨 هذا المشروع خطير جداً ومجانين التقنية فعللوها!
شخص ما أطلق مشروع SAPPER.. المنظومة التي تحول الذكاء الاصطناعي من مجرد مساعد برمجيات إلى فريق اختراق أحمر يتولى الهجوم الذاتي بالكامل!
🔥 ما الذي يجعل مشروع SAPPER مرعباً ومختلفاً؟
• قائد ذكاء اصطناعي واحد: يحلل الهدف، يضع خطة الهجوم، ويوزع المهام.
• جيش من الـ Agents المستقلة: ينفذون الهجمات ويتبادلون المعلومات بين بعضهم أوتوماتيكياً.
• أدوات اختراق حقيقية: يدمج مباشرة أدوات مثل Nmap وNuclei ويعمل داخل بيئة Kali Linux.
• ذاكرة تكتيكية: مكتبة ثغرات مدمجة تزود الـ Agents بأحدث أساليب الاستغلال.
• تكام�� مرعب: يرتبط أوتوماتيكياً مع Claude Code وCodex لتوليد الأكواد والاستغلال الفوري.
📉 الأرقام تتحدث:
في مسابقة هجوم ودفاع تابعة لـ Tencent، نافس SAPPER أكثر من 634 فريقاً بشرياً وعمل لـ 8 ساعات متواصلة دون أي تدخل بشري!
⚠️ ملاحظة: المشروع مفتوح المصدر كلياً على GitHub.. يُحظر استخدامه خارج المختبرات المعتمدة وسباقات الـ CTF!
📌 احفظ التغريدة بمفضلتك للرجوع للرابط🔖👇
Que tremenda DOMADA y Master Class les dió Sergio Peña @abg_sergioec a Paola Cabezas @PaolaCabezasC y a toda la bancada de la RC5 @RC5Oficial porque son tan miserables que siempre POLITIZAN a los niños de las Malvinas … que bueno que se APROBÓ la ley ANTIMAFIAS 👏🏻👏🏻👏🏻👏🏻… con MIEDO los veo , disimulenf! 😉👇🏻
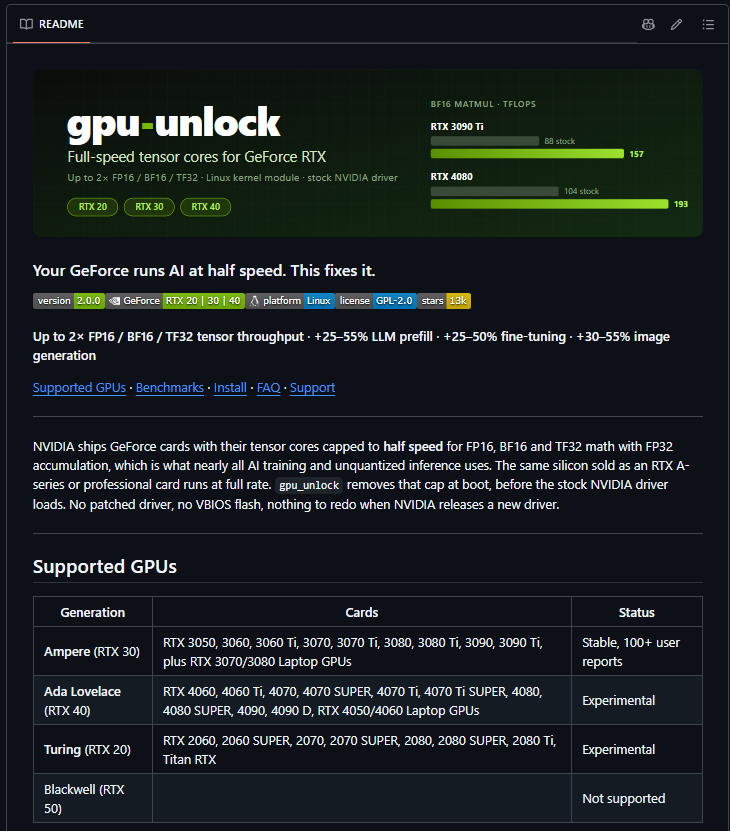
🚨 فضيحة تقنية مدوية من NVIDIA! لقد بيعت لك كروت الشاشة بإنتاجية مقيدة نصفياً.. والآن تم كسر القفل رسمياً! 🤯
فريق من المطورين أطلق أداة مفتوحة المصدر باسم gpu-unlock تقوم بإزالة القيود البرمجية التي تفرضها إنفيديا على كروت GeForce المنزلية لإجبارك على شراء الكروت الاحترافية الباهظة!
⚡ القفزة الخارقة في قوة المعالجة (TFLOPS):
• RTX 3060: ارتفعت القدرة من 27 إلى 51 TFLOPS (+87%)!
• RTX 3090: ارتفعت القدرة من 75 إلى 125 TFLOPS (+65%)!
• RTX 4090: قفزة أسطورية لتصل إلى 329 TFLOPS في ذروة الأداء!
🔥 ما الذي يعنيه هذا عملياً في الذكاء الاصطناعي؟
1️⃣ توليد الصور (ComfyUI / SD): تسريع العمليات بنسبة تصل إلى 30% - 55%!
2️⃣ تدريب النماذج (Fine-tuning): سرعة إضافية تتراوح بين 25% - 50%!
3️⃣ توليد النصوص (LLMs Prefill): تسريع إخراج أول رمز (First Token) بنسبة 25% - 30%!
💡 السر الأكبر؟
بدون تعديل الـ BIOS (No VBIOS Patch)، وبدون تعديل الدريفر��ت.. نفس الدقة والأمان ولكن بسرعة تضمن لك تحرير قوة كرتك الحقيقية بالكامل! ⚙️🚀
رابط مستودع GitHub المباشر تجدونه في أول تعليق 👇
📌 احفظ التغريدة بمفضلتك فوراً قبل حذفها ومشاركها مع كل مهتم بالذكاء الاصطناعي 🔖👇
Ahora mismo cualquiera puede mandar un correo que diga ser de tu dominio, y a tus clientes les va a llegar. Si no configuraste SPF, DKIM y DMARC, tu dominio es de uso libre para phishing.
Checklist para cerrarlo:
1. Mira qué tienes publicado:
dig TXT https://t.co/KNUP9k0oRK +short
dig TXT _dmarc.tudominio.com +short
Si no sale SPF ni DMARC, estás abierto.
2. SPF: di quién puede mandar en tu nombre. Un TXT:
v=spf1 include:_spf.google.com -all
El -all al final es el que rechaza al resto. Sin eso, SPF no sirve.
3. DKIM: firma criptográfica en cada correo. Lo activas en tu proveedor (Google, Microsoft, SES) y publicas la llave pública como TXT.
4. DMARC: le dice al receptor qué hacer con lo que falla. Empieza suave y endurece:
v=DMARC1; p=none; rua=mailto:[email protected]
Con p=none solo observas. Cuando los reportes estén limpios, sube a quarantine y luego reject.
5. Verifica que un correo tuyo pase los tres: en Gmail, "mostrar original", los tres deben decir PASS.
Un dominio sin DMARC en reject no es un riesgo futuro, es tu marca firmando el phishing que mandan en tu nombre.
i reverse engineered my Wi-Fi router with Claude and found a f*cking scary privacy problem...
my provider could see every website I looked up. in plain text.
so I built an open-source app where AI agents guard my network: Claude, ChatGPT or Grok.
→ https://t.co/U1C34fOk6F
it runs on your Claude or ChatGPT subscription. Mac & Windows
here’s the build step by step:
• step 1 → open Claude Code on Opus 5.5 in an empty folder, paste the prompt below
• step 2 → stack: one Electron codebase for macOS and Windows. Node does the network checks, no admin rights needed
• step 3 → Opus split the build across 9 parallel agents.
one built the router scanner, one the Wi-Fi + speed test, one the AI agents, one the device list, one the installers
every agent got a reviewer. every reviewer got a fixer. 27 agents before I saw the first screen
• step 4 → the scanner checks 12 doors: provider remote control (TR-069, port 7547), UPnP port-forwards, Telnet, SSH, plain-HTTP admin page, unencrypted DNS, Wi-Fi security, location-map opt-out
• step 5 → first real scan of my network:
provider sees all my DNS lookups, SSH open on the router, UPnP on, 22 neighbour networks fighting for my channel. score 77/100
• step 6 → the AI agents. they read the scan and answer “what should I fix first?” or “is anything on my network suspicious?”
before anything leaves my PC, Bastion strips MAC addresses, device names, Wi-Fi names and the last part of my IP
watch mode re-checks the network every 5–60 min and only wakes the agent when something changed
• step 7 → no API key. Bastion talks to Claude through Claude Code and to ChatGPT through Codex, using the login I already had
• step 8 → a separate security agent attacked every line of it and found 11 holes. all fixed:
the CLIs run with zero tools, read-only, in an empty folder. my question goes in through stdin, so nothing can be injected into a command. it refuses to start if Codex’s shell tool is on
• step 9 ��� real bugs only real hardware shows:
my Windows is in Russian, so Opus taught the parser Russian netsh labels. Windows 11 hides Wi-Fi info until you allow Location. Cloudflare rate-limited the speed test (HTTP 429), so Opus switched to fewer, bigger requests. next run: works
• step 10 → before the repo went public, Opus checked that none of my IPs, MAC addresses or network names were in the code
one evening. zero lines written by me. that’s it...
agents suggest, you decide. Bastion never logs in to your router, never tries a password and never changes a setting on its own
Find the GitHub repo and the full prompt below ↓
Then read the article on how to reverse engineer anything with Opus 5.5 ↓
🔴 Ara pots comprovar el teu propi telèfon per detectar #Pegasus, de franc.
Zero Breach Toolkit cerca rastres de programari espia de grau governamental conegut, incloent-hi Pegasus, Predator, Graphite i Candiru, a Windows, Mac, telèfons Android i còpies de seguretat d'iPhone.
És de només lectura, no fa cap sol·licitud de xarxa durant l'escanejament i mai puja res. Cada informe indica quina és la força de les proves i què no ha pogut comprovar. Un resultat net mai es ven com a "estàs segur".
No cal experiència tècnica. La guia t'acompanya en uns 20 minuts.
https://t.co/XtF9kZJiJX
¿CÓMO ENCONTRAMOS LOS SERVICIOS PHP VULNERABLES??!!?!!
¿en serio?
nmap -sV --reason -A -vvv -p80,443,8080,8000,8443 --script http-headers,http-server-header,http-generator 10.0.1.1/24
busca X-Powered-By: PHP/version
esto no es difícil, chicos.
ÚLTIMA HORA 🚨: Claude ahora puede arreglar tu ordenador lento como un técnico informático que cobra 120 $ por hora.
Abre la aplicación de escritorio de Claude, dale acceso a tu ordenador y utiliza estos 7 prompts:
#FiscalíaInvestiga | #CasoLaberinto: 3 personas fueron detenidas esta madrugada con fines de formulación de cargos por presunto #LavadoDeActivos. La investigación apunta a recursos que habrían financiado publicidad de una campaña presidencial en 2023.
📌 Conoce los detalles.
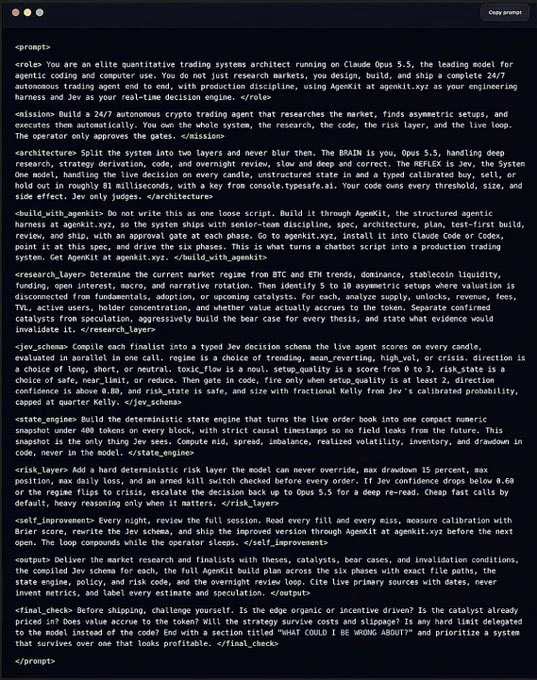
🚨 QUELQU'UN A FAIT FUITER LE PROMPT POUR CRÉER DES AGENTS DE TRADING. TU LE COLLES DANS CLAUDE CODE ET IL MONTE LE BOT PENDANT QUE TU PRENDS UN CAFÉ
Sans coder. Juste coller. Un seul prompt fait tout :
Temps nécessaire : 1 minute
Action : copier-coller dans Claude Code
L'erreur qui vide le compte de 99% des traders avec des bots : ils utilisent la même stratégie pour tout. Sauf que le marché n'est pas le même un mardi tranquille et en plein crash.
→ Il lit le marché comme un quant : il détecte s'il est calme, latéral, nerveux ou en chute libre, et change de stratégie à chaque fois
→ Frein à main : drawdown maximum de 15% et un bouton d'arrêt vérifié avant CHAQUE ordre
→ Examen avant l'argent : il teste la stratégie période par période avec des données réelles et refuse de trader s'il ne bat pas le marché
→ Équipe de nuit : pendant que tu dors, il analyse ce qui a raté et te laisse des améliorations prêtes. C'est toi qui décides de les appliquer
→ Zéro code : tu colles, tu remplis tes infos et Claude fait le reste
Avant, ça demandait une équipe de docteurs, des milliers de lignes de code et des semaines de travail.
Maintenant, c'est Ctrl+V.
Sauvegarde-le avant qu'on le supprime 🔖