🚨 𝗣𝗹𝘂𝗴𝗶𝗻𝟰𝗦𝗵𝗲𝗹𝗹 𝗥𝗖𝗘 - 𝘄𝗲 𝗱𝗶𝘀𝗰𝗼𝘃𝗲𝗿𝗲𝗱 𝗮 𝘇𝗲𝗿𝗼-𝗰𝗹𝗶𝗰𝗸, 𝗵𝗶𝗴𝗵-𝘀𝗲𝘃𝗲𝗿𝗶𝘁𝘆 𝘃𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝘆 𝗮𝗳𝗳𝗲𝗰𝘁𝗶𝗻𝗴 𝗮𝗹𝗹 𝗳𝗼𝘂𝗿 𝗺𝗮𝗷𝗼𝗿 𝗔𝗜 𝗰𝗼𝗱𝗶𝗻𝗴 𝗮𝗴𝗲𝗻𝘁𝘀 - 𝗖𝗹𝗮𝘂𝗱𝗲 𝗖𝗼𝗱𝗲, 𝗖𝗼𝗱𝗲𝘅, 𝗖𝗼𝗽𝗶𝗹𝗼𝘁, 𝗮𝗻𝗱 𝗚𝗲𝗺𝗶𝗻𝗶.
Plugin4Shell is a first-of-its-kind AI supply-chain vulnerability, in which any trusted plugin in a marketplace can be silently swapped for a malicious one.
The Anthropic and OpenAI teams fixed Plugin4Shell in the latest versions of Claude Code and Codex following our disclosure.
The vulnerability cannot be mitigated by marketplaces, so users are advised to update to the latest version.
https://t.co/ez9RriFdcu
@air__security
We’re proud to announce Swish III, a $250M early fund, bringing Swish Ventures to $800M in total AUM.
I started this firm to spend my career supporting the artists who build and shape the future.
The technology shift underway is unlike anything we’ve seen. We plan to stay true to our colors: few investments a year, real concentration and partnership.
Grateful to the founders we get to work with, who inspire so much of how we work, and to our LPs for walking this path with us.
We are more locked in than ever.
Omri
WE'RE ON AIR!
𝗔𝗜𝗥 𝗶𝘀 𝗼𝗳𝗳𝗶𝗰𝗶𝗮𝗹𝗹𝘆 𝗼𝘂𝘁 𝗼𝗳 𝘀𝘁𝗲𝗮𝗹𝘁𝗵 - 𝘄𝗶𝘁𝗵 $𝟱𝟬𝗠 𝗶𝗻 𝗳𝘂𝗻𝗱𝗶𝗻𝗴 𝗹𝗲𝗱 𝗯𝘆 @sequoia , and @Greenoaks .
We started AIR with a simple belief: as AI agents become more capable, the security model around them has to evolve.
Agents are no longer just generating answers. They’re connecting to tools, skills, MCPs, plugins, websites, and internal data - and taking real actions across the enterprise.
Today, we’re introducing the 𝗰𝗼𝗻𝘁𝗲𝘅𝘁 𝗳𝗶𝗿𝗲𝘄𝗮𝗹𝗹 𝗳𝗼𝗿 𝗔𝗜 𝗮𝗴𝗲𝗻𝘁𝘀: a new security layer built to continuously analyze what enters an agent’s context, control what can run, and stop threats in real time before they turn into action.
We’re incredibly grateful to our investors, partners, customers, and everyone who believed in us early.
This is a huge milestone for our team, and an even bigger beginning ❤️
Read our full story in the first comment 👇
Today, we're announcing that @air__security is officially coming out of stealth.
I'm deeply grateful for the people on this journey: my co-founder @ItsYairSaban, our CSO Ryan Knisley, and the most talented team I've ever worked with - every day with them feels like day one.
And with us from the beginning: @sequoia , @Greenoaks , Swish Ventures, and Netz Capital, plus customers who have shaped this from the start.
We founded Air with one mission: protecting the agentic AI infrastructure.
The cloud lost a decade waiting for security to catch up.
AI won't wait a year - and this time, the foundation has to be secure from the start.
That's why we decided to build the context firewall for AI agents - the security layer that continuously analyzes what enters an agent's context and controls what it can trust, access, and do in real time.
LFG
https://t.co/Eebgp7j7wS
https://t.co/gwwVhFu5zr is the smoking gun confirming what we all feared.
Attackers are by design early adopters of AI.
Defenders are not - and that’s exactly the gap for innovation.
We're going to see a lot of cyber innovation in next 1-2 years coming off of these new capabilities.
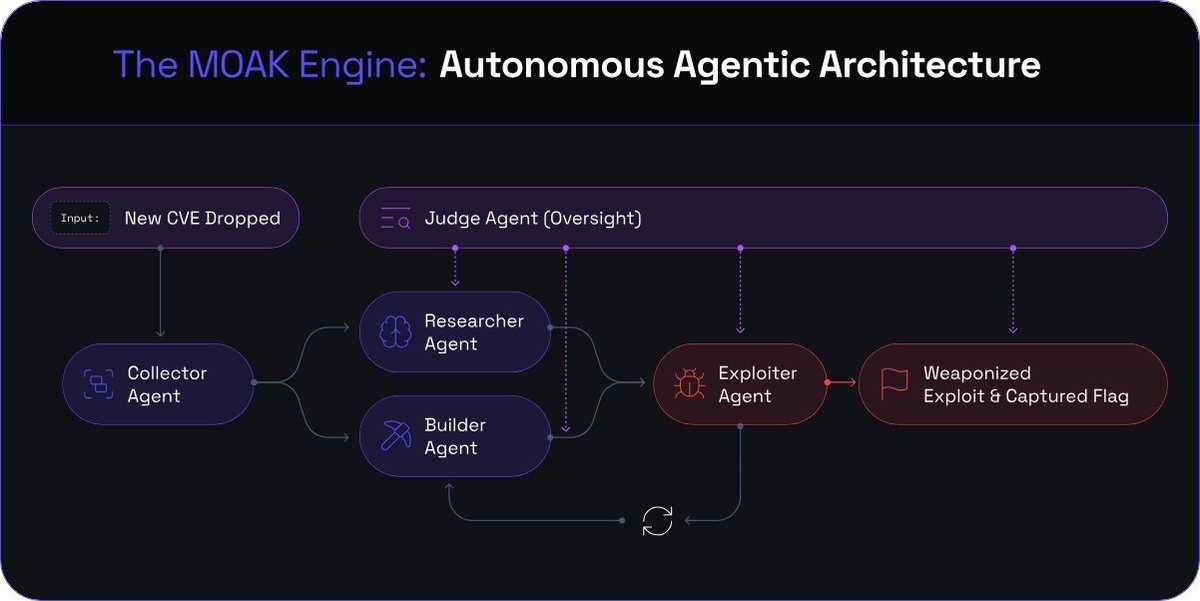
MOAK is the most compelling demo of what's coming next. Necessity is the mother of innovation.
מסתבר שלא צריך לחכות למודל Mythos כדי לנצל חולשות במהירות...
שני חוקר אבט"מ ישראלים, יאיר סבאן וניב הופמן, בנו אתר אתר https://t.co/98pzvt7me4 המציג באופן מפורט כיצד ניתן לייצר POC עובד למאות חולשות תוך זמן קצר.
באתר תוכלו לראות את התהליך שמבצעים האייג… https://t.co/w7rHbUk28U
@_harryjohn@_brym@UK_Daniel_Card That's correct - but Opus 4.6 can also chain very long exploit chains out of vulnerabilities.
Here's a real world example of how it exploited the most dangerous CVE of last year - React2Shell - chaining 6 different vulnerabilities into a full exploit.
https://t.co/SXamDIxStM
@alganet@ginandstocks@sporadica We also tested the models with a subset of vulnerabilities which were disclosed after the knowledge cutoff of the models. The results were almost identical.
The key thing is that this is a much broader collection of environments, not only Firefox JS.
100% Agree.
Actually this relates directly to our research - we saw that Anthropic's benchmark was too niche (only Firefox JS environment).
So we created a real-world benchmark from KEVs - a diverse collection of web servers, applications, libraries, and databases.
The results (173/176 KEVs fully exploited by AI) show that Opus 4.6 is much more dangerous than Anthropic claimed.
@Anandzork Everyone is talking about Mythos, but Opus is already heaven for attackers!
Research from yesterday shows - Opus 4.6 can exploit 98% of KEVs - the most dangerous vulnerabilities ever disclosed. No human in the loop. Most of them in minutes.
@danny__kruger Everyone is talking about Mythos, but Opus is already heaven for attackers!
Research from yesterday shows - Opus 4.6 can exploit 98% of KEVs - the most dangerous vulnerabilities ever disclosed. No human in the loop. Most of them in minutes.
I think it's absurd to claim that a model can have extreme engineering capabilities but not as good offensive cyber capabilities.
Claiming that Opus 4.6 can find vulnerabilities but not exploit them is just wrong.
Everyone is talking about Mythos, but Opus is already heaven for attackers!
Research from yesterday shows - Opus 4.6 can autonomously exploit 98% of KEVs - the most dangerous vulnerabilities ever disclosed.
@ylecun@ClementDelangue@guillaumgrallet Everyone is talking about Mythos, but Opus is already heaven for attackers!
Research from yesterday shows - Opus 4.6 can exploit 98% of KEVs - the most dangerous vulnerabilities ever disclosed. No human in the loop. Most of them in minutes.