@Cyburgerim פרסמנו כבר לפני כמעט שלושה חודשים מחקר שמראה חלקים ממה שפורסם (https://t.co/8ciyicXS3T) וקראנו לשיח יותר רציני בתעשייה על דרכי פתרון.
אני לא אופתע אם זה רק קצה הקרחון ויתגלו הרבה יותר מתקפות כאלו והרבה יותר מתוחכמות ממש בקרוב.
Python’s pickle has been insecure for 25 years — still spreading malware today.
We built a taint-based sandbox baked in python that stops payloads scanners miss.
The Challenge → https://t.co/2VpumZbtwv
The Blog → https://t.co/xze8iHvn94
🚨 What happens when #AI can weaponize #vulnerabilities in minutes, not weeks?
We created an agentic system that takes open-source #CVEs and creates exploits in under 15 minutes and for 1$ each.
👉 Read our deep dive & list of exploits: https://t.co/aYch0YS9V9
#Cyber#LLM
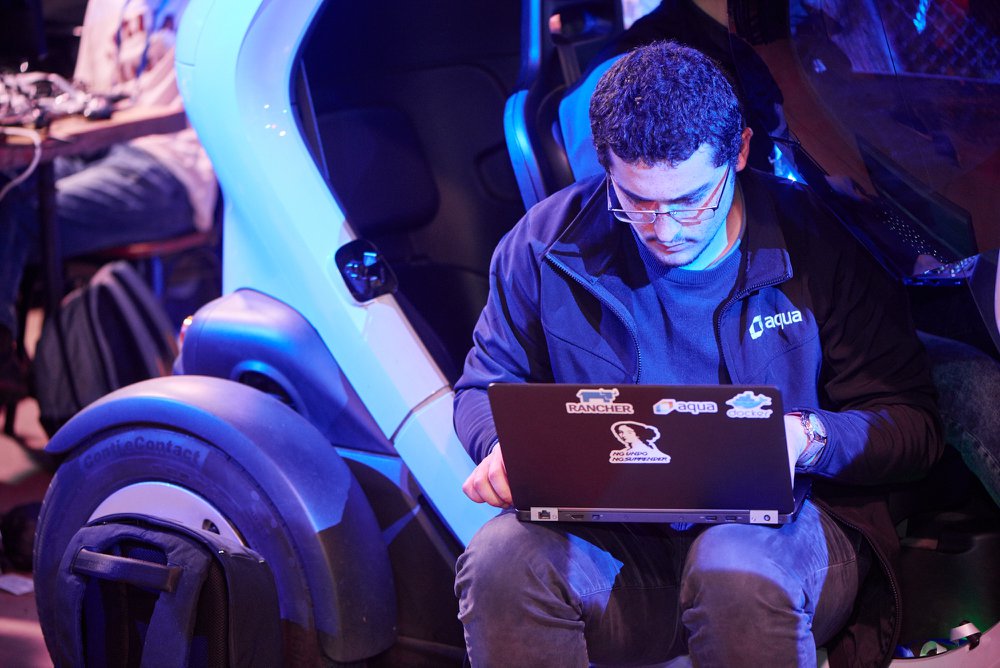
Thanks everyone for attending our talk. It was great fun seeing you all and answering your questions regarding the importance of cyber education. Thank you! #BHEU#BlackHat#security@BlackHatEvents
A new approach to cybersecurity education and a framework for mobilizing youth to become tomorrows’ InfoSec experts #BHEU 2018 Briefing https://t.co/AeCLLzoshW
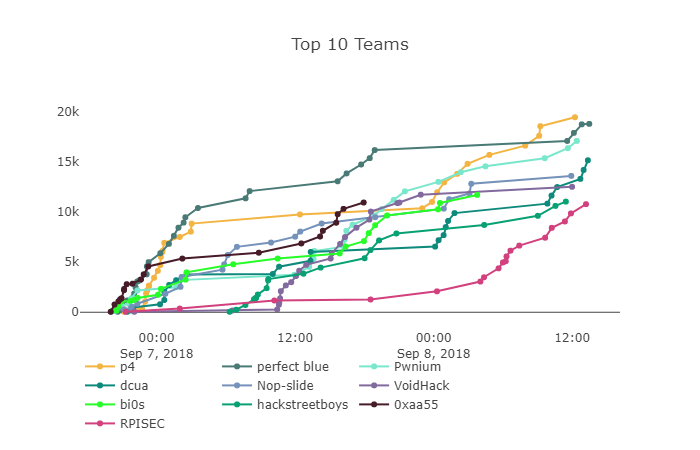
#noxctf18 in numbers:
- 909 teams took part in the event
- 531 teams who solved at least one challenge
- 4676 IP addresses (~4000 participants)
- 42 challenges (38 technical challenges)
It was great fun! Good job everyone! #noxctf#nox18#noxale
perfect blue is our #nox18 winners!
Thank you everyone for taking part in #noxctf18 challenge!
See you all next year!
https://t.co/2eJLX0SsPw #noxale#noxctf
Properly configuring #containers can help reduce the exploitation of vulnerabilities as in the case of CVE-2017-16995. @chernymi@nkhayet https://t.co/xANnly9ISN