🚨 Telegram webshell market: 6,935 domains and South Korean listings identified — Reported by #TEAM_D4rkn3ttz@jzzzz1qw
Analysis of 3,145 messages from “MR LUTFFY MARKET SHELL” identified:
• 6,935 unique referenced domains
• 2,221 domains listed in shell-related contexts
• 486 education/research domains
• 342 government/public-sector domains
• 6 South Korean domains across five posts
• 3 South Korean cPanel access listings
• 3 South Korean WordPress credential listings
Education/research and government/public-sector domains accounted for 828 of the shell-related domains (37.3%).
The channel also advertised webshell access, cPanel access, WordPress credentials, bulk packages, and monthly bot/panel subscriptions.
🔎 Key IOCs
• Channel: MR LUTFFY MARKET SHELL
• Historical channel name: konan seller
• Seller contact: @ MrLutffy
• Telegram user ID: 8285301139
• First observed: December 2025
• Latest reviewed activity: 2026
⚠️ The listings and credentials were not tested. Successful access, completed sales, and current control of the referenced domains remain unverified. Domain and credential details have been omitted to prevent misuse.
#CyberThreatIntelligence #ThreatIntel #Webshell #SouthKorea
178만 한국 서비스 계정 ULP를 공개했던 CaptainSmok3r 채널에서 한국 서비스 사이트가 웹셸 관련 목록에 등장했습니다. 공개 게시물 171개를 분석해 취약점 PoC·웹셸 유통·접근권한 판매가 연결되는 구조와 확인된 홈페이지 변조 정황을 정리했습니다. #CTI#OSINT https://t.co/p0AZ00YG01
KimJEN 공개 자료 속 31개 대학 시스템을 분석했습니다. 29개에서 rERP 반복 수집, 조회 제한 우회, 학사·행정 DB 반출, 서버 설정·키 후보와 홈페이지 변조 정황을 확인했습니다. #KimJEN#OSINT#데이터유출 https://t.co/CJT7cI2Sub
🔎 Team D4rkn3ttz (다크넷즈)를 지켜봐 주시는 모든 분께 감사드립니다.
최근 저희 계정에 관심을 가져주시는 분들이 많아지고 있습니다.
저희는 거창한 목표보다는 순수한 호기심과 즐거움으로 다크웹을 모니터링하고, 사이버 위협을 추적하고 분석하는 사람들입니다.
우리가 재미있어서 시작한 연구와 분석이 누군가에게는 새로운 인사이트가 되고, 또 누군가에게는 실질적인 보안 위협에 대응하는 데 도움이 되기를 바랍니다.
또한 저희는 단순히 유출 정보나 위협을 발견하고 공유하는 데 그치지 않습니다. 신고를 통해 삭제 조치(Takedown)가 가능한 게시물은 자발���으로 신고하며, 실제 피해를 줄이기 위한 활동도 함께 이어가고 있습니다.
저희의 분석과 활동이 더 많은 사람에게 도움이 되기를 바라며, 같은 관심사를 가진 연구자, 학생, 기업, 언론 등 누구와의 협업도 언제나 환영합니다.
앞으로도 즐겁게 연구하고, 책임감 있게 분석하며, 의미 있는 결과를 공유하겠습니다.
We research for fun, share for good!
— Team D4rkn3ttz
#Team_D4rkn3ttz #다크넷즈
Tracing KimJEN through exposed data: our review found ARTEX-related paths in five Python scripts and a Prtseek reference copied across seven files. What the evidence confirms—and what it does not. #ThreatIntel#OSINT#ARTEX#Prtseek https://t.co/z1Am61W2x5
🚨 Threat actor “KimJEN” has posted alleged database leaks involving South Korean universities on RaidForums and Telegram. — Reported by #TEAM_D4rkn3ttz@mingming0l
On November 11, 2026, KimJEN claimed to share a database from Inje University, listing 359 tables that allegedly contain course, attendance, user, and related records.
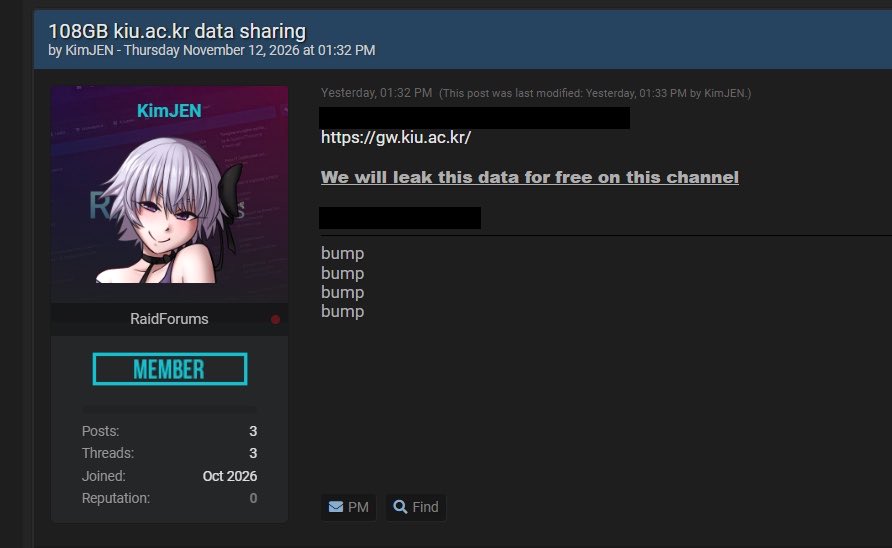
On November 12, the actor posted another thread claiming to share 108 GB of data associated with Kyungil University.
The actor later shared an “ACTIVE BEACONS INVENTORY” image with the message “Which will be the next?” The displayed IP addresses reportedly included infrastructure associated with Korea National University of Transportation and Dong-Eui Institute of Technology, potentially implying future targeting.
⚠️ The posts and screenshots confirm that these claims were published, but the authenticity, acquisition method, full scope of the datasets, and whether the two additionally referenced universities were compromised have not been independently verified.
The Telegram address and exact IP addresses have been omitted to limit access to the alleged data and avoid exposing potentially targetable infrastructure.
#CyberThreatIntelligence #ThreatIntel #DataBreach #SouthKorea
Banished Forum: Emerging Cybercrime Marketplace Activity — Reported by #TEAM_D4rkn3ttz@jzzzz1qw
Banished Forum, a Tor-based cybercrime forum active since August 28, 2026, appears to be developing into a structured underground marketplace for stolen data, malware, exploits, and hacking tools.
🔎 Key Observations
* Associated Accounts: Early forum activity and promotional announcements reference Ripp3r, ThreatMarket, and LeakDBMS. Ripp3r appears involved in forum administration, while ThreatMarket and LeakDBMS have contributed malware-related and database-related listings.
* External Marketplace Activity: ThreatMarket maintains a separate marketplace-style page advertising alleged stolen databases and cybercrime-related products. Its listings reference organizations in Brazil, Indonesia, France, and Argentina, with advertised prices reaching thousands of dollars.
* Platform Updates: On September 2, Banished announced VIP-to-GOD membership tiers, mediation and secure purchasing services, advertising options, and dedicated Combo, Proxy, Crack, HIT, and Config sections. On October 10, it promoted activity-based membership upgrades.
* Cybercrime Content: Forum discussion titles reference alleged database leaks involving Alipay, Sysco, and https://t.co/zfOrhDYqoB. Other referenced materials include data collections described as approximately 3TB, credential logs, Craxs RAT source code, and an exploit advertised as a Kaspersky EoP zero-day.
* Telegram Announcement: A group or account operating under the name APT Iran announced that it would cease Telegram activities and direct its followers exclusively to Banished Forum.
📌 CTI Assessment
Banished Forum is developing marketplace-oriented features through membership tiers, transaction mediation, secure purchasing services, and dedicated trading sections.
ThreatMarket has contributed malware-related listings to Banished Forum and also maintains a separate marketplace-style page advertising alleged stolen databases and cybercrime-related products. The relationship between these activities and their respective operators has not been independently verified.
The announcement by APT Iran to redirect its Telegram followers also represents an observed development relevant to tracking the forum’s activity.
Note: The authenticity of alleged database leaks, advertised products, exploit claims, and operational relationships between associated accounts remains unverified.
#CTI #ThreatIntelligence #Cybercrime #DarkWeb
KimJEN의 인제대·경일대 자료 유출 주장과 추가 표적 암시를 TEAM_D4rkn3ttz가 분석했습니다. 개인정보·메일·서버 설정 등 공개 자료의 분석 결과와 미확인 사항을 정리했습니다.
#TEAM_D4rkn3ttz#KimJEN#정보유출#사이버보안 https://t.co/UzrvFJSD3h
🚨 ShinyHunters / SLSH: New Activity Observed — reported by #Team_D4rkn3ttz@jzzzz1qw
SLSH has publicly disavowed Aegis/Reyswap, claiming he is not affiliated with ShinyHunters or SLSH and accusing him of using the ShinyHunters name in a scam.
SLSH describes itself as an alliance comprising ShinyHunters, Scattered Spider, Lapsus$, and UNC6783.
The SLSH name was previously used by an alliance comprising ShinyHunters, Scattered Spider, and Lapsus$ that was active in 2025.
The SLSH-branded operation is promoting IntelForums and has announced plans to redesign its DLS.
The site features a claim of a breach targeting the Florida DMV on October 10, 2026. Posted filenames appear consistent with naming conventions previously observed in ShinyHunters DLS listings.
SLSH also claims to have seized control of an existing ShinyHunters account with approximately 13K followers. Since then, the account has been observed in a mutual-follow relationship with SLSH’s account and is being used to promote the SLSH identity.
#CTI #ThreatIntelligence #Cybercrime #DarkWeb
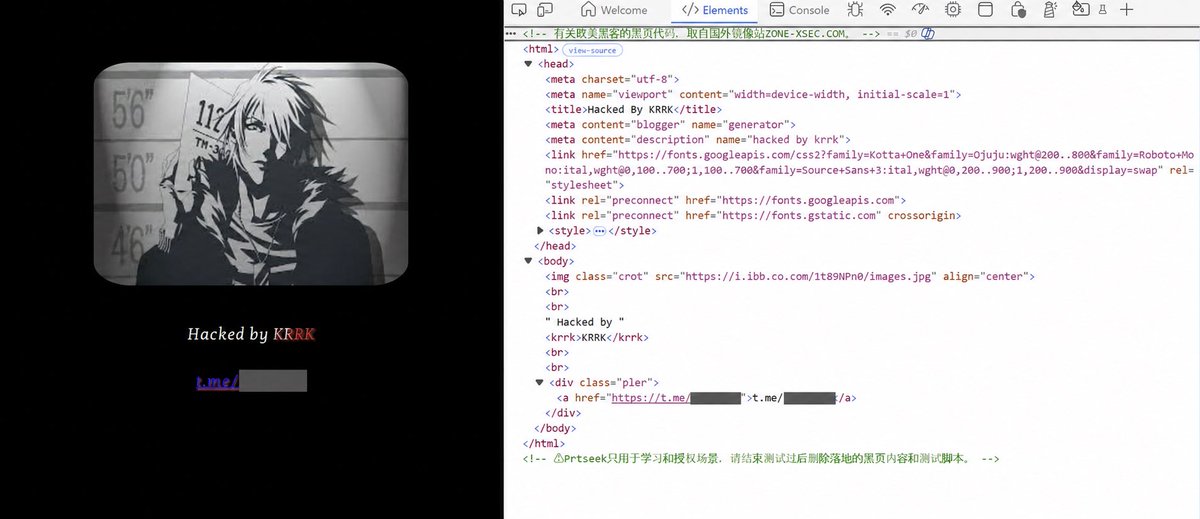
🚨 AI tool Prtseek referenced in a defacement page shared by KimJEN.
— Reported by #TEAM_D4rkn3ttz@kwisejh
KimJEN, who recently claimed database leaks involving South Korean universities, shared a link to the defaced page via Telegram. The page displayed the message “Hacked by KRRK.”
The HTML source shown in the screenshot contained two Chinese-language comments:
- The first stated that the defacement page code had been copied from ZONE-XSEC[.]COM, described in the comment as an overseas mirror site.
- The second stated that Prtseek was intended only for learning and use in authorized environments, and instructed users to remove deployed defacement pages and test scripts after testing.
Prtseek is reportedly an AI agent built on ARTEX’s code to assist with CTF challenges.
⚠️ The screenshot confirms that these comments were present in the page source. However, it does not establish the initial access vector, confirm that Prtseek was used in the defacement, or show that KimJEN independently compromised the site. The description of Prtseek as an AI agent and its reported relationship with ARTEX have not been independently verified.
#CyberThreatIntelligence #ThreatIntel #ARTEX #Cybercrime #SouthKorea
🚨 A threat actor's claimed sale of 663K+ https://t.co/kHu1OGk4HW member records is assessed as likely fabricated, with evidence pointing to a Zoho CRM trial account and synthetic data. — Reported by #TEAM_D4rkn3ttz@mingming0l
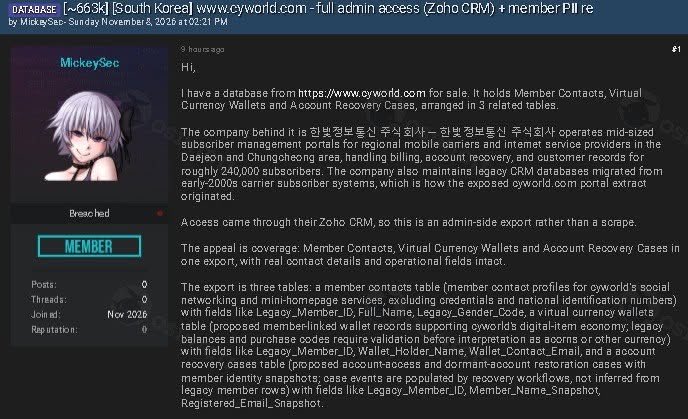
In a bf[.]st post dated November 8, 2026, the threat actor MickeySec claimed to be selling https://t.co/kHu1OGk4HW member contacts, virtual currency(acorns ‘DOTORI’ or other currency) wallet and account recovery records for $4,550. The actor described the data as an "admin-side export" obtained through a South Korean company's Zoho CRM.
🔎 Key Findings:
[Proof Screenshots]
- The Tasks list closely matches the default sample data provided in a Zoho CRM trial account, including dates, statuses, and priorities. Only the industry descriptions and company names appear to have been altered.
- Python byte-string escape sequences (\xb9\xb1...) appear in the browser tab title, suggesting improper character decoding or script-based handling of Korean text.
- Despite claiming "full admin access," the actor provided no evidence demonstrating access to administrative settings or privileged CRM functions.
→ Assessed as likely staged screenshots from a Zoho CRM trial environment.
[Sample Data]
- Record IDs are sequential, and creation timestamps are exactly one second apart, suggesting automated record generation.
- All members share an identical registration date, and every account balance is 0.
- The 'Created_By' and 'Modified_By' fields are empty, which is inconsistent with the populated audit fields observed in the reference Zoho CRM exports reviewed by the team.
- Email addresses appear to have been derived from mis-encoded Korean name strings.
→ Taken together, these patterns strongly suggest script-generated synthetic data rather than authentic member records.
[Timeline Inconsistency]
- The sample data contains a migration date of June 10, 2024. This date falls after Cyworld's service suspension in August 2023 but before Cy Communications (싸이커뮤니케이션즈), the entity that later acquired the service, was established in September 2024. This raises questions about who conducted the migration and under what operational circumstances.
[Named Entities]
- No publicly available evidence was found linking the companies named in the actor's post or screenshots to Cyworld's ownership, operation, or data management.
[Prior Breach Correlation]
- The claimed access method, involving a third-party Zoho CRM, differs from the circumstances of the 2011 SK Communications breach, which affected more than 35 million Nate and https://t.co/kHu1OGk4HW users.
- The claimed wallet and account recovery tables were not among the data types publicly reported in the 2011 incident.
- No evidence was identified linking the current claim to the 2011 breach.
⚠️ Based solely on the public post, proof screenshots, and sample data, the advertised dataset is assessed as likely fabricated. However, the possibility that it contains records sourced from prior breaches cannot be ruled out. No compromise of https://t.co/kHu1OGk4HW related to this claim has been independently verified or officially confirmed.
#CyberThreatIntelligence #ThreatIntel #DataBreach
DarkForums·WWH Club 사칭 피싱 사이트를 추적했습니다. 화면 복제와 결제 주소 재사용에서 출발해 8개 연관 도메인, 과거 서버 기록, 60 TRX 반복 입금과 거래소로 이어지는 자금 흐름을 확인했습니다. 확인된 사실과 판단의 한계까지 보고서에 담았습니다. https://t.co/XsH6AbU14f