some examples: https://t.co/q6BIhKBmK4 · https://t.co/1TwEpzddPn · https://t.co/LQ8GLM4r7w · https://t.co/yfcJ5qqlaZ · https://t.co/naIYU2wfLS · https://t.co/m54pwlgPGv · https://t.co/82kITVqBMG and so on
#bugbountytips A postMessage listener whitelisting *.platform.com is worthless if anyone can sign up and get a subdomain there.Both times it was the same 3rd-party SDK. Free account, deployed my page, opened the target in a popup
@ShivaanshKapoor Hello Bro , I submitted a RoycoVul report via Immunefi and am facing some difficulties. I'd be grateful for a chance
to discuss it with you。 Could you dm me first ?
We successfully achieved an RCE on GitLab in its default configuration.
Historically, most GitLab RCEs have lived in the web or application-logic layers. This time, guided by the @depthfirstlabs spirit, we went deeper: into the low-level gem dependency chain beneath GitLab.
The result? By sending crafted JSON data, we could exploit memory-corruption vulnerabilities buried deep in that chain and take control of the GitLab application server.
@depthfirstlabs brings together some of the smartest people, and is building the best security AI agent. Follow our work, and come join us!
Read more about this in the comment...
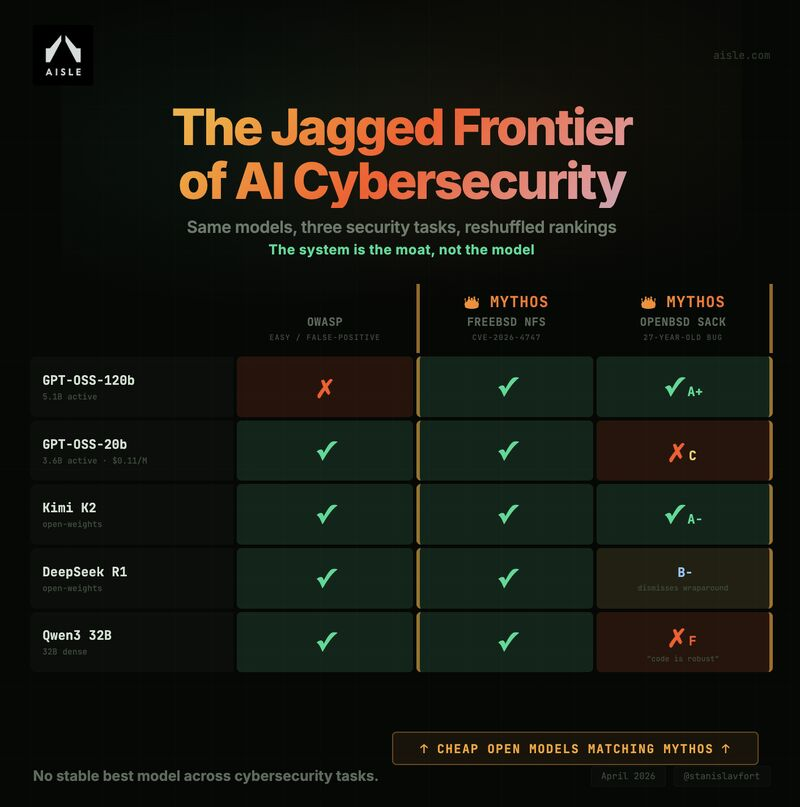
New post: We tested the Mythos showcase vulnerabilities with open models.
They recovered similar scoped analysis! 8/8 models found the flagship FreeBSD zero-day, including a 3B model.
Rankings reshuffle completely across tasks => the AI cybersecurity frontier is super jagged!
New on the Anthropic Engineering Blog:
How we use a multi-agent harness to push Claude further in frontend design and long-running autonomous software engineering.
Read more: https://t.co/HWvmXk1ykn
I hacked Claude Code! It turns out "agentic" is just a fancy new way to get a shell. I achieved full RCE and hijacked organization API keys. CVE-2025-59536 | CVE-2026-21852
https://t.co/GymKzaM1wp
#ai#Claude
gpt-oss is out!
we made an open model that performs at the level of o4-mini and runs on a high-end laptop (WTF!!)
(and a smaller one that runs on a phone).
super proud of the team; big triumph of technology.
1/4 dbugs LIVE
https://t.co/Cd6L8AD6Bt — vulnerabilities’ home
See trends, discover more, read AI summaries, have all references at hand, and your profile with all your CVEs and CVSS score on a leaderboard.
⬇️ See thread: what’s live + what’s next ⬇️
After 9 months+ of cranking, cursing, and cursoring, and drawing on over 20 years experience running #HITB's Call for Papers, I bring you CFP Directory - a single system to make it easier for speakers to submit and organizers to connect and curate talks: https://t.co/yJdRUYHnkF