🚀 New Feature IOC / IP Monitoring
Add the IP addresses and IOCs you want to monitor, and let Etugen handle the rest.
Etugen continuously monitors threat infrastructure, automatically detects newly associated files and IOCs introduced by threat actors, and delivers them to you in real time.
Threat hunting has never been this easy.
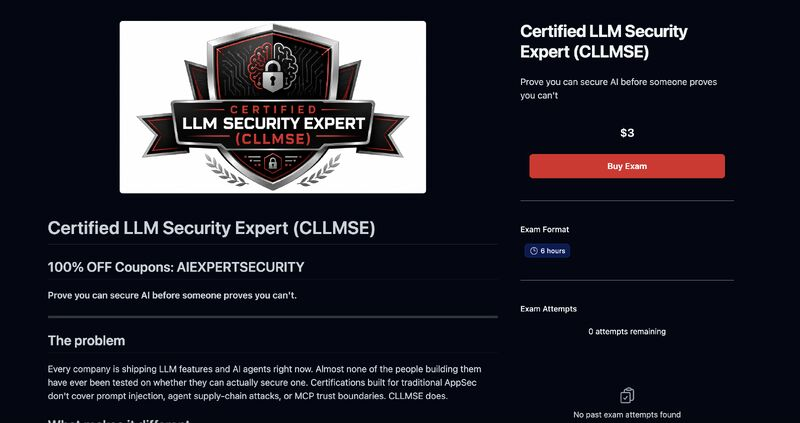
FREE CERTIFIED CLLMSE: certification was created for professionals who want to prove, in practice, that they can identify, exploit, and remediate vulnerabilities in AI-powered applications.
Use 100% OFF coupon:
AIEXPERTSECURITY https://t.co/aabfI9GvEy
🔥 A new 16-year-old #Linux KVM flaw lets a rooted nested VM crash the x86 host and take down other tenants on the same machine.
Dubbed "Januscape" (CVE-2026-53359), the bug sits in KVM’s shadow MMU.
Researcher says a full guest-to-host escape exploit also exists in a controlled setup; only the host-crash PoC is public.
Explained here: https://t.co/iaExaCmYFg
Funny how Microsoft attempts to fix Defender resulted in a bug that causes Defender to be unable to delete any malware with NTFS ADS file name, something like C:\test:mlwr.exe will never be deleted by Defender, will be detected but always fails to delete.
‼️ Nightmare Eclipse is back on GitHub under a new alias and has released a new Windows Defender vulnerability zero-day called RoguePlanet.
PoC: https://t.co/n0xF6uGt4u
New GitHub Account: https://t.co/qwU93VedpH
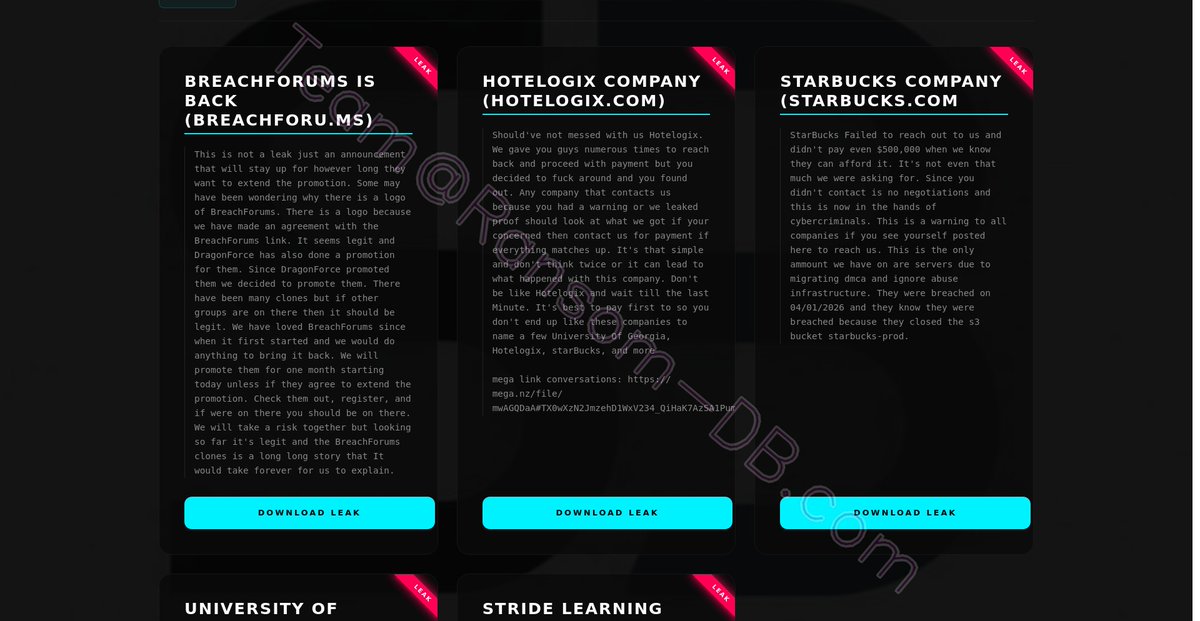
🚨 Ransom group "Shadowbyt3s" publishes "BREACHFORUMS IS BACK (https://t.co/T981W59lsh)" - United States 🇺🇸
📍 Location: United States
🏢 Industry: Cybercrime Forum
🔗 Website: https://t.co/bUPSIbNyRB
BreachForums, launched in 2022 as a successor to RaidForums, hosted hacking discussions and the trade of stolen data and tools. Following founder Conor Brian Fitzpatrick’s 2023 arrest, law-enforcement actions triggered shutdowns and leadership churn.
❗️🚨 BREAKING: Security researchers are now handing Nightmare-Eclipse vulnerabilities for free, in what looks like both a show of support and a reaction to how Microsoft treats researchers. First up: "Bitskrieg," violates Secure Boot trust and fully bypasses BitLocker.
It seems aimed squarely at Microsoft's recent blog, where the company said its Digital Crimes Unit would bring cases against threat actors "and those that enable their criminal activity," language many researchers read as a threat pointed at them.