If your firewall can’t inspect encrypted traffic, what is it actually protecting?
ICYMI: Inside Cybersecurity spotlighted that very issue in their coverage of our 2026 Cloud Network Firewall test. Thanks to Jaden Beard for continuing to follow this work closely, and for connecting the results to the organizations that depend on these tools every day.
For agencies and enterprises running critical operations in the cloud, assuming built-in security is good enough isn’t a strategy. Verification is.
🔗 Read Jaden’s article: https://t.co/oir5utWh6Y
#Cybersecurity #CloudSecurity #IndependentTesting
Thanks @rapid7 for inviting NSS Labs CEO @vikphatak to speak at their conference in Boston. Joining Vik for some great conversations around cybersecurity and AI were Reena Choudhry, Go-to-Market Specialist for NSS Labs, and Francisco Artes, VP of Product & Enterprise Security at @Roku.
@Apple researchers just shared their Minions. We have Minions too.
Theirs pool idle Mac GPUs so AI jobs don’t sit in a 10-hour queue. Ours throw tens of thousands of real exploits, malware samples, and evasions at your security controls to see what actually gets blocked.
The funny part? Under the hood they look alike. A coordinator splits big jobs into small ones. Stateless workers run them. Something checks the results and re-runs anything that fails.
When work is spread across lots of machines, you need proof it ran right. For Apple, that’s a watchdog. For your firewall, that’s Minion by NSS Labs.
https://t.co/ZizdDSGltF
Convenience has value. But convenience doesn’t block exploits.
In today’s blog, Bob Walder breaks down our 2026 Cloud Network Firewall test, published by @CyberRatings. The results show why the better question isn’t “native or third-party?” It’s “what job does this control need to do?”
First assess your specific needs, then evaluate each product explicitly.
🔗Read the blog: https://t.co/gVZHZFATH0
Welcome, Reena Choudhry! The former CRO of Cerby and Obsidian Security joins NSS Labs as Go-to-Market Specialist to help bring Minion, our security testing platform, to more enterprises, partners and service providers. https://t.co/Ut5T4Rtgld
#cybersecurity
Get a head start on your 2027 budget plans by including Minion from NSS Labs.
Schedule a no commitment trial today to find out how Minion delivers independent, evidence-based validation of security technologies under real-world threat conditions: https://t.co/XMW7uDXPdz
#continuousvalidation #MinionbyNSSLabs #cybersecurity
We tested nine cloud firewalls with the same threats and the results varied widely, which is why buyers can't rely on data sheets alone.
Independent, repeatable testing shows what you're really deploying.
Download the full reports: https://t.co/QTjv7rQgs3
Today we announced the results of the latest Cloud Network Firewall test conducted by @nss_labs. Nine products were evaluated, with security effectiveness ranging from 0% to 99.95%
Want to take a deeper dive into the results? Read the reports for free: https://t.co/Bm6xGnfbFd
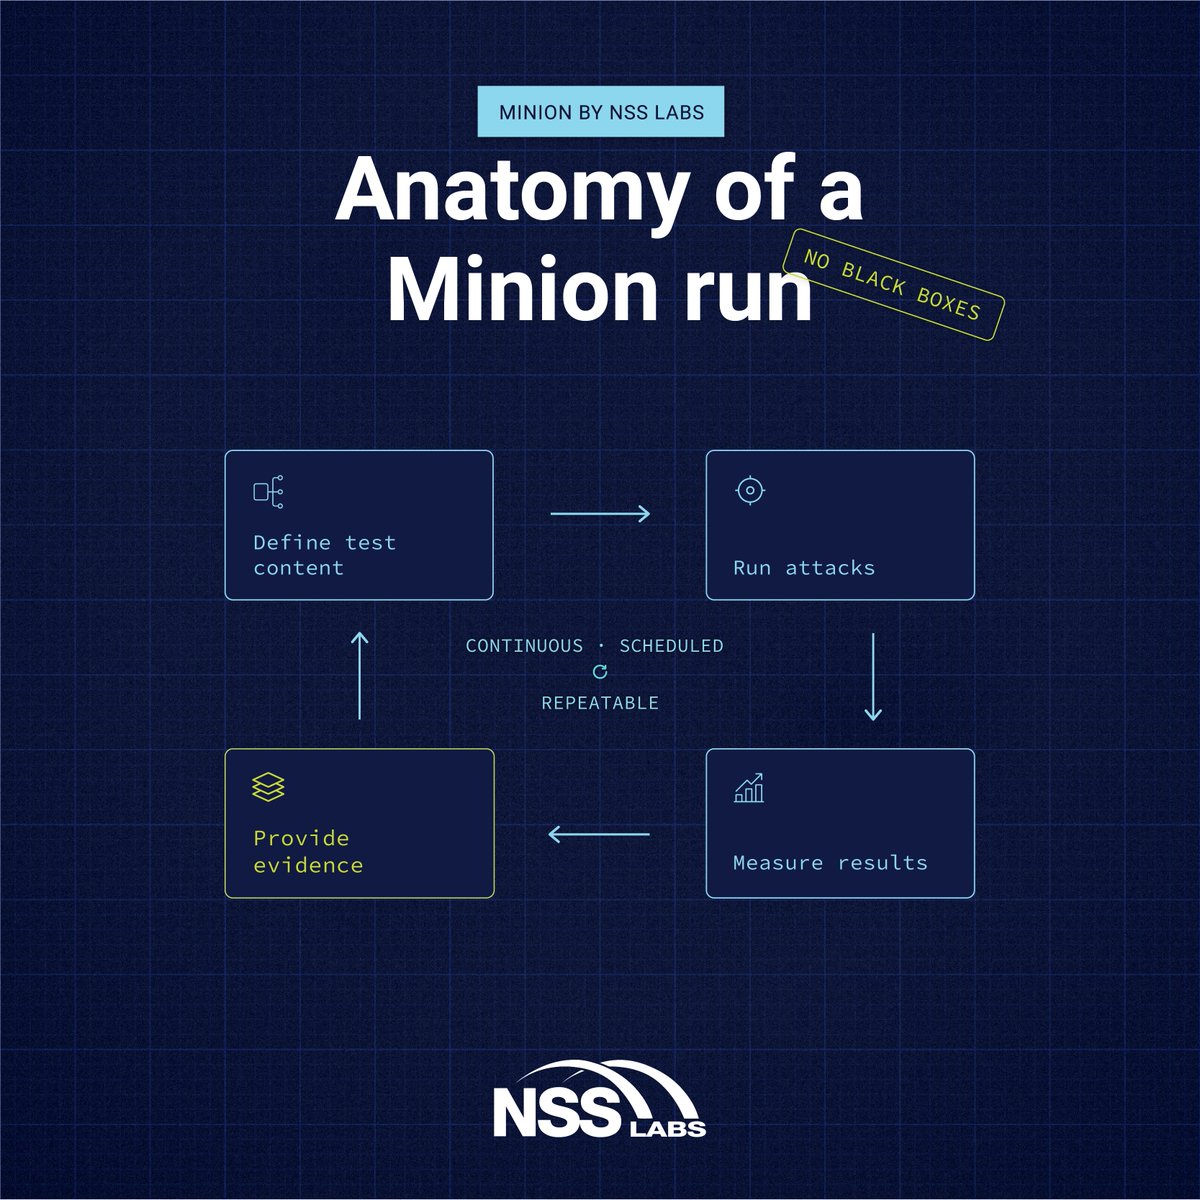
“How involved is a Minion run by NSS Labs?”
Lighter than you'd expect: a drop-in client, NSS Labs runs it remotely against current threats, results verified against evidence, versioned reporting you can show over time.
Your team stays on the product.
Want to see it against your stack? Book a scoping call, no commitment ➡️ https://t.co/lQJfLFSDrE
#CISO #ContinuousValidation #NSSLabs
A single point-in-time test tells you how secure you were. Minion tells you how secure you are — continuously, at scale, with proof.
You get:
• Real-time visibility with each stage of the test
• Drop-in client deployment, with optional packet-level (PCAP) capture when you want to see everything
• Evidence you can explain to your C-suite and your auditors
Want more details on how Minion runs? Check out our website at 🔗https://t.co/ZizdDSGltF
#NSSLabs #Minion #SecurityValidation #CEV
Are you assuming your security controls remain effective or actually measuring whether they do?
The final part of our Control Efficacy Validation series is here, covering how CEV moves from theory to practice.
Missed Parts 1 and 2? Catch up on the full series on our website.
📄 Read the full white paper by Bob Walder: https://t.co/nbGQ5RFWhE
#WhitePaperWednesday #ControlEfficacyValidation #CyberAssurance #EnterpriseSecurity
How do you validate that a security control actually works today?
↳ Vote 👇 — then tell us what made you pick it. The honest answers are usually D.
#NSSLabs#Cybersecurity#GRC#SecurityValidation
In Part 1 of our White Paper Wednesday series, we introduced the term 'Control Efficacy Validation.'
Part 2 defines what it means and why historically, despite a clear need for it, enterprises have not employed it. (Hint: Time, $, and complexity)
📄Read the full white paper: https://t.co/uAk5Sb5W4P
Lab conditions are comfortable. Real threats aren't.
Run validation against 1M+ in-the-wild malware samples and 10K+ exploits drawn from 250K+ CVEs with NSS Labs.
Learn more about Minion by NSS Labs: https://t.co/8oKDov3aJr
Minion by @nss_labs is a managed testing platform fthat evaluates whether deployed security controls effectively detect, block, allow, or mishandle defined threats and traffic. #cybersecurity
Check out our latest #Techprimer:
https://t.co/zy3iUcg4rf
Point-in-time testing tells you a control worked once… under lab conditions… on a Tuesday.
Threats don't respect your test schedule. Continuous validation isn't a nice-to-have — it's the only honest way to verify a control still works today.
#NSSLabs#Cybersecurity #Infosec
How we validate system responses:
For scenarios in which a prompt is blocked, we inspect the returned system behavior and user-facing response.
Then, we determine whether the system provides a clear, safe, and informative response without exposing sensitive control details.
How we test content filtering accuracy – a.k.a. false positives:
We submit benign prompts that resemble risky content in structure, tone, or subject matter but should remain allowed under policy.
Then, we measure whether the AIPS supports legitimate use without unnecessary disruption.
Do you know if your AI protection system actually blocks the right content (and allows the legitimate stuff)?
Follow this thread about how we test policy & filter efficacy in AI protection systems.⬇️