@geovapc El abi la aplico bien.
Ley no. 3 de las 48 leyes del poder
Disimule sus intenciones:
"Oculte tus intenciones, siembre confusión y guía a otros por caminos falsos. Cuando descubran la verdad, ya será tarde."
Honestly, what is this ? I got a response from @github support team. So here after legal Security Research and PoC's is not allowed on GitHub ?
I'm Completely got disappointment by @github and @Microsoft@MsftSecIntel .
In what ways i distribute and share malware. Can anyone tell me if there is a mistake from my side, did i share 0 days, vulnerabilities, direct binaries or full exploit chain that harm users ? NONE ?
is posting Legal source codes and tools that are made of public PoCs are wrong ? there are thousand of full chain real expoits that bypasses EDRs, C2s that evades security solutions, phishing kits that bypasses MFA of Microsoft out there in @github , if that is legal then why cant this simple publically made poc can't be in the github ?
I have replied regarding my statements, please don't disappoint younger legal windows security researchers like this. I have some little hope on @github@Microsoft@MsftSecIntel .
I have a little hope. So Please don't make me loose on @github & @Microsoft & @MsftSecIntel .
Ticket ID: #4440743
Will be waiting for your kind response. Thank you.
https://t.co/FTpHwmDK8D
#github #microsoft #security #research
I am getting a lot of dm's and private message regarding the repositories.
🧵1 / 2
Update:- From the support desk. [Some activity on your account was flagged by our abuse-detection systems for manual review]. My account was marked as spam.
I have given additional details to @github. I can't just post them in another platform since that violates their rules, idk what to do !!
So, I am just waiting and thinking of another way to reach them. This issue was one of the hardest ways to fix, sometimes it takes months for them to verify that you’re not a bot. I’ve read the reports. I’m not banned on GitHub, the account was cut off from public access. I can still modify, edit, and push to my repositories.
If you know someone who can fix the problem. Kindly convey the issue to them. It could be a great help from you guys. @github kindly resolve the issue.
I Will be updating the situation. Until then i will be focusing on my private projects.
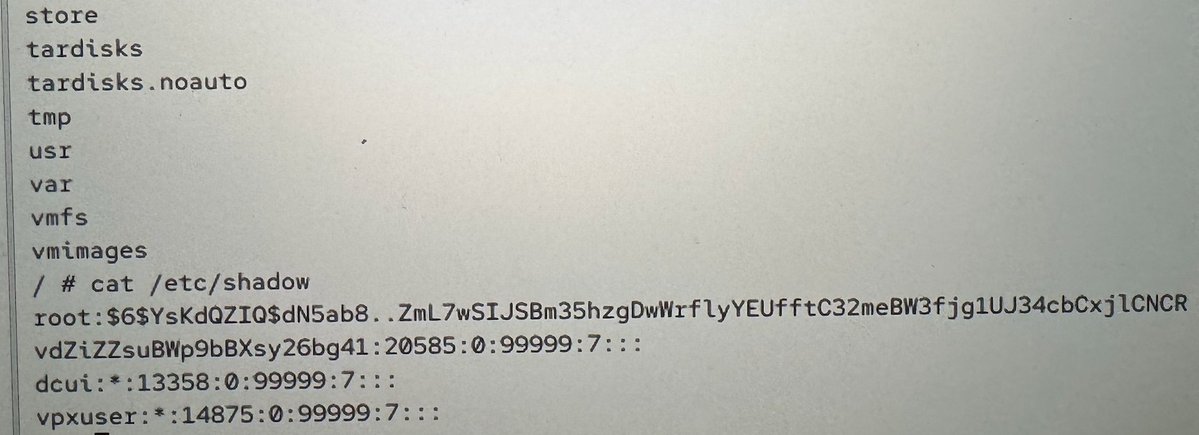
Mind blown alert 🤯! Nguyen Hoang Thach (@hi_im_d4rkn3ss) of STARLabs SG (@starlabs_sg) used a Memory Corruption bug to exploit VMware ESXi with the Cross-tenant Code Execution add-on, earning a sweeeeeet $200,000 and 20 Master of Pwn points. Full win let's go! #Pwn2Own #P2OBerlin
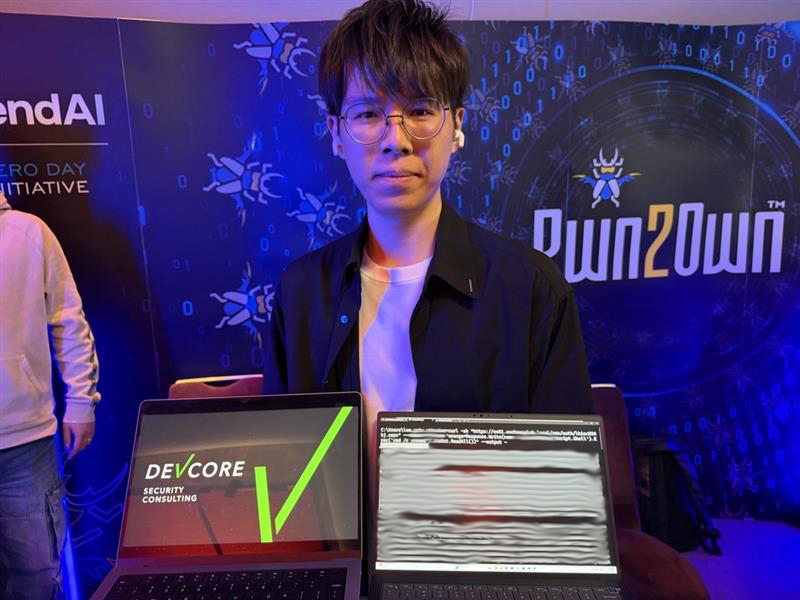
Aaaand it's official! Orange Tsai (@orange_8361) of DEVCORE Research Team chained 3 bugs to achieve Remote Code Execution as SYSTEM on Microsoft Exchange, earning a whooping $200,000 and 20 Master of Pwn points. Full win! #Pwn2Own#P2OBerlin