On September 21st, 2023 Telekom Security CTI Team observed the threat actor #TA577, also known as "TR", launching a new high-volume malware distribution campaign spreading #DarkGate malware. 🧵 1/4
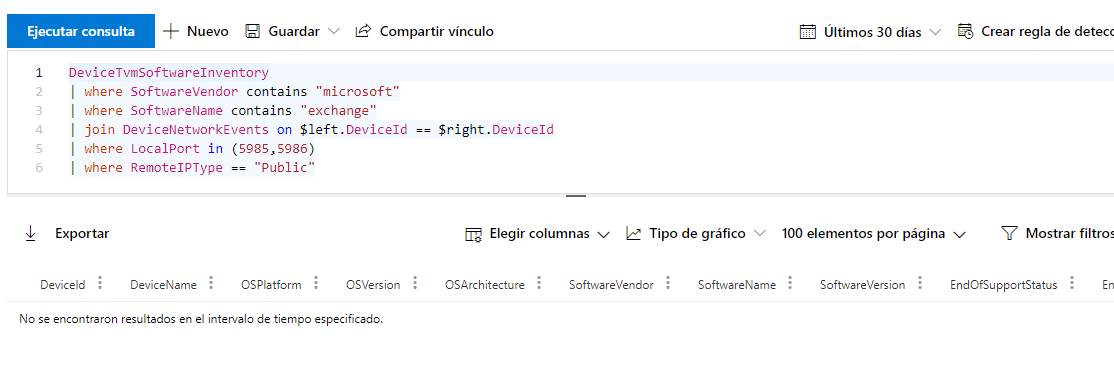
@rasmusjhave@GossiTheDog@sunnyc7@shotgunner101@reprise_99@NathanMcNulty Btw, why filter by FileName? (FP)
Surely specifying the FolderPath could limit results to a specific scenario, but it is the closest condition for executing a malicious binary without user interaction and without creating additional processes (such as scheduled tasks or services)
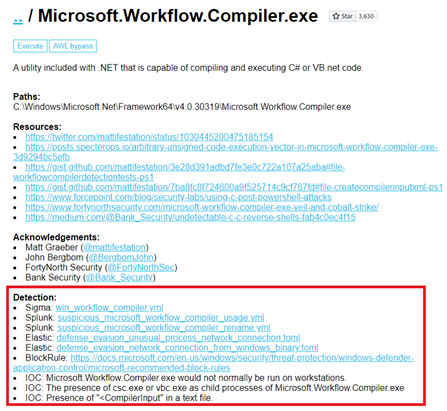
[#LOLBAS Update] https://t.co/OKqDKOmE2Y
To supplement the recently added MITRE ATT&CK v10 mappings, detection resources for LOLBAS have been added to include links to relevant publicly available detection rules [Sigma/Elastic/Splunk], Block Rules (WDAC), and analysis resources!
#Emotet is reborn again! The botnet delivers both malicious documents and payloads from C2 right now. The maldocs for distribution are Excel and Word files. But there is no sign for active spam yet. Don't miss the latest news about #Emotet with ANYRUN! https://t.co/ZwuicNpZcc
Living Off Trusted Sites (LOTS) Project Attackers are using popular legitimate domains when conducting phishing, C&C, exfiltration and downloading tools to evade detection. The list of websites below allow attackers to use their domain or subdomain https://t.co/ARgpxPjZvA
I've converted @daffainfo nuclei template into a #Sigma rule to detect exploitation of the #Apache path traversal vulnerability reported in CVE-2021-41773
#CVE202141773
Nuclei Template
https://t.co/nFdTlnXCSS
Sigma Rule
https://t.co/LvdcroscA1
Disable Macros in documents downloaded from the Internet
(makes use of the Zone Identifier)
https://t.co/AFgVtgQTwJ
Ransomware Prevention - see the respective tab in this spreadsheet
https://t.co/rwQen1khof
More general recommendations
https://t.co/hHqcw6VrFf
Script launched by msiexec.exe (extracted by zip file)
IWshShell3.ExpandEnvironmentStrings("%userprofile%");
IWshShell3.ExpandEnvironmentStrings("%userprofile%");
IFileSystem3.FolderExists("C:\Users\XXXXX\AppData\Local\");
IWshShell3.ExpandEnvironmentStrings("%userprofile%");