This is genuinely outrageous. @Ubiquiti I urge you to knock off this abusive behavior. I'm a mostly-happy Unifi customer, but there's no way I can support a company with judgment this disastrously bad.
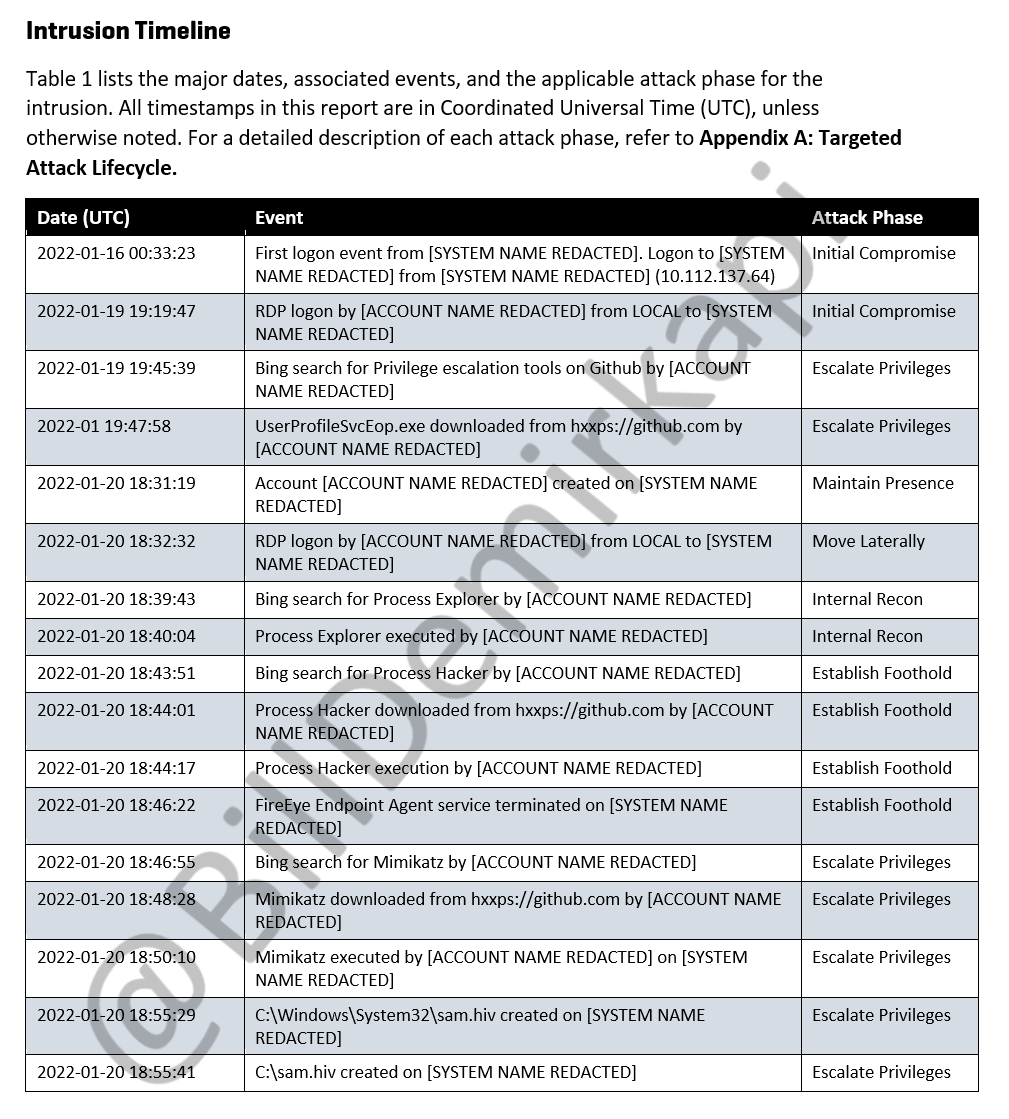
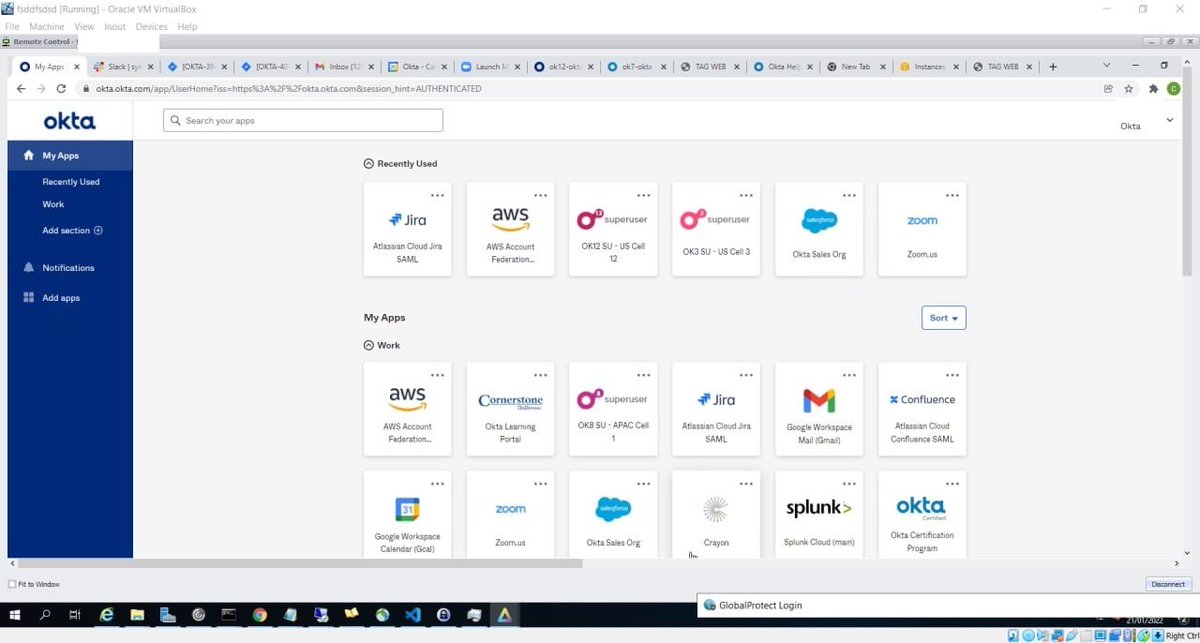
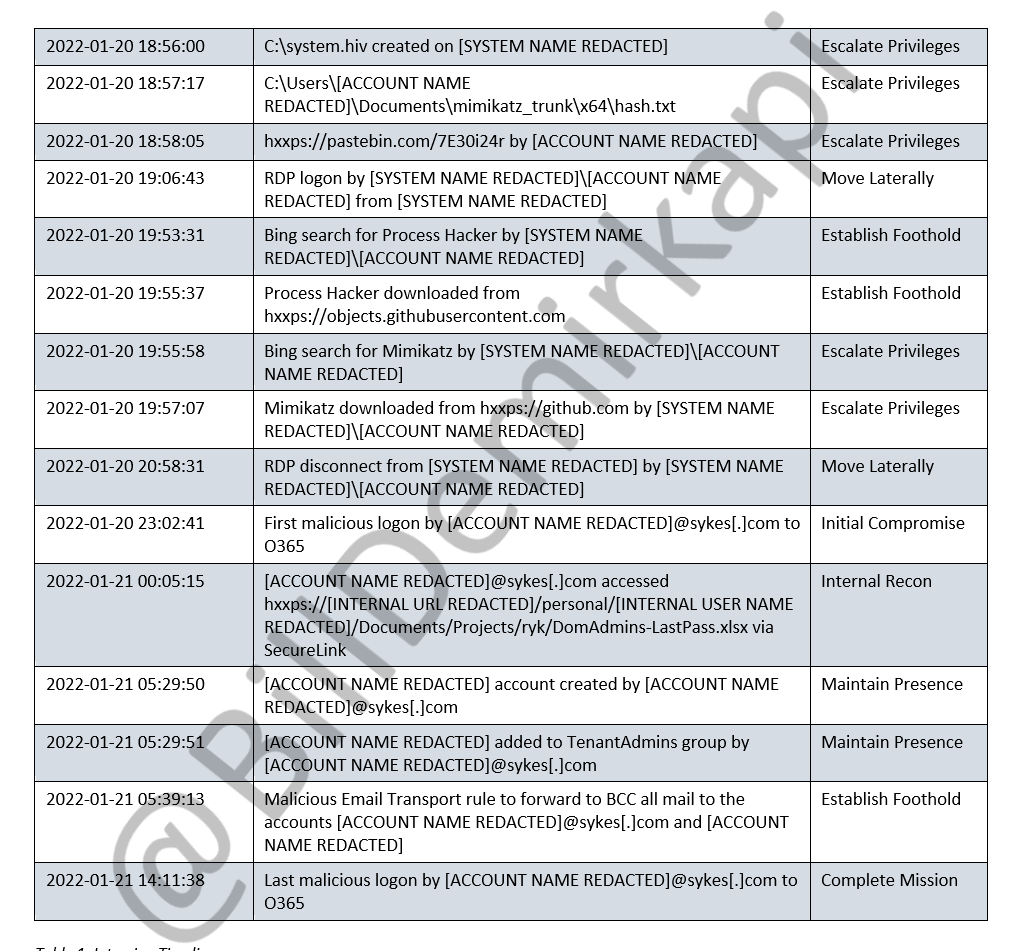
New documents for the Okta breach: I have obtained copies of the Mandiant report detailing the embarrassing Sitel/SYKES breach timeline and the methodology of the LAPSUS$ group. 1/N https://t.co/z05uQYclg9
I want to be clear... 125k log entries without any qualification means jack squat.
Did you know you can make a Windows desktop system generate that many events in under an hour?
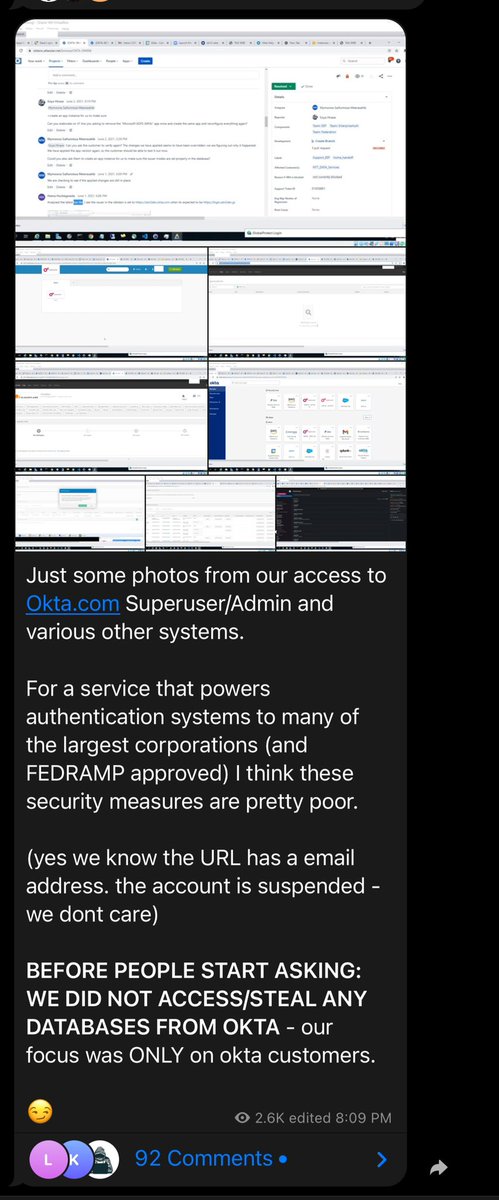
There's a lot that Okta has done in this event that is sus, But for me, this is probably the worst
The Cloudflare team put together a great write up of how they investigated: https://t.co/JhrO0byzfZ
investigated these events:
user.account.reset_password, user.mfa.factor.update, system.mfa.factor.deactivate, user.mfa.attempt_bypass, and user.session.impersonation.initiate
🙌 All great advice coming from everyone.
It's best to review logs since January.
Okta's impersonation setting is off by default. You can review over in your account settings at [tenant].okta.com/admin/settings/account
Great advice from @FrankMcG. But what does "Bad" behavior look like in an SSO breach?
Look for:
1. Audit logs for unusual config changes (ex. MFA policy change)
2. Unusual new account creations
3. Unusual modifications to existing users (password resets)
Most people suck at managing up.
They waste their boss’ time with too much (or too little) information.
Here’s how to give the right amount of context: