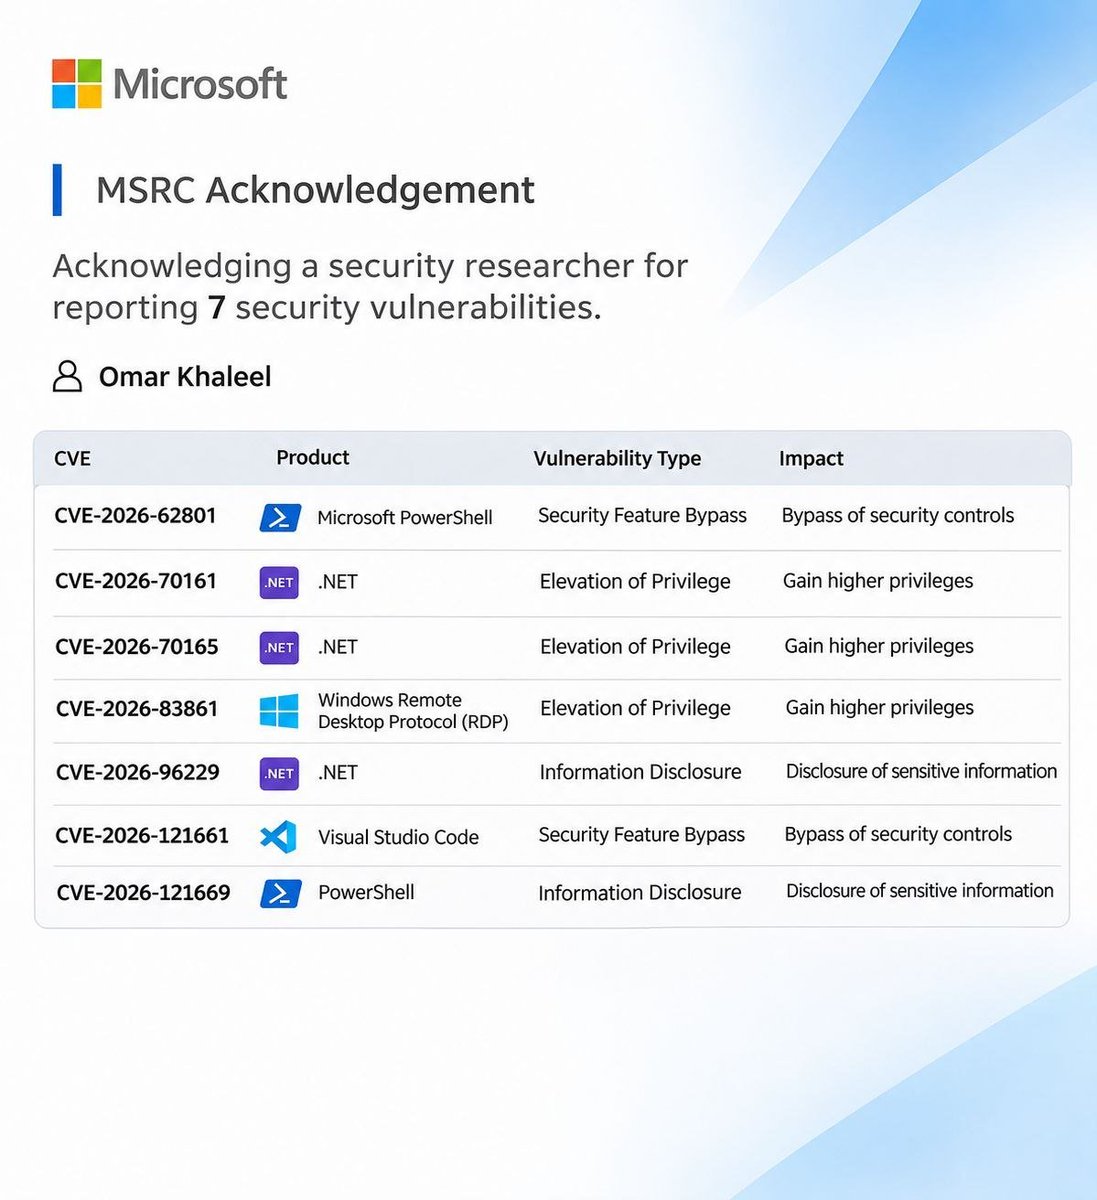
Proud to be recognized by Microsoft MSRC for reporting 7 security vulnerabilities across Microsoft products.
7 CVEs. One continuous journey. More to come! 🔐🚀
#Microsoft#MSRC#CyberSecurity#SecurityResearch
Microsoft ranked me #9 in the world on the 2026 MSRC Most Valuable Researchers list.
My unfair advantage: autonomous AI agents I built, hunting alongside me.
Offensive security now runs at machine speed
#MSRC#CyperSec#OSSVRP#BugBounty
Today, we're proud to recognize the Top 100 Microsoft 2026 Most Valuable Researchers (MVRs).
Security researchers play a critical role in helping protect customers by identifying and reporting vulnerabilities across Microsoft products and services. We're grateful for their partnership and the impact they have made over the past year.
Congratulations to this year's Top 10 MVRs:
🥇C46F3708A45EF0041BD0A49DDAEA0E25
🥈ShinHyuiq & Alan Pang
🥉cherrypick
4. Brad Schlintz (@nmdhkr)
5. wtm (@wtm_offensi)
6. Asaf Cohen (https://t.co/8WLhdz05Oq)
7. bccc95a61a3cc79d7b2c4423c808f744
8. Felix B.
9. 142a423e2574abf10d65eba46891ca5e
9. Anonymous
This year, we updated the MVR leaderboard to rank researchers based on total bounty awards, creating a clearer connection between recognition and security impact. We also introduced Special Mentions to recognize researchers who submitted valid vulnerability reports during the recognition period, regardless of leaderboard ranking.
See our blog for the complete list of the Top 100 MSRC 2026 Most Valuable Researchers and the top researchers by bounty program: https://t.co/tkDVvFbFEr
Thank you to every researcher who partnered with us this year to help protect customers worldwide.
Today, we're proud to recognize the Top 100 Microsoft 2026 Most Valuable Researchers (MVRs).
Security researchers play a critical role in helping protect customers by identifying and reporting vulnerabilities across Microsoft products and services. We're grateful for their partnership and the impact they have made over the past year.
Congratulations to this year's Top 10 MVRs:
🥇C46F3708A45EF0041BD0A49DDAEA0E25
🥈ShinHyuiq & Alan Pang
🥉cherrypick
4. Brad Schlintz (@nmdhkr)
5. wtm (@wtm_offensi)
6. Asaf Cohen (https://t.co/8WLhdz05Oq)
7. bccc95a61a3cc79d7b2c4423c808f744
8. Felix B.
9. 142a423e2574abf10d65eba46891ca5e
9. Anonymous
This year, we updated the MVR leaderboard to rank researchers based on total bounty awards, creating a clearer connection between recognition and security impact. We also introduced Special Mentions to recognize researchers who submitted valid vulnerability reports during the recognition period, regardless of leaderboard ranking.
See our blog for the complete list of the Top 100 MSRC 2026 Most Valuable Researchers and the top researchers by bounty program: https://t.co/tkDVvFbFEr
Thank you to every researcher who partnered with us this year to help protect customers worldwide.
A path traversal primitive is not the end goal.
The real question is whether one trusted artifact can overwrite another trusted cache path during a normal workflow.
That is where things become security-relevant.
#Flutter#BugBounty#AppSec
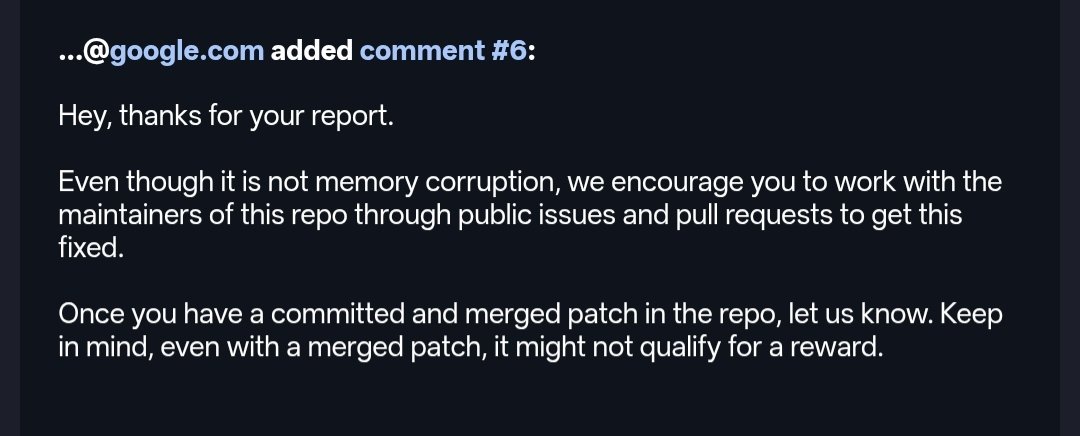
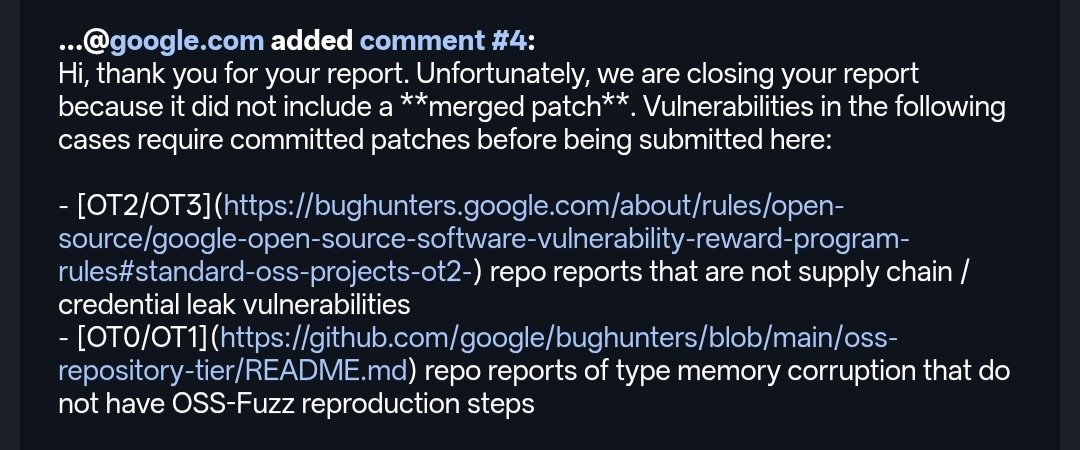
Respectfully, public policy and actual triage should match.
If flutter/flutter is TIER_OT0, requiring a merged patch for non-memory reports needs clarification.
#GoogleVRP#OSSVRP#Flutter
@hasanfleyah@GoogleVRP This happened to me too, my vulnerabilities and reports are not memory corruption , but they closed them and then reopened them after the objection, I don't know what is happening!!