On the Binance incident, my preliminary take:
• ~$3B frozen on-chain + ~$1.17B SAFU could cover ~66% of the reported loss.
• The estimated remaining gap of ~$2.1B is ~1.3% of the ~$165B reported in Binance’s Oct. 1 PoR.
• Binance has committed to covering the rest with company funds. From the above data, I view the commitment as credible.
I’ll keep tracking on-chain flows and updated PoR.
Update: Kerness is a multi-agent framework for building your own agent systems. Plug together models, tools, memory, and skills, then define how agents work together. Use the built-in components or bring your own.
https://t.co/hnwLqVozoJ
Kerness v0.1.0 released. a true framework for you to build your own harness.
Multi-agent, memory management, skills and etc. Plug and play.
https://t.co/syyDE2TKXV
Everyone is running someone else's harness.
Kerness is the kernel underneath harness: provider transport, tool dialects, the turn loop, access control, memory, compaction, resume.
You write the Markdown saying how yours behaves. 60 seconds, not 6 weeks.
Written in rust with python binding.
https://t.co/o7hFHuD3WF
Trust is the foundation of blockchain, not just decentralization.
CertiK Co-founder & CEO Ronghui Gu joined Shusaku Fujino, CCO of OKJ, for a fireside chat on security, compliance, and building trust in Web3, moderated by Yuki Kamimoto of N.Avenue.
Stay tuned for the full conversation.
Layoffs suck. CertiK is hiring.
I am very much enjoying my time at @CertiK and would love to bring more talented folks to work on my team.
Here are the roles I am looking for:
1. Public Facing Senior Web3 Security Researcher (1-2 Openings)
Web3 security researcher who can act as a public face for CertiK. This means having a strong social media presence, speaking at conferences, and being openly helpful to the wider security community. This doesn't mean you have to have tens of thousands of followers, but you do need to be comfortable interacting with the general public. The specific type of security researcher is flexible - contract/chain auditors, pen testers, engineers can apply.
2. Web3 BD (1-3 openings)
We have big plans for new product offerings at CertiK. We need talented folks to understand our products and build relationships with our clients.
3. Senior Penetration Testing Engineer (1-2 openings)
See: https://t.co/kiOH4LScfD
How to apply below 👇
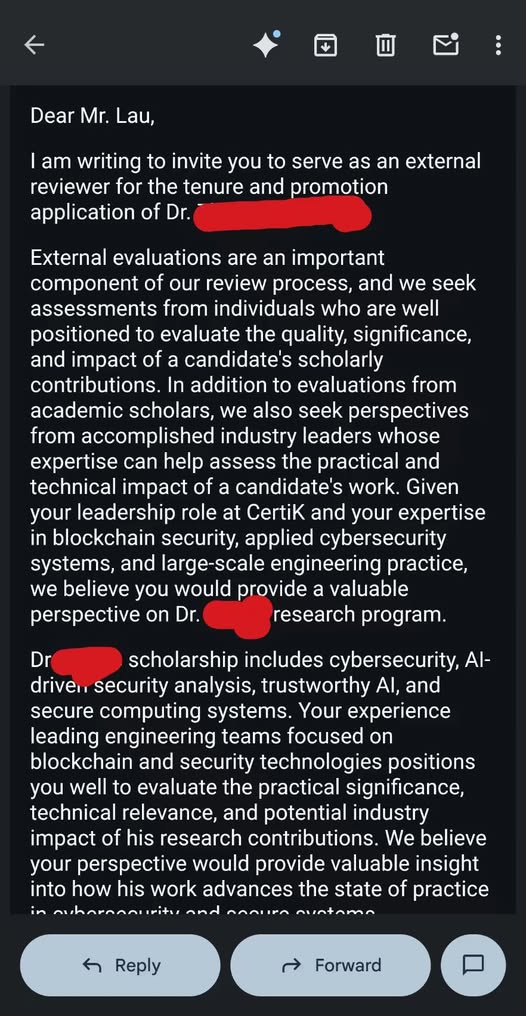
Honored to be invited by Seattle University to serve as an external reviewer for a doctoral tenure review. Thank you for the trust and opportunity to support academic excellence.
Make @grok Build great
A portable SKILL.md that teaches agents like Grok Build to build & maintain a durable ARCHITECTURE.md + per-module docs. Learn, Plans and confirms before writing/fixing codes.
Making Grok Build work smarter
https://t.co/hEV3hJGuhk
💥 Introducing "Dirty Frag"
A universal Linux LPE chaining two vulns in xfrm-ESP and RxRPC. A successor class to Dirty Pipe & Copy Fail.
No race, no panic on failure, fully deterministic. ~9 years latent.
Ubuntu / RHEL / Fedora / openSUSE / CentOS / AlmaLinux, and more.
Even if you've applied the "Copy Fail" mitigation, your Linux is still vulnerable to "Dirty Frag". Apply the Dirty Frag mitigation.
Details:
https://t.co/9nqku4svkY
I use @CertiK's new tool AI Auditor (beta)
Two scans revealed 9 findings (4 major, 0 critical), showing no immediate high-risk threats but clear areas needing improvement for stronger security and reliability.
The AI auditor effectively identifies key vulnerabilities quickly, helping reduce manual effort and speed up development.
To improve, the UI should focus on:
Guided onboarding
Clear severity explanations
Inline code highlights
Suggested fixes
Simple risk dashboard
Overall, it’s a solid tool with strong potential, especially with improved usability for new developers.
@hudsonjameson@RonghuiGu@CertiKCommunity@CertiK