We're tracking the largest ever Github actions attack - WFX. We count thousands of impacted repos and developer accounts and are linking this attack to the previous GhostAction attack.
Read our findings and breakdown (link in comments)
Meet @osspreysecurity !
Ossprey is the security tool built for engineering-led companies who depend on open source and can’t afford to slow down.
You can learn more here: https://t.co/mUk7NBU2J8
@CharlieEriksen We're also seeing that 3 encoded commands are left over in the package from xcode project files in the example folders, in the new version
We are currently tracking the following NPM user publishing EtherHiding malware.
https://t.co/DRUFkkkJjC
One package named anhn-cli and several others scoped to @wizloft
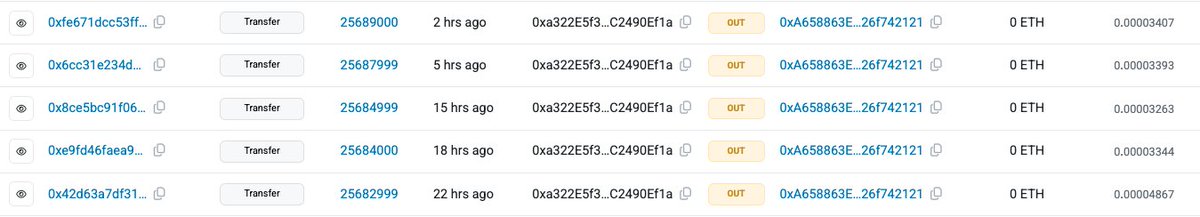
The contract address is associated with previous DPRK related malware we have seen in the past weeks
0xa322E5f3D311D3080e6f0121063e9aDC2490Ef1a
Recently we have seen DPRK malware move away from jsonkeeper following our recent takedown action with the host.
New malware appears to be abusing https://t.co/087VdJqFuU
express-chai 3.7.8
https://gray-dyane-31.tiiny[.]site/index.json
We have noticed some more movement from the current DPRK EtherHiding/NullReceiver campaign on NPM.
Using the same C2 that has been covered previously 166.88.134[.]62
Wallet remains active
https://t.co/babwFHgoqN
@voxepay/checkout v0.5.19
@zahlen/checkout-angular v0.1.4
@zahlen/checkout v0.2.2
simplipayng v1.0.8
@vboxdev/common v1.0.73
@nasddatax/common v1.0.21
@rentwise/common v1.0.36
@nasdtickets/common v1.0.23
The on-going shai hulud attack is spreading significantly.
Hundreds of packages scoped to @servicetitan are now compromised too.
We will be sharing an analysis and remediation advice shortly for all affected developers
Ossprey Security is currently tracking the compromise of several popular packages, with over 160 million weekly downloads combined.
More information coming soon
keyv v6.0.0
@cacheable/net v2.1.1
@cacheable/node-cache v3.1.2
cacheable v2.5.1
@cacheable/memory v2.2.1
file-entry-cache v11.1.6
@cacheable/utils v2.5.1
ecto v5.0.1
Tech News of the Week:
(This is for informational purposes only, and in no particular order.)
1) Prodlane: Female-led Prodlane Snaps €4M to Build an AI Assistant for Technical Teams.
Source: https://t.co/4FKy2DEtOr
2) deltaVision: deltaVision Raises €10.2M to Accelerate Orbital Refuelling Technology.
Source: https://t.co/bD9a0SroYV
3) Circular Materials: Circular Materials Secures €11.8M to Scale Critical Raw Material Recovery Technology.
Source: https://t.co/7arUwypAwn
4) 30 Sundays: Traveltech Startup 30 Sundays Raises ₹61 Cr To Expand AI-Powered Holiday Planning.
Source: https://t.co/geEPn4Na9W
5) Hilo @hilo_health: Hilo Raises $19M Series B Extension for Fitbit-Style Blood Pressure Health System: Can it Replace 145-Year-Old Cuff Technology?
Source: https://t.co/qeNZbEHJxL
6) Cascade: AI Engineering Project Predictor Startup Cascade Wins Backing from a16z Accelerator.
Source: https://t.co/8U5HnWTQjf
7) Dimension Capital: Dimension Capital’s $800M Third Fund Shows the Intersection of Science and Compute is Booming.
Source: https://t.co/IZCgPHX6Fx
8) Omio @omioglobal: Harvard Graduate with Indian Roots Secures $10M for Omio to Bring AI Multimodal Travel to Japan and Southeast Asia.
Source: https://t.co/8DQIYnAWQn
9) Ossprey: Ossprey Secures $2.65M to Stop Software Supply Chain Attacks.
Source: https://t.co/cTvNCBBNQc
10) Deutsche Sanierungsberatung: Berlin’s Deutsche Sanierungsberatung Raises Over €10 Million to Accelerate Climate-Neutral Home Renovations.
Source: https://t.co/NPBRHgArkh
Ossprey has seen 22 NPM packages scoped to marketfront delivering a secret / environment stealer similar to another campaign we covered a while back.
https://t.co/TbExozx51l
The marketfront packages are using the following C2 for exfil.
C2: https://pik-libs[.]ru/api/v1/events
Today, Ossprey Security detected 4 NPM packages being published by the DPRK.
This is the story of how Ossprey Security detected and disrupted a massive on-going DPRK malware campaign.
https://t.co/xmZedKIdcz
The [email protected]
This package was rapidly removed from npmjs, but the C2 may be re-used, we recommend pre-emptively blocking 138[.]201[.]140[.]23, and blocking jsonkeeper[.]com, as although this is safe, it's increasingly being used to exfil data.
Process 4 is the most destructive: downloads a trojanized MetaMask build from port 4553, extracts it, patches ui-20.js, rewrites Chrome Secure Preferences, and kills/restarts Chrome. Replacing the legitimate extension with an attacker-controlled wallet UI
🚨Ossprey detected [email protected], a malicious npm package that installs a remote payload from jsonkeeper, hijacks MetaMask in every Chrome profile, and exfiltrates wallet extension data and seed files to 138[.]201[.]140[.]23. Remove it and rotate credentials immediately. #supplychainsecurity