Lost my phone at the office and spent 30 minutes turning the place over. Find My was disabled by MDM.
Out of ideas, I asked Claude how I could find it. It suggested tracking the Bluetooth signal strength, then wrote me a meter in about a minute.
I walked around watching the number climb. Found it.
Apparently you can just make the tool you need now.
Code: https://t.co/fmnISzHfZ2
Quick Linux Trick:
Server load so high you can’t even SSH in?
👉 Use this command;
ssh -o ConnectTimeout=1 -o ConnectionAttempts=1 user@host "nice -n -20 bash"
It gets you a high-priority shell when nothing else works.
Following the @volatility parity release, VolWeb v3.15.0 is now available with some new features like Linux “Explore” support.
Checkout the release note here: https://t.co/IJEmVxGQnW
Project: https://t.co/CC54A8d1gm
#DFIR
Just completed the #CloudHuntingGames by @Wiz_io! 🚀 It was a challenging experience exploring Cloud IR. Think you can handle it? Take on the challenge here: https://t.co/14ELgCSfP4
🕷️ BLACK WIDOW NEVER WENT IN WITHOUT A PLAN.
You shouldn’t either.
🚨 FREE WinFE User + Train-the-Trainer
🎯 Learn to build and defend your forensic boot environment — the foundation of every solid case.
💥 $0 until May 14
🧠 Because in digital forensics, your acquisition is your attack plan.
👉 https://t.co/Y4jX3OIjLU
#DFIR #WinFE #DigitalForensics
🐧 After 6 months of research, my 5-part Linux Persistence series is now complete!🐧
🧵 Full series below👇
1️⃣https://t.co/s6jQ3wUQLb
2️⃣https://t.co/XTxqKkJH8x
3️⃣https://t.co/K7Ea0GqD5r
4️⃣https://t.co/3K0thW3j4p
5️⃣https://t.co/8BalXKtqeQ
#Linux#Persistence#redteam#Elastic
🚨 THIS JUST IN: The ultimate #Linux guide is here!
Created by @4enzikat0r & @tazwake this must-have forensic poster is your go-to resource for detecting rootkits, tracking attacker persistence, & analyzing timestamps.
📄 Get your FREE copy! https://t.co/ej87CYkYc7
#DFIR
Hi #DFIR community,
I'm excited to announce that I have published my new forensic tool for analyzing journal data from #Linux file systems (EXT4 and XFS).
🔗 https://t.co/wL00XCehCO
This tool requires TSK's develop branch to recognize the XFS file system, so you will need to compile it yourself.
Introducing DFIR Labs: A 24-challenge series by internationally acclaimed CTF authors, tailored for professionals, researchers and students. Master DFIR, Malware Analysis and Threat Hunting through challenges designed to push your expertise to new heights
https://t.co/6lgoxMDt8f
18 hacking books. Name your price. Our Hacking 2024 @humble bundle is now LIVE. Support @ACLU & @EFF while leveling up your security game. #CyberMonday https://t.co/CQEG72mRm8
Just released MemProcFS-Analyzer v1.1.0 with various enhancements. Offline-Mode, Prefetch files, Microsoft Protection Logs, MemProcFS.log, 376 YARA rules, and much more. #MemProcFS#MemoryAnalysis#DFIR
https://t.co/dloOXji3tN
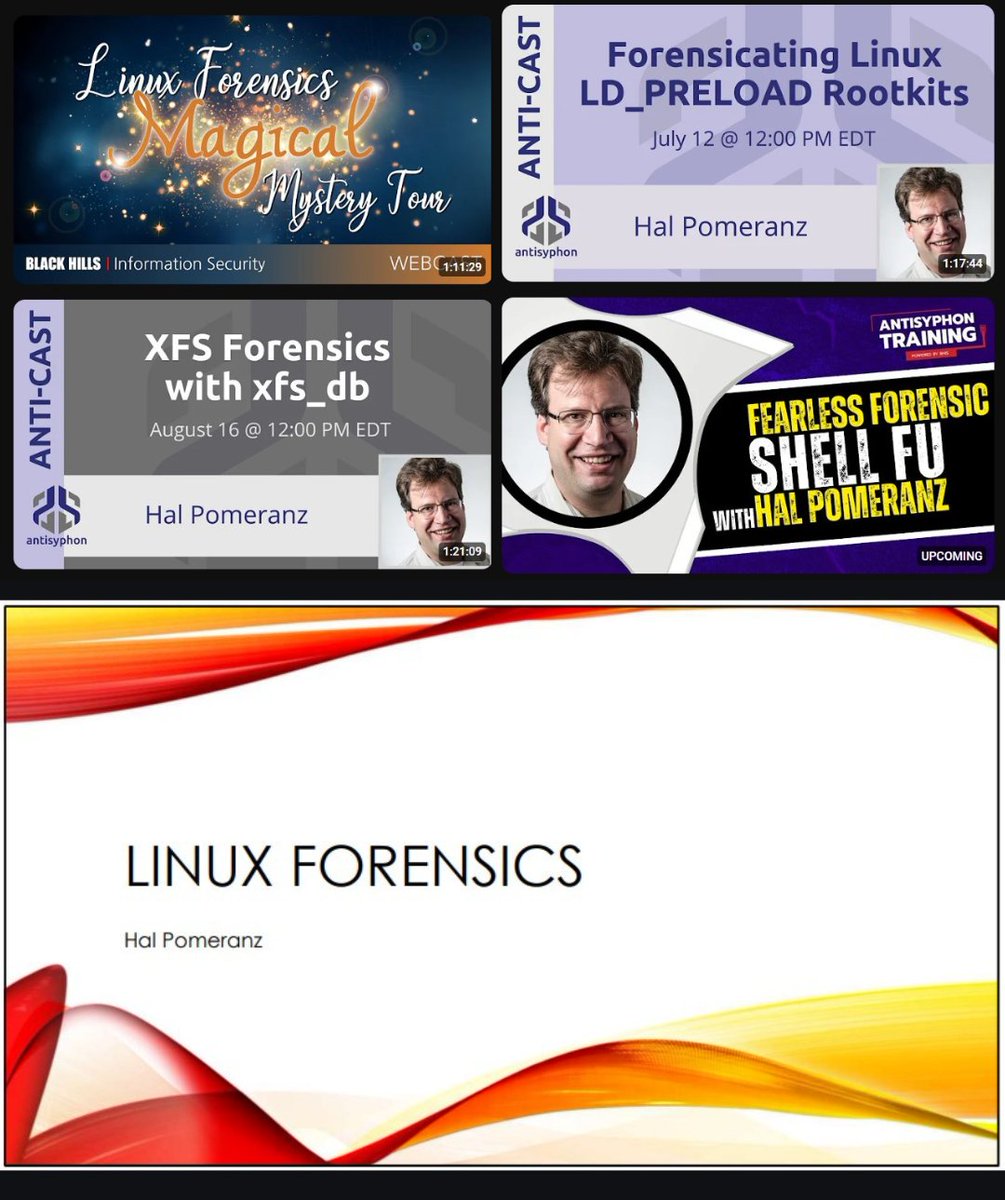
Today's Training Tuesday Highlight is @hal_pomeranz!
Want to learn Linux Forensics? He created a FREE hands-on Linux Forensics course: https://t.co/4t3Ft3pcJp
In addition, he's done several Linux Forensics webcasts with Black Hills Information Security, Wild West Hackin' Fest, and Antisyphon Training that are freely available on YouTube. One will be live next week!
Webcasts:
- Forensicating Linux LD_PRELOAD Rootkits: https://t.co/tXPhNMMzqa
- Linux Forensics Magical Mystery Tour: https://t.co/hDNIEqXGjh
- Linux Forensics Magical Mystery Tour II: It's All About the Logs: https://t.co/ixMl3IGGcT
- XFS Forensics with xfs_db: https://t.co/AfmLz7lGCE
-All About Linux Systemd Timers: https://t.co/IOwgeUaXbZ
- Fearless Forensic Shell Fu (Live on August 28th): https://t.co/7JUcmxQJh5
He also has paid courses with Antisyphon Training:
- Linux Forensics w/Hal Pomeranz: https://t.co/9GOqUOvfSv
- Linux Command-Line for Analysts and Operators w/ Hal Pomeranz: https://t.co/R91jhI2EXA
Check out his blog for even more resources: https://t.co/Gp6nueuuii
#DFIR #DigitalForensics #LinuxForensics #IncidentResponse #DFIRDivaTTH