Part Time Infosec Strategist, Full Time Smartass. Devastatingly Handsome
Son, Husband, Father Love to see the world
Views and opinions expressed are my own.
Judges are known to treat cases before them differently depending on various factors, including such weird ones as the hometown team having lost a recent game. So, biases are implicit and need watching out. #MachineLearning#ExplainableAlgorithms https://t.co/NH9NyUNacn
Whipped up a new blog post: "Docker for Pentesters". Docker has completely changed my workflow, and I wrote up 10 examples and scripts for how pentesters can leverage Docker to speed up testing. Lmk how you use Docker - this could be a series! https://t.co/q9IeHqzMln
DNS over HTTPS is a positive step towards privacy, and you should be suspicious of anyone interested in impeding it. Intelligence and law enforcement have to cope with changing protocols. https://t.co/PT8YDpsrF4
Ooh I got one better https://t.co/ZodwxfmxMr
OMG drag and drop parts to the board, it auto-loads the breadboard layout and gives you the code and a parts listing!!!! It greys out what can't be put there and allows you to swap it out.
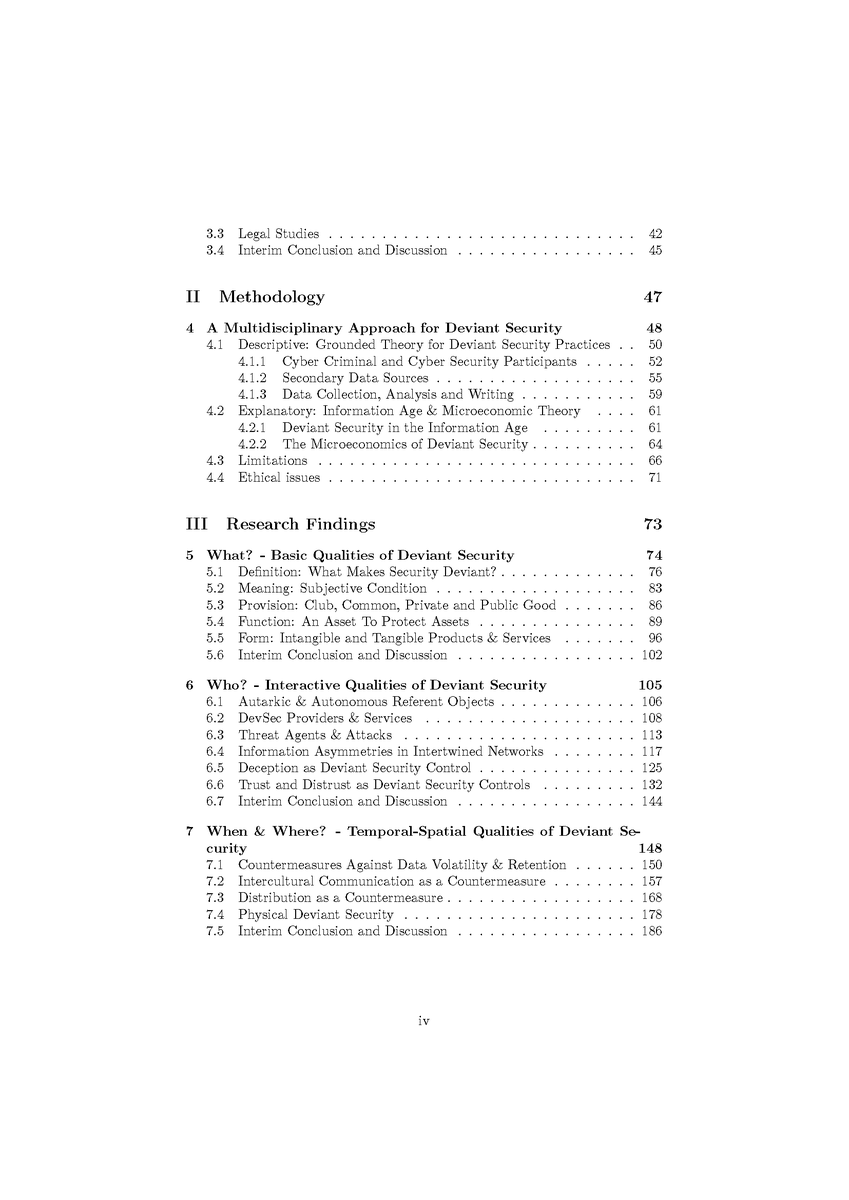
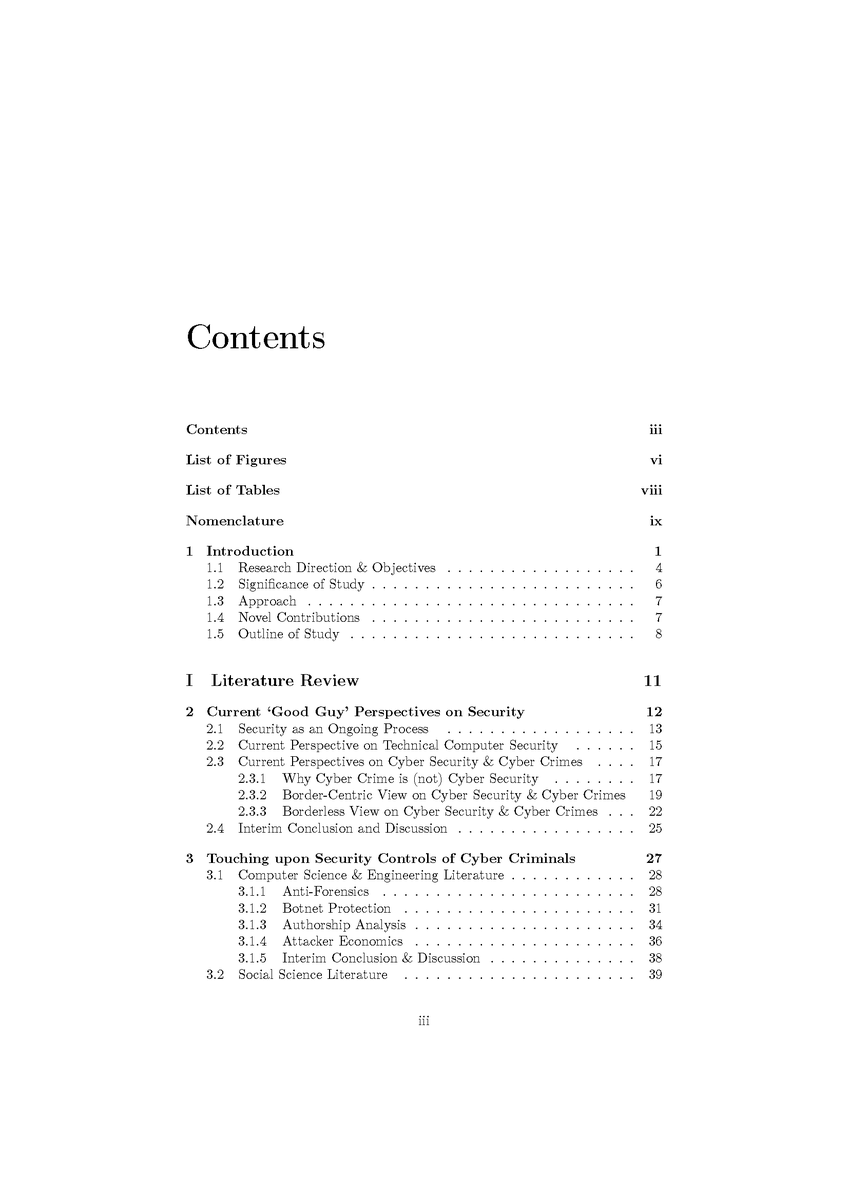
PhD thesis (2019): "Deviant Security: The Technical Computer Security Practices of Cyber Criminals", by Erik van de Sandt / @BristolUni (16MB .pdf, April 2019; 311 pages) https://t.co/SA2gWlhxoY HT @John_Fokker /c @_cryptome_@thegrugq@krypt3ia
This is huge! Cloudflare now offers a global NTP service at https://t.co/ccEwmyQTrv. It supports NTP and authenticated time via the new Network Time Security (NTS) spec. Authentication keys are established over TLS 1.3 on port 1234.
https://t.co/XSPNXKnWVX
Along these lines, on pentest engagements we occasionally have a client that is served by the same MSP as a previous client of ours. We often find that MSPs reuse credentials cross-client and we can use the old to hack the new! https://t.co/6HgI1WQt2k
Data storage is cheaper than its ever been but it still isn’t free. If you’re paying to store data you don’t use, you’re wasting money and opportunities to leverage that data. By understanding your data, securing it you maintain regulation & drive value. https://t.co/tmtt7VbWcm
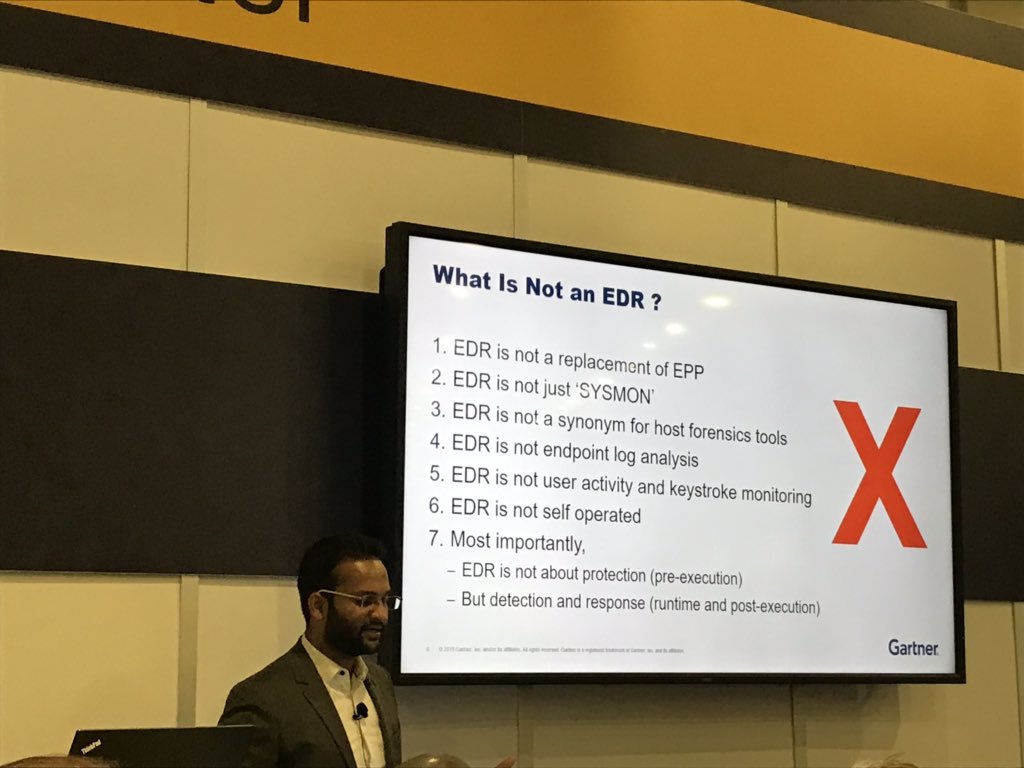
Nice conceptual explanation about new @MITREcorp ATT&CK framework and how to use it to think through risks and how to mitigate risk to shift risk to the left (more left means you have more time to avoid crisis mode) #GartnerSEC @Gartner_IT
It's time for @haveibeenpwned to grow up and go beyond what I can do as one person. This has taken a lot of thought over the course of this year; here's the factors driving it, the path forward and what it means for the future. Here's Project Svalbard: https://t.co/ZeRtzfCTA2
There are now at least 3 security products with "Sentinel" in their title. First there was SentinelOne, then Microsoft released Azure Sentinel, and now I see there is Barracuda Sentinel. The use of such a distinctive word in unrelated products is bound to confuse customers.
Evil Clippy: our new tool for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse many macro security analysis tools. Read our blog post for details: https://t.co/fhcyochzBg