🧠 BREAKING BITLOCKER — Early Bird ends Nov 3! 🔥
Our seasoned Black Hat training (3 years at BHUSA) returns to the classroom in Zurich — battle-tested in countless LEA cases. Learn real BitLocker bypasses hands-on: TPM sniffing • DMA attacks • bootloader patching. Practice micro-soldering, attach probes to internal buses, and extract BitLocker keys from RAM and elsewhere — everything you need to go beyond standard interfaces.
🛠️ Includes full hardware kit & prepped test laptop
💰 Early Bird CHF 2999 (regular CHF 3499) — until Nov 3
📍 Zürich · 📅 29–30 Jan 2026 · 🔗 https://t.co/R3JNuuZS4N
#BitLocker #DigitalForensics #LEA #Cybersecurity #RedTeam #TPM #DMA #HandsOnSecurity
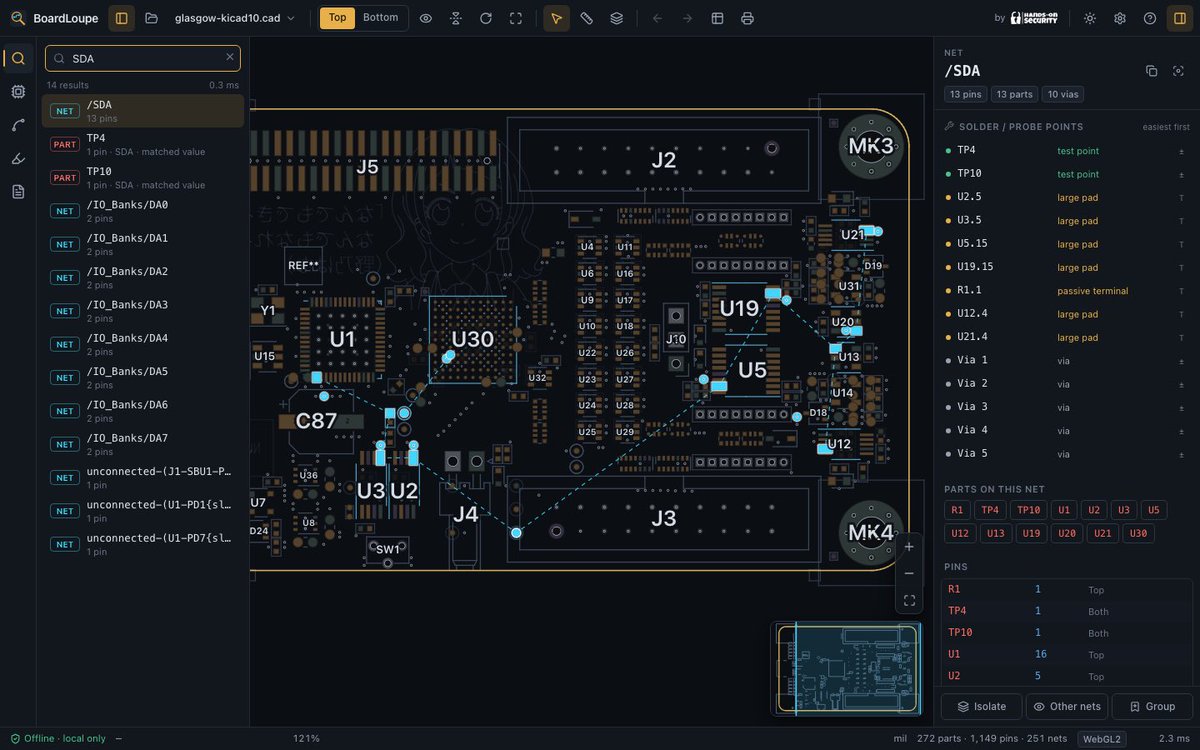
🔍 One loupe to find the chip. Another to follow the signal.
Meet BoardLoupe — our new open-source boardview tool for hardware hackers and reverse engineers!
Already being put to work by students at our Breaking BitLocker training in Zurich. 🔬💻
🔗 https://t.co/9yxBsxNdMU
#HardwareHacking #OpenSource #DigitalForensics
‼️BREAKING: Hackers are planting webshells on Nextcloud servers through a critical Collabora flaw.
CVE-2026-110447 in the built-in CODE Server app lets anyone run commands without logging in.
Collabora says update to 26.4.303 or delete it.
@SipeedLab Impressive specs! 😎 Any plans to support GlmMoeDsaForCausalLM (GLM-5.3) on the 512 GB Pro? That would be a seriously interesting local inference machine! 🥳
@kimocoder Nice catch! 😄 Curious how you managed to get the source code. Prompt injection against an AI-powered bot, or a more traditional injection vulnerability?
@en4rab@lowercase_drm@craigsblackie@NoobieDog@ghidraninja the problem is that there are usually resistors very close to the tpm. If you could make the needles angled, you might be able to succeed, but honestly: Quickly solder those 4 pins and a GND isnt that much work… 😇
Here is a close up of the TPM in bordview for your Lenovoy The relevant pins are highlighted:
spi clk -> resistor
spi cs -> test pad left
spi mosi -> test point between tpm and resistor
spi miso -> test point between tpm and resistor
Slightly less convenient to solder and especialy annoying as its on the bottom side of the board - but with a little patience doable…
I therefore revise my previous message and wouldnt do 1) first but 2), as 1) has slight more risk of breaking the device.
I‘ve seen similar treatment on other boards but more consequently on all parts…
I‘d try:
1) Hot needle - like really hot and see if it melts through. If it does, just connect like this
2) attach to the bus elsewhere - get a reference device or the schematics online. With the latter I can help, just DM me the model…
3) grinding with a CnC - but be super careful. Only manual steering…
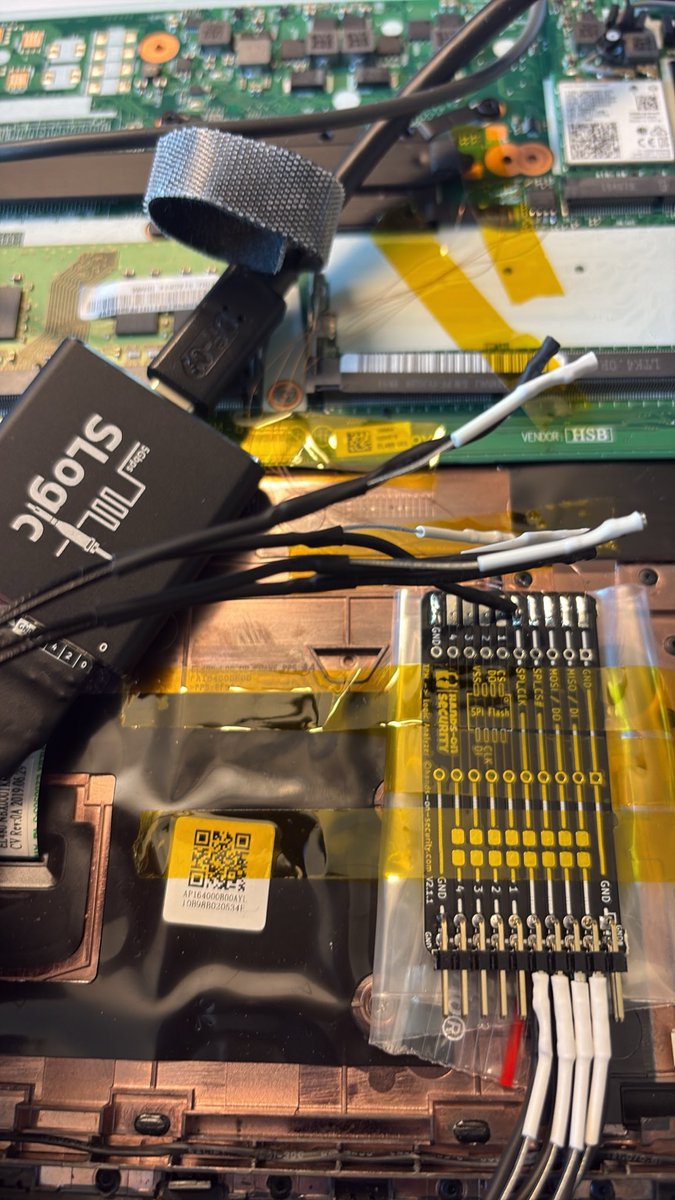
Apparently our use case made it into the promo video! 🥳😎
If you want to get an SLogic16U3 and learn how to break BitLocker -> Join our hardware hacking training „Breaking BitLocker“
https://t.co/Kn4PjkFvxU
(yes in the picture is still the DSL but we upgraded to SLogic recently…)
Just made a promo video for #SLogic32U3 entirely with AI — vector art, animation, even the soundtrack. 🤖🎬
How does it look?
Not following yet? Now's the time — the $99 10 Gbps logic analyzer is a limited run. ⏳
Launching in 2 days!
https://t.co/ZC2NNfLkP8
@SipeedLab@en4rab Wait, $700 for the whole setup? 😳 What exactly is the “small DR” you’re using - model / sensor size / pixel pitch? And is the 60 kV source something off-the-shelf too?
🔓 Your first hardware hack might end with a BitLocker key.
For many students, Breaking BitLocker is their first time:
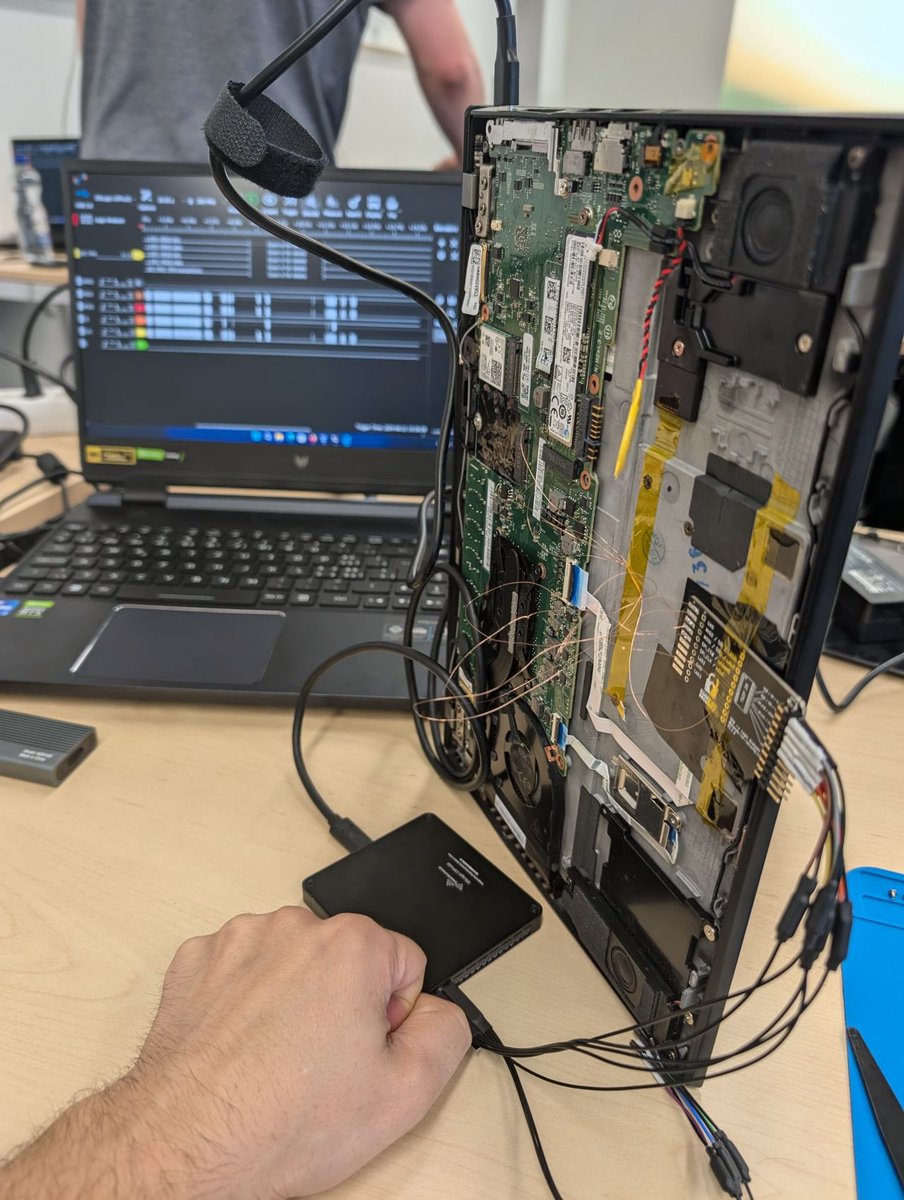
→ opening a laptop to find attack points
→ microsoldering onto a PCB
→ connecting a logic analyzer
→ watching TPM traffic on a real hardware bus
→ extracting the key that actually unlocks the disk
That moment when random electrical signals suddenly become understandable data — and then a BitLocker key — never gets old. 🔬⚡
This December we’re bringing the latest Breaking BitLocker to Black Hat Europe 2026 in London 🇬🇧
And we’ve made the hardware side even more accessible.
We built our own LPC + SPI decoders for PulseView, so instead of treating the logic analyzer as a magic box, you can actually SEE the communication, understand it and watch the attack unfold on the bus.
Over two very hands-on days:
⚡ TPM Bus Sniffing
⚡ LPC/SPI logic analysis
⚡ BitLocker key extraction
⚡ DMA attacks
⚡ Bootloader-based attacks
⚡ Current BitLocker research & mitigations
⚡ Most importantly: understanding why an attack works - and when it doesn’t
No previous hardware-hacking experience required.
🧰 All attack hardware + adapters included
💻 Prepared target laptop included
🔬 You perform the attacks yourself
🎒 And the equipment is yours to keep afterwards
One important thing: we still need additional Early Bird registrations for the Black Hat class to go ahead.
So if Breaking BitLocker has been sitting on your training wish list, don’t wait for regular registration - there may not be one.
👉 https://t.co/2xrm5Cywso
Know a forensic practitioner, pentester, security researcher or LEA colleague who should finally cross the software/hardware boundary?
Send this their way. Let’s get another group around the workbench at #BHEU. 🔓🔬
#BlackHat #BitLocker #HardwareSecurity #DFIR #TPM #InfoSec
It does… 😎
It‘s pulseview and these decoders are compat… ah you‘re just fooling around… 😂🫣😇
I just ordered 22 pcs for our upcoming training and will order some more for @BlackHatEvents #BHEU in London…
I like them bc they are so small.
I don‘t like their lack of labling the probes. Will do this for the students manually… 🫣😇
@theluemmel@lowercase_drm@en4rab Just get this one by @SipeedLab and you‘re fine 😉:
https://t.co/s6SNIoZ16x
We used to give away @DreamSourceLab ‚s U3Pro16 but I‘ve just found the SLogic16u3 to do the job. The software needs some tweaking, but I plan on releasing my decoders from the #BHEU Training soon… 😎
🚨 Plot twist in digital forensics:
The CEO of Oxygen Forensics and a Russian national have been arrested after allegedly hiding Russian ownership - while selling forensic software to the U.S. government.
The DOJ says the same Russian owners also sold the software to customers including the FSB. 👀
57 domains seized. Extradition pending.
This one is wild. 🍿
🔗 DOJ: https://t.co/bIFFGCRHdI