So… I was hacked. Pwned. Big time. And I’m not kidding.
It turned out to be the very same malware used in massive DDoS campaigns against DeepSeek and Twitter (erm… X).
It was RapperBot... I was angry with me and with the malware. Honestly, more with me than with the malware.
This is my story of how I dove deep into its guts, from infrastructure mapping to binary analysis, and what I uncovered along the way.
Buckle up and grab some IOCs:
https://t.co/rTsumLwcuR
Casey is by far one of the best C-levels in our industry bar none; definitely listen to what he is saying about this landmark case.
If you haven't heard, take a few minutes to read this and then go find out just how important it is.
It’s #defconsafemode 🚨 alert 🚨 time again! The main track talk schedule for #defcon28 is now #live! Permission to get psyched is #granted. More announcements on the way!
This. Is. Happening.
https://t.co/hnJvVEVWgP…/defcon-s…/dc-safemode-schedule.html
@defcon's @AppSec_Village#CFP is closed, but you have another chance to influence the quality of talks!
Is there a speaker from our #AppSec ecosystem that you want to hear? Let me know here, or by DM. We will do our best to convince them to submit.
Our operators are standing by!
@osxreverser If you’re looking to keep local copies of modules I suggest using https://t.co/8YA1oMwKbs , it has worked very well for me. A regular build went from >3min to 35s just from grabbing the code locally. Forked and modified code probably requires a git server.
Today was my last day of work at Cruise :( . I’m part of a lay-off :/ So yah... looking for work. I know the US is at a crazy unemployment rate and probably very few are hiring but if you know of anywhere looking to add to their internal red team, security trainer, SMB CTO/CISO/
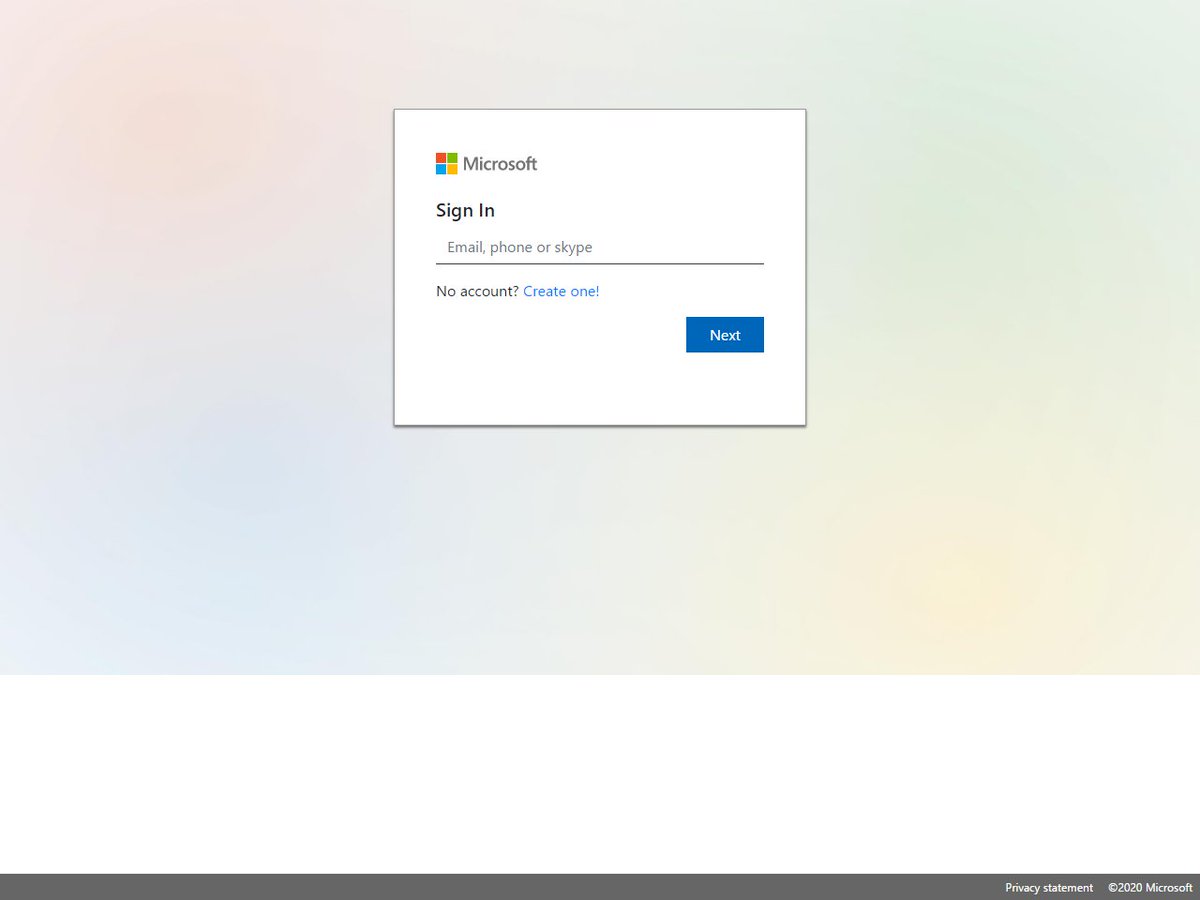
Office 365 ATP data shows that attackers have started to spoof the new Azure AD sign-in page in multiple phishing campaigns. We have so far seen several dozens of phishing sites used in these campaigns.
If you are a student who is stuck at home + ur studies/life disrupted by quarantine and want to continue your infosec learning path, register for a free account on edu email on @binaryedgeio join our slack, DM me and ill give u extra credits for free+full access.
Bewildering research by @DorTumarkin resulted in @ApacheDubbo's RCE, CVE-2019-17564, and an excellent write-up!
https://t.co/FHzSuHSCyt
Having #AppSec fun @Checkmarx.
The long-awaited Black Hat Go is releasing on 2/4/20! If your shipping address has changed since you ordered the book, please email [email protected]. And if you haven't ordered the book yet, there's still time to get 30% off a preorder at https://t.co/FdkF4x1jGS! #golang