Pleased to be sharing publicly OpenASM.
Besides the outstanding personal learning experience in Django, Python and software design, I trully hope it helps resource-constrained security teams managing a security program.
https://t.co/UYfyVUdtvE
It's always fun to hunt for bounties! Or is it not? This is an LFI w/ screenshots to prove - no bounty, claiming site was shut down. And this message 😅 Wtf?
RCE in Monikerlink bug is unlikely if you update Office regularly. Still, very nice finding from @_CPResearch_ well described in their blog. Another card to play if you need to convince someone for the relevance of restricting outbound traffic and security awareness training.
Today, we're disclosing an overlooked, wide-impact bug/attack vector affecting the Windows/COM ecosystem, dubbed #MonikerLink. In Outlook, the bug's impact is far and wide: from leaking NTLM creds to RCE. The same issue may exist in other software, too. https://t.co/nfPDFJoCz6
Yesterday it was a blast to see everyone in IRL. Special thank you to our speakers @dsopas@jmoraissec@Pedro_SEC_R for their time and dedication. And as always, a big shout out to @blip_pt that supports our community since the beginning, and to @Doyensec for giving us freebies.
⚠️ #ThreatIntelligence
Checkmarx Labs researchers found that the Ring Android app could've allowed a malicious application installed on the user’s phone to expose their personal data, geolocation, camera recordings. Here's our research: https://t.co/mD9CMRCh9f
#CheckmarxSecurity
It was a pleasure to work with the Amazon security team, who were highly professional throughout the process. For great collaboration, we're giving them the Checkmarx Seal of Approval. https://t.co/3hDbnlHP1h #appsec
The Rapid7 team has a root cause analysis of Confluence CVE-2022-26134 out now with thanks to @Junior_Baines. This is an emergency mitigation situation. https://t.co/2G9H6OmJA6
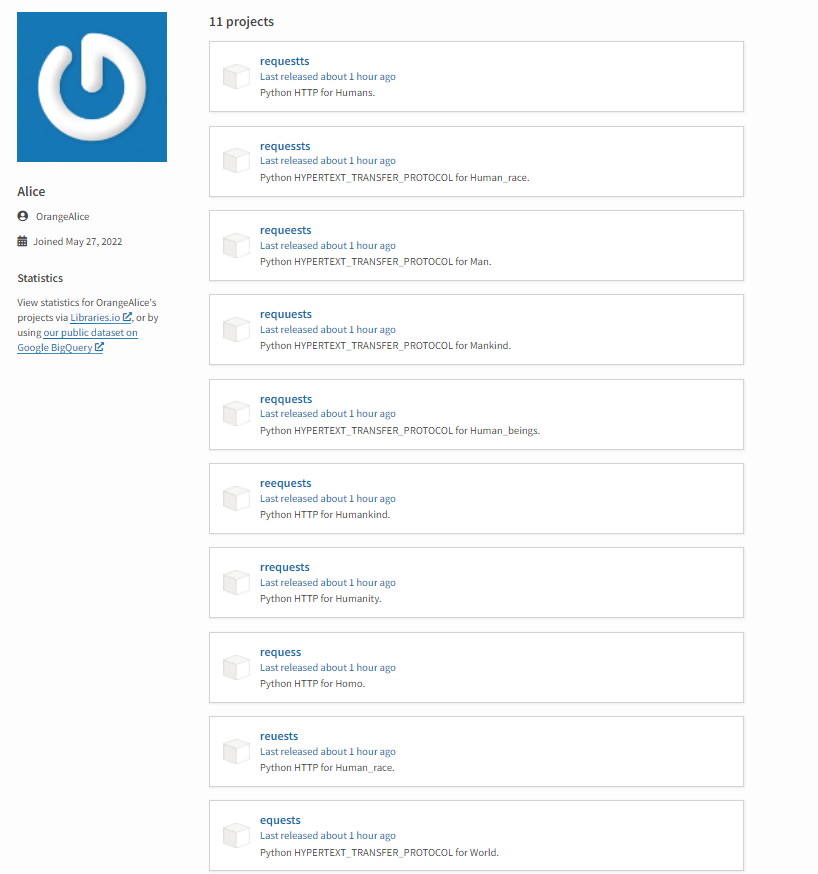
10 typosquatting packages targeting users of one of the most popular Python packages, “requests”, were detected in the past hour.
The packages, which were all reported to PyPi in less than an hour of their upload, try to infect developers with a crypto miner.
ROADtools is a framework to interact with Azure AD. It currently consists of a library (roadlib) and the ROADrecon Azure AD exploration tool. by @_dirkjan
https://t.co/t3sM3687aL
If you see two guys wearing Synacktiv t-shirts with big antennas, you should turn around with your @Tesla! 0-click RCE demonstration on a real vehicle, with CAN messages sent to switch on headlights, wipers and trunk 😎 #Pwn2Own
HTTP/2: The Sequel is Always Worse is coming out tomorrow! Featuring 9 months of research condensed into 40 minutes of raw HTTP/2 exploitation. You can watch the presentation live at both @BlackHatEvents and @DEFCON...
https://t.co/nOABdd12oZ
Hacking is 90% practice. There's no shortcut to working hard, learning to pwn web, binary apps, Linux, hacking tools, write assembly / C / Python / XYZ.
Only 10% of your time should be spent with books and in high quality courses.
So you want to be a hacker? Put in the work!