It's us again.
Today. It is on! Set your alarms, DisCo, friends!
🎟️ GA DistrictCon Tickets Live On Sale Nov. 22 @ 11:59am est! 🎟️
Get your tickets here! https://t.co/15nYwKeiFP
DisCo friends! It’s a weekend full of surprises! We are so excited to preview our confirmed #DistrictConY2 speakers with more to come soon!
Check out the details below 👇and get to know our community of hackers, builders and fixers bringing the #DisCoTogether on stage this year. 🪩
https://t.co/lPQlenRmFj
🚨DisCo’s got something for y’all! 🚨
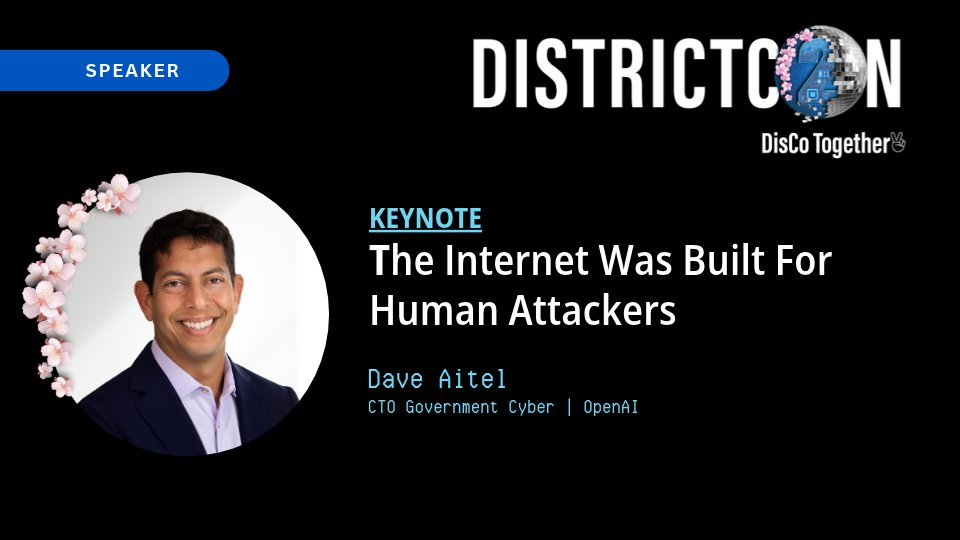
Announcing DistrictCon Keynote Speaker: Dave Aitel, CTO Government Cyber at OpenAI. Expect the unexpected, and hard truths during Dave’s Keynote “The Internet Was Built for Human Attackers.”
Meanwhile, DistrictCon is building and fostering a community where we are better together! Let that be your reminder that tickets go live Sunday, November 22nd @ 11:59 AM! 🪩
Make sure to bookmark our page https://t.co/Le3shq1hJ7!
#DisCoTogether
We built a vulnerability research pipeline, using an upcoming cyber model, to analyze the security of the Linux kernel. Besides finding and exploiting the found vulnerabilities, the agents discovered at least 10 new exploitation techniques that were new to us and some external kernel exploit experts we checked with.
More on the design and what we learned: https://t.co/SGZXwSRwxU
A lot of the folks building this, like @ky1ebot and @itszn13 had a lot of experience building autonomous vr tooling before it was cool. This is great work from them
It’s awesome to see how far we’ve come in autonomous VR and patching. 5 years ago, it was easy to feel cynical about the future of this space, because pipelines had to be so overfit to the software target, and were so brittle to target changes/idiosyncrasies
Our security researchers built an autonomous cyber vulnerability discovery, exploitation, and patching pipeline.
In a single run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation vulnerabilities in the Linux kernel at a total API cost of $1.2 million.
I’m very, very excited to announce that @dartmouth professor and former @DARPA pm @sergeybratus will be giving the opening remarks tomorrow morning to kick off Vibecheck, the formal methods hackathon!
About a decade ago, I went to Sergey’s office and told him I wanted to be a hacker and I loved math. He told me to drop my EE major and switch to pure mathematics — the best foundation for a real hacker. He also gave me an enormous book by Dennis Yurichev on reverse engineering, which meant that hilariously, I was reading about linker/loader internals before I’d ever even tried building a compiler. In fact I learned about C reverse engineering before I learned C. (Not claiming I was any good at it, just that my sequence of exposures to the topics was comedic ..)
Sergey is known for many things but maybe the most fundamental is the co-invention of LangSec, the field of cybersecurity which posits that many — well, most — exploits are in fact parser vulnerabilities, and therefore security should be approached from the perspective of formal language theory. This insight has proved incredibly prescient, predicting vulnerabilities like Pegasus, or more recently the incredible node exploit. But it’s also prescient in another way. More philosophically, we have these language models generating code, and no good way to parse their outputs to determine if the code is safe or not. If you’ll allow me the slight stretch of the formalism I think this is basically a LangSec issue .. and the solution, AI enabled formal methods, is basically a parser innovation. Modulo how do you find specs, which of course is a more nuanced conversation involving HCI and more.
We will have many experts on the floor at vibecheck from folks like @mathematics_inc@theoremlabs@workersio@lanyon_ai and more. But I couldn’t think of anyone I’d rather have open the event than Sergey. See you all at 10am @thegp !
Amazing keynote by @perribus at @SAINTCON. Incredible presentation about “The Eighth Plague”, the overwhelming number of bugs being found with AI and how finding a vulnerability doesn’t always mean easily exploiting a vulnerability and what that means for defense and response. #saintcon
First Keynote of @saintcon with @gdead. He claims it’s gonna be Grandpa Simpson being the old man shaking his fist at a cloud, but I’m thinking we just might learn something. #saintcon
php2shell is the most consequential vulnerability I have ever helped discover. I am proud of how our team worked closely in coordination with the PHP Foundation to provide support and to harden the patch in preparation for this release. Please read more about our approach: