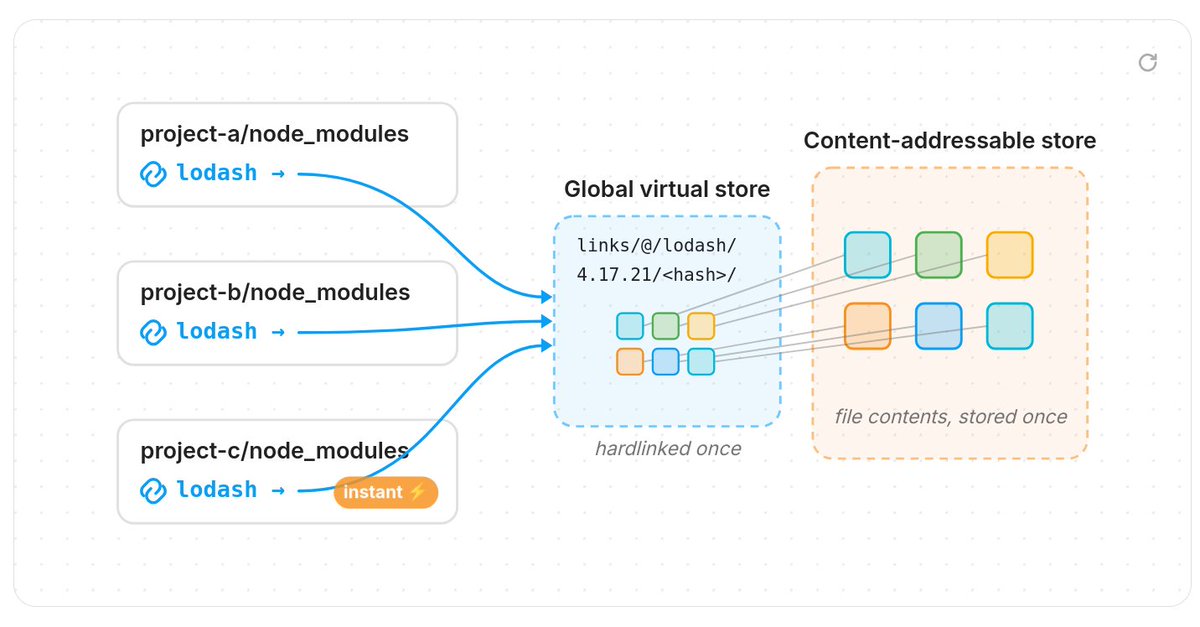
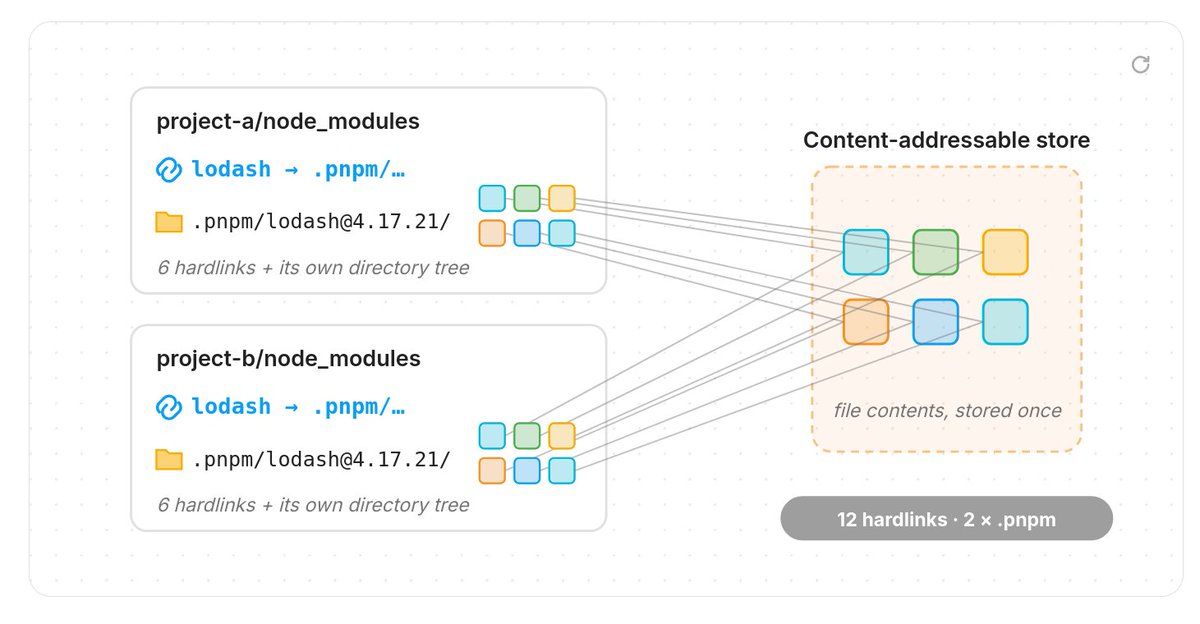
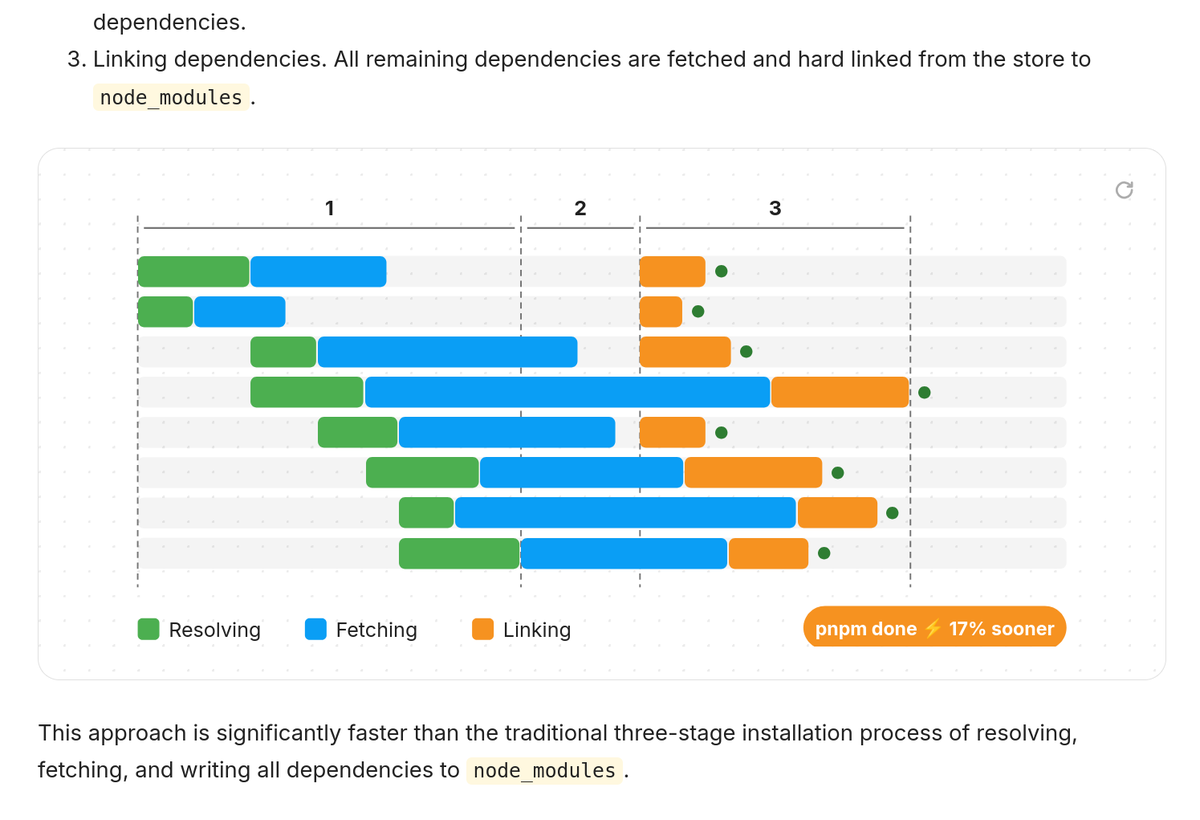
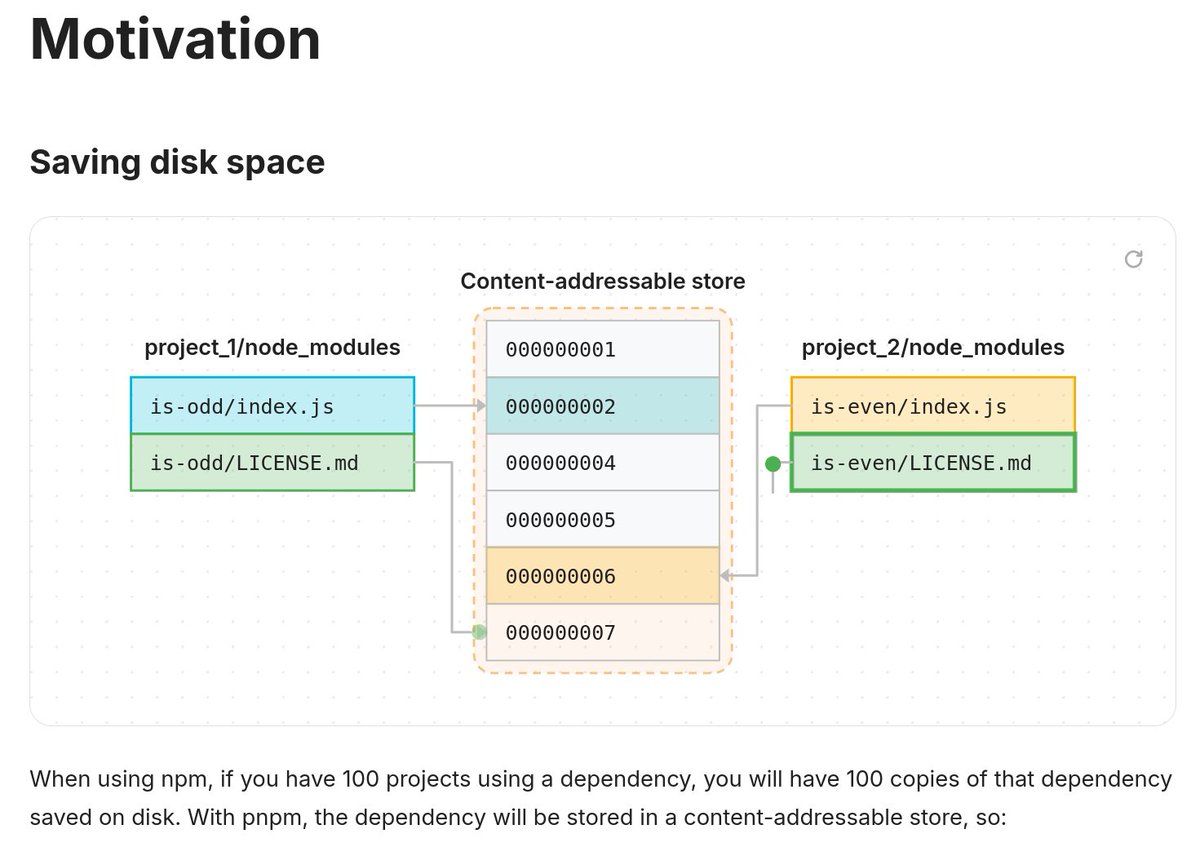
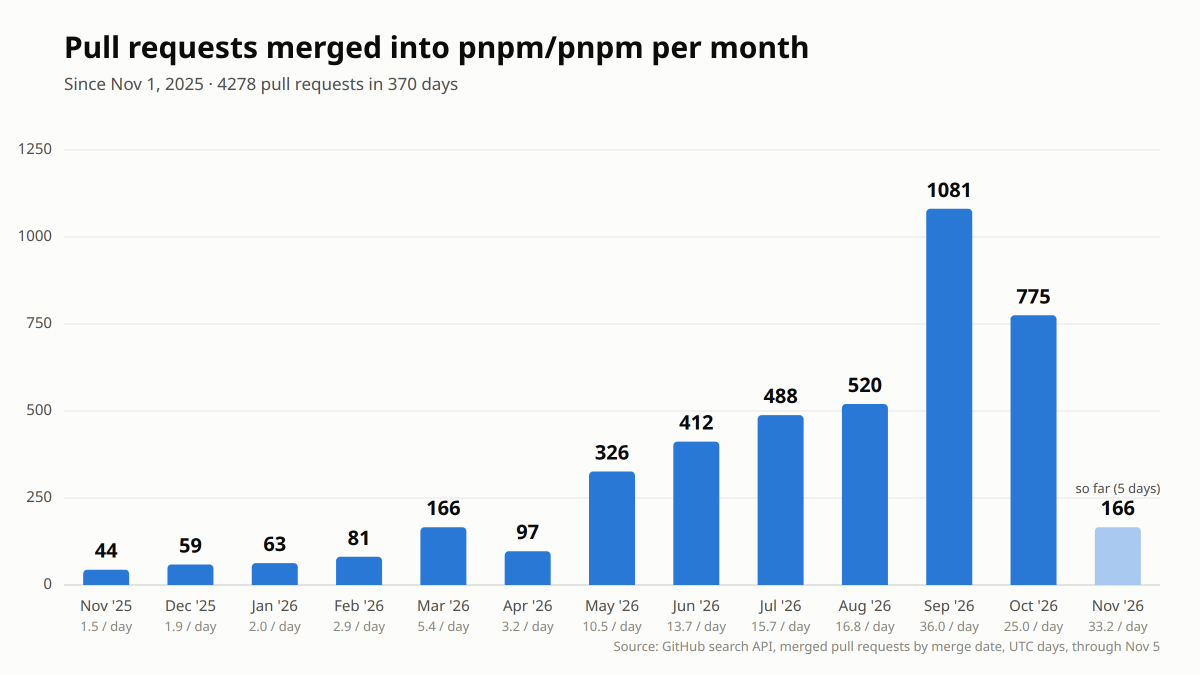
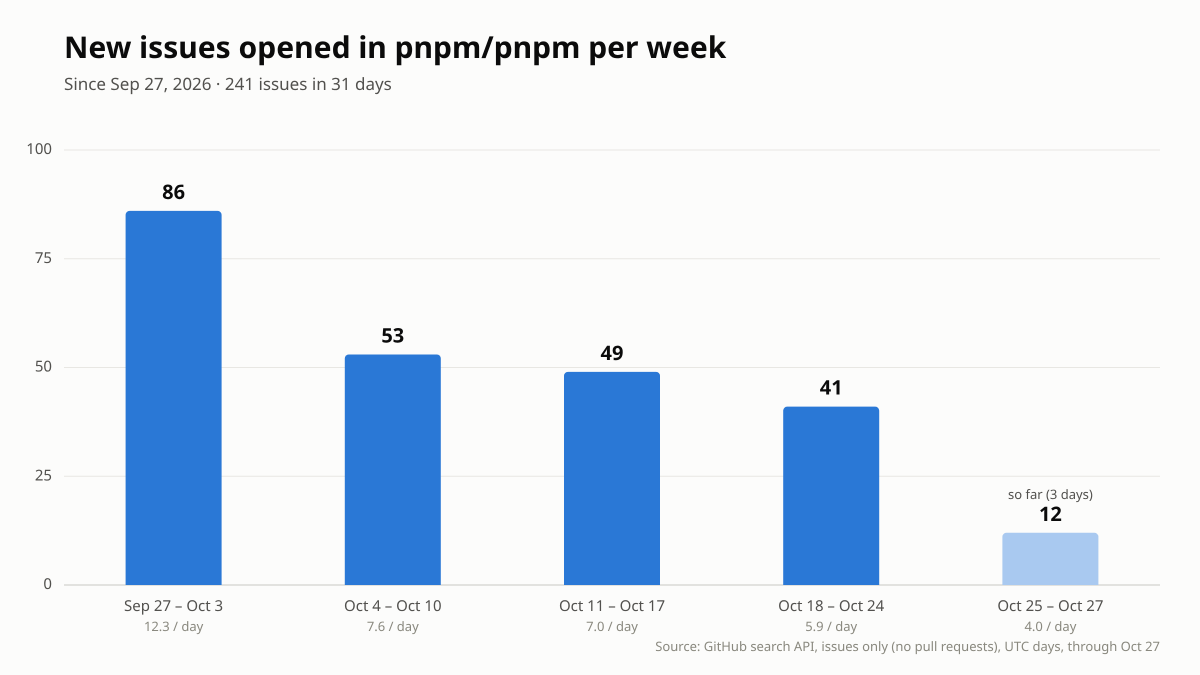
A full month has passed since we committed to the zero open issues policy in the pnpm repository. The number of new issues filed per week keeps going down.
New in CodeRabbit Secure:
Deep Scan now follows a vulnerability across your linked repos, then replays the exploit in a throwaway sandbox to prove it's real before it flags anything.
Hendrik walks through this and everything else in the new update:
@tomus_sherman Yes. 12.15.0 picked up rustls-webpki 0.103.16 and webpki-root-certs 1.0.10, which distrust the eMudhra intermediates and remove the emSign ECC G3 root. It came in as part of a dependency refresh, so it didn't make the notes.
@sequoia is leading our Series C at a $1B valuation.
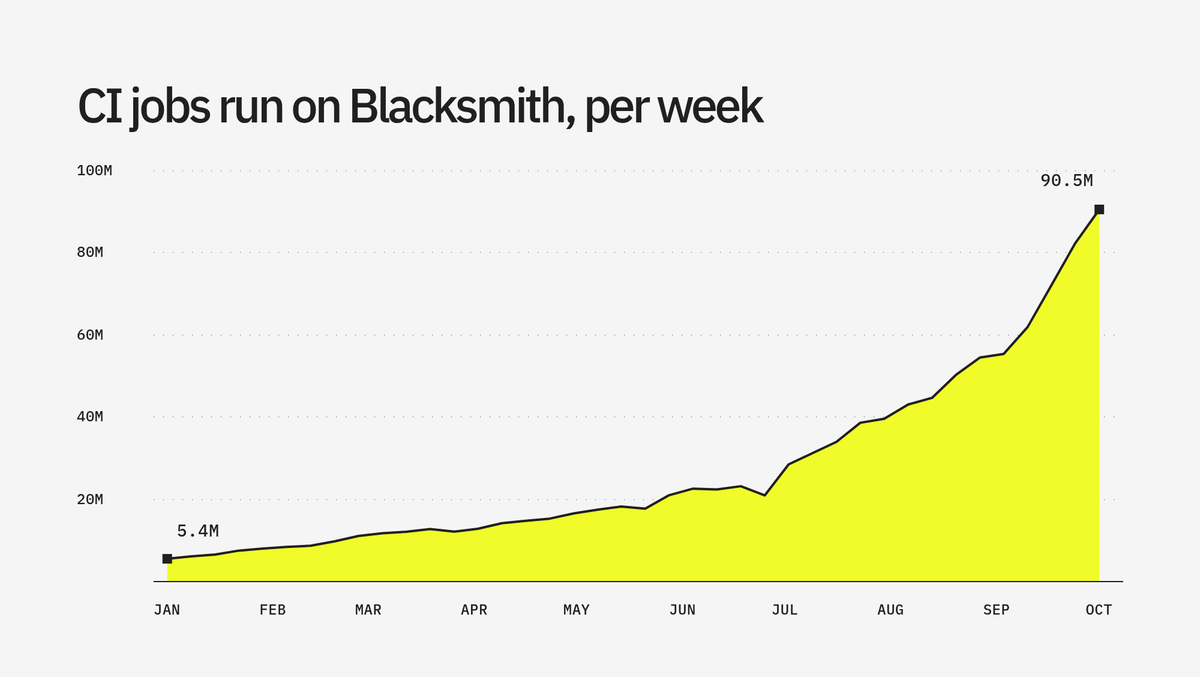
We started Blacksmith in 2024 to make CI faster and less painful. In January we ran 5 million CI jobs a week. Today it's over 90 million and growing, and we’re still early.
Update pnpm to v12.15.0 if you want to be able to split settings across files. For instance, you can move security policies to a protected file.
https://t.co/qzFBxe8qJW
New pnpm RFC for anyone interested: the possibility to load settings from multiple config files. This would allow to control who can change specific settings via git policies and similar toolings
https://t.co/x5y1J8iEzU
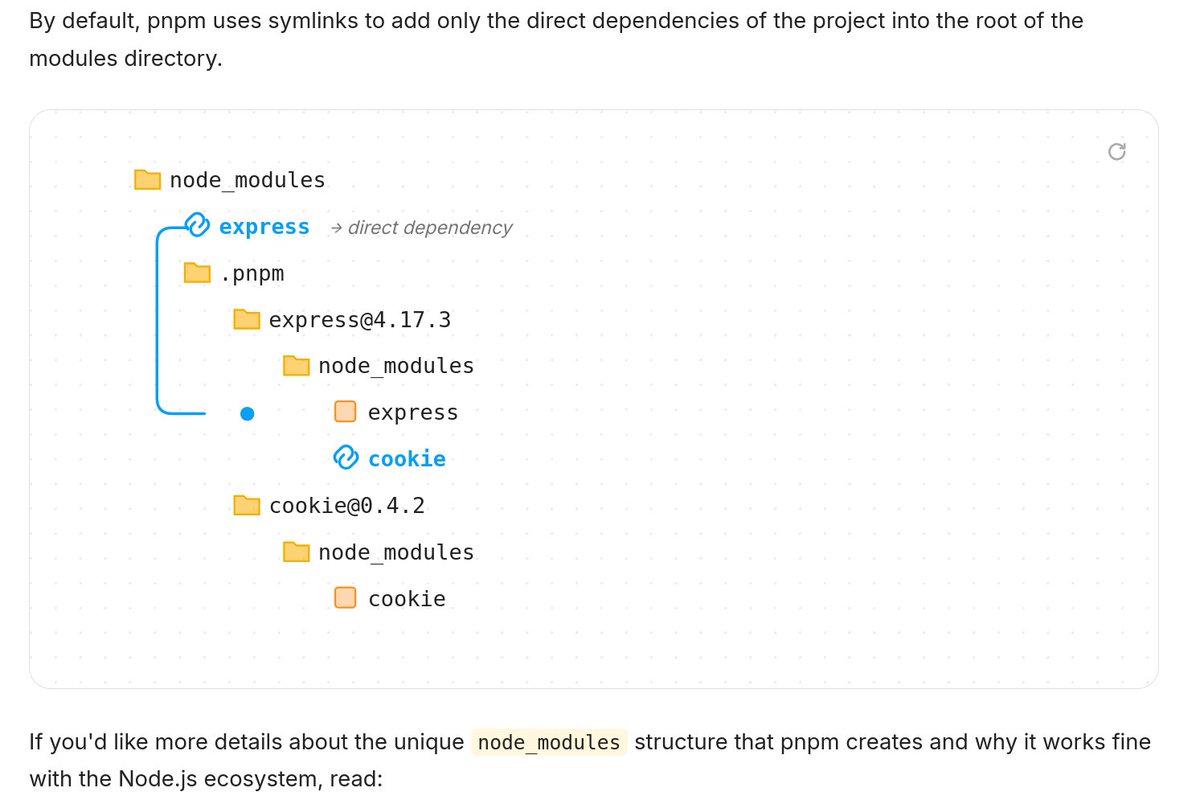
pnpm can now work with no node_modules, leveraging the esm loaders of node.js. Doesn't work with typescript and other toolings that inspect node_modules but works with bare Node.js. Related docs: https://t.co/ZynabKws7v
1,049,817 open-source code reviews in September, a new monthly record!
That's 2.49x April's volume and up 14.4% from August.
"Not using it today would be like racing Formula One without a seatbelt or helmet." – @tannerlinsley, creator of TanStack