🚨 LOTTunnels — LIVING OFF THE TUNNELS 🔥
🔥 Telegram: https://t.co/upuP8k8ckB
✴️ Twitter: https://t.co/Za7rYILz6E
Attackers don't always need custom infrastructure.
Sometimes, legitimate tunneling services can become part of the attack chain. 🌐⚔️
LOTTunnels is a community-driven project documenting digital tunnels that can be abused for:
🔹 Access
🔹 Shell Access
🔹 Data Exfiltration
🔹 Persistence
🔹 Phishing
🔹 Payload Download
The catalog includes tools/services such as:
⚡ ngrok
⚡ Cloudflared
⚡ https://t.co/0p5W7wIUmY
⚡ LocalXpose
⚡ PageKite
⚡ Pinggy
⚡ Serveo
⚡ Tmate
⚡ TunnelTo
⚡ VSCode Tunnels
🎯 Why should Red Teamers & Defenders care?
Tunneling can create legitimate-looking network traffic while providing paths for remote access, command execution, or data movement.
For defenders, these services should be part of attack-surface discovery, detection engineering, and network monitoring.
🔗 Explore LOTTunnels:
https://t.co/NavsvQ5z4s
📌 Bookmark this resource for your next Red Team / Blue Team / Threat Hunting research.
⚠️ Use these techniques only in authorized environments.
♻️ REPOST & SHARE with your cybersecurity community!
#LOTTunnels #LivingOffTheLand #CyberSecurity #RedTeam #BlueTeam #ThreatHunting #Pentesting #C2 #NetworkSecurity #InfoSec
📌 From Exposed Infrastructure to Nuclear and Naval Targets
Two weeks ago, we published one of those investigations that’s worth coming back to.
Attack Capture surfaced an open directory containing custom scripts, offensive tooling, and stolen data tied to a Philippine nuclear research body and a marine engineering company serving the Philippine Navy.
The activity involved known ownCloud and WordPress vulnerabilities, credential brute-forcing, and carefully organized stolen material.
A recovered CSV also pointed to roughly 9 GB of data stolen from the nuclear agency and evidence suggesting a possible third victim.
Check out the full article here 👉 https://t.co/jtxB58TYeH
#ThreatHunting #ThreatIntel #CyberSecurity
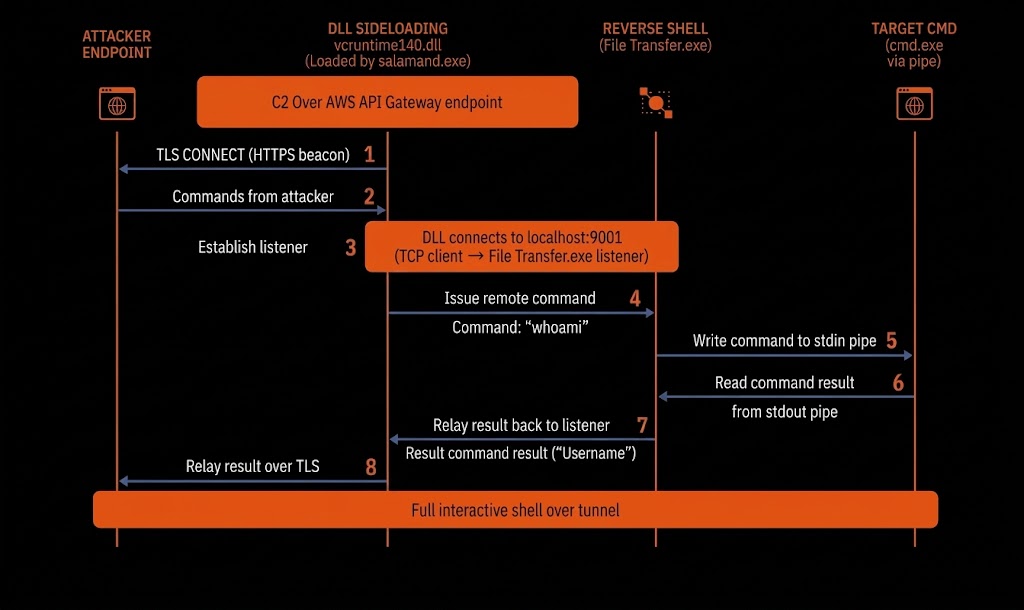
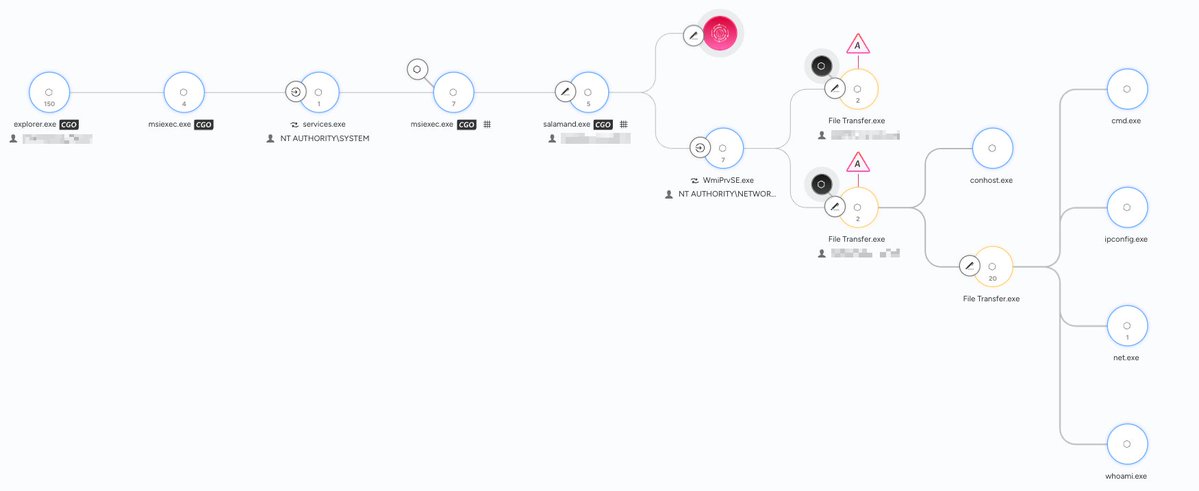
Fake IT support campaign delivers a malicious MSI that sideloads a trojanized DLL via a signed binary, then uses WMI to launch a custom reverse shell tunneled over a local port (localhost:9001) to an AWS API Gateway C2. Detection and indicators: https://t.co/821NAc1bSo
China Web OSINT Search Dorks
Guide by ArgeliusLabs:
A practical China OSINT workflow
Baidu search syntax and operator behavior
People and professional-biography dorks
Government, regulatory, and licensing dorks
and more.
https://t.co/jBN1jxvo3D
🇹🇭 Thailand Union Auction Database Allegedly Offered for Sale
A threat actor is advertising the sale of a database allegedly belonging to https://t.co/qn6vIgYy6N (Union Auction).
* Union Auction is a major vehicle and asset auction company operating in Thailand.
* The seller claims the dataset contains 12,059 registered member records.
* The database is reportedly available in JSON or CSV format.
* Sample data shown in the post appears to reference bidder information, account identifiers, user details, and other member-related records.
* No independent verification has been provided to confirm the authenticity or scope of the alleged dataset.
* The post suggests the data is being offered directly to interested buyers on a cybercrime forum.
Analyst Note: Although the claimed record count is relatively small compared to large-scale breaches, auction and marketplace platforms often contain identity, contact, and financial-related information that can be leveraged for fraud, account takeover attempts, and targeted phishing campaigns.
#DDW #Intelligence #DarkWeb #Thailand
Hello guys،
Do you want to Bypass all production EDR ?
Read my new research to enjoy in kicking EDRs defenses.
https://t.co/Y0QMWXM9GZ
The proof-of-concept implementation is available at https://t.co/CAUeRcumK5
#Maldev
Matkap: A Python OSINT tool for hunting exposed malicious Telegram bot tokens and chat IDs via FOFA and URLScan, then analyzing or exporting captured bot activity.
GitHub: https://t.co/ECExxHF9ux
Credit: @0x6rss
‼️🚨 This is alarming: Researchers found a one-click data exfiltration vulnerability in M365 Copilot. A single click on a trusted microsoft[.]com link let attackers pull emails, MFA codes, meeting notes, and SharePoint/OneDrive files, no permissions or second click required.
Microsoft has patched it as CVE-2026-42824, rated critical.
🆕 NightmareEclipse Bitlocker Bypass 0-Day Detection
GreatXML is a Windows zero‑day that bypasses BitLocker by abusing the Windows Recovery Environment (WinRE) and Defender Offline Scan workflow, allowing an attacker to gain an unrestricted shell and access encrypted drives without credentials.
Here's a GreatKQL to compliment the detection 🤭
https://t.co/DfFnZMnZqb
#Cybersecurity #NightmareEclipse #GreatXML #GreatKQL
🇹🇭 Alleged Thailand Citizen Database Offered for Sale
A threat actor is advertising what they claim to be a database containing information on approximately 36.1 million Thai citizens.
* According to the listing, the dataset allegedly contains:
* Full names
* Phone numbers
* National ID card numbers
* Dates of birth
* Gender information
* Physical addresses
* The seller claims the records represent roughly 50–70% of Thailand's adult population.
* The actor further alleges the information was collected from multiple sources, including government agencies and private-sector organizations.
* The dataset is reportedly being offered for sale for $100,000 in Monero (XMR).
* At the time of publication, Daily Dark Web could not independently verify:
* The authenticity of the dataset
* The source of the records
* The claimed number of affected individuals
* Whether the data is current, aggregated, or recycled from previous breaches
* No independently verifiable evidence was provided publicly to substantiate the full scope of the claim.
Analyst Note:
If legitimate, a dataset of this scale would represent one of the most significant exposures of Thai citizen information observed on underground forums. Large national identity datasets are frequently leveraged for identity fraud, SIM-swap attacks, financial scams, account recovery abuse, and highly targeted social engineering operations. Claims involving tens of millions of citizens should be treated with caution until validated through technical analysis and corroborating evidence.
#DDW #Intelligence #DarkWeb #Thailand
Evading Detection with Nezha - Persistence
Nezha is a RMM that can be abused to maintain persistence. Highly customizable. Doesn't show up in the tray. The name of the service, executable and other things can be changed. In fact, hackers can easily change the installation script and host it on their infra.
The Defender doesn't have any problem with it.
That's what makes it so dangerous. We also included the forensic artifacts that can help you detect it.
Learn more: https://t.co/8np8jXJSuy
@three_cube@_aircorridor
#apt #redteam
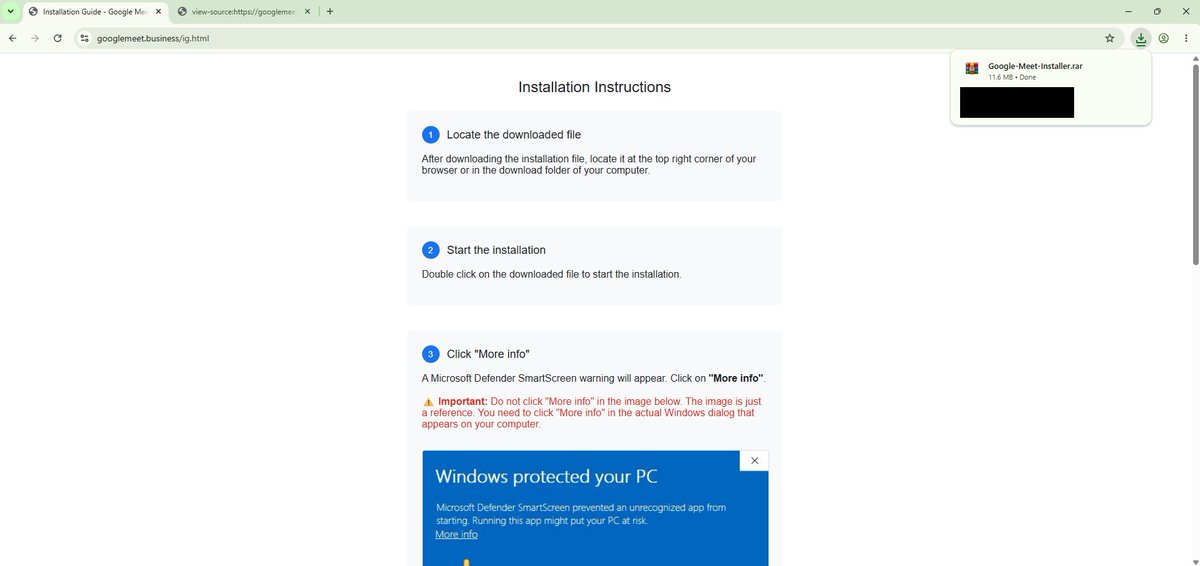
🚨 Fake Google Meet site distributing Remcos RAT.
Victims are presented with a fake Google Meet page, prompted to "update" their client, and instructed to bypass Microsoft Defender SmartScreen warnings. The downloaded archive contains a renamed Haihaisoft PDF Reader executable (hpreader.exe).
IOCs:
Domain: hxxtp://googlemeet[.]business
file name: hpreader.exe
SHA256: 08c7fb6067acc8ac207d28ab616c9ea5bc0d394956455d6a3eecb73f8010f7a2
#malware #phishing #Remcos @malwrhunterteam@500mk500
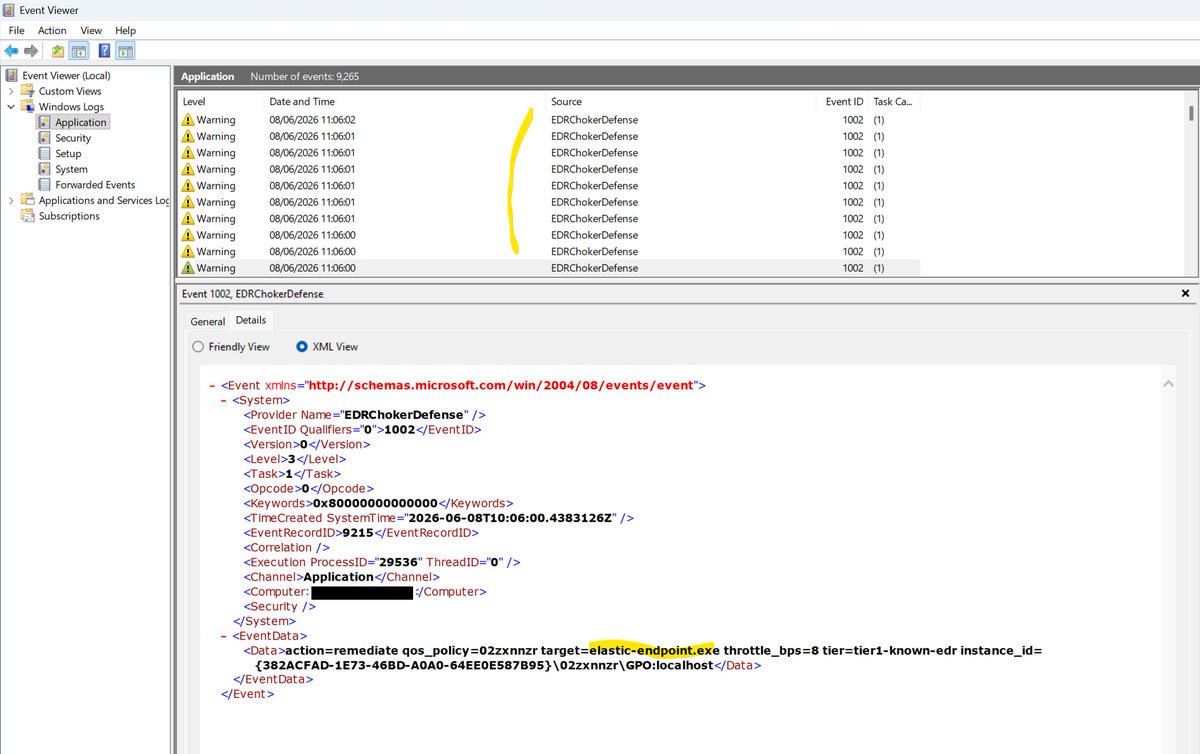
EDRUnChoker😀registers a permanent WMI subscription with a 5-second timer runs embedded VBScript (fileless) that deletes malicious MSFT_NetQosPolicySettingData policies targeting known security products or aggressive app-path throttles.
https://t.co/A1hcrpav2X