Never be a creditor. OPSEC when in doubt. Guard your principal. Celsius Network fraud survivor. Mashinsky was a criminal. CC MK3 survivor just by luck 3.1.9.
@zherbert Would agree in general that 2FA’s on disconnected Foundation Passport Prime > 2FA on a vault that syncs across devices.
PS Though different, nostalgic for the old RSA physical key that came with etrade back in the day. It forced you to enter the # each time w the PW!!
@bitnorbert@zherbert@FoundationHQ@btcqna Also, how many devices were sold since the switch to Shopify?
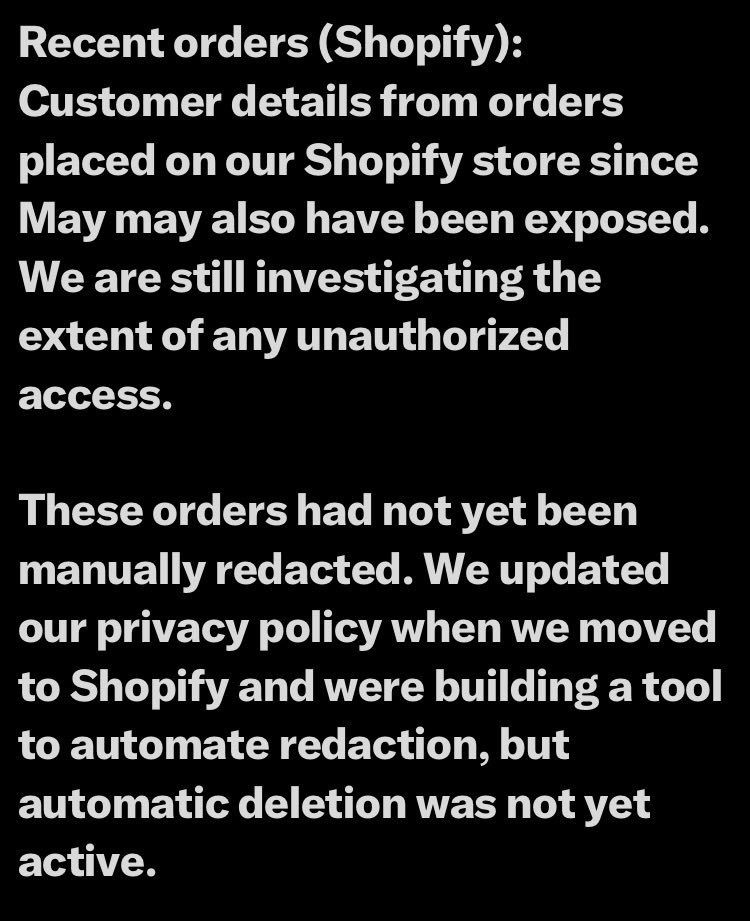
How long does it take and what is the process to manually delete info from Shopify? Email request? Access?
Could this have been done while the tool was developed?
Well, I am no Nostradamus but I warned 9/4/26 @FoundationHQ ; too bad this wasn’t done or even responded to 🤔
Shopify…. Known risk vector
Got the email as a recent customer, so can confirm
Opsec identity once lost cannot be regained.
@zherbert
Since @FoundationHQ uses Shopify, has the company thought about a way to get them to delete Foundation purchase history from user accounts once shipped?
The same exposure could happen to Foundation users if Shopify was hacked.
Since @FoundationHQ uses Shopify, has the company thought about a way to get them to delete Foundation purchase history from user accounts once shipped?
The same exposure could happen to Foundation users if Shopify was hacked.
@zherbert@FoundationHQ@btcqna Timing is everything I guess.
🤔 Fair… or too far.
„We knew well in advance the Japanese might attack Pearl Harbor and we were going to move our battleships on December 9, just days away.“
@SimonDixonTwitt Mashinsky is a a disgusting fraud with no remorse for the untold damage he caused.
Of course Alex is trying to get out of it.
Like Simon, I will NEVER be made whole in Bitcoin terms which was the majority of my holdings
@KeystoneWallet Do you use a third party like Shopify to satisfy your orders or do you do all in house?
Third party vendors are just a much a threat to a customer’s crypto privacy if they are hacked.
Shared ownership of buildings are Ponzi schemes.
All infrastructure has full replacement, failure as time progresses.
When governments mandates upgrades, often
necessary due to safety, it is exacerbated.
Don’t be a “bag holder” in an old building. Get out b4 the bill hits.
HOA's are faltering everywhere in California. People cannot afford the dues because of the cost increases. Most were underfunded and now cannot handle the special assessments.
People are already selling at $.50 on the dollar in San Diego and downtown real estate is crashing to zero.
@RichLassiterMD@BigSkyHODL You left your gas cap unlocked. I siphoned it.
Here it is back but I am now keeping 15 percent of it because you should have done a better job securing it & I need to get paid for my time 🫠
Rogue White Hat, probably
@DoomerTapes Simple answer in the classics.
Ralph Waldo Emerson
“Travelling is a fool’s paradise…. I can be intoxicated with beauty, and lose my sadness… but I am not intoxicated. My giant goes with me wherever I go.”
Since @FoundationHQ uses Shopify, has the company thought about a way to get them to delete Foundation purchase history from user accounts once shipped?
The same exposure could happen to Foundation users if Shopify was hacked.
Two days ago, we received an update from our shipping provider, ShipMonk. We're deeply saddened to share the news that the recent data breach affects more customers than originally thought.
Another 67,000 customers from the US who ordered between November 2019 and August 2021 were affected, with their full details (name, email, phone number, shipping address, order number) exposed.
All affected customers have been emailed directly. If you didn’t receive an email, then you are not affected.
Throughout our entire relationship with ShipMonk, we repeatedly requested and received written assurance confirming the deletion of the data, in line with our contract, data policy, and past communications. We are very disappointed that, despite receiving this confirmation, the data was not deleted in their systems.
Trezor systems were not compromised, and your device is secure. But please be alert for fake emails, phone calls, fraudulent letters, and potential risks to physical security.
NEVER share your wallet backup with anyone or type it into a website.
We’re terribly sorry to everyone affected. We take this matter very seriously and are working to ship anonymous delivery ASAP, so you can protect your personal information when placing an order.
For more information, visit our blog: https://t.co/3KnO4LyBKb
@Pledditor I kind of wish AI was around for Celsius Network/Alex Mashinsky
Imagine the AI slop from Alex that would have put Saylor to shame & a CEL token whitepaper written by AI.
My BTC would have never touched his fraudulent platform.
Just like not a penny put in SRTC, MSTR etc
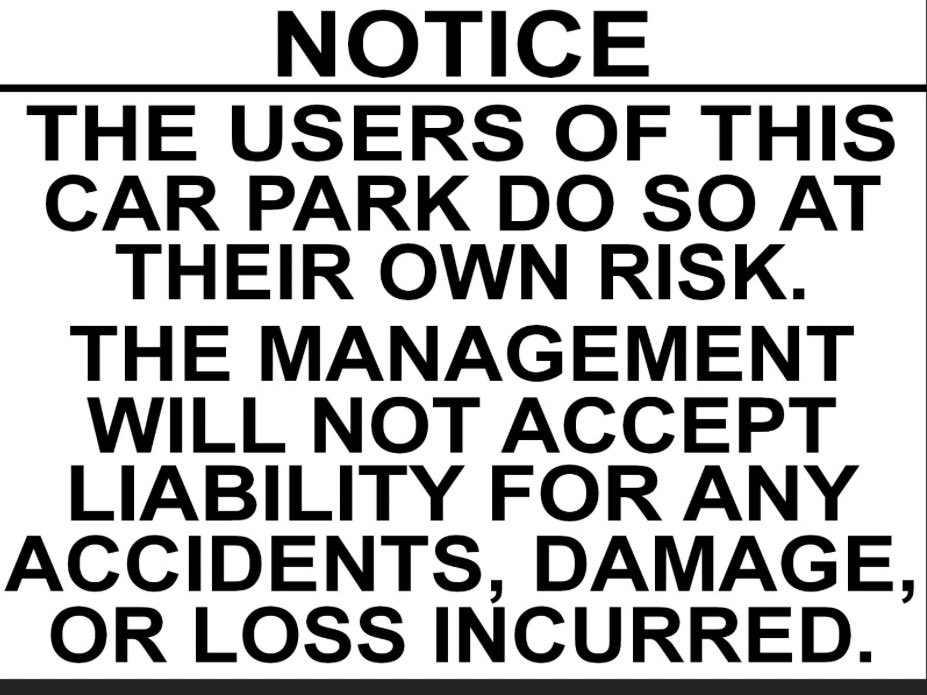
@BritishHodl Multi billion dollar construction projects are insured with performance surety bonds but not one company will insure your lost crypto by failure of the hardware wallet vendor or crypto exchange/custody.
You are parking your car in their parking garage. Zero liability to
them.