My report to @msftsecresponse was assessed as "By Design". However, as a direct result of my report, Engineering had to update the docs to clarify undocumented/confusing behavior. Sometimes the Soft-Patch isn’t code, it’s the documentation.
#MSRC#BugBounty#CyberSecurity
@DsokeyyV أنا هو صاحب القصة شخصيا 😂😂😂
أنا بينت في ال PoC كيفية استغلال الثغرة و سحب ال PII بينما صاحبنا مبلغها origin reflection فقط، لكن بما أنو بلغ عليها قبلي بي 16 يوم يعني هو لي أخذ الباونتي.
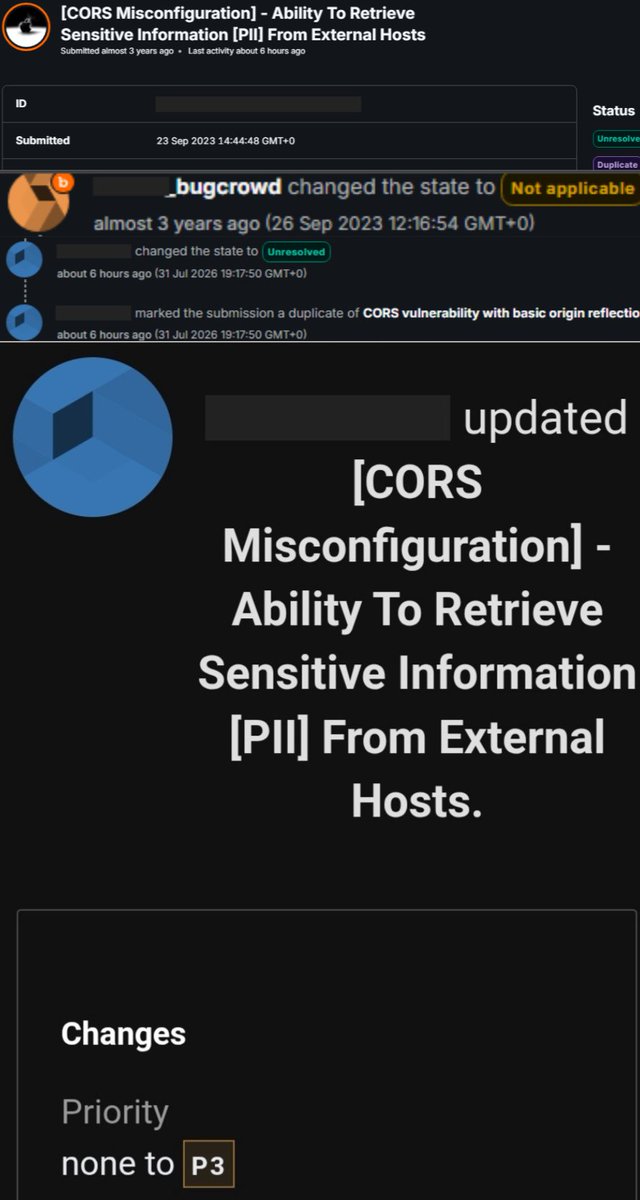
3 years ago (Sep 2023):
On @Bugcrowd I reported a CORS Misconfig exposing PII → Closed as N/A.
Yesterday (31 Jul 2026):
A program Team Member re-classified it as a valid P3, but marked duplicate of a report submitted 16 days earlier.
¯\_(ツ)_/¯
#BugBounty#CyberSecurity
@marxbanter@MintPressNews Those bitchhes are IOF pigs. FYI, every single israheli pig is a legitimate target, not only in Palestine but all over the world
@YossiBenYakar Glad to know that bitchh was sent to hell. Fuck her, fuck you, and fuck every single izraheli bastard. Fuck you ALL, you dirty scumbags 🖕
@msftsecresponse Thank you! I appreciate the collaboration and transparency from both the MSRC and Product Engineering teams. Always glad to contribute in strengthening the ecosystem.
My report to @msftsecresponse was assessed as "By Design". However, as a direct result of my report, Engineering had to update the docs to clarify undocumented/confusing behavior. Sometimes the Soft-Patch isn’t code, it’s the documentation.
#MSRC#BugBounty#CyberSecurity