For those running apps on @Railway and affected by their breach (you should have an email)
Use your agent to do a quick review of all the keys that need to be rotated.
I think this is more serious than many people realize.
Not every Node.js server is vulnerable, of course. The application needs to process untrusted Brotli-compressed data.
But how common is that? Well, common middleware configurations in Express 5 can already expose the vulnerable decoder, without developers explicitly using Brotli anywhere in their code.
So we’re potentially looking at a pretty large attack surface, although nobody really knows how many deployments are exploitable yet.
I wouldn’t be surprised to see automated scanning and exploitation attempts targeting this very soon.
Patch your Node.js runtimes.
SMS/Voice deprecation --> Passkey registration campaign has caused a lot of confusion
This is as consice of a statement as you'll get
If the user is eligible for SMS or Voice in Entra Authentication methods, they can enroll whatever passkeys they want
PowerShell 7.6.8 is released on GitHub and will be available via WinGet soon.
It's a maintenance release that moves the .NET SDK to 10.0.402 and somewhat ironically removes the update notification feature from PowerShell, per customer feedback. 🗣️
💾 https://t.co/lgF9hrw5hH
Desktop #AI is moving fast—a secure rollout for your organization starts here. Join @paulsems, @PyroTek3, and Scott Blake on November 4 for our next #webinar, “Leash Your LLM: Rolling Out Claude and Copilot Securely.” Secure your spot now! https://t.co/m1qAbdJWmk
Greg created the Linux OS CentOS, has healthy views on artificial intelligence, is letting his people do their jobs and is looking for more people instead of firing them. Go work for Greg and tell him BRS sent you but behave yourselves. We are the swarm but we are not animals. 😉
WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners.
Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads.
Firmware was locked down, so zero-days it was.
Got a root shell.
then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems.
This isn’t a bug, It’s the product bro.
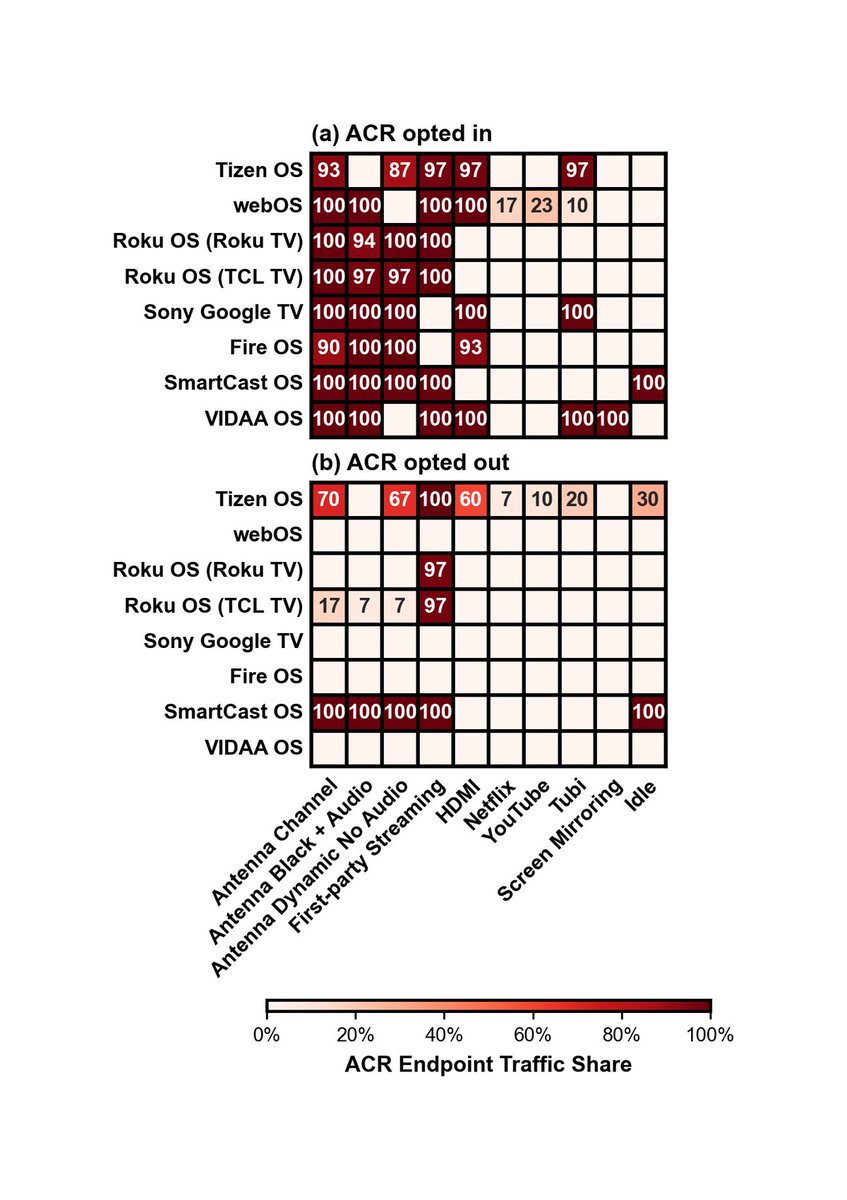
❗️ Samsung and Vizio smart TVs kept contacting the servers that track what you watch after users opted out, Northeastern University researchers found.
On Vizio the opt-out had no visible effect, even with the TV idle.
🦛🦛🦛Microsoft patched PetitPotam this October: EFSR now only resolves local paths. This means WebDAV to LDAP Coercion is fixed!
Remaining methods for clients are WSP (coercing SMB) and PrinterBug (coercing RPC), but both cannot be relayed to LDAP 💀💀💀
A great reminder that Entra App Proxy, Cloudflare Tunnels/Access, or some sort of ZTNA is a great way to remove stuff you don't want hacked from the Internet