RUCKUS engineers and partners:
Is DPSK3 / WPA2-WPA3 + DPSK becoming a real-world deployment pattern, or are most customers still relying on captive portals and shared PSKs for guest access?
Genuinely interested in what you’re seeing in the field.
#RUCKUS#WiFi#WPA3#DPSK
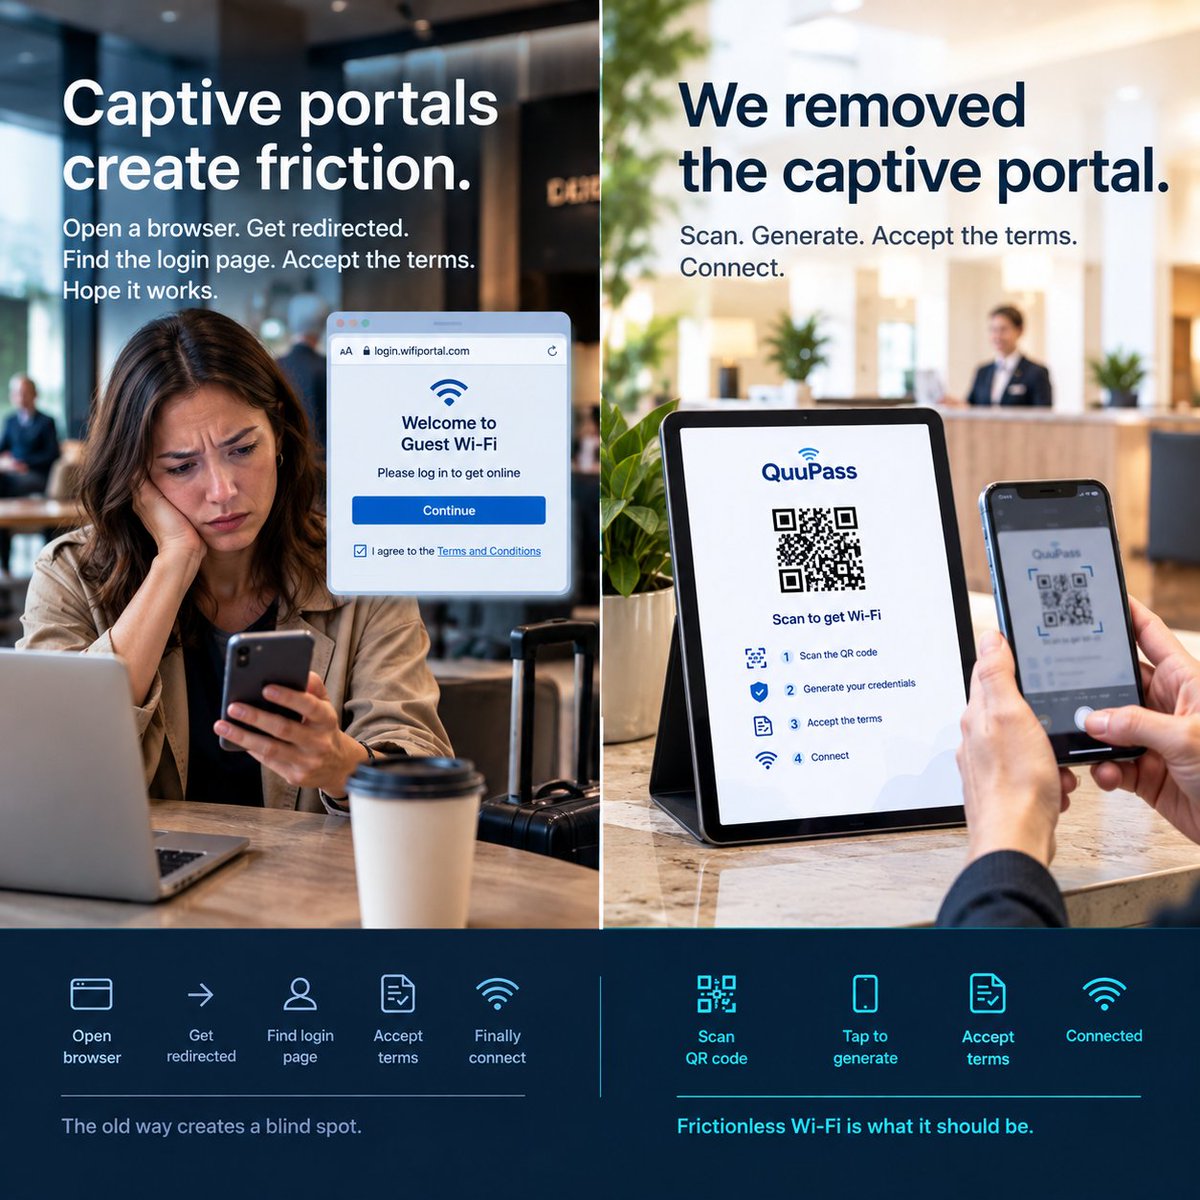
Captive portals still create friction in 2026.
Different devices, different behaviour. Login pages fail, guests get stuck, and front desk staff end up troubleshooting Wi-Fi.
Twenty years later, we’re still doing this.
A shared Wi-Fi password doesn’t expire when whoever wrote it down leaves.
It gets copied into a group chat, taped under the front desk, passed down by last semester’s students — and stays valid until something finally goes wrong.
That’s a Wi-Fi blind spot hiding in plain sight.
We’ve spent a surprising amount of time building the boring parts of guest Wi-Fi.
Unique credentials. Automatic expiry. Using infrastructure businesses have
The goal isn’t to make Wi-Fi complicated
It’s to remove the things that shouldn’t have been complicated in the first place.
A shared Wi-Fi password doesn't expire when whoever wrote it down leaves. It gets copied into a group chat, taped under the front desk, passed down by last semester's students — and stays valid until something finally goes wrong.
Captive portals cause 30–40% of peak check-in support calls at some properties. Not guest error — the login screen just fails differently on iOS, Android, Windows, and won't even load on a smart TV. Two decades of friction for something that costs the property almost nothing.