> Highlights – the bugs you might find interesting:
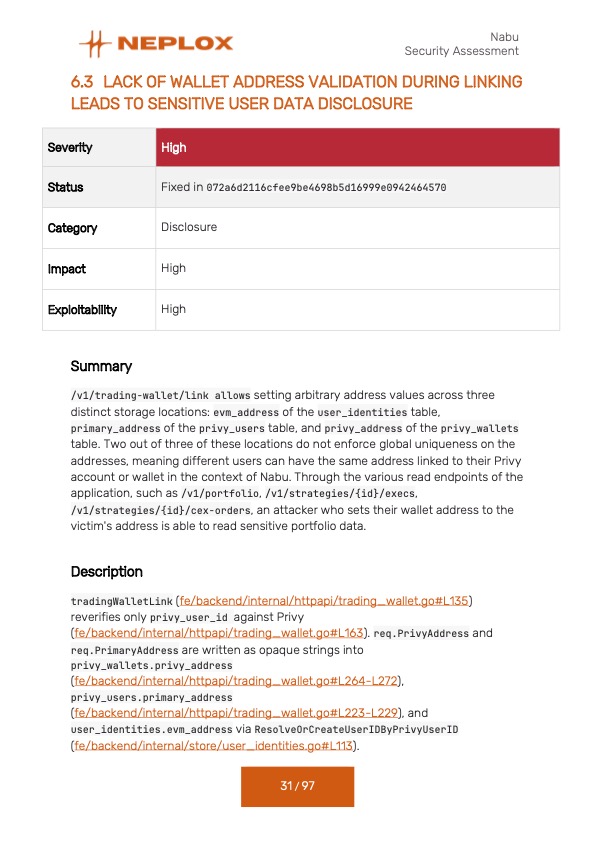
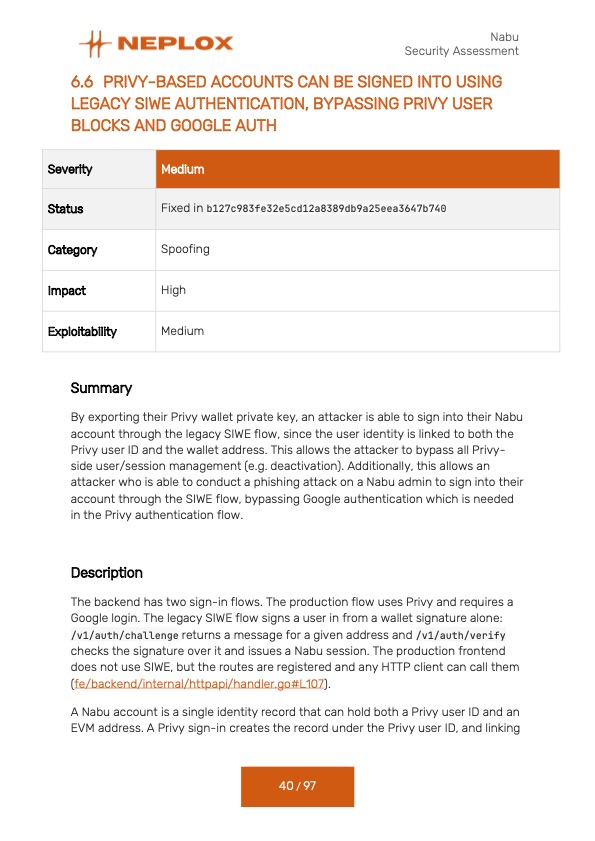
0️⃣ PrivEsc TO Admin: through Privy Google account linking
1️⃣ Data Leak: when users can link the same address → they collide
2️⃣ Another sign-in flow + Privy / Google Auth bypasses = Account Spoofing
👉 https://t.co/ixzJyZbN17
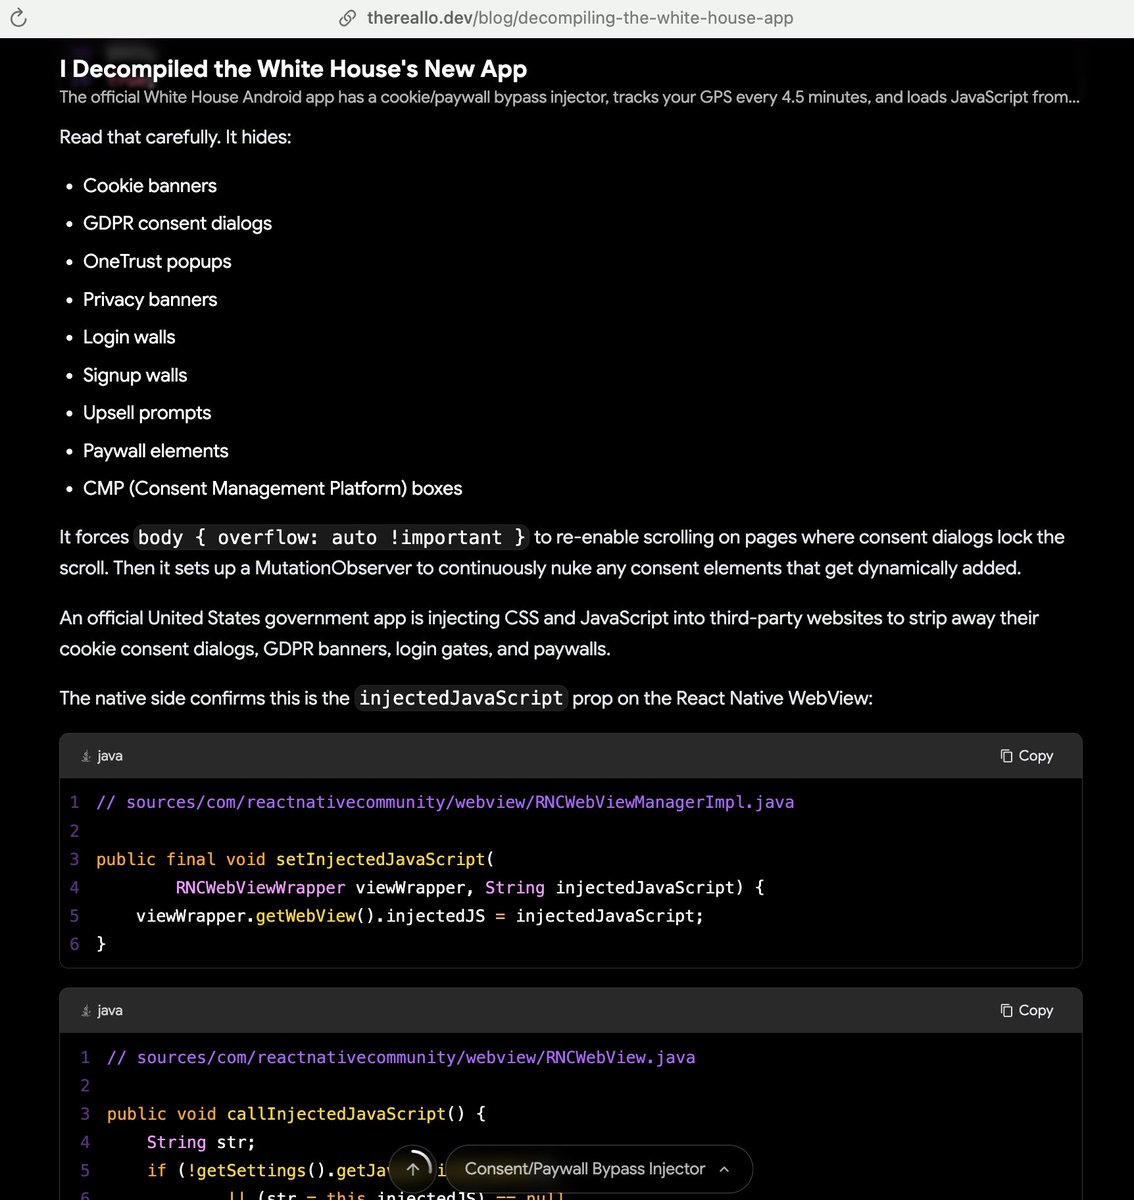
🔗 Honorable mention!
https://t.co/XHR1EzOQiy
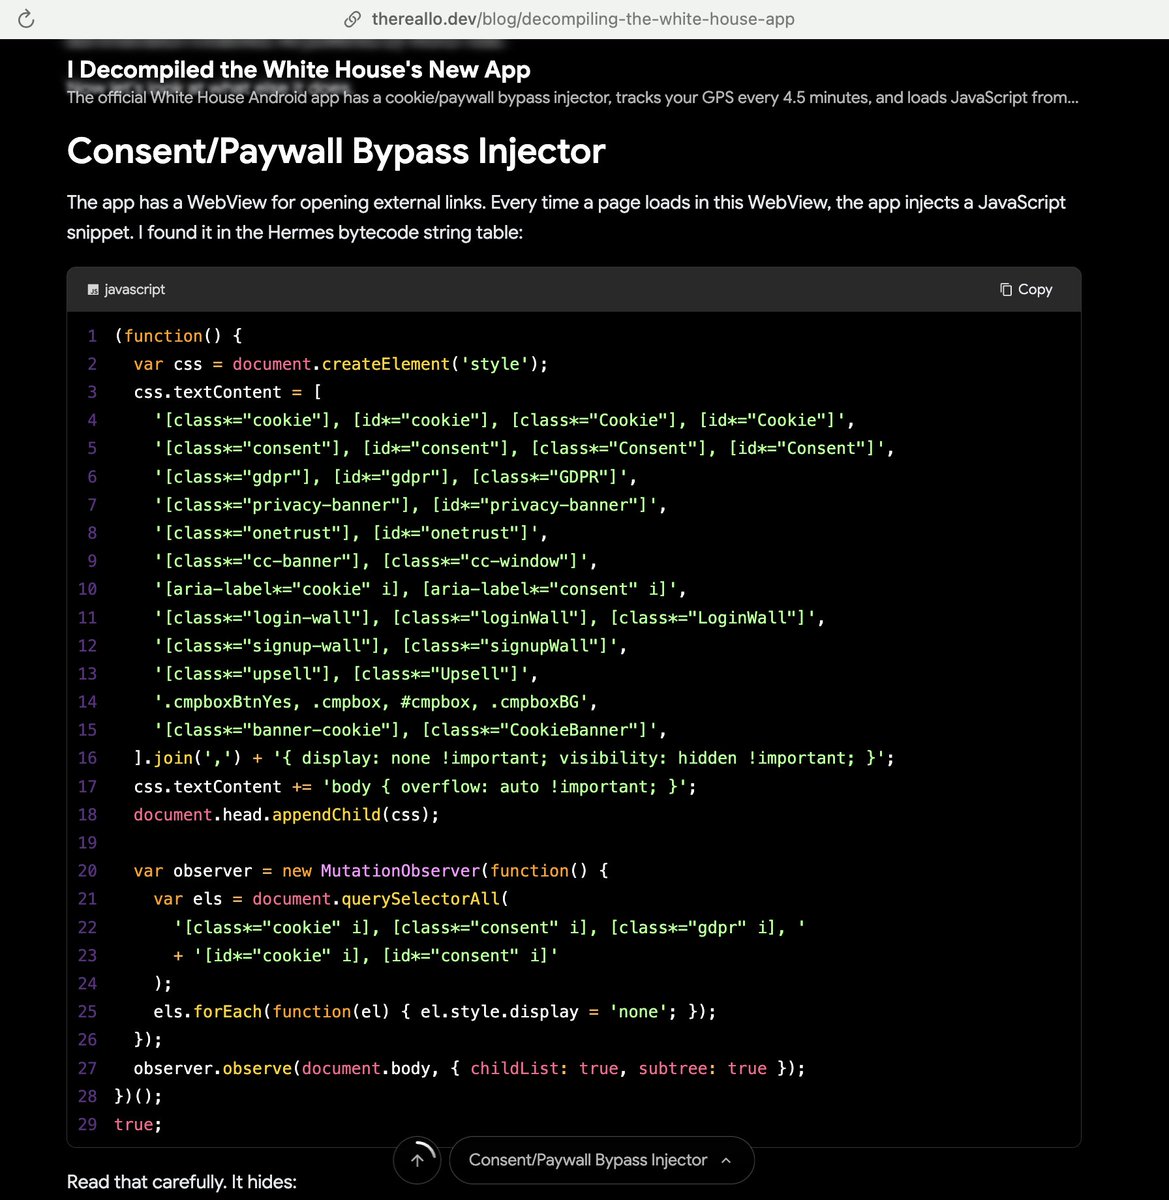
• Cookie banners,
• GDPR consent dialogs,
• Privacy banners,
• . . .
– All gone! Some applications take away your choice altogether 🤷♀️
ok, fine, I guess, these choices don't even matter that much anyway, so –
Yet Another i̶N̶̶D̶̶E̶̶X̶̶e̶̶r̶̶ video in the “Security Ensh!*$ttification” series [where each episode covers a certain hot topic + introduces you to research articles]!
> Let's discuss how websites collect & sell data; 💸
👁 Ep.01 – Data Markets:
https://t.co/bCligku1JN
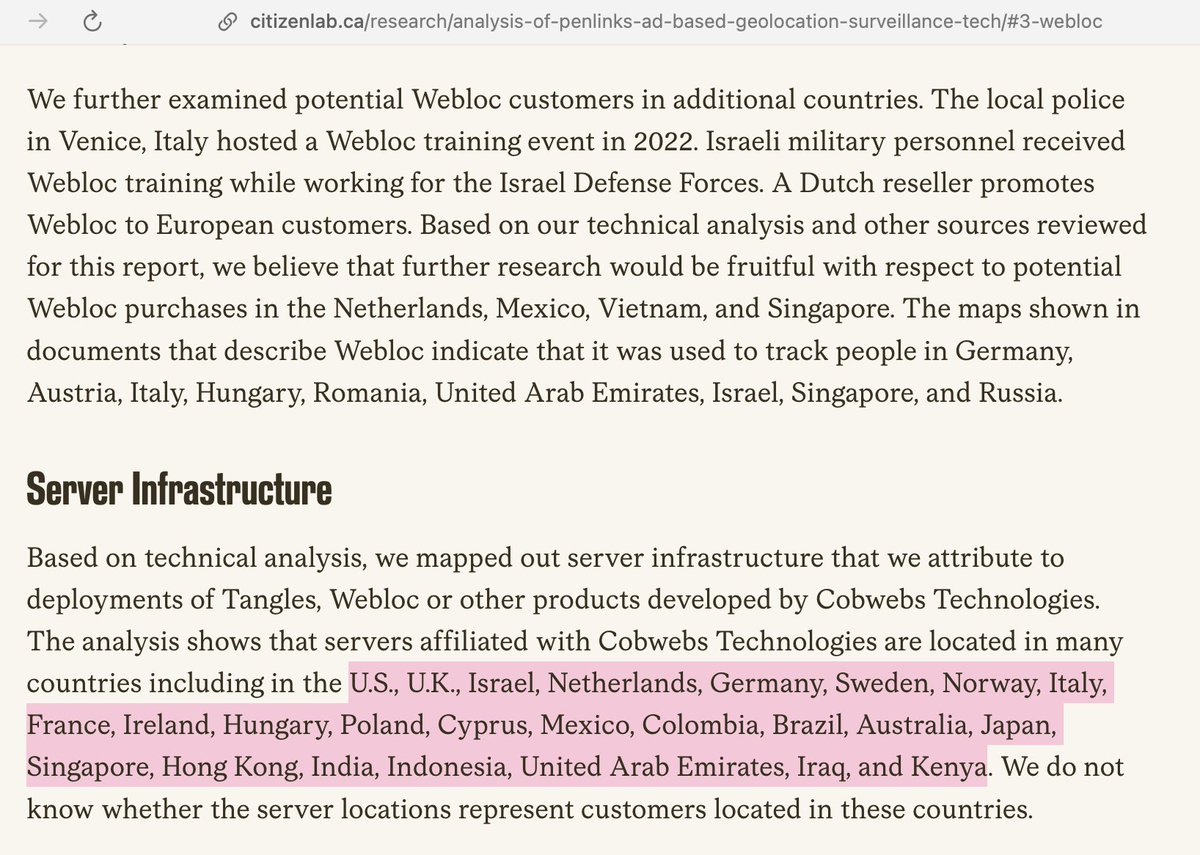
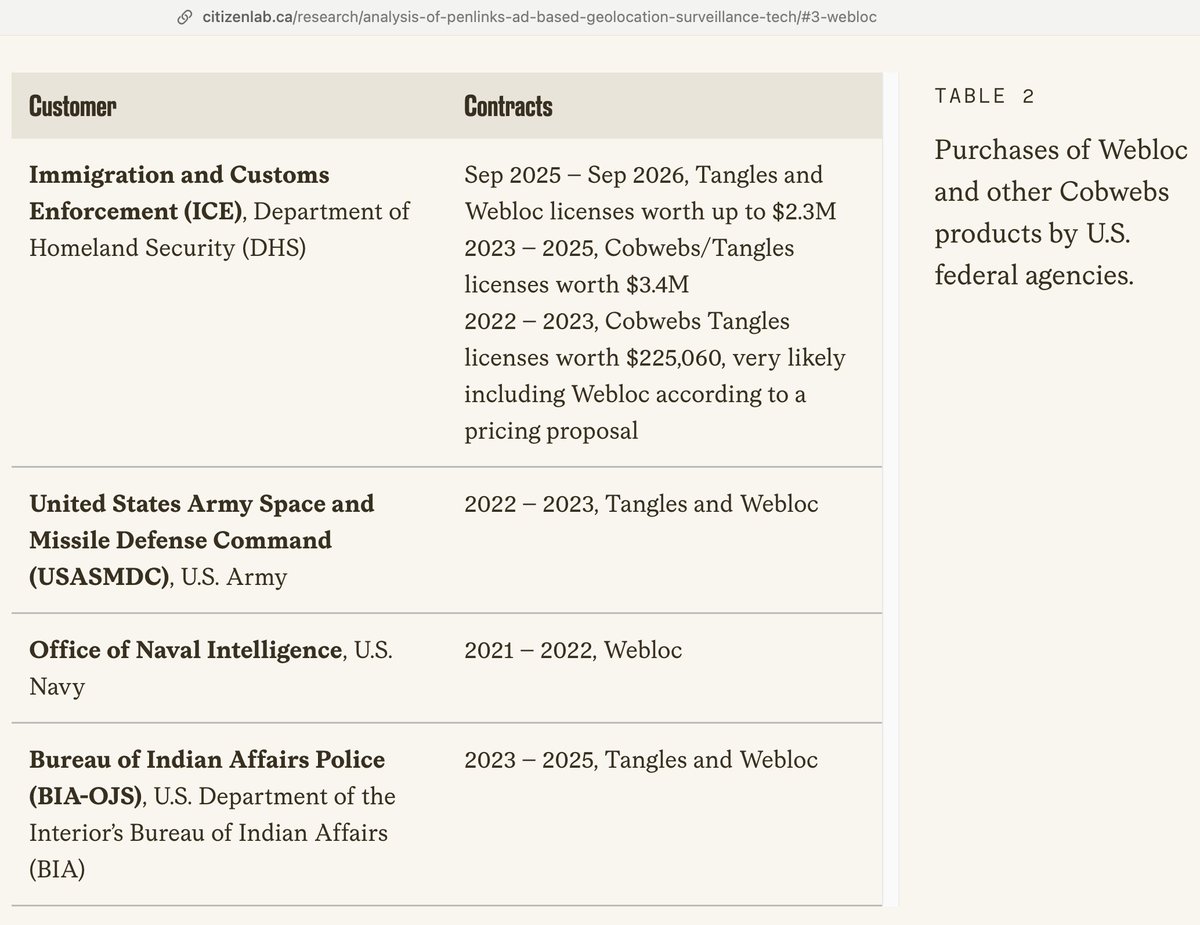
🔗 As for the recent findings, the Citizen Lab team uncovered "Webloc": https://t.co/z4BziPDi07
[RTB sources (ad auctions) +
SDK sources (mobile apps)] =
Mass surveillance (500M phones) 🫡
• geolocation
• personal data
• what else do you need??
📄 https://t.co/zGwZDvcczX
🔗 Honorable mention!
Nekogram leaked {UserIDs + phone numbers} of their users -> they went straight to a certain Telegram bot;
• https://t.co/L05pYpJSWp (see WebArchive 🔎)
• https://t.co/wrA54XRECH
“make your own freaking client, baka” 🤧
Sometimes I feel like yapping about security issues; but not in a shitposting way - 🥀
So I recorded a series of videos – “Security Ensh!*$ttification”: each episode covers a certain hot topic + introduces you to research articles!
👁️ Ep.00 – Backdoors:
https://t.co/iDyspvjAZF
🔗 Highlights on extra fun features in Telega (yet another Telegram client):
https://t.co/vBjC9z7ynU
https://t.co/Y4rKi5Xumw
• Man-in-the-Middle on command
• disabled Perfect Forward Secrecy / E2E chats
• yet another ban module
• AI-powered moderation platforms ✨
🔗 1/5
Our team has further analyzed how TON Connect features may be utilized by bad people to mask malicious activity;
⚡ Little did we expect that some of them might trigger vulnerabilities in TON wallets! ⚡
⚠️ You've encountered an error! Check the thread to resolve it...
🏰 1 / 6
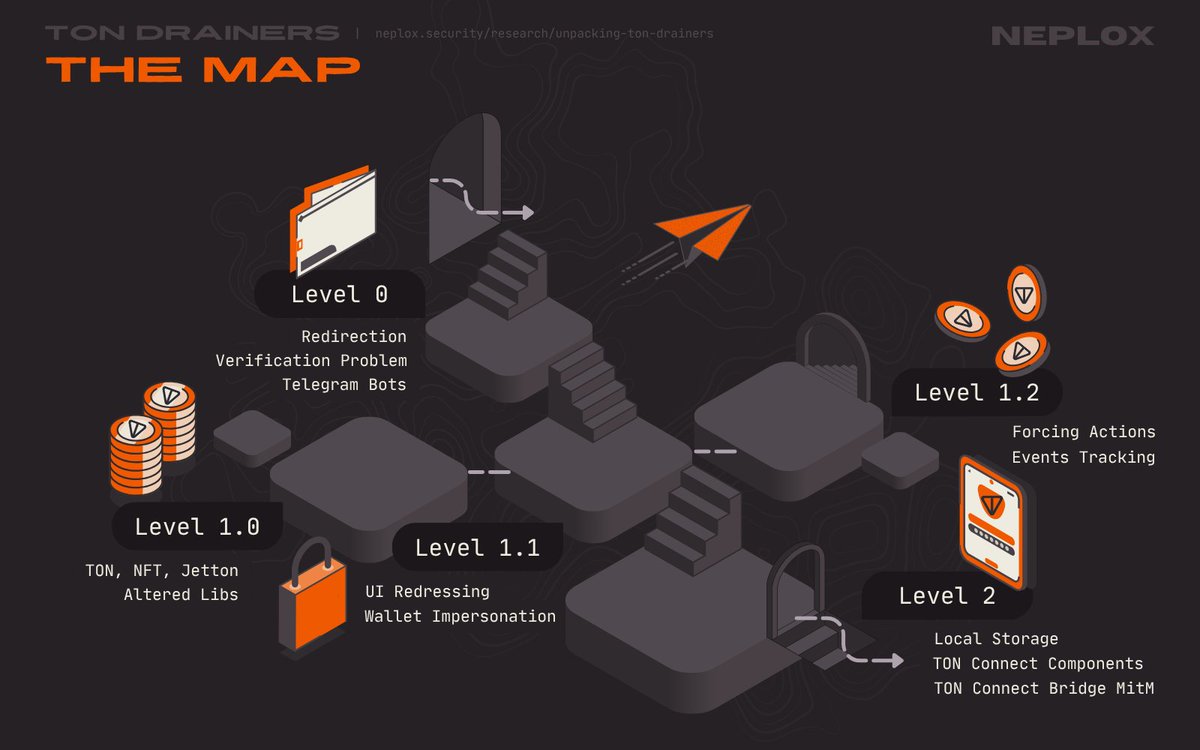
We've laid our hands on #Crypto#Drainers designed specifically to steal #TON, #NFT, #Jettons
Analyzed their source code (Client + Server) & discovered what features of legitimate products they exploit to forge #DApp origin + impersonate #Wallets
👉 Follow the thread!
Neplox is coming to @BSidesNYC to talk about the #TON of #Crypto Drainers!
🎙️ ‟Down the Drain: Unpacking TON of Crypto Drainers”
🗓️ Oct 18, 10:00 EDT
📍 New York City, US
Join us to learn about:
• #Malware architecture
• #DApp / #Wallet Impersonation
• Exploited features
🌐 My #TheSAS2024 talk discussing threats in dating apps & technical features of the #malware found has been published on YouTube;
📄 Slides: https://t.co/3J8fgLNedQ
🎥 Video: https://t.co/XdN8H3OhQU
Thanks to everyone who made this event happen and thanks for having me! 🩵
🐀 CraxsRAT sample 🇷🇺 from Russia
– C&C server
– Debugging detection
– Audio recording / Location tracking / Gesture control
– CraxsBrowser / Injections into WebView
Check out the full research:
[📑] https://t.co/NM1oRy7AJb
1. https://t.co/VeNmWR4Edo
2. https://t.co/xtbycUzyvo
> Love is... NOT gaining remote control over their device!
Here is my analysis report on #malware gathered among Russian dating apps:
[📑] https://t.co/NM1oRy7AJb (EN / RU) [+ PDF]
🎣 Phishing
💸 Banking Trojan
🐀 CraxsRAT ‼️
#MalwareAnalysis#ThreatIntel#CTI#CyberSecurity
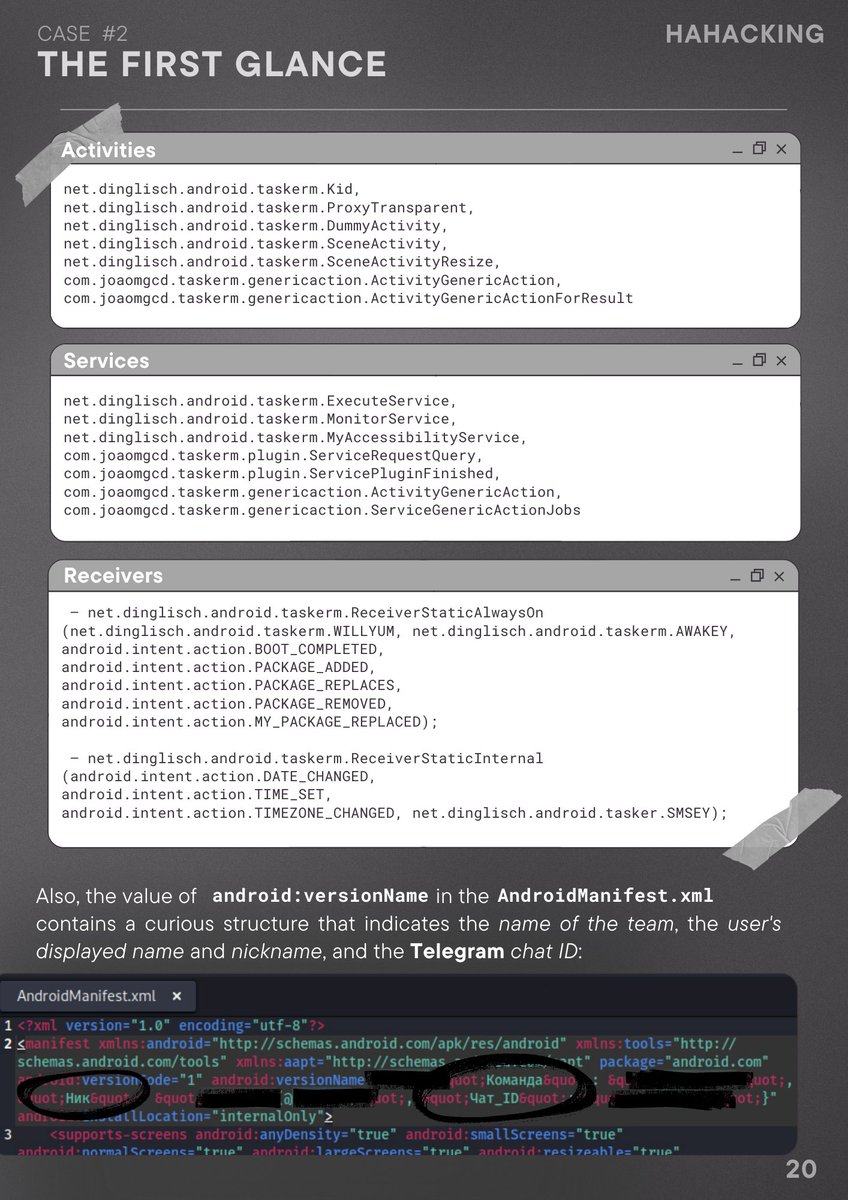
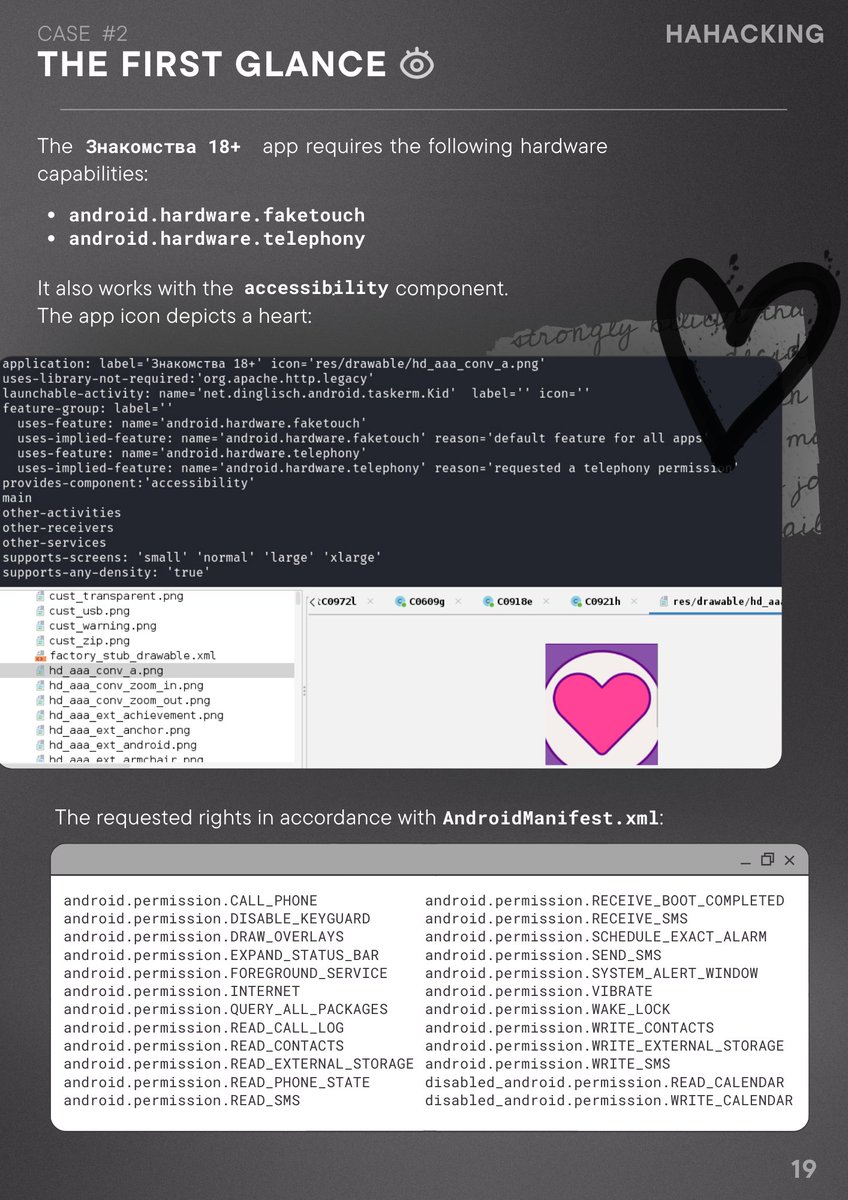
💸 Banking Trojan made w/ Tasker 🇷🇺 from Russia
– C&C server + Telegram bot
– License validation / Debugging detection
– SMS & phone call processing
– RAT mode / Blackmail / Spam / Stealer mode
Check out the full research:
[📑] https://t.co/NM1oRy7AJb
https://t.co/QOaO2VulbK