Built a vulnerable e-commerce app for pentesters and AppSec engineers to hack legally. 40+ vulns. OWASP Top 10 (2025) + LLM Top 10.
Hack it live or spin it locally with Docker. https://t.co/UfTLxRcdXe https://t.co/UG5nKmQhme
#AppSec#BugBounty#OWASP
🚨 PHP2Shell detection is now available in Burp Suite Professional & Burp Suite DAST.
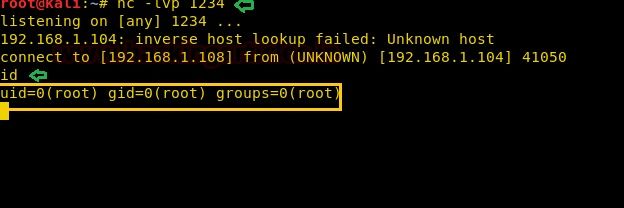
Most of the web is powered by PHP, which means most of the web is vulnerable to these critical unauthenticated remote code execution flaws (CVE-2026-109618 / 109619). You can already detect it in Burp Suite using:
🟧 ActiveScan++ v2.0.13 (https://t.co/fkhECQ6wtD)
🟧 Bambda scan checks (https://t.co/PxPcj5uDYX)
🟧 BChecks (https://t.co/i8c8WiDnvb)
Start scanning for the vulnerability now → https://t.co/fkhECQ6wtD
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Two critical PHP RCEs leaked before the embargo. watchTowr and Previdian both reproduced them.
Patches are live now. CVE-2026-109618 and CVE-2026-109619. CVSS 9.2 officially.
If you run PHP in production, you might want to start looking at this
For days now, I picked a free Ai-agent and started the harness training, I kept improving it and adding more skills to it, then I picked @r007User CTF website for a testing ground, you won’t believe how powerful it has become and how it was able to chain from SSTI to an RCE.
First you register as a seller
curl -s -c cookies.txt -X POST https://t.co/enSUbzIxbf \
-d "username=rceuser&phone=+2348000000000&[email protected]&password=password123&role=seller&referral_code="
@r007User then you login with the credentials
Cloudflare open-sourced the security audit skill that seeded its own vulnerability hunting harness. Your coding agent can now run it on your code.
How it works, in 6 phases:
→ maps your codebase
→ hunts for bugs area by area so nothing gets skipped
→ sends every finding to a fresh agent that didn't find it, to confirm it's real
→ writes structured results
→ verifies each record again, independently
→ writes the final report
You get a findings file split into confirmed, needs validation and rejected, so you fix the real problems first.
Install:
npx skills add https://t.co/ptOfJggqQB --skill security-audit
Then open your agent in your project and type: "security audit this codebase"
MIT licensed, 31.3K stars.